









I spent last week at Gartner's Identity & Access Management Summit EMEA in London. Authorization was everywhere this year. Not tucked away in a single session. Woven through at least a dozen analyst presentations, and honestly, most of the hallway conversations too.
The vibe in the corridors was different from previous years. AI agents have gone from "interesting demo" to board-level initiative at a lot of the organizations I spoke with. Execs have signed off on agent strategies, announced them to stakeholders, set timelines. And the job of actually securing it all? That's landed squarely on the laps of identity and security teams, many of whom are still working through their existing IAM backlogs. The question I kept hearing wasn't "should we do authorization?" but "how do we do authorization for agents when we haven't even finished doing it properly for humans?"
Paul Mezzera dedicated an entire session to Authorization Management Platforms. For those of us who've been building in this space, the structural diagnosis wasn't surprising, but hearing Gartner say it this clearly matters. IGA handles static roles and groups. Access management gives you coarse-grained controls. Neither does fine-grained, dynamic, real-time authorization. AMPs fill that gap.
What caught my attention was his framing of the interoperability problem. Authorization engines and enforcement points are built by different vendors, deployed in different environments. For externalized authorization to work at scale, they need a common protocol. AuthZEN fills that role at the PDP-to-PEP layer. This maps directly to how we think about Cerbos: your policies are authored and evaluated centrally, but enforcement happens wherever the access decision needs to be made, in your API gateway, your application code, your service mesh. The PDP doesn't care where the PEP lives, and AuthZEN is what makes that contract explicit.
Mezzera also went after DIY authorization. 5 risks: dev costs, exploitable bugs, regulatory difficulty, no community support, longer time to market. I've written about this exact pain before (it's literally why Cerbos exists). Hearing it from a Gartner analyst in front of a room full of enterprise security leaders is a different thing entirely. I had at least 3 conversations afterwards with security architects who've been burned by homegrown authorization logic that nobody wants to maintain.
Homan Farahmand's session on IAM for LLM-based AI agents was where the room really leaned in. 13% of banks and 16% of insurers have already deployed agents. Another 34% plan to within 12 months. And the authorization requirements he laid out are exactly the kind of thing that role-based access control can't handle.
Fine-grained access control. Context-aware decisions. Delegation of authority with human-in-the-loop flows. Rich authorization requests that carry enough context for a policy engine to make a good decision. That's 6 distinct authorization requirements, and every one of them points toward policy-based, attribute-driven authorization rather than static role assignments.
His architecture for MCP authorization is the part I keep coming back to. He described an in-line proxy where every MCP tool call flows through a PEP that queries a PDP. The PDP evaluates policy against signals and context, then returns a decision. This is exactly where Cerbos fits, authorizing calls If you squint, that's a Cerbos check call sitting between an agent and its tools. The principal is the agent (with its delegation chain). The resource is whatever the tool is accessing. The action is the tool call itself. The context is everything the PDP needs to make the decision: who delegated to this agent, what scopes were granted, what the agent has done so far in this session.
Farahmand listed AuthZEN as one of 4 emerging standards relevant to agent authorization. The others were OID4VC, SSF/CAEP, and SPIFFE. AuthZEN is the one that standardizes the actual authorization request and response between PEP and PDP. It's the protocol that makes it possible to swap out your policy engine or your enforcement point without rewriting your integration.
The hallway conversations after this session split into two camps: people whose organizations deployed agents and are now scrambling to retrofit IAM controls, and those watching from the sidelines because leadership pushed ahead without consulting the identity team. Neither group felt comfortable.
Erik Wahlstrom's Identity Fabric session gave the architectural framing that ties it all together. His Identity Fabric 2.0 placed AMP as its own tool category in the IAM honeycomb, alongside IGA, PAM, AM, and ITDR. That's a significant shift. Authorization isn't a checkbox inside your access management platform. It's its own category of infrastructure.
He mapped AuthZEN on a standards maturity chart. It's early (low adoption, still evolving) but sits on the same trajectory as OAuth 2.0 and OpenID Connect, which are now established and pervasive. The pattern is familiar: a standard emerges, early adopters prove it out, and then it becomes table stakes. We're in the early adopter phase for AuthZEN, and the Cerbos PDP already supports it.
Wahlstrom's maturity model puts most of the industry between L1 (Integrated) and L2 (Interoperable). The move to interoperability requires standards. You can't build a composable identity fabric if your authorization engine speaks a proprietary protocol that nothing else understands. This is why we've always built Cerbos around open standards and open policy formats. Policies as code, stored in git, evaluated by a stateless PDP, enforced wherever you need it. That architecture was designed for interoperability from day one.
Nathan Harris drew the clearest line of the conference. His fit-for-purpose test scored authorization as red (not fit for AI) because it requires deterministic decisions and real-time performance. His quote: "Agentic AI could be used to improve access policies or provide insights used by access control, but NOT to make runtime access control decisions."
This felt like the session a lot of people needed. There's a gravitational pull right now to throw AI at every problem, partly because boards are asking "where's our AI strategy?" and partly because vendors are packaging everything as AI-powered. Harris gave identity teams a framework to push back: AI helps upstream (analyzing access patterns, modeling better policies, finding over-provisioning) but the runtime decision stays deterministic.
That maps to something I think about a lot. The value of AI in authorization isn't in making the yes/no decision. It's in helping you write better policies in the first place. Analyze your access logs, find the patterns, suggest tighter scopes, identify the permissions nobody uses. Then encode those insights as policies that a deterministic engine enforces consistently, every time, at millisecond latency. AI makes the policies smarter. The PDP makes the decisions.
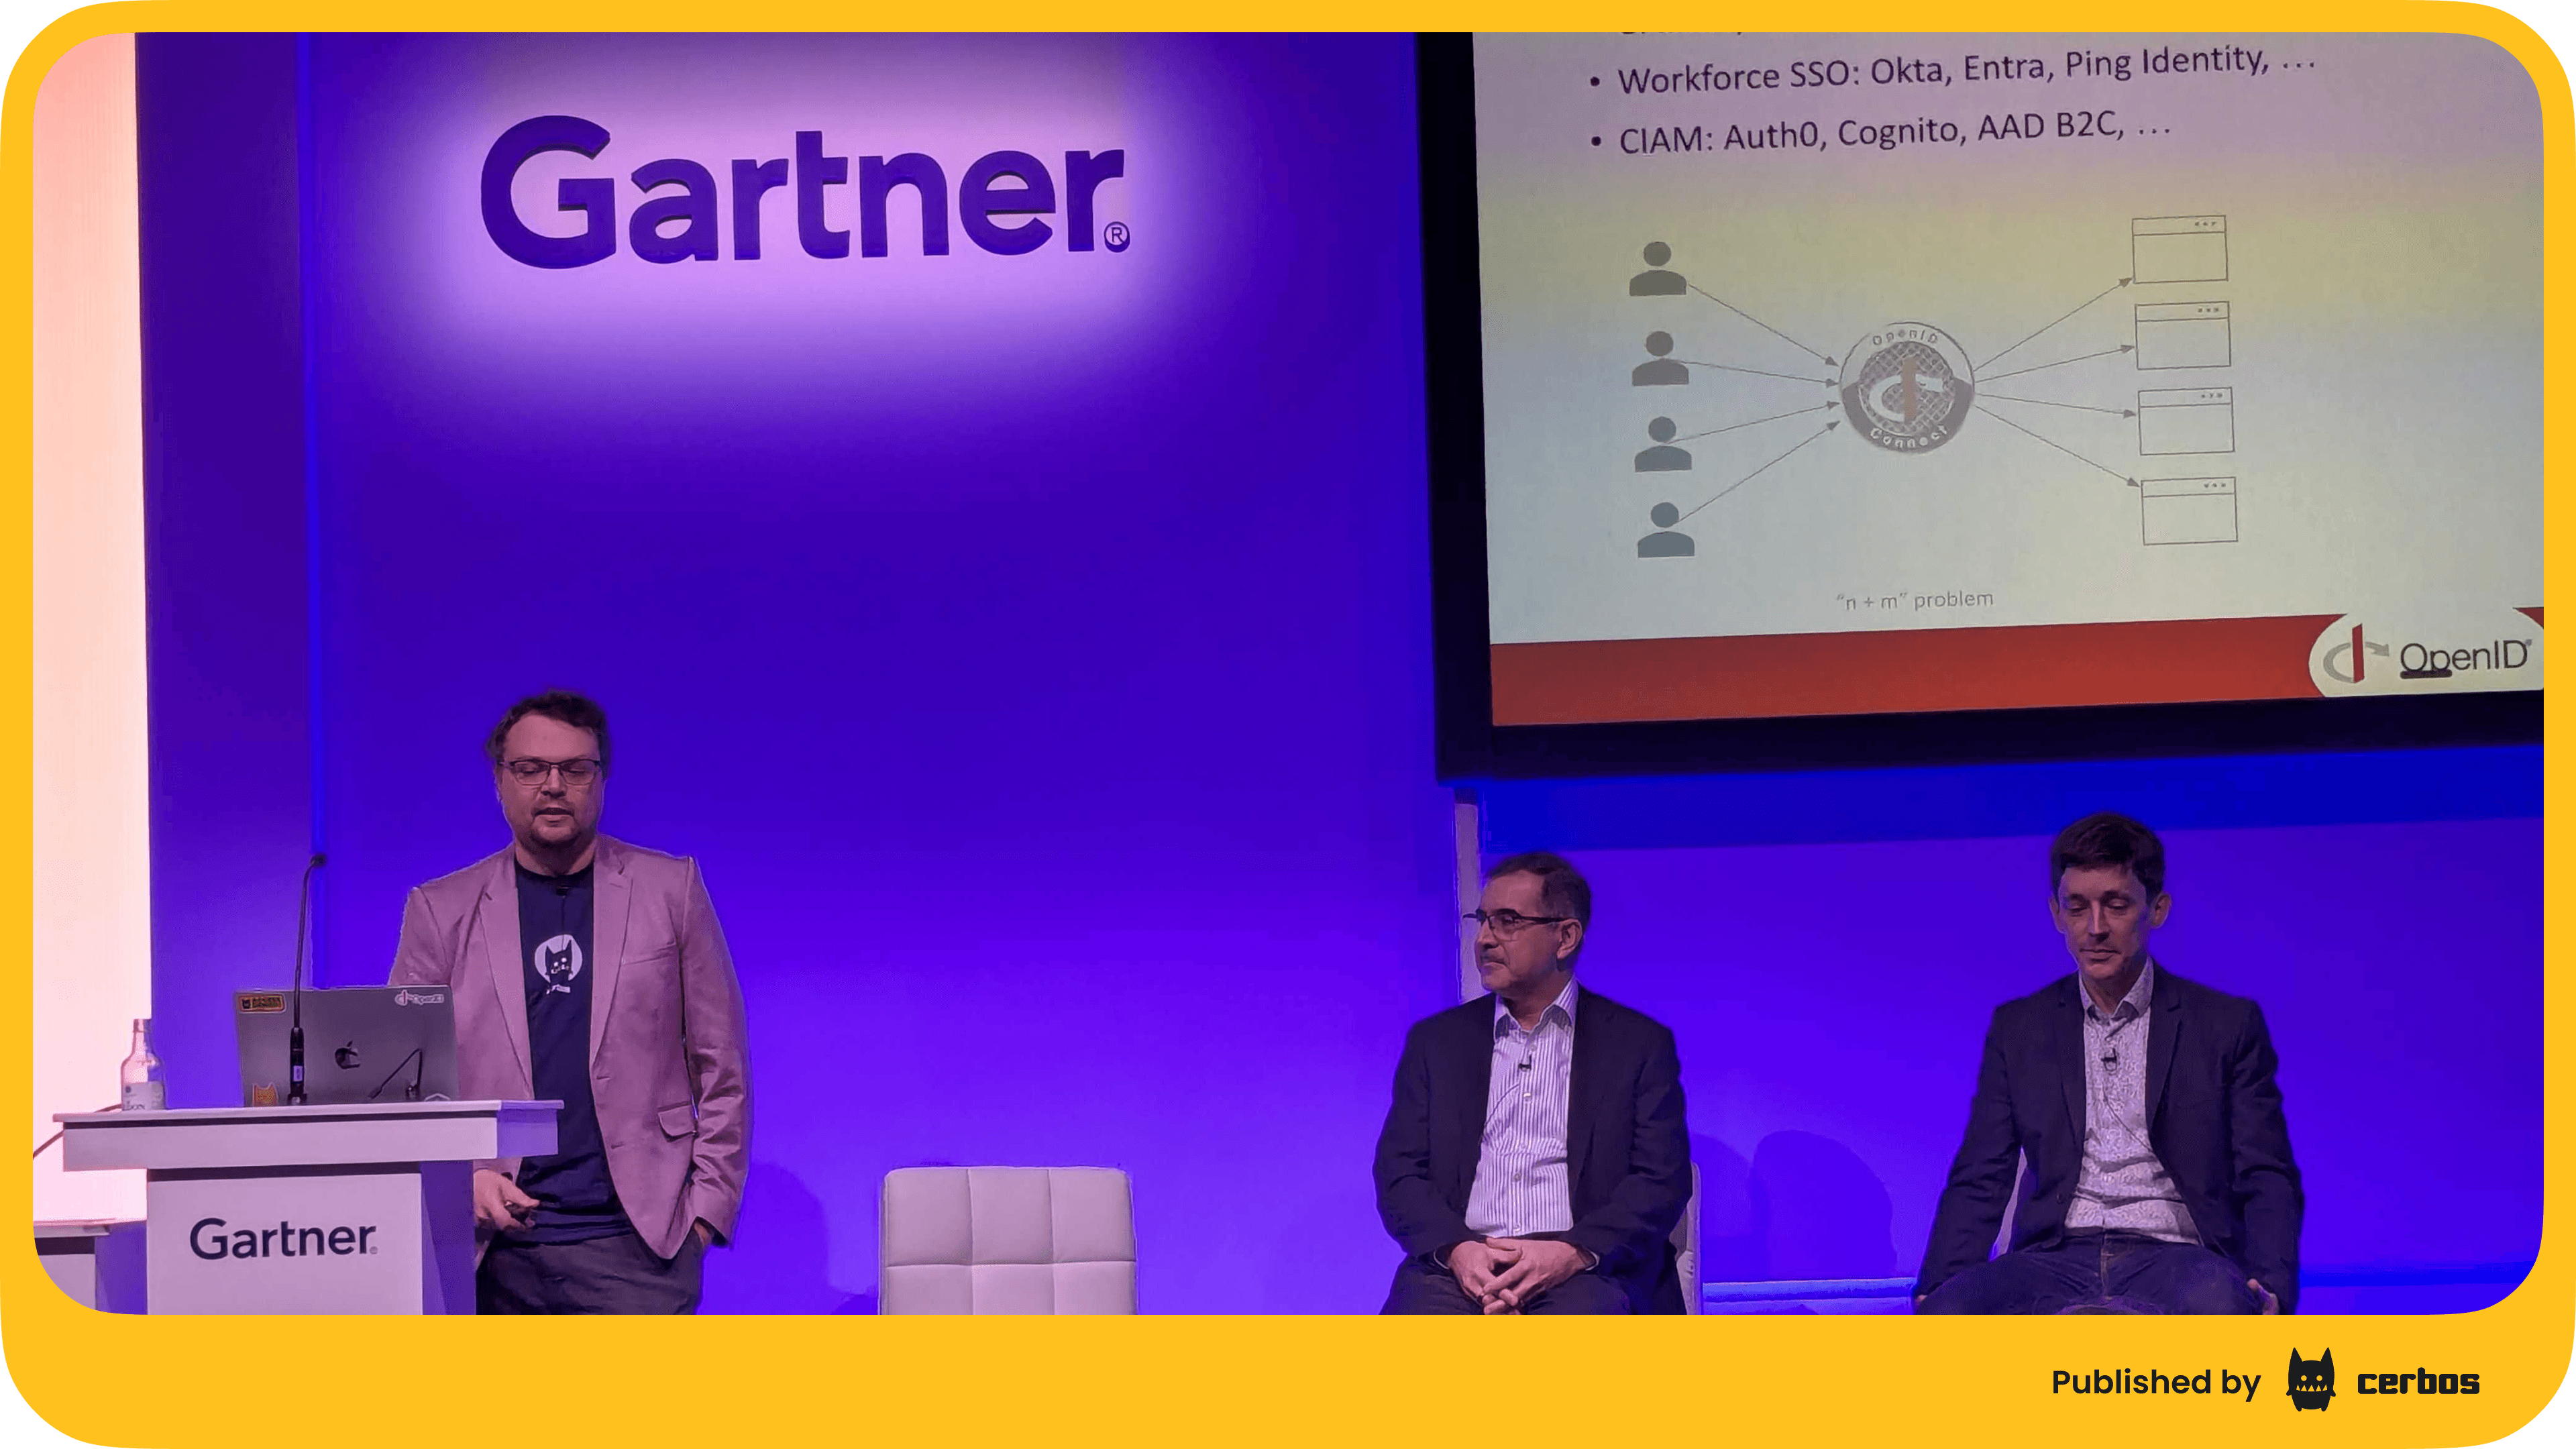
I was at the conference in a second capacity too. Alongside my co-chair, David Brossard, and Homan Farahmand, we presented an update on the latest AuthZEN spec and the working group's progress. I also gave a demo of the IdP interop, showing how different authorization engines can speak the same protocol and produce consistent results across implementations.
The audience questions were practical, not theoretical. People wanted to know how AuthZEN handles the kind of context-rich requests that agent authorization demands, how it fits with their existing identity providers, and what real-world adoption looks like. A year ago, those conversations were "what is this and why should I care?" Now they're "how do I implement this and who else is doing it?" That's a meaningful shift.
Presenting alongside Farahmand was particularly interesting given his earlier session on agent IAM. The MCP proxy pattern he described, where a PEP queries a PDP for every tool call, is exactly the kind of integration AuthZEN was designed for. Seeing the spec work and the analyst research converge in the same week, at the same conference, made the trajectory feel concrete rather than aspirational.
Mezzera's second session drove home the data: more than 95% of identities use less than 3% of their granted cloud entitlements, and AI agents are now explicitly in scope as privileged users. Nat Krishnan named runtime authorization as a distinct layer (L4) in a 5-layer IAM stack, above PAM. Tarun Rohilla quantified the market: AI-borne threats up 200% year-over-year, and through 2028, over 50% of AI initiatives will halt due to unresolved agentic identity challenges.
That last prediction came up in every hallway conversation I had on the final day. The pattern is consistent: the board has bought into AI, budget is flowing, agents are being built or bought, and the identity team found out somewhere between "proof of concept" and "we're going live next month." The work to figure out who these agents are, what they can access, how to govern delegation chains, and how to audit their behavior has landed on teams already stretched thin. Authorization is where most of them are getting stuck.
Across 7 presentations from 6 Gartner analysts, and from the conversations I had presenting the spec and demoing interop, the same pattern emerged. Authorization is its own infrastructure layer. It requires its own tooling. It demands interoperability standards. AuthZEN keeps showing up at the PDP-to-PEP integration point.
Mezzera's AMP architecture. Wahlstrom's standards assessment. Farahmand's agent IAM standards. 3 independent analysts, 3 sessions, same standard.
For us at Cerbos, this conference confirmed what we've been building toward. A stateless, standards-based PDP that evaluates context-rich authorization requests and returns deterministic decisions. Policies as code that can be versioned, tested, and audited. An architecture where the PDP sits wherever the enforcement point needs it, whether that's in front of an API, inside a service, or between an agent and its tools via MCP.
The orgs that build this authorization layer now will ship agents faster. The ones that don't will be in that 50% whose AI initiatives stall because they couldn't solve the identity and authorization problem.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。