





AI agents + private keys is not innovation. It is operational debt with a liquidation timer.
A single hallucination can misprice a swap. A single stale RPC can poison an intent. A single unsafe action can turn a product demo into a post-mortem.
That is the problem Lirix was built to solve.
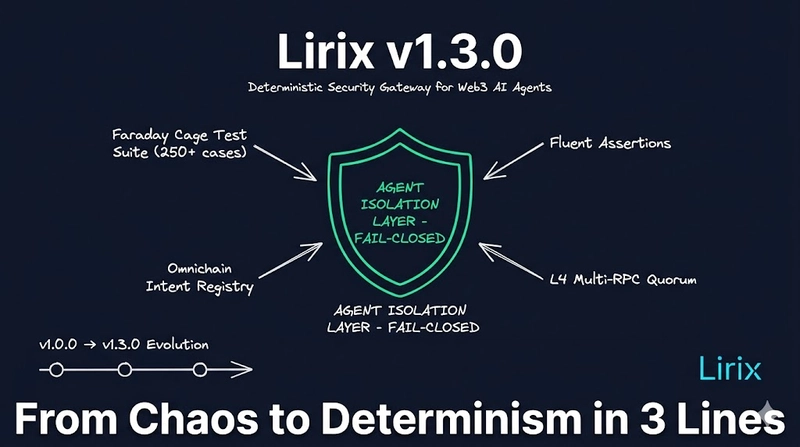
Today, we are launching Lirix v1.3.0 — the release that turns Lirix from a simple proxy into a deterministic security gateway for Web3 AI agents.
If v1.0.0 was the prototype, v1.2.0 was the hardening, then v1.3.0 is the moment the architecture becomes a real system:
AI can propose.
Lirix decides.
Your app signs only when the outcome is provably safe.
This is the technical retrospective from v1.0.0 → v1.3.0.
Why this exists
The current AI stack is incredibly good at producing plausible actions. That is exactly why it is dangerous.
Web3 does not forgive plausibility. It rewards determinism.
In Web3, an “almost correct” action is often the same thing as a loss:
a stale quote becomes MEV bait,
a honeypot token drains your balance,
a hidden tax token breaks execution assumptions,
a mismatched RPC state causes the agent to act on a false world.
Lirix was designed around a simple belief:
Security should not be inferred after execution. It should be proven before execution.
That belief shaped every release.
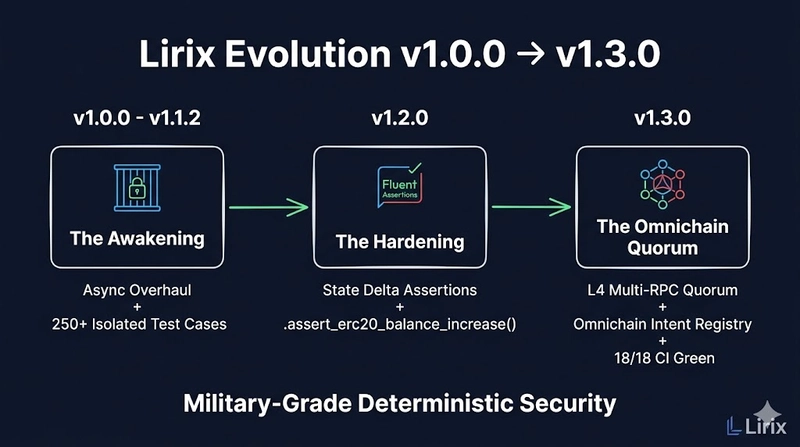
v1.0.0 → v1.1.2: Building the Faraday Cage
The first phase was about creating the boundary.
We wanted an environment where an agent could explore, simulate, and reason — without ever leaking into the live network during validation.
1. The async overhaul
Early on, we hit a classic Web3 bottleneck: eth_call deadlocks under concurrency.
That may sound like a small engineering issue. It is not.
For agentic systems, deadlocks are more than latency bugs. They destroy the trust model. If the validator cannot keep up with the agent, the system becomes non-deterministic under load.
So we rebuilt the async execution path to handle high-concurrency intent execution without flinching.
The result:
fewer race conditions,
cleaner request orchestration,
and a validation layer that behaves like infrastructure, not a best-effort helper.
2. The isolated test baseline
Security tools fail quietly when their test environments are porous.
So we built a 100% isolated Faraday Cage test suite with 250+ cases.
The goal was not just coverage. The goal was containment.
We wanted confidence that:
nothing accidentally touches the live net,
simulations remain deterministic,
and validation logic can be trusted under repeated execution.
This was the foundation. Without it, everything else would have been theater.
v1.2.0: State Delta Assertions
By v1.2.0, the question changed.
It was no longer enough to ask, “Can we simulate this?” The real question became:
Can we prove that the simulated outcome is the outcome we actually want?
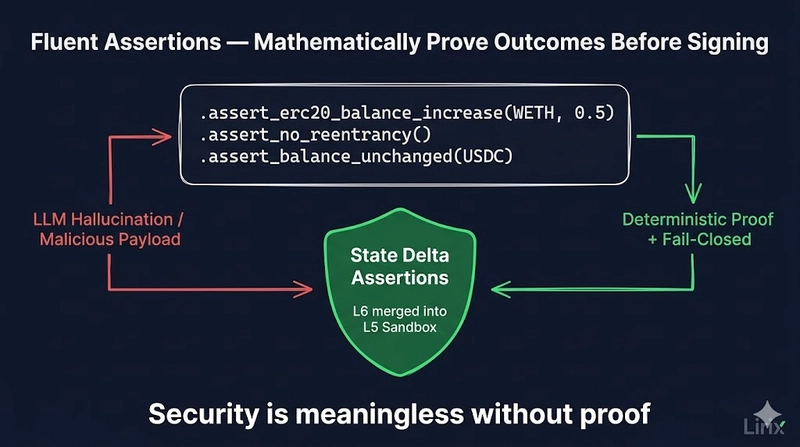
That is where state delta assertions changed the game.
The core idea
Instead of validating only that a transaction “looks valid,” Lirix began validating what changes after execution.
That means the system can reason about:
token balance deltas,
expected asset movement,
and whether the result matches the intent.
The killer feature
This is where fluent assertions like:
.assert_erc20_balance_increase()and other outcome-based checks
became foundational.
Why that matters:
A malicious token can pass superficial checks and still steal value. A honeypot can look liquid and still trap the user. A 100% tax token can make an execution technically succeed while economically failing.
Lirix v1.2.0 introduced a different standard:
If the state delta is wrong, the transaction is wrong.
That means Lirix can fail closed by default before a bad action is signed.
Not after.
Before.
That is the difference between a convenience layer and a security boundary.
v1.3.0: The Omnichain Quorum
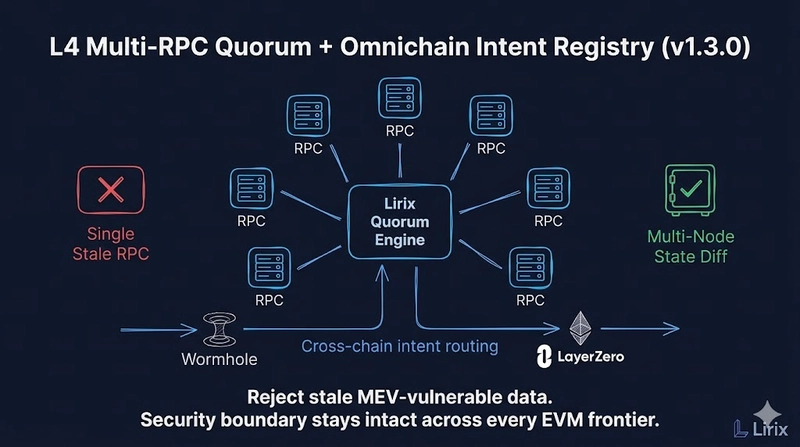
If v1.2.0 was about proving outcomes, v1.3.0 is about proving reality.
Because one of the biggest risks in agentic Web3 is not bad logic. It is bad state.
A single RPC endpoint can lie by omission. A stale node can hand you a false world model. An agent that trusts one source too much becomes easy prey for MEV and latency games.
1. L4 multi-RPC quorum
Lirix v1.3.0 introduces a multi-RPC quorum layer.
Instead of trusting a single node, Lirix gathers state from multiple sources concurrently and diffs the responses.
This does two things:
it reduces reliance on stale reads,
and it hardens the agent against MEV-sensitive misinformation.
That matters because in a fast-moving onchain environment, the state you see is often the attack surface.
Lirix now treats read consistency as a security primitive.
2. Omnichain intent registry
Lirix v1.3.0 also lays the groundwork for cross-chain intent routing.
Why does that matter?
Because the future of Web3 is not single-chain. It is multi-domain, multi-router, and increasingly cross-chain by default.
We built the foundation for intent routing across systems like:
Wormhole,
LayerZero,
and other omnichain pathways,
while preserving the security boundary that makes Lirix useful in the first place.
In plain English:
Cross-chain flexibility should not mean cross-chain chaos.
3. Universal compatibility
Security infrastructure is only useful if it actually ships.
So v1.3.0 achieved 18/18 CI green across:
Python 3.9 → 3.14,
Ubuntu,
macOS,
and Windows.
That may sound boring. It is not.
For protocol infrastructure, cross-platform reliability is part of the trust surface. If the tool behaves differently across environments, the security model is already weaker than it should be.
The Lirix Triple-Zero Standard
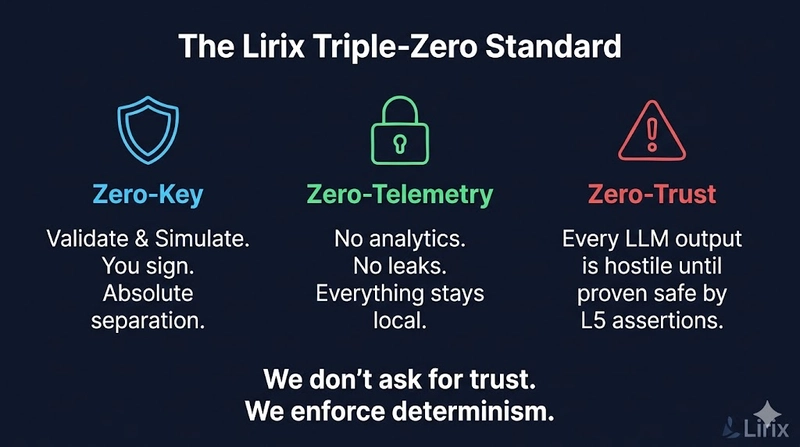
We do not ask for trust. We design for minimized trust assumptions.
That is the philosophy behind the Triple-Zero Standard:
1. Zero-Key
Lirix does not take custody of your private keys. It validates and simulates. Your app signs. The separation is absolute.
This is crucial. The moment the security layer becomes the key holder, the architecture changes from protection to privilege concentration.
2. Zero-Telemetry
No analytics. No hidden operational leakage. No unnecessary surface area.
Your workflow stays local by default. That is not just a privacy preference — it is an attack-surface reduction strategy.
3. Zero-Trust
Every LLM output is treated as untrusted until it is proven safe.
This is the principle most teams claim to follow and few actually implement. Lirix implements it in the most practical way possible:
simulate,
verify,
assert,
and only then allow execution.
That is what makes the system deterministic.
From chaos to determinism in 3 lines
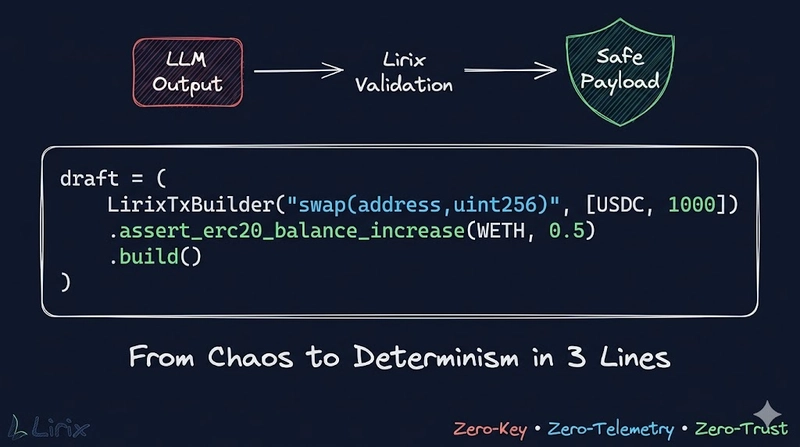
Sometimes the best way to understand a system is to see it in motion.
draft = (
    LirixTxBuilder("swap(address,uint256)", [USDC, 1000])
    # Prove the outcome or revert.
    .assert_erc20_balance_increase(WETH, 0.5)
    .build()
)
That is the entire philosophy in miniature:
the agent proposes an action,
the system verifies the expected state change,
and the transaction only survives if the result is mathematically acceptable.
In a space full of “smart” abstractions, this is intentionally blunt. Because security should feel boring when it works.
What this means for builders
If you are building on:
LangChain,
AutoGen,
a custom agent stack,
or any workflow where an LLM can influence onchain actions,
then your biggest risk is not that the model is wrong. It is that the model is confidently wrong at scale.
Lirix exists to make that failure mode survivable.
It gives you:
deterministic validation,
state-aware assertions,
multi-source state checking,
and a clean boundary between reasoning and signing.
That boundary is the product.
Final verdict
The Web3 AI era is here. So is the Dark Forest.
And the gap between them is not hype. It is engineering.
Lirix v1.3.0 is our answer to that gap:
a security gateway built for AI agents,
a deterministic execution boundary for Web3,
and a framework for proving safety before value moves.
If your agent is going to touch private keys, then “probably safe” is not a strategy.
Determinism is the strategy.
Get started
Install:
pip install lirixGitHub:
lokii-D/lirix
If you are building in the open and shipping agentic Web3 systems, I would love to hear how you are approaching deterministic execution, simulation, and state verification.
Tags
#Web3 #AI #Security #Ethereum #DevOps #Python #DeFi #Hashnode #Developers