








How VeilShift™ Works — The Protocol That Bypasses DPI Blocking
If you've ever tried using a VPN in Turkey, UAE, or Indonesia and found it suddenly stopped working, you've run into Deep Packet Inspection. This article explains what DPI is, why it defeats most commercial VPNs, and how VeilShift™ approaches the problem differently.
What is Deep Packet Inspection?
Deep Packet Inspection (DPI) is a method ISPs and governments use to analyze internet traffic in real time — not just where it's going, but what it looks like at the packet level.
Traditional firewalls only check headers (source IP, destination IP, port). DPI goes further: it inspects the actual content and structure of packets to identify the protocol being used.
This is how ISPs in Turkey can block WireGuard without blocking all of port 443. They don't need to know your destination — they just recognize the traffic pattern.
Why Standard VPN Protocols Fail
WireGuard, OpenVPN, and even standard IKEv2 all have recognizable signatures:
- WireGuard has a distinctive UDP handshake pattern. A single packet is enough to identify it.
- OpenVPN has a recognizable TLS certificate pattern and packet timing.
- IKEv2 uses well-known ports (500, 4500) that are trivial to block.
The result: ISPs in censored countries maintain blocklists that get updated faster than VPN providers can respond. A VPN that works today may be blocked next week.
The Four Layers of DPI Detection
To understand VeilShift™, it helps to understand what DPI systems actually check:
Protocol signature — Does the traffic match a known VPN protocol's byte pattern?
TLS fingerprint — What does the TLS handshake look like? Different clients (browsers, VPN apps) produce different fingerprints. A VPN app's fingerprint doesn't look like Chrome's.
Traffic pattern analysis — VPN traffic has predictable timing, packet sizes, and flow characteristics. Even encrypted traffic can be identified statistically.
Packet size distribution — Machine learning models can classify traffic by packet size patterns even without decrypting it.
Most VPN obfuscation methods address one or two of these layers. VeilShift™ addresses all four simultaneously.
How VeilShift™ Works
VeilShift™ is built on a stack of four components:
VLESS + XHTTP + Reality
VLESS is a lightweight proxy protocol with no encryption overhead of its own — it delegates encryption to TLS. XHTTP carries it over standard HTTPS. Reality is the key innovation: instead of using a self-signed certificate that screams "VPN," it borrows the TLS certificate of a legitimate high-traffic website. To any inspection system, the handshake looks like a connection to that website.
Result: protocol signature layer — defeated.
uTLS with Chrome fingerprint
uTLS is a library that allows precise control over TLS fingerprint. VeilShift™ uses it to produce a TLS handshake that is byte-for-byte identical to what Chrome produces. Not "similar to" — identical.
Result: TLS fingerprint layer — defeated.
xPaddingBytes
xPaddingBytes normalizes packet sizes by adding randomized padding. This disrupts the statistical patterns that ML-based DPI systems use to classify traffic by size distribution.
Result: packet size distribution layer — defeated.
HTTPS traffic pattern
Because the entire stack runs over port 443 as standard HTTPS, the traffic timing and flow characteristics match normal web browsing.
Result: traffic pattern layer — defeated.
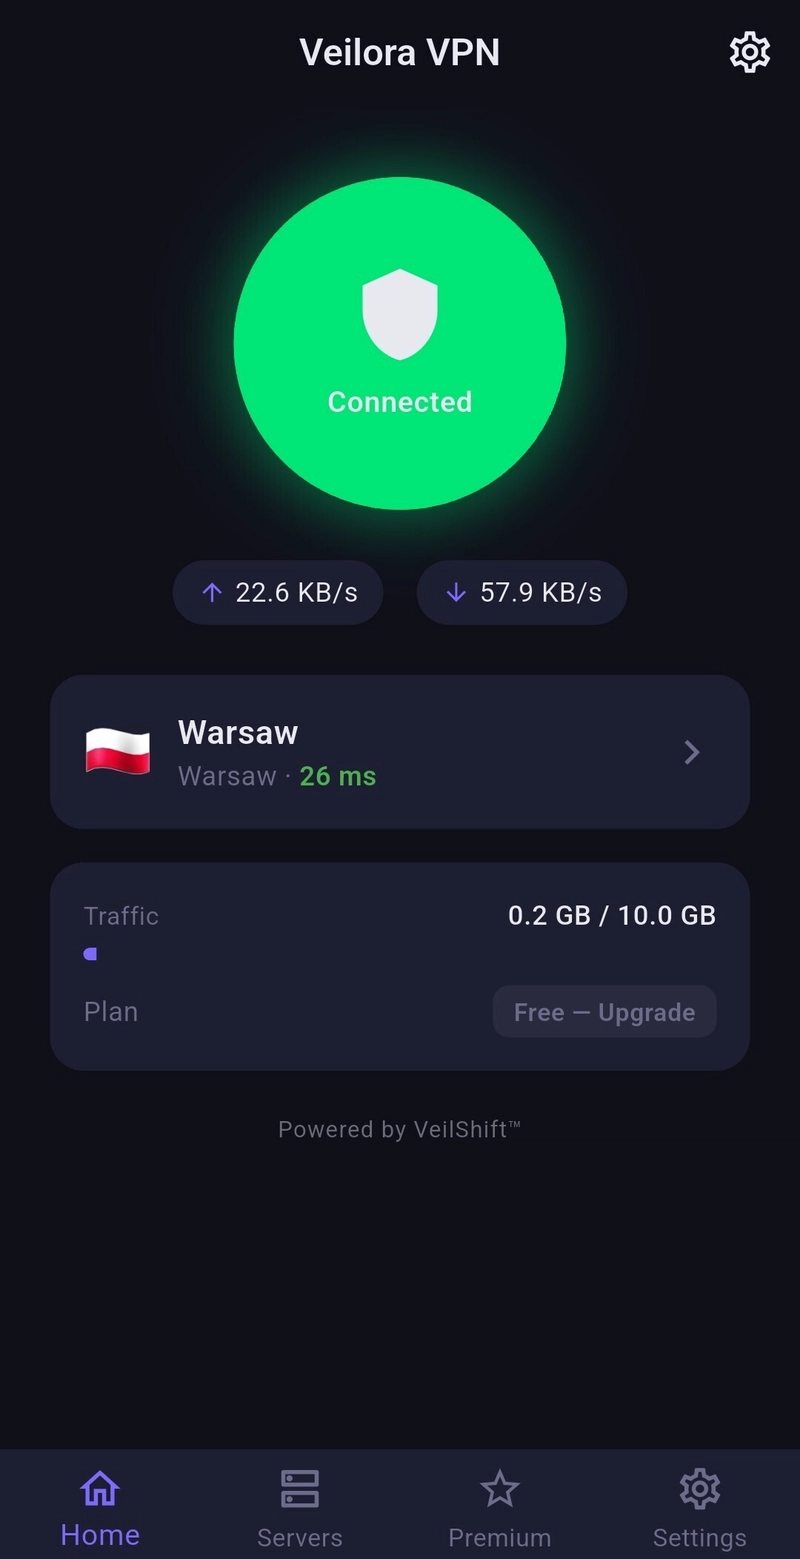
Veilora connected to Warsaw — 26ms latency, powered by VeilShift™
What This Looks Like to an ISP
When a Veilora user in Turkey connects, the ISP sees a TLS 1.3 connection to what appears to be a major website, a Chrome browser fingerprint, standard HTTPS traffic patterns, and normal packet size distribution. There is no VPN fingerprint to detect. The only way to block this traffic is to block all HTTPS — which would take down the entire web.
Server Network
Every Veilora server runs VeilShift™ — there's no "obfuscated mode" to toggle on. It's the default.
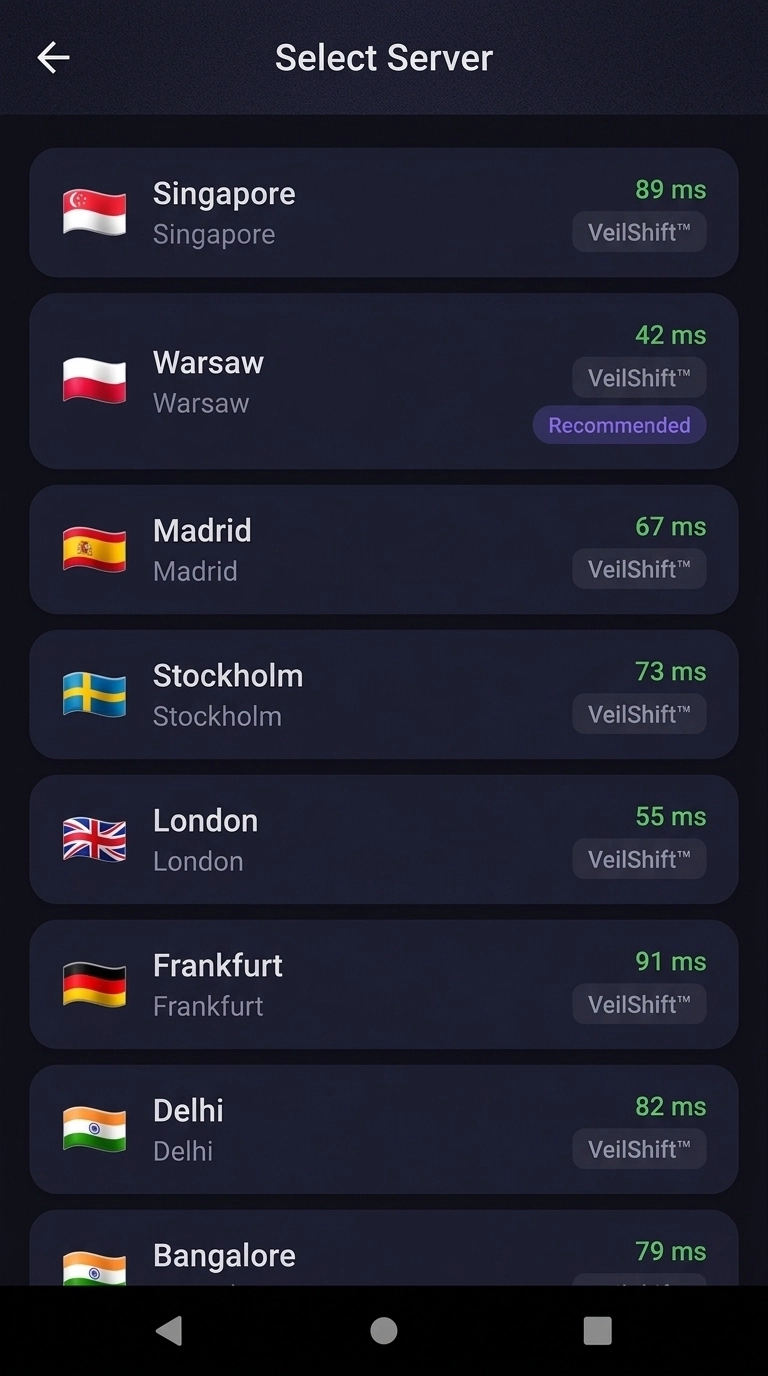
All servers run VeilShift™ protocol
Pricing
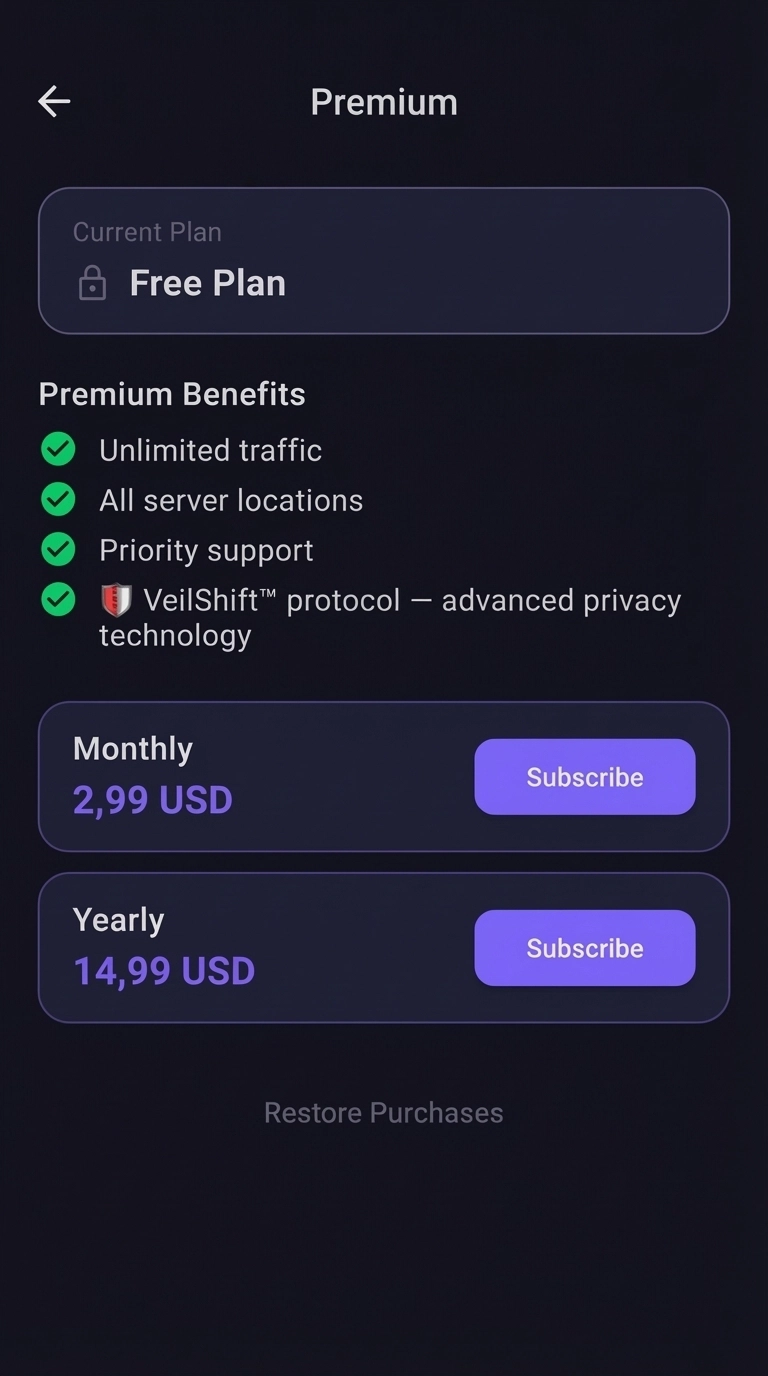
Free plan — 10 GB/month, no email or card required
Monthly: $2.99 | Yearly: $14.99 ($1.25/month)
Kill Switch & Settings
Connection protection doesn't stop at the protocol level. If the VPN drops for any reason, Kill Switch cuts all traffic instantly — your real IP is never exposed.
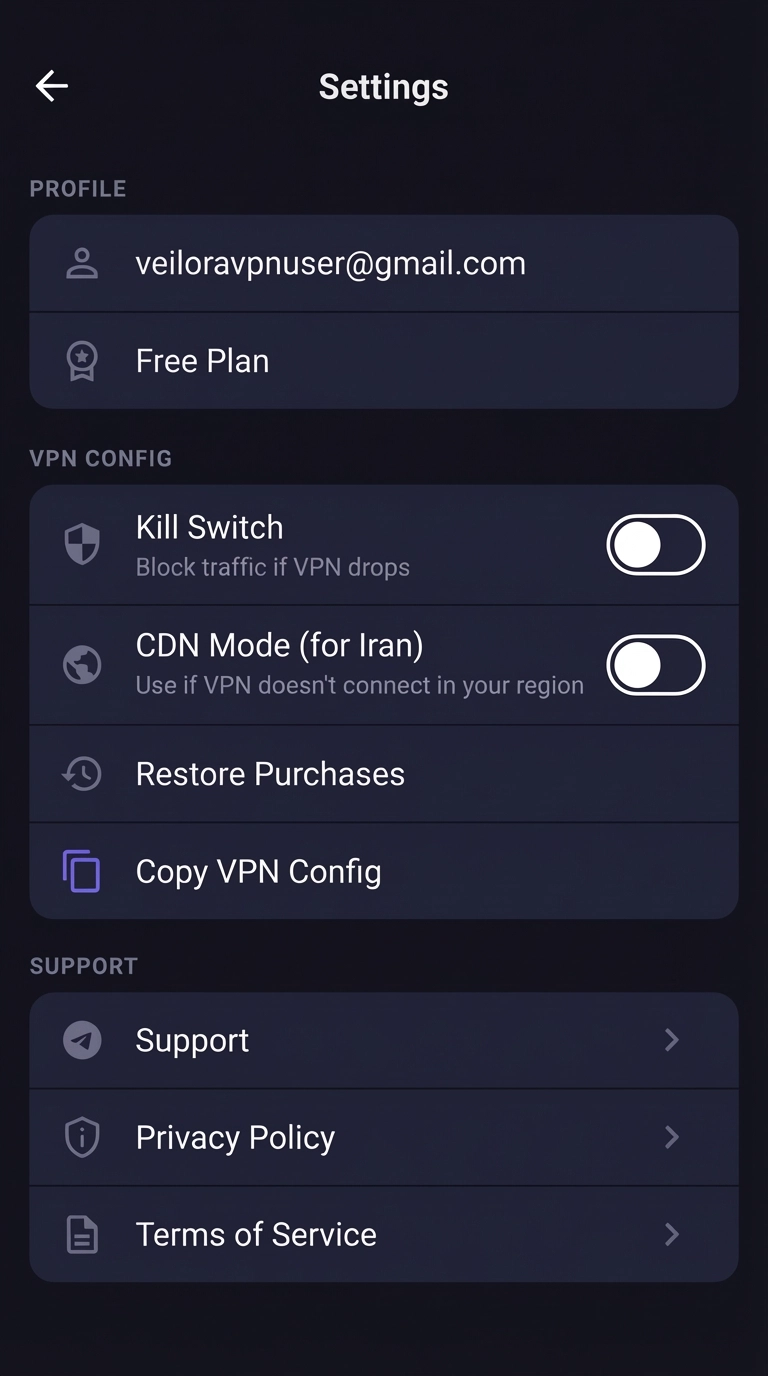
Kill Switch included on all plans
The Practical Result
VeilShift™ maintains a 99% success rate in Turkey and 97% in UAE — markets where NordVPN and ExpressVPN regularly fail. This isn't a claim about server count or speed. It's a claim about protocol architecture.
Try It
Veilora is available at veilora.net. Free plan is 10 GB/month — no email, no card required. The web dashboard works directly in your browser without installing an app.
If you're in a region where standard VPNs have stopped working, this is why — and this is the fix.