


Version 1.0.0
File modification detection sounds simple until you realise that timestamps can be forged, file sizes can stay identical while content changes, and simple diff tools often miss what matters most: the actual bytes.
If you work in IT security, digital forensics, compliance, or system administration, you need a way to verify file integrity that goes deeper than metadata. In this tutorial, you'll build a PowerShell script that creates cryptographic hash baselines of directories and detects modifications that other tools miss.
The Problem with Simple File Comparison
Most file comparison tools check three things:
- File name
- File size
- Timestamp (created/modified)
An attacker with filesystem access can modify all three. A legitimate user editing a document might change content while the file size stays identical. A script running with admin privileges can alter files and reset timestamps to cover its tracks.
What doesn't lie: the cryptographic hash. Change a single bit in a multi-gigabyte file, and the SHA-256 hash changes completely.
What You'll Build
A PowerShell script called hash_verifier.ps1 with two modes:
Generate mode: Scans a directory, computes SHA-256 hashes for every file, and writes a baseline manifest to a timestamped .txt file.
Verify mode: Re-scans the same directory, compares current hashes against the baseline, and flags any files that have been modified, deleted, or added.
Prerequisites
- PowerShell 5.1 or later (built into Windows 10 and above)
- No external modules required - uses built-in
Get-FileHashcmdlet - Read access to the directory you want to monitor
How It Works
The script uses PowerShell's Get-FileHash cmdlet, which computes cryptographic hashes using the SHA-256 algorithm. For each file in the target directory, it calculates a 256-bit hash value that uniquely represents that file's content.
Generate mode workflow:
- Scan the directory (optionally recursing into subdirectories)
- Compute SHA-256 hash for each file
- Write hashes + file paths to a baseline manifest file
- Store the manifest somewhere safe
Verify mode workflow:
- Load the baseline manifest
- Re-scan the directory and compute current hashes
- Compare current hashes against baseline hashes
- Report four categories: OK (unchanged), MISMATCH (modified), MISSING (deleted), NEW (added)
The Complete Script
Here's the full implementation:
# PowerShell File Hash Verifier
# Purpose: Generate hash baselines and detect file modifications
# Author: ShadowStrike (Strategos)
# License: MIT

param(
    [Parameter(Mandatory=$true)]
    [string]$Path,

    [Parameter(Mandatory=$true)]
    [ValidateSet("Generate","Verify")]
    [string]$Mode,

    [Parameter(Mandatory=$false)]
    [string]$Manifest = "",

    [Parameter(Mandatory=$false)]
    [string]$OutputDir = ".",

    [Parameter(Mandatory=$false)]
    [switch]$Recurse
)

# Ensure output directory exists
if (-not (Test-Path $OutputDir)) {
    New-Item -ItemType Directory -Path $OutputDir -Force | Out-Null
}

$timestamp = Get-Date -Format "yyyyMMdd_HHmmss"

function Get-FileHashMap {
    param([string]$DirectoryPath, [bool]$RecurseSubdirs)

    $hashMap = @{}

    $files = if ($RecurseSubdirs) {
        Get-ChildItem -Path $DirectoryPath -File -Recurse -ErrorAction SilentlyContinue
    } else {
        Get-ChildItem -Path $DirectoryPath -File -ErrorAction SilentlyContinue
    }

    foreach ($file in $files) {
        try {
            $hash = Get-FileHash -Path $file.FullName -Algorithm SHA256 -ErrorAction Stop
            $hashMap[$file.FullName] = $hash.Hash
        } catch {
            Write-Warning "Could not hash file: $($file.FullName)"
        }
    }

    return $hashMap
}

if ($Mode -eq "Generate") {
    Write-Host "[GENERATE MODE] Hashing files in: $Path" -ForegroundColor Cyan

    $hashMap = Get-FileHashMap -DirectoryPath $Path -RecurseSubdirs $Recurse

    $outputFile = Join-Path $OutputDir "HashVerifier_Generate_$timestamp.txt"

    $output = @()
    $output += "# Hash Baseline Generated: $(Get-Date)"
    $output += "# Path: $Path"
    $output += "# Recurse: $Recurse"
    $output += "# Total Files: $($hashMap.Count)"
    $output += ""

    foreach ($key in ($hashMap.Keys | Sort-Object)) {
        $line = "$($hashMap[$key])  $key"
        $output += $line
        Write-Host "[GENERATE] $key" -ForegroundColor Green
    }

    $output | Out-File -FilePath $outputFile -Encoding UTF8

    Write-Host "`n[COMPLETE] Manifest written to: $outputFile" -ForegroundColor Green
    Write-Host "[INFO] Use this file as -Manifest parameter in Verify mode" -ForegroundColor Yellow

} elseif ($Mode -eq "Verify") {
    if (-not $Manifest -or -not (Test-Path $Manifest)) {
        Write-Error "Verify mode requires a valid -Manifest file path"
        exit 1
    }

    Write-Host "[VERIFY MODE] Comparing current state against: $Manifest" -ForegroundColor Cyan

    # Load baseline hashes
    $baselineMap = @{}
    $manifestLines = Get-Content $Manifest | Where-Object { $_ -notmatch '^#' -and $_.Trim() -ne '' }

    foreach ($line in $manifestLines) {
        if ($line -match '^([A-F0-9]{64})\s{2}(.+)$') {
            $baselineMap[$matches[2]] = $matches[1]
        }
    }

    Write-Host "[INFO] Baseline contains $($baselineMap.Count) files" -ForegroundColor Yellow

    # Get current hashes
    $currentMap = Get-FileHashMap -DirectoryPath $Path -RecurseSubdirs $Recurse

    Write-Host "[INFO] Current directory contains $($currentMap.Count) files`n" -ForegroundColor Yellow

    $outputFile = Join-Path $OutputDir "HashVerifier_Verify_$timestamp.txt"
    $output = @()
    $output += "# Hash Verification Run: $(Get-Date)"
    $output += "# Baseline: $Manifest"
    $output += "# Path: $Path"
    $output += ""

    $okCount = 0
    $mismatchCount = 0
    $missingCount = 0
    $newCount = 0

    # Check for matches and mismatches
    foreach ($filePath in ($baselineMap.Keys | Sort-Object)) {
        if ($currentMap.ContainsKey($filePath)) {
            if ($currentMap[$filePath] -eq $baselineMap[$filePath]) {
                Write-Host "[OK]       $filePath" -ForegroundColor Green
                $output += "[OK] $filePath"
                $okCount++
            } else {
                Write-Host "[MISMATCH] $filePath" -ForegroundColor Red
                Write-Host "           Expected : $($baselineMap[$filePath])" -ForegroundColor Gray
                Write-Host "           Found    : $($currentMap[$filePath])" -ForegroundColor Gray
                $output += "[MISMATCH] $filePath"
                $output += "           Expected : $($baselineMap[$filePath])"
                $output += "           Found    : $($currentMap[$filePath])"
                $mismatchCount++
            }
        } else {
            Write-Host "[MISSING]  $filePath" -ForegroundColor Magenta
            $output += "[MISSING] $filePath"
            $missingCount++
        }
    }

    # Check for new files
    foreach ($filePath in ($currentMap.Keys | Sort-Object)) {
        if (-not $baselineMap.ContainsKey($filePath)) {
            Write-Host "[NEW]      $filePath" -ForegroundColor Yellow
            $output += "[NEW] $filePath"
            $output += "           Hash: $($currentMap[$filePath])"
            $newCount++
        }
    }

    $output += ""
    $output += "# Summary"
    $output += "# OK:       $okCount"
    $output += "# MISMATCH: $mismatchCount"
    $output += "# MISSING:  $missingCount"
    $output += "# NEW:      $newCount"

    $output | Out-File -FilePath $outputFile -Encoding UTF8

    Write-Host "`n[SUMMARY]" -ForegroundColor Cyan
    Write-Host "  OK:       $okCount" -ForegroundColor Green
    Write-Host "  MISMATCH: $mismatchCount" -ForegroundColor Red
    Write-Host "  MISSING:  $missingCount" -ForegroundColor Magenta
    Write-Host "  NEW:      $newCount" -ForegroundColor Yellow
    Write-Host "`n[COMPLETE] Report written to: $outputFile" -ForegroundColor Green
}
Troubleshooting: Execution Policy
If you see this error when first running the script:
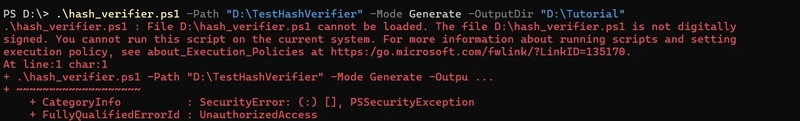
.\hash_verifier.ps1 : File D:\hash_verifier.ps1 cannot be loaded. The file
D:\hash_verifier.ps1 is not digitally signed. You cannot run this script on
the current system.
This is PowerShell's execution policy blocking unsigned scripts. Fix it with these steps:
Step 1: Set RemoteSigned Policy
Set-ExecutionPolicy -ExecutionPolicy RemoteSigned -Scope CurrentUser

This allows locally-created scripts to run without digital signatures, while still requiring signatures for scripts downloaded from the internet.
Check your current policy:
Get-ExecutionPolicy -List
You should see CurrentUser showing RemoteSigned.
Step 2: Unblock the File (If Still Blocked)
If you still get the error even with RemoteSigned policy set, the file has been marked as "downloaded from the internet" by Windows. This happens when you download scripts from GitHub, copy files from certain locations, or create them with some text editors.
Unblock the file:
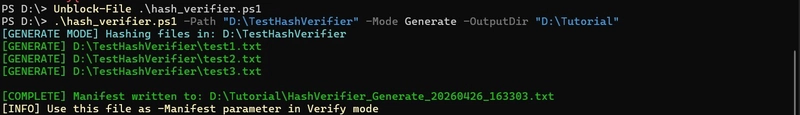
Unblock-File .\hash_verifier.ps1
Why this happens: Windows tags downloaded files with Zone.Identifier metadata. Even with RemoteSigned policy, Windows blocks these files unless they're digitally signed OR explicitly unblocked. The Unblock-File cmdlet removes this metadata flag.
Alternative: Bypass for Single Run (No Permanent Changes)
powershell -ExecutionPolicy Bypass -File .\hash_verifier.ps1 -Path "C:\ImportantFiles" -Mode Generate -OutputDir "C:\Baselines"
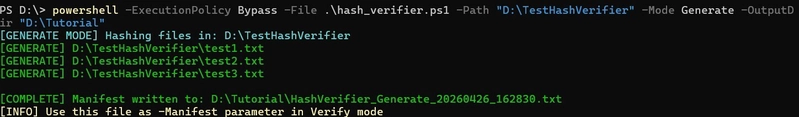
Good for one-off testing without changing system settings or unblocking files.
Security Note: Why This Script Isn't Digitally Signed
This script is deliberately not digitally signed. Here's why:
Code signing certificates cost $200-500/year from Certificate Authorities and require annual renewal. For open-source scripts where you can read the source code, transparency is more valuable than blind trust in a signature.
Before running ANY PowerShell script (including this one), you should:
- Read the entire script — understand what it does, line by line
- Verify the logic — does it do what it claims and nothing else?
- Check for suspicious behaviour — network calls, registry modifications, file deletions outside stated scope
This is the ABC principle from British policing and serious crime investigation — formally codified in the ACPO Murder Investigation Manual (1998):
- Assume nothing
- Believe nothing
- Check everything
A digital signature only tells you WHO wrote the code, not WHETHER the code is safe. You are the final verification step. Never execute code you haven't read and understood, regardless of where it came from or who signed it.
How to Use It
Step 1: Generate a Baseline
.\hash_verifier.ps1 -Path "C:\ImportantFiles" -Mode Generate -OutputDir "C:\Baselines"
This scans C:\ImportantFiles, computes SHA-256 hashes for every file, and writes the baseline to something like C:\Baselines\HashVerifier_Generate_20260424_153045.txt.
With recursion:
.\hash_verifier.ps1 -Path "C:\ImportantFiles" -Mode Generate -OutputDir "C:\Baselines" -Recurse
The -Recurse switch includes all subdirectories.
Step 2: Verify Against the Baseline
Wait some time (hours, days, weeks), then re-run in Verify mode:
.\hash_verifier.ps1 -Path "C:\ImportantFiles" -Mode Verify -Manifest "C:\Baselines\HashVerifier_Generate_20260424_153045.txt" -OutputDir "C:\Reports"
The script compares the current state against the baseline and writes a verification report to C:\Reports\HashVerifier_Verify_[timestamp].txt.
Understanding the Output
Generate mode writes a baseline file like this:
# Hash Baseline Generated: 24/04/2026 15:30:45
# Path: C:\ImportantFiles
# Recurse: False
# Total Files: 15

A1B2C3D4E5F6...  C:\ImportantFiles\document.docx
FF00AA11BB22...  C:\ImportantFiles\spreadsheet.xlsx
Each line contains a 64-character SHA-256 hash followed by the full file path.
Verify mode produces colour-coded console output:
-
[OK](green) - File unchanged -
[MISMATCH](red) - Hash doesn't match baseline (file modified) -
[MISSING](magenta) - File was in baseline but no longer exists -
[NEW](yellow) - File exists now but wasn't in baseline
The verification report file contains the same information plus a summary count of each category.
Real-World Use Cases
Configuration management: Baseline critical system configuration files (C:\Windows\System32\drivers\etc\hosts, registry exports, GPO backups) and detect unauthorised changes.
Compliance auditing: Demonstrate to auditors that controlled documents haven't been altered between assessments.
Incident response: Establish known-good baselines for investigation machines, then verify they haven't been tampered with during analysis.
Change detection on network shares: Monitor shared directories for modifications, especially useful for detecting ransomware encryption in progress (files changing rapidly en masse).
Software deployment verification: After deploying application updates, verify that only expected files changed and nothing else was modified.
What This Detects That Other Tools Miss
Traditional file comparison tools check metadata. This script checks content.
Scenario 1: Timestamp forgery
An attacker modifies important.docx but resets the "Date Modified" timestamp to the original value using Set-ItemProperty. Windows Explorer shows no change. hash_verifier.ps1 detects the modification immediately because the content hash changed.
Scenario 2: Size-preserving edits
Someone edits a text file, deleting one character and adding another elsewhere. File size stays identical. hash_verifier.ps1 flags it as [MISMATCH] because even a single-bit change produces a completely different SHA-256 hash.
Scenario 3: File replacement
An executable is replaced with a different executable of the exact same size. Metadata looks normal. Hash verification catches it.
Performance Considerations
Hashing is CPU-intensive. On modern hardware:
- Small files (< 1 MB): Nearly instant
- Medium files (10-100 MB): 1-5 seconds each
- Large files (1+ GB): Several seconds to minutes
For directories with thousands of files, generation takes time. Run it as a scheduled task during off-hours if monitoring production systems.
The verification step is typically faster than generation because PowerShell can skip re-hashing files if their metadata hasn't changed (though the script doesn't implement this optimisation for simplicity — it re-hashes everything to ensure accuracy).
Extending the Script
Email alerts on mismatch:
Add an if ($mismatchCount -gt 0) block that calls Send-MailMessage to alert administrators.
Scheduled task integration:
Create a Windows Scheduled Task that runs Verify mode daily and logs results to a central location.
SIEM integration:
Parse the output .txt file with a log ingestion tool and feed mismatch events into your security monitoring system.
Multi-algorithm verification:
Add MD5 or SHA-1 alongside SHA-256 for legacy compatibility or additional assurance (though SHA-256 alone is sufficient for integrity verification).
GitHub Repository
The complete script, sample baseline files, and this tutorial are available on GitHub:
powershell-hash-verifier
Automate file hash verification and mismatch detection with PowerShell.
Conclusion
File integrity verification doesn't require expensive enterprise tools. PowerShell's built-in Get-FileHash cmdlet provides cryptographic-strength assurance that files haven't changed. This script packages it into a practical baseline-and-verify workflow that works on any Windows system without dependencies.
For IT security professionals, system administrators, and compliance teams working in Windows environments, hash-based file verification is a fundamental technique that catches modifications other tools miss.
Built by ShadowStrike (Strategos) — where we build actual security tools instead of theatre 🎃.