


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

IT之家
IT之家
A
About on SuperTechFans
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
N
Netflix TechBlog - Medium
Microsoft Security Blog
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
博客园 - 三生石上(FineUI控件)
博客园 - 聂微东
博客园 - Franky
D
Docker
Martin Fowler
Martin Fowler
Engineering at Meta
Engineering at Meta
The Cloudflare Blog
人人都是产品经理
人人都是产品经理
Last Week in AI
Last Week in AI
U
Unit 42
F
Fortinet All Blogs
H
Help Net Security
Blog — PlanetScale
Blog — PlanetScale
Microsoft Azure Blog
罗磊的独立博客
P
Proofpoint News Feed
月光博客
月光博客
G
Google Developers Blog

Orca Security

Langflow RCE Actively Exploited to Deploy Cryptominers on AI Infrastructure Orca MCP: When Text Stops Scaling Kubernetes Compliance Tools: Automating CIS Benchmarks Risk-Based Vulnerability Management for the Cloud: A 2026 Guide Private Cloud Security: Top Risks and Best Practices (2026) What Is Generative AI in Cybersecurity? Best Vulnerability Management Tools and Software in 2026 2026 State of Application Security Report Recap: What the Data Says and What Security Teams Should Do About It AI Security for Sensitive Data: Best Practices and Guidelines Best AI Code Security Solutions 2026: How to Secure AI-Generated Code From Platform to Program: How to Ensure Your Cloud Security Solution Delivers Best AI Cybersecurity Providers 2026: A Buyer's Guide to AI-Powered Security Platforms Join Orca Security at Black Hat USA 2026 CNAPP Tools That Reduce Security Tool Sprawl: CNAPP vs. Dedicated Solutions What Is Container Runtime Security? A Practical Guide 2026 What Is Application Security Testing? Tools and Types What Is Managed Cloud Security? A Practical Guide What Is SaaS Security Posture Management? SSPM Guide Top 10 Cloud Security Standards for Compliance What is the MIT License? Compliance and Comparisons AI Agents vs. Agentless Security vs. Agent-based Security 144 Mastra npm Packages Compromised via Supply Chain Attack The Complete Guide to LLM Security: Risks, Best Practices, and Solutions Cloud Security LIVE 2026: Top 10 Takeaways Practitioners Can Use Now Cloud Security LIVE 2026: Top 10 Takeaways CISOs Can Use Now (and What to Do Next) How Orca Traced an nginx Flaw to 1.45 Million Tengine Servers All Running Vulnerable Code What to Look for in Container Security Tools Cloud Application Security Best Practices for DevSecOps Cloud Security Tools: 10 Types Explained for Teams What Is NIST CSF? Framework 2.0 Explained
Credential‑Stealing Malware in LiteLLM Supply Chain Attack
2026-03-25 · via Orca Security

Executive Summary

A severe malware incident (no formal CVE yet, but tracked as a high‑risk supply chain compromise) was disclosed affecting the widely used Python package LiteLLM (PyPI). Attackers from the TeamPCP threat group trojanized LiteLLM by publishing malicious versions 1.82.7 and 1.82.8, allowing them to harvest credentials and deploy backdoors when the package is installed or imported. Due to the potential large‑scale credential theft and persistent access, immediate mitigation is required.

Overview: The LiteLLM Supply Chain Attack

The issue stems from a compromised maintainer account and CI/CD abuse that injected malicious code into the package’s build artifacts. In the backdoored LiteLLM versions, attackers embedded payloads that execute at import time or even at every Python process startup via a crafted .pth file. These payloads harvest SSH keys, cloud provider credentials, Kubernetes secrets, crypto wallet keys, and other sensitive secrets from developer environments, and exfiltrate them to attacker infrastructure. In some cases, the malware also includes tools for Kubernetes lateral movement and a persistent systemd backdoor for ongoing access.

No authentication is required to trigger the malicious logic: simply installing or importing the affected LiteLLM versions can activate it. The components affected are LiteLLM PyPI package versions 1.82.7 and 1.82.8. LiteLLM is commonly used as a unified interface for calling dozens of large language models in Python applications, and its wide adoption means many development and CI/CD environments may have pulled these tainted releases.

The Impact

At the time of writing, both malicious versions have been removed from PyPI, but proof‑of‑concept exploitation is effectively embedded in the distributed code and there are reports of active credential collection. Regardless of formal exploit tooling, the ease of triggering the payload via normal package installation makes this high risk, especially for development environments with cloud access keys or deployment credentials.

Successful execution could allow attackers to steal cloud and crypto credentials, deploy backdoor services in Kubernetes clusters, and maintain persistent access to build and production systems, leading to data exposure, unauthorized resource usage, and full environment compromise.

Mitigation Recommendations

Users should immediately:

  • remove any instances of LiteLLM 1.82.7 and 1.82.8 from their environments
  • rotate all credentials and API keys that may have been present 
  • pin to a known good version such as 1.82.6 or earlier until a verified patched release is published

Environments that installed the malicious versions—even transiently—should assume compromise and rotate secrets accordingly, as the malware is capable of silent exfiltration.

How can Orca help?

Orca enables customers to quickly identify assets running vulnerable or tainted package versions, understand their exposure in context—including internet accessibility, runtime reachability, and asset criticality—and prioritize remediation based on real risk rather than CVSS alone. Orca’s platform highlights affected assets directly in the newItem view, helping security teams focus on the most critical remediation paths first.
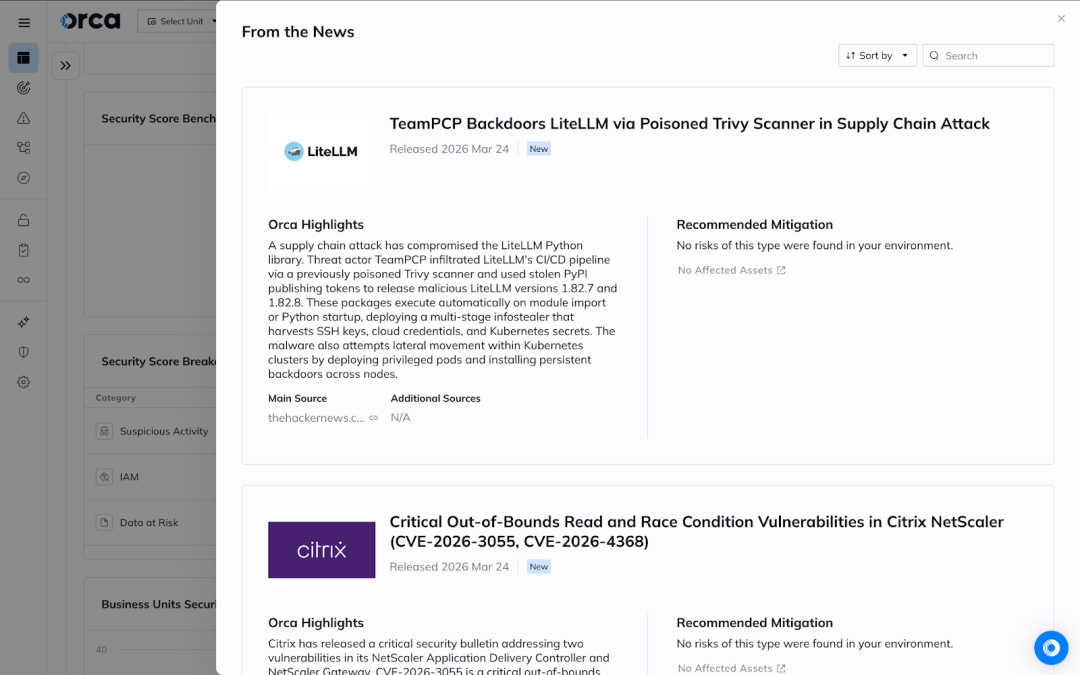
A screenshot of the From the News widget in the Orca Platform
From the News widget in the Orca Platform