
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

D
Docker
I
InfoQ
L
LangChain Blog
阮一峰的网络日志
阮一峰的网络日志
Y
Y Combinator Blog
博客园_首页
Martin Fowler
Martin Fowler
宝玉的分享
宝玉的分享
A
About on SuperTechFans
Apple Machine Learning Research
Vercel News
Vercel News
T
The Blog of Author Tim Ferriss
C
Check Point Blog
B
Blog RSS Feed
Cyber Security Advisories - MS-ISAC
Engineering at Meta
Engineering at Meta
B
Blog
爱范儿
爱范儿
Stack Overflow Blog
Stack Overflow Blog
aimingoo的专栏
aimingoo的专栏
WordPress大学
WordPress大学
F
Fortinet All Blogs
月光博客
月光博客
GbyAI
GbyAI

Orca Security

Langflow RCE Actively Exploited to Deploy Cryptominers on AI Infrastructure Orca MCP: When Text Stops Scaling Kubernetes Compliance Tools: Automating CIS Benchmarks Risk-Based Vulnerability Management for the Cloud: A 2026 Guide Private Cloud Security: Top Risks and Best Practices (2026) What Is Generative AI in Cybersecurity? Best Vulnerability Management Tools and Software in 2026 2026 State of Application Security Report Recap: What the Data Says and What Security Teams Should Do About It AI Security for Sensitive Data: Best Practices and Guidelines Best AI Code Security Solutions 2026: How to Secure AI-Generated Code From Platform to Program: How to Ensure Your Cloud Security Solution Delivers Best AI Cybersecurity Providers 2026: A Buyer's Guide to AI-Powered Security Platforms Join Orca Security at Black Hat USA 2026 CNAPP Tools That Reduce Security Tool Sprawl: CNAPP vs. Dedicated Solutions What Is Container Runtime Security? A Practical Guide 2026 What Is Application Security Testing? Tools and Types What Is Managed Cloud Security? A Practical Guide What Is SaaS Security Posture Management? SSPM Guide Top 10 Cloud Security Standards for Compliance What is the MIT License? Compliance and Comparisons AI Agents vs. Agentless Security vs. Agent-based Security 144 Mastra npm Packages Compromised via Supply Chain Attack The Complete Guide to LLM Security: Risks, Best Practices, and Solutions Cloud Security LIVE 2026: Top 10 Takeaways Practitioners Can Use Now Cloud Security LIVE 2026: Top 10 Takeaways CISOs Can Use Now (and What to Do Next) How Orca Traced an nginx Flaw to 1.45 Million Tengine Servers All Running Vulnerable Code What to Look for in Container Security Tools Cloud Application Security Best Practices for DevSecOps Cloud Security Tools: 10 Types Explained for Teams What Is NIST CSF? Framework 2.0 Explained
Critical Langflow Path Traversal Flaw Exploited for Unaut...
The Orca Research Pod · 2026-06-12 · via Orca Security

Executive Summary

A high-severity vulnerability (CVE-2026-5027, CVSS 8.8) was disclosed affecting Langflow, an open-source low-code platform widely used for building AI applications, allowing attackers to achieve remote code execution via a path traversal in the file upload endpoint. Due to the potential for full system compromise and the trivial nature of exploitation, immediate patching is required.

About the Vulnerability: CVE-2026-5027

The issue originates from Langflow’s POST /api/v2/files endpoint, where the upload_user_file() function in the backend fails to sanitize the filename parameter in multipart form data. By sending specially crafted filenames containing directory traversal sequences (../), attackers can write arbitrary files to any location on the server’s filesystem. Because Langflow enables unauthenticated auto-login by default, a single request is all that is needed to obtain a valid session token and exploit the vulnerability — no credentials required.

The following versions are affected:

  • langflow-base versions below 0.8.3
  • Langflow versions up to and including 1.8.4

These components are used across AI development workflows and production pipelines, particularly when Langflow is deployed with default auto-login settings and exposed to the network. Censys scans have identified approximately 7,000 publicly exposed Langflow instances, primarily in North America, underscoring the breadth of potential exposure.

Risk Impact

Tenable discovered the vulnerability and attempted responsible disclosure, contacting Langflow maintainers three times between January and February 2026 before publicly disclosing as advisory TRA-2026-26 on March 27, 2026. VulnCheck has since confirmed active exploitation in the wild, with honeypots detecting attackers dropping test files onto vulnerable instances. A public proof-of-concept exploit is available. Prior Langflow vulnerabilities, including CVE-2026-0770, CVE-2026-33017, and CVE-2025-34291 (weaponized by the MuddyWater threat group), demonstrate sustained adversary interest in agentic AI applications infrastructure.

Successful exploitation could allow attackers to write malicious files to arbitrary filesystem locations, escalate to full remote code execution through cron job injection or overwriting configuration files, and potentially pivot across the environment, leading to service disruption, data exposure, or full infrastructure compromise.

Mitigation Recommendations

Upgrade to the following patched versions immediately:

  • Langflow 1.10.0 (released June 10, 2026) or at minimum version 1.9.0 / langflow-base 0.8.3

Organizations should also:

  • Disable the default auto-login configuration to require authentication
  • Restrict network exposure by placing Langflow behind a VPN or firewall
  • Monitor for suspicious file write activity, unexpected cron job modifications, and anomalous requests to /api/v2/files

How can Orca help?

Orca enables customers to quickly identify assets running vulnerable versions of Langflow, understand their exposure in context — including internet accessibility, runtime reachability, and asset criticality — and prioritize remediation based on real risk rather than CVSS alone. Orca’s agentless scanning detects Langflow installations across cloud environments through software composition analysis, while Orca’s platform highlights affected assets directly in the alert view, helping security teams focus on the most critical remediation paths first.
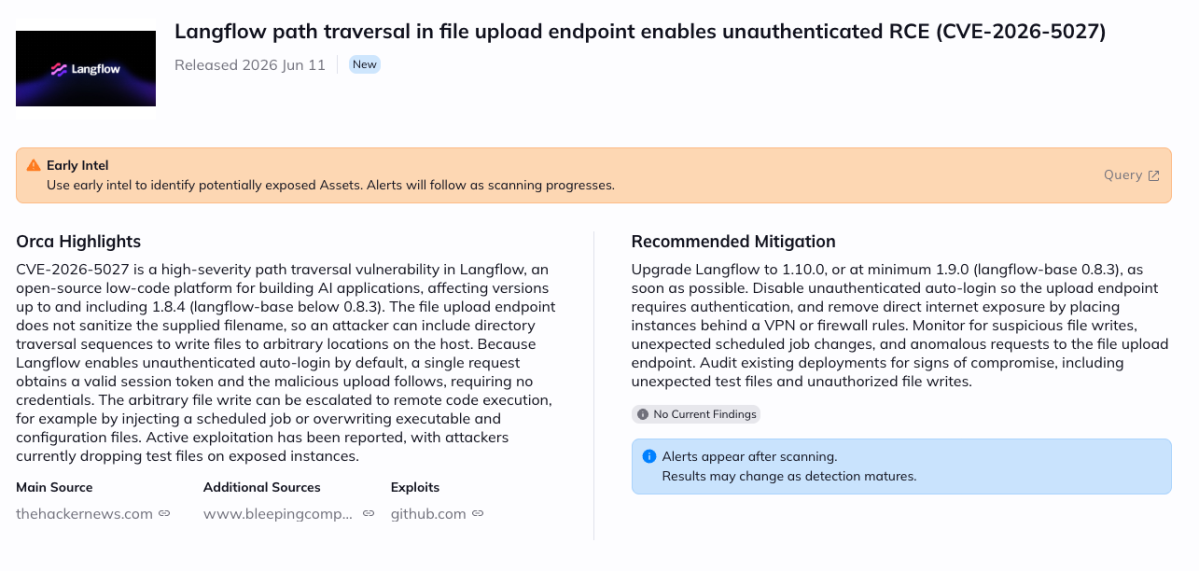
A screenshot of the Langflow RCE announcement in the Orca Platform