

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

D
Docker
人人都是产品经理
人人都是产品经理
小众软件
小众软件
博客园 - Franky
WordPress大学
WordPress大学
Jina AI
Jina AI
Google DeepMind News
I
InfoQ
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
F
Fortinet All Blogs
博客园 - 【当耐特】
IT之家
IT之家
G
Google Developers Blog
J
Java Code Geeks
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
云风的 BLOG
云风的 BLOG
Recent Announcements
有赞技术团队
有赞技术团队
V
Visual Studio Blog
U
Unit 42
阮一峰的网络日志
阮一峰的网络日志
月光博客
月光博客
GbyAI
GbyAI
雷峰网
雷峰网

SANS Internet Storm Center, InfoCON: green

From a VHDX File to a Remcos RAT - SANS Internet Storm Center ISC Stormcast For Tuesday, June 16th, 2026 https://isc.sans.edu/podcastdetail/9974 Evil MSI Background: BASE64 Statistical Analysis - SANS ISC ISC Stormcast For Monday, June 15th, 2026 https://isc.sans.edu/podcastdetail/9972 ISC Stormcast For Friday, June 12th, 2026 https://isc.sans.edu/podcastdetail/9970 ISC Stormcast For Thursday, June 11th, 2026 https://isc.sans.edu/podcastdetail/9968 How has use of framing protection security headers changed in the past 3 years? ISC Stormcast For Wednesday, June 10th, 2026 https://isc.sans.edu/podcastdetail/9966 Microsoft June 2026 Patch Tuesday - SANS Internet Storm Center ISC Stormcast For Tuesday, June 9th, 2026 https://isc.sans.edu/podcastdetail/9964 TeamPCP Supply Chain Campaign: Activity Through 2026-06-07 ISC Stormcast For Monday, June 8th, 2026 https://isc.sans.edu/podcastdetail/9962 The Evil MSI Background is Back! - SANS Internet Storm Center ISC Stormcast For Friday, June 5th, 2026 https://isc.sans.edu/podcastdetail/9960 Microsoft's Coreutils for Windows - SANS Internet Storm Center ISC Stormcast For Thursday, June 4th, 2026 https://isc.sans.edu/podcastdetail/9958 Continuing Scans for swagger.json - SANS Internet Storm Center ISC Stormcast For Wednesday, June 3rd, 2026 https://isc.sans.edu/podcastdetail/9956 New Wave Of Phishing Emails with SVG Files - SANS ISC ISC Stormcast For Tuesday, June 2nd, 2026 https://isc.sans.edu/podcastdetail/9954 ISC Stormcast For Monday, June 1st, 2026 https://isc.sans.edu/podcastdetail/9952 Unidentified RAT pushes NetSupport RAT - SANS ISC YARA-X 1.17.0 Release - SANS Internet Storm Center ISC Stormcast For Friday, May 29th, 2026 https://isc.sans.edu/podcastdetail/9950 Analysis of a Year of Files Uploaded to DShield Sensors ISC Stormcast For Thursday, May 28th, 2026 https://isc.sans.edu/podcastdetail/9948 Reconstructing an Akira Ransomware Kill Chain from Perimeter and Endpoint Logs ISC Stormcast For Wednesday, May 27th, 2026 https://isc.sans.edu/podcastdetail/9946 ISC Stormcast For Tuesday, May 26th, 2026 https://isc.sans.edu/podcastdetail/9944 Possible ACR Stealer From Page Impersonating Claude
Lumma Stealer infection with Sectop RAT (ArechClient2)
2026-04-17 · via SANS Internet Storm Center, InfoCON: green

Introduction

This diary provides indicators from a Lumma Stealer infection that was followed by Sectop RAT (ArechClient2). I searched for cracked versions of popular copyright-protected software, and I downloaded the initial malware after following the results of one such search. This is a common distribution technique for various families of malware, and I often find Lumma Stealer this way.

In this case, the initial malware for Lumma Stealer was delivered as a password-protected 7-zip archive. The extracted malware is an inflated Windows executable (EXE) file at 806 MB. The EXE is padded with null-bytes (0x00), a technical which increases the EXE size while allowing the compressed archive file to be much smaller. The password-protected archive and inflated EXE file are designed to avoid detection.

Images from the infection
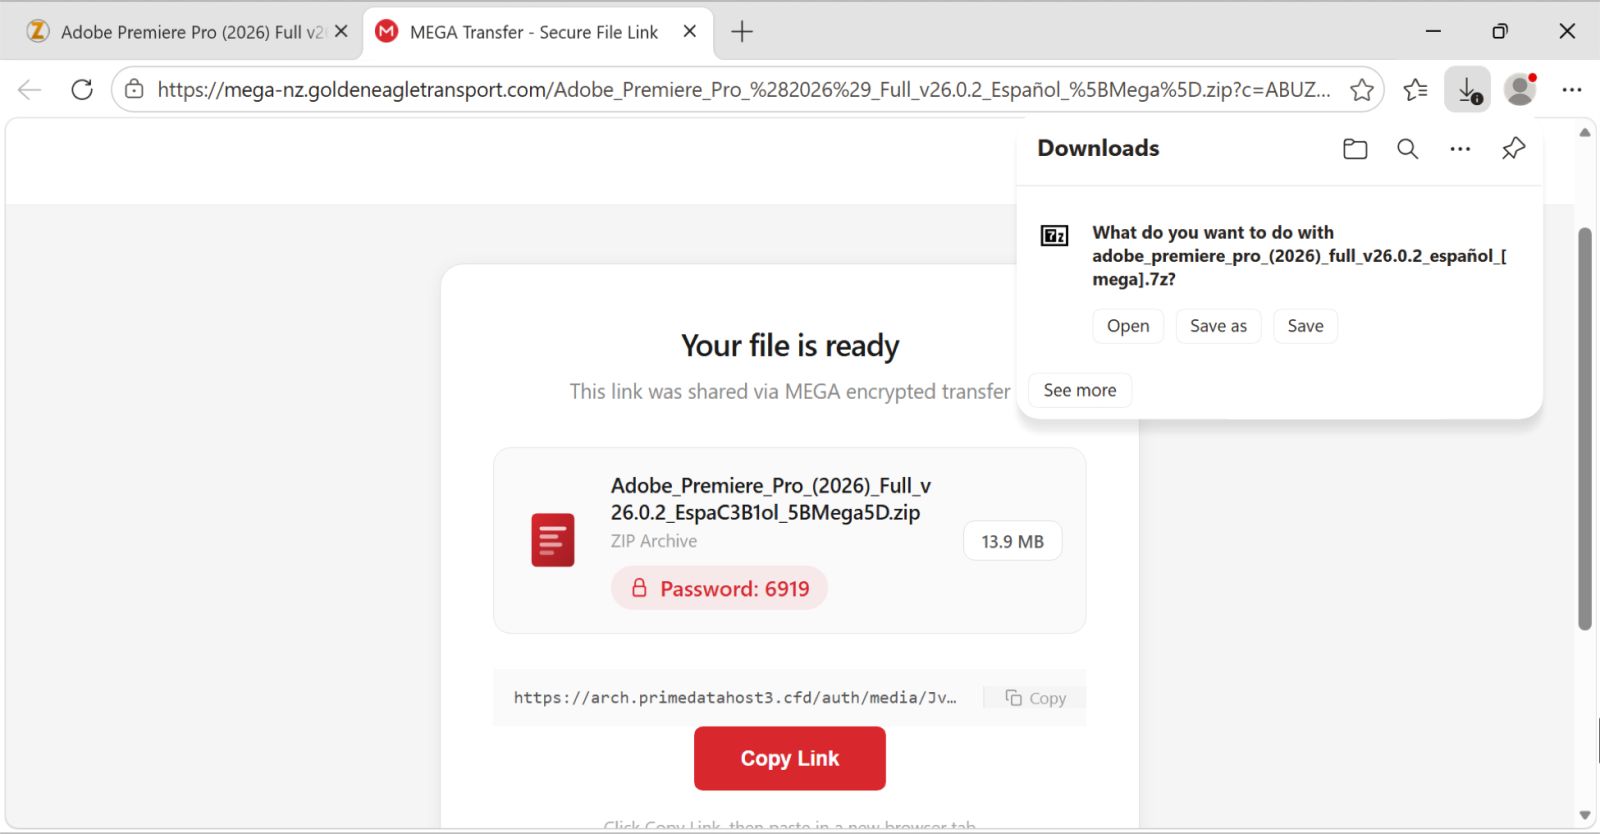

Shown above: Example of a page with instructions to download the initial malware file.
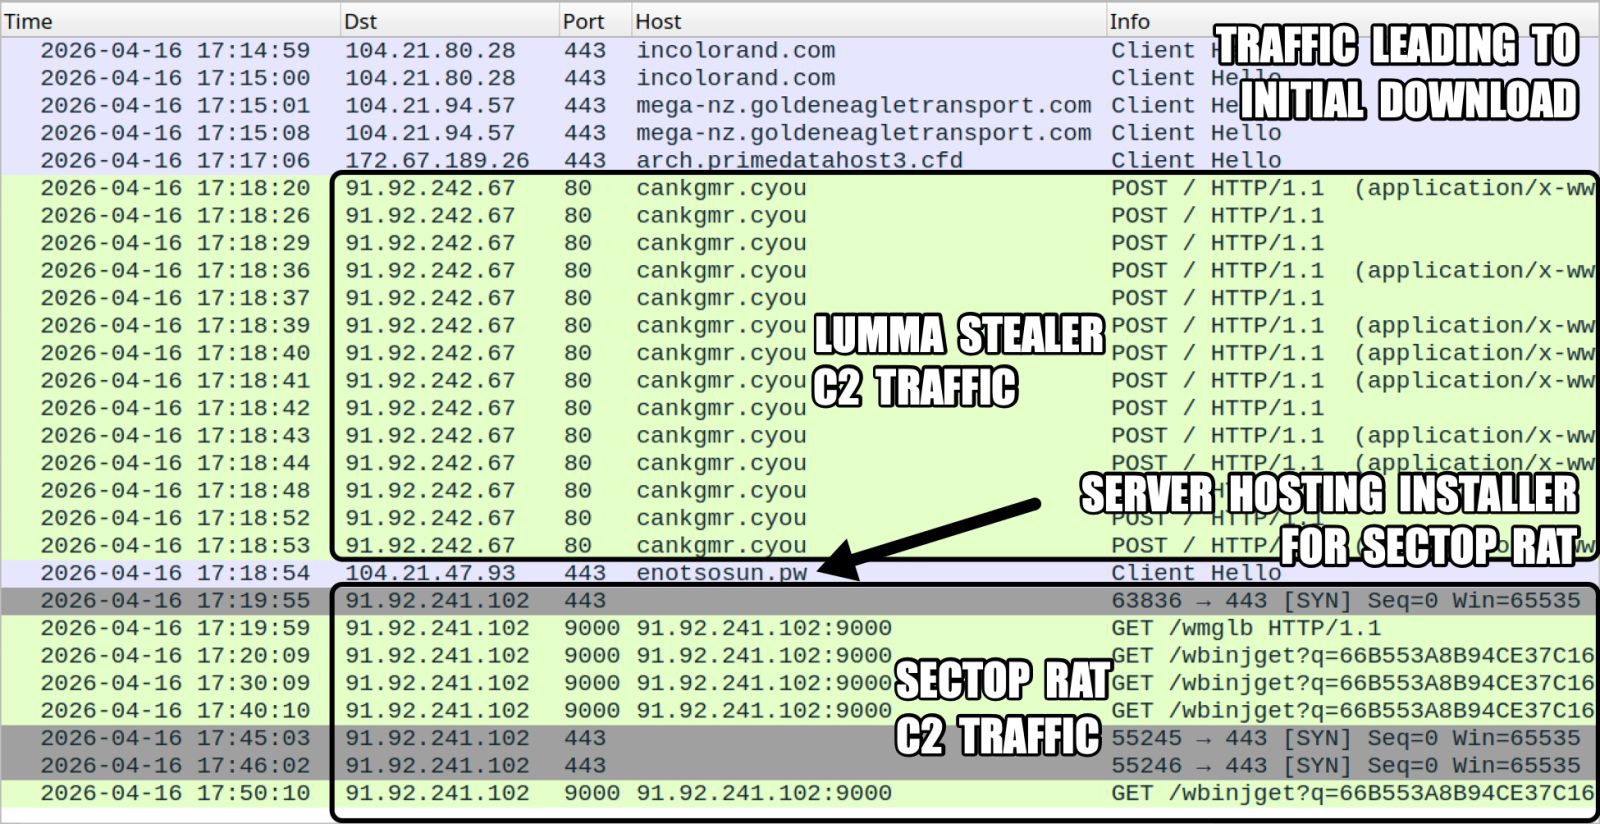

Shown above: Traffic from the infection filtered in Wireshark.
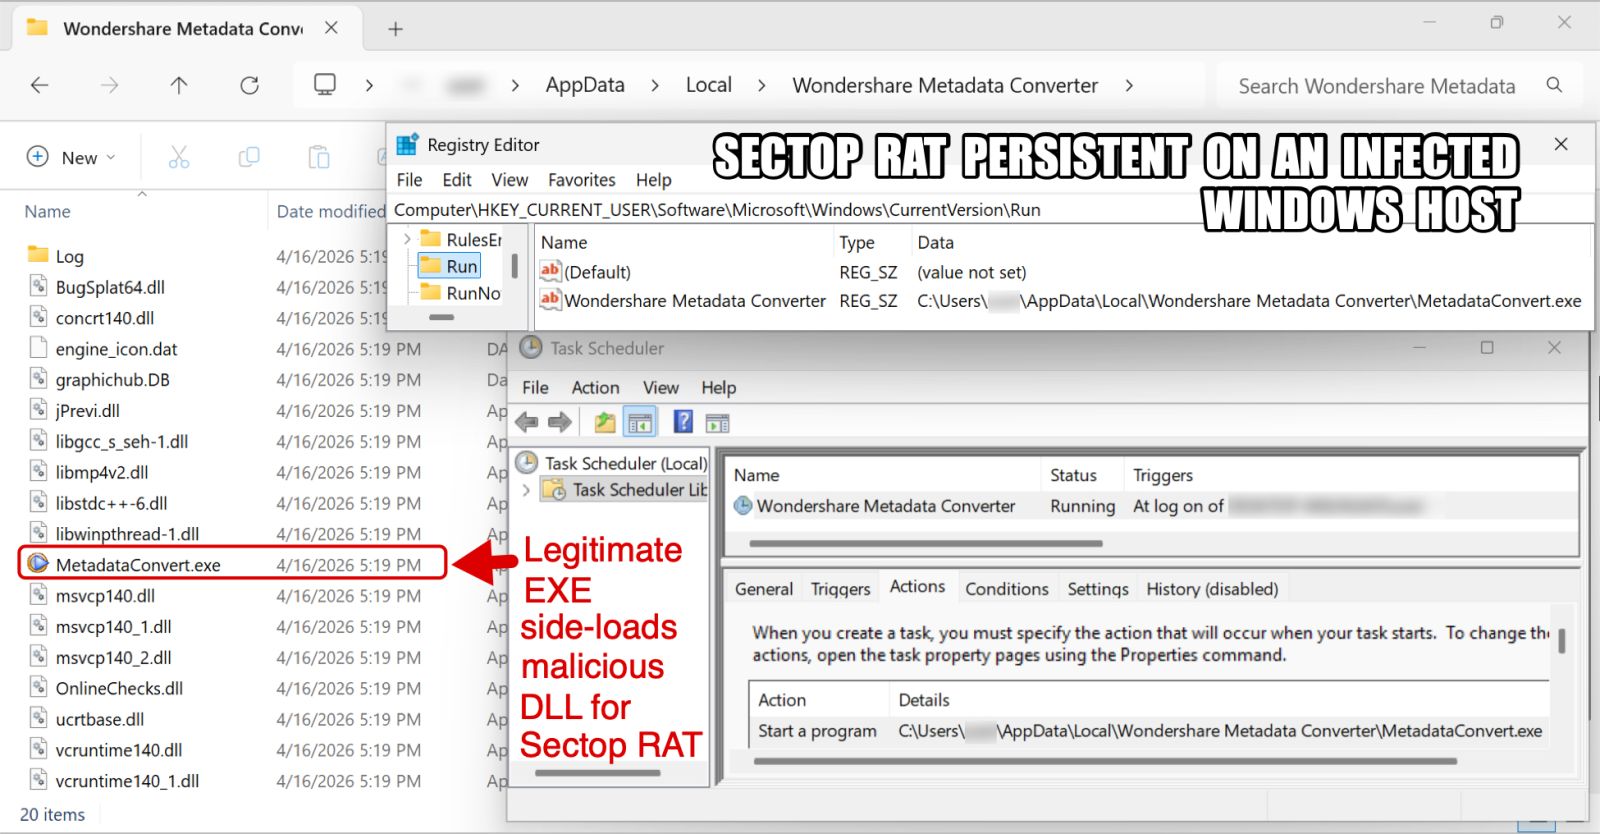

Shown above: Sectop RAT persistent on an infected Windows host.

Indicators of Compromise

Example of download link from the site advertising cracked versions of copyright-protected software:

hxxps[:]//incolorand[.]com/how-visual-patch-enhances-ui-consistency-across-releases/?utm_source={CID}&utm_term=Adobe%20Premiere%20Pro%20(2026)%20Full%20v26.0.2%20Espa%C3%B1ol%20[Mega]&utm_content={SUBID1}&utm_medium={SUBID2}

Example of URL for page with the file download instructions:

hxxps[:]//mega-nz.goldeneagletransport[.]com/Adobe_Premiere_Pro_%282026%29_Full_v26.0.2_Espa%C3%B1ol_%5BMega%5D.zip?c=ABUZ4WkRgQUA_YUCAFVTFwASAAAAAACh&s=360721

Example of URL for file download from site above site impersonating MEGA:

hxxps[:]//arch.primedatahost3[.]cfd/auth/media/JvWcFd5vUoYTrImvtWQAASTh/Adobe_Premiere_Pro_(2026)_Full_v26.0.2_Espa%C3%B1ol_%5BMega%5D.zip

Downloaded file:

Extracted malware:

  • SHA256 hash: 4849f76dafbef516df91fecfc23a72afffaf77ade51f805eae5ad552bed88923
  • File size: 806,127,604 bytes
  • File name: appFile.exe
  • File type: PE32 executable (GUI) Intel 80386, for MS Windows
  • File description: Inflated Windows EXE file for Lumma Stealer, padded with null-bytes

Deflated malware:

Lumma Stealer command and control (C2) domains from Triage sandbox analysis:

  • cankgmr[.]cyou
  • carytui[.]vu
  • decrnoj[.]club
  • genugsq[.]best
  • longmbx[.]click
  • mushxhb[.]best
  • pomflgf[.]vu
  • strikql[.]shop
  • ulmudhw[.]shop

Follow-up malware:

Example of Sectop RAT C2 traffic from an infected Windows host:

  • hxxp[:]//91.92.241[.]102:9000/wmglb
  • hxxp[:]//91.92.241[.]102:9000/wbinjget?q=66B553A8B94CE37C16F4EBC863D51FCC
  • tcp[:]//91.92.241[.]102:443/ - encoded or otherwise encrypted traffic (not HTTPS/TLS)

---
Bradley Duncan
brad [at] malware-traffic-analysis.net