


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Microsoft Azure Blog
WordPress大学
WordPress大学
小众软件
小众软件
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
V
V2EX
Hugging Face - Blog
Hugging Face - Blog
美团技术团队
博客园 - 三生石上(FineUI控件)
Last Week in AI
Last Week in AI
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园 - Franky
Microsoft Security Blog
Y
Y Combinator Blog
A
About on SuperTechFans
The GitHub Blog
The GitHub Blog
U
Unit 42
H
Hackread – Cybersecurity News, Data Breaches, AI and More
云风的 BLOG
云风的 BLOG
IT之家
IT之家
MyScale Blog
MyScale Blog
V
Visual Studio Blog
Cyber Security Advisories - MS-ISAC
I
InfoQ
博客园 - 司徒正美

Unit 42

Unmasking Cloud Identities: From Behavioral Clustering to Automated Detection The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE Untracked Nightmares: The Threats Hiding Behind Commodity Infrastructure Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America An AI-Assisted Cyber Attack: Inside a Unit 42 Investigation Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams Perturbation Probing: A New Diagnostic for the Fragility of LLM Safety The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution Connecting the Dots: Securing the Overlooked Corners of the Software Development Lifecycle (SDLC) Supply Chain Identity Abuse Through Trusted Communication Channels Kimwolf v7: An Evolution of the Kimwolf Botnet The Permanent Threat: Analyzing Aeternum’s Blockchain-Based C2 Operations and Communications Inside the Modern SOC: The Identity Front Door ChainDrop: Inside a Self-Propagating npm Worm Token Jacking: Cybercriminals Could Be Stealing Your AI Resources The Frontier AI Vulnerability Burst: Industrializing Autonomous Zero-Day Discovery in Open-Source Software Almost Half of Malware Samples Communicate Direct to IP Pass the Passkey: A Novel Attack Surface in Passwordless Authentication The Xcode Assassin Returns: A Deep Dive Into the Latest XCSSET Version Chinese-Speaking Threat Actor Harnesses AI Models for Autonomous Cyberattacks Russian Global Webmail Espionage Three Steps to the Terminal: A Siemens ROX II Zero-Day Trilogy AI, Automation and Attacks: Unpacking the Unit 42 2026 Global Incident Response Report AI, Automation and Attacks: Unpacking the Unit 42 2026 Global Incident Response Report TuxBot v3: Inside an IoT Botnet Framework With LLM-Assisted Development No Manners Here: The Ruthless Rise of The Gentlemen Ransomware Vidar Stealer Unmasked: Code Signing Abuse, Go Loaders and File Inflation How We Added WebAuthn to a Browser-Based RDP Client Phantom Squatting: AI-Hallucinated Domains as a Software Supply Chain Vector CL-STA-1062 Targets Southeast Asian Governments and Critical Infrastructure
Threat Brief: Mitigating Large-Scale Credential Attacks
Andy Piazza · 2026-06-20 · via Unit 42

Unit 42 is aware of a large-scale password spraying and credential theft campaign (“FortiBleed”) against Fortinet devices. We observed attempts targeting MSSQL devices as well, and have seen reports of Sophos devices also being targeted. While this activity is not targeting Palo Alto Networks devices, Unit 42 has observed suspicious login attempts in customer telemetry and we are providing this report out of an abundance of caution to ensure our customers have the latest intelligence and product recommendations to protect, detect and respond to attacks to their network.

The threat actors are using a curated password list to attempt password spraying against services exposed to the internet. Unit 42 assesses that the initial password list for this activity was likely developed through a mix of previous breaches, including the successful exploitation of vulnerabilities. Once they obtain credentials, they add them to their password list for future attempts against additional targets, as well as for logging into accounts they successfully compromised.

The threat actors are leveraging a multi-stage process to gain persistent, high-privilege access:

  • Password spraying for initial access: Massive internet-wide scanning and password spraying attempts against Fortinet, Sophos and MSSQL services
  • Configuration Extraction: Depending on the permissions of their initial access, the actor may exploit a privilege escalation vulnerability prior to pulling device configuration files, including stored credentials
  • Offline Cracking: Offline password cracking of the stolen credentials adds to the password list used in step one to target new devices, as well as to log into compromised devices to establish persistence as an administrator

Unit 42 observed an initial access broker (IAB) on the Russian-language cybercrime forum Exploit[.]in claiming responsibility for this campaign, referencing a CVE (no further information), and offering the harvested credentials for sale on June 16, 2026. Unit 42 has not validated their claims at this time.
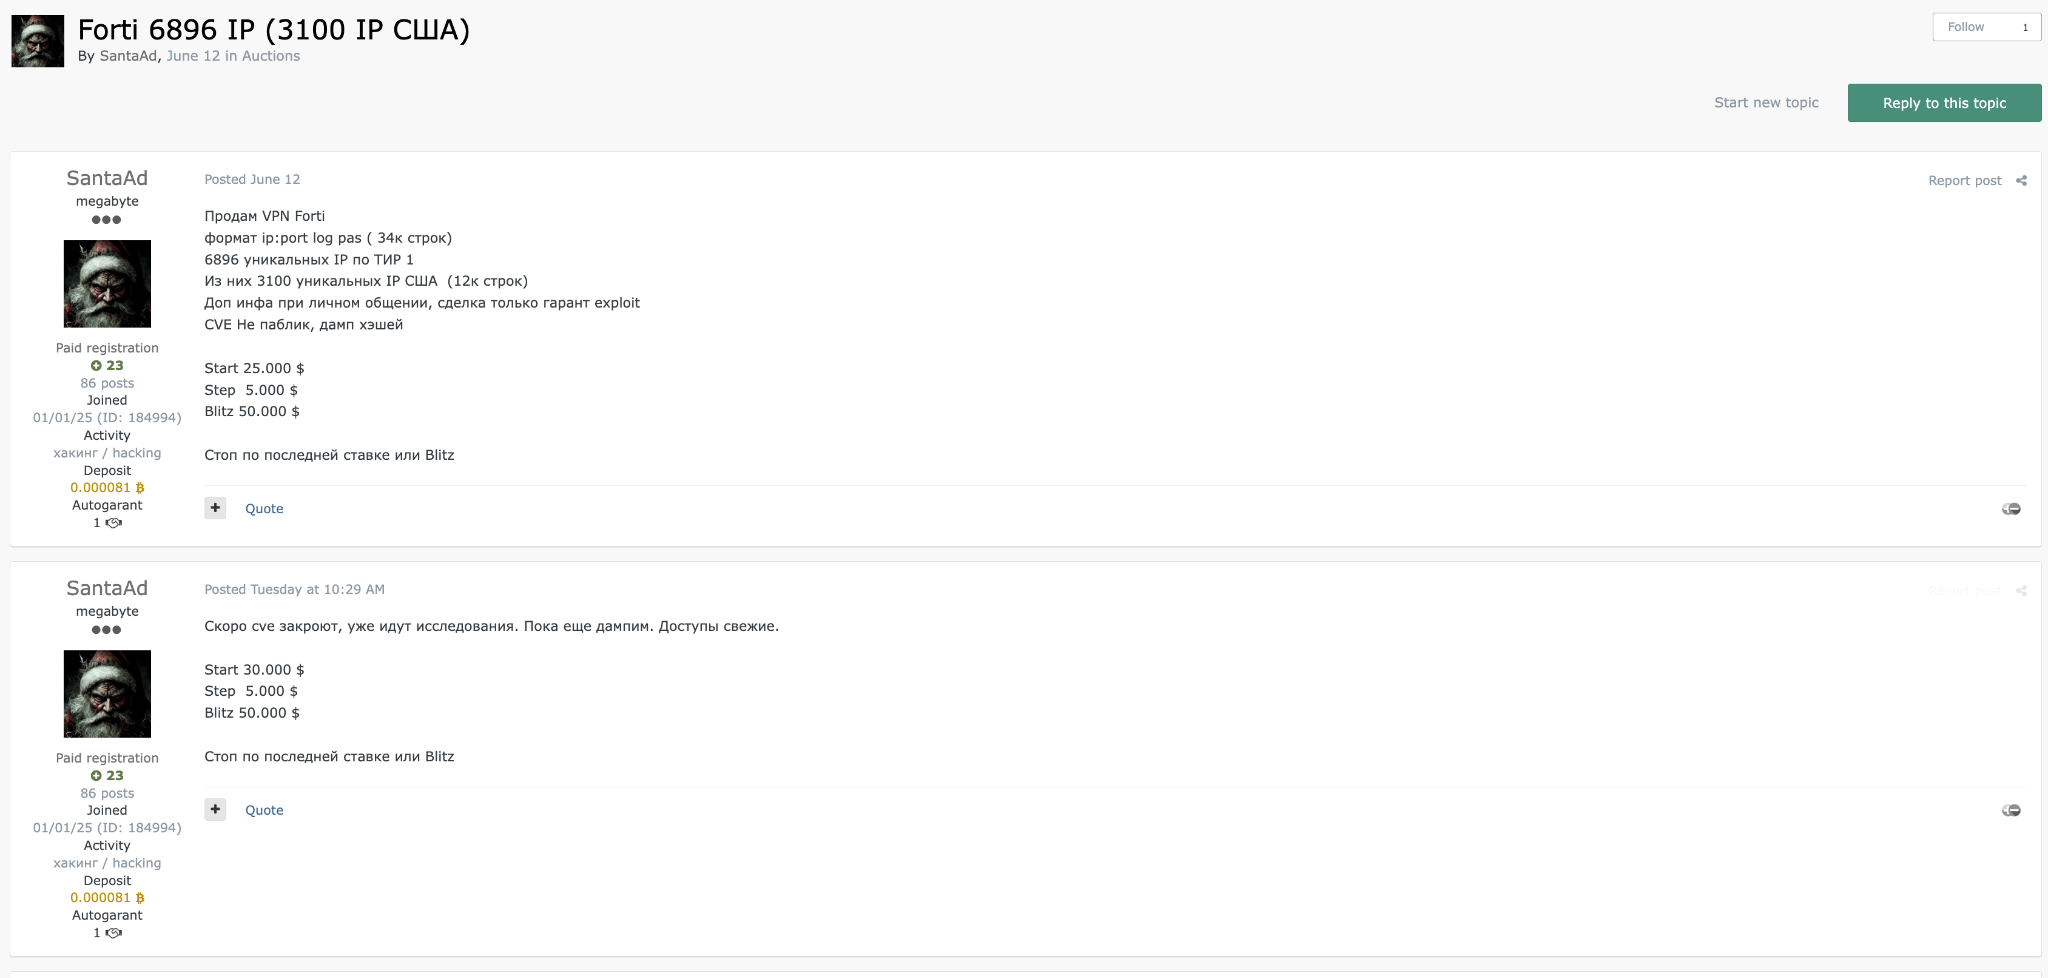
Unit 42 observed an initial access broker (IAB) on the Russian-language cybercrime forum Exploit[.]in claiming responsibility for this campaign of large-scale credential attacks, referencing a CVE (no further information), and offering the harvested credentials for sale on June 16, 2026. Unit 42 has not validated their claims at this time.
Figure 1. Darkweb post of IAB selling credentials.

Unit 42 recommends auditing remote access logs for suspicious activity with a focus on successful logins shortly after large volume password failure events. We also recommend reviewing and implementing the hardening guidance below for edge devices.

SOCRadar provided the initial reporting on the targeting of FortiGate devices. We observed attempts targeting MSSQL devices as well, and have seen reports of Sophos devices also being targeted.

Palo Alto Networks customers receive assistance protecting against and mitigating credential attacks in the following ways:

Palo Alto Networks also recommends the following hardening guidelines:

  • Require MFA: Require multi-factor authentication for all remote services. NGFW customers can integrate several MFA platforms and customize their Password Profiles and complexity to enhance their security posture.
  • Adopt Zero Trust Architecture: Leverage “jump boxes” and Zero Trust Network Access (ZTNA) policies to ensure management interfaces are never exposed directly to the public internet, further narrowing the attack surface for configuration extraction.
  • Change Default Credentials: Change the credentials for default accounts, ensuring long, complex passwords are used to mitigate the risk of password guessing attempts.
  • Disable Unused Accounts: Disable unused accounts to limit the attack surface.
  • Update and Patch: Ensure you have the latest software versions and patches installed to mitigate known vulnerabilities, including local privilege escalation vulnerabilities.

The Unit 42 Incident Response team can also be engaged to help with a compromise or to provide a proactive assessment to lower your risk.

Conclusion

Unit 42 will continue to monitor the situation for updated information. We encourage customers to implement the hunting and hardening recommendations to identify, mitigate, and prevent credential attacks against their networks.

Palo Alto Networks has shared our findings with our fellow Cyber Threat Alliance (CTA) members, including Fortinet. CTA members use this intelligence to rapidly deploy protections to their customers and to systematically disrupt malicious cyber actors. Learn more about the Cyber Threat Alliance.

Palo Alto Networks customers are better protected by our products, as listed below. We will update this threat brief as more relevant information becomes available.

Palo Alto Networks Product Protections and Consulting Services

Palo Alto Networks customers can leverage a variety of product protections and consulting services to identify and defend against this threat.

If you think you might have been compromised or have an urgent matter, get in touch with the Unit 42 Incident Response team or call:

  • North America: Toll Free: +1 (866) 486-4842 (866.4.UNIT42)
  • UK: +44.20.3743.3660
  • Europe and Middle East: +31.20.299.3130
  • Asia: +65.6983.8730
  • Japan: +81.50.1790.0200
  • Australia: +61.2.4062.7950
  • India: 000 800 050 45107
  • South Korea: +82.080.467.8774

Deep and Darkweb Monitoring  

Unit 42's Deep and Dark Web (DDW) monitoring is a service that assists clients in identifying sensitive information and leaked credentials that surface on the dark web, providing critical insights to reduce risk exposure and reduce the time between detection and response.

References