







Published on:
Nov 28, 2025
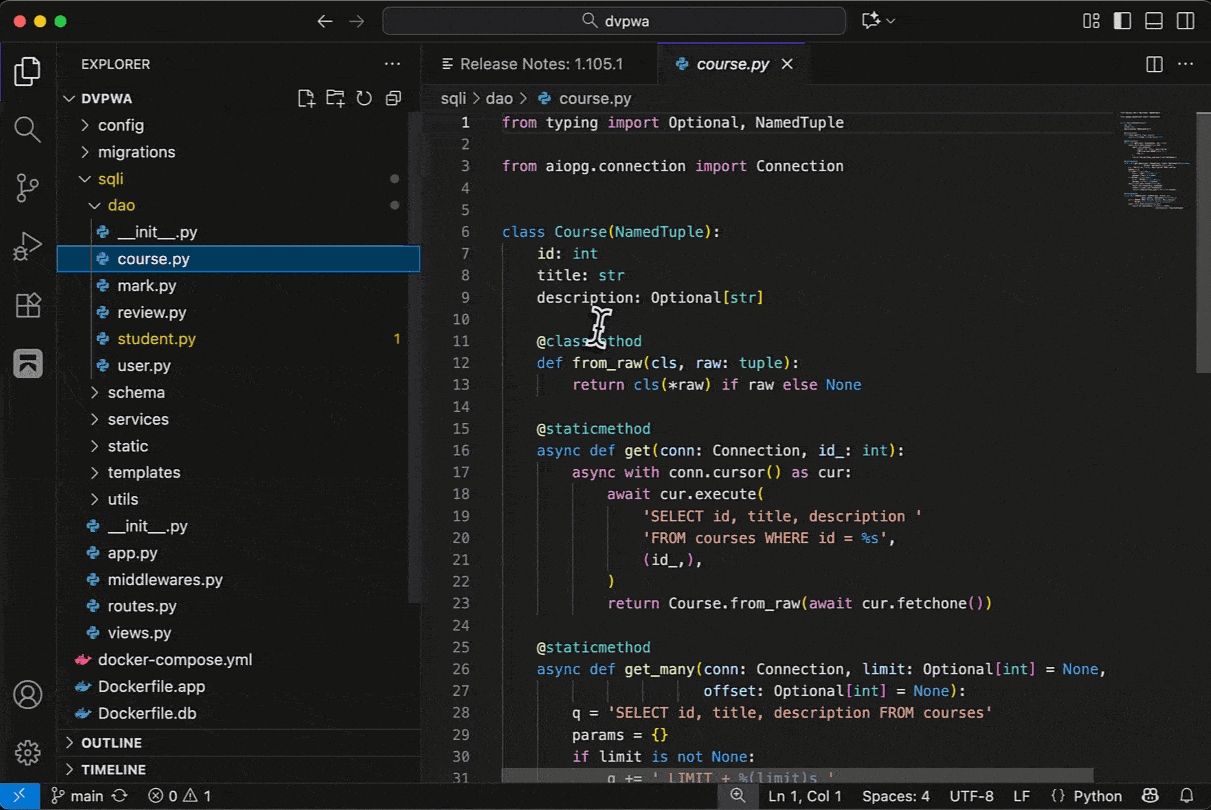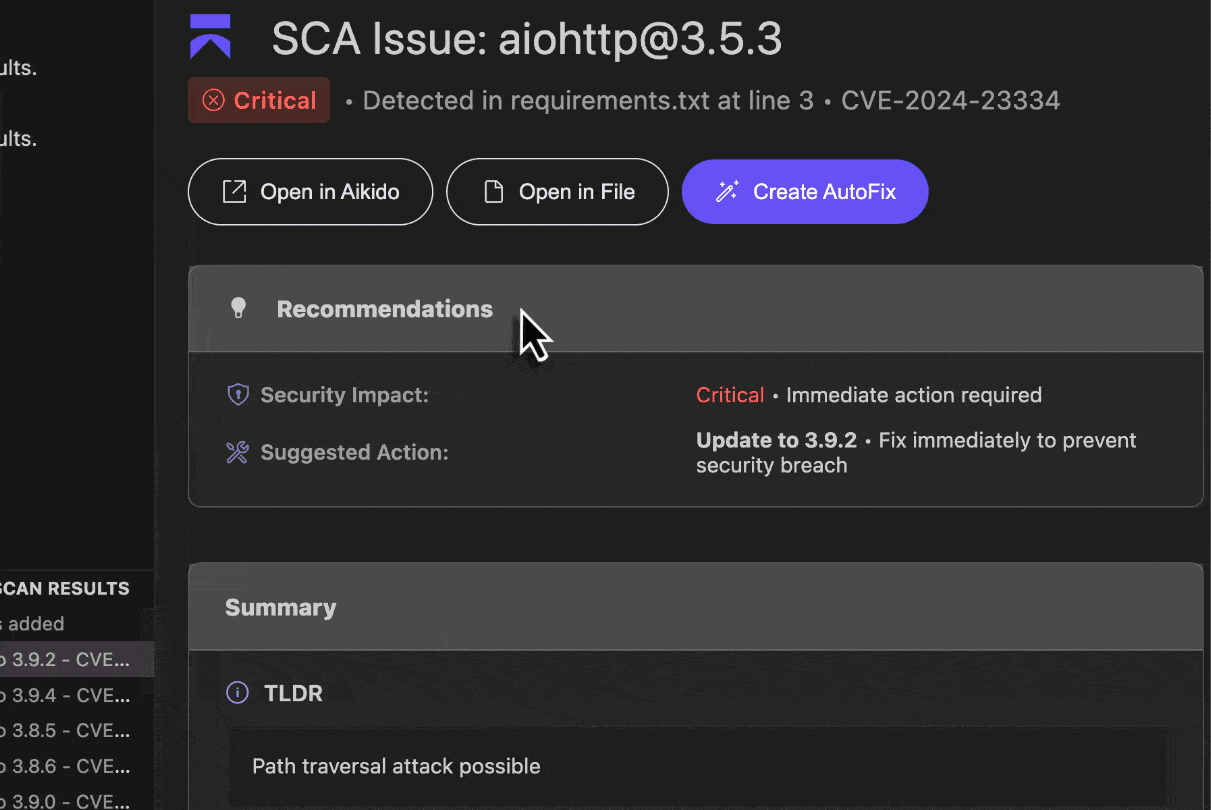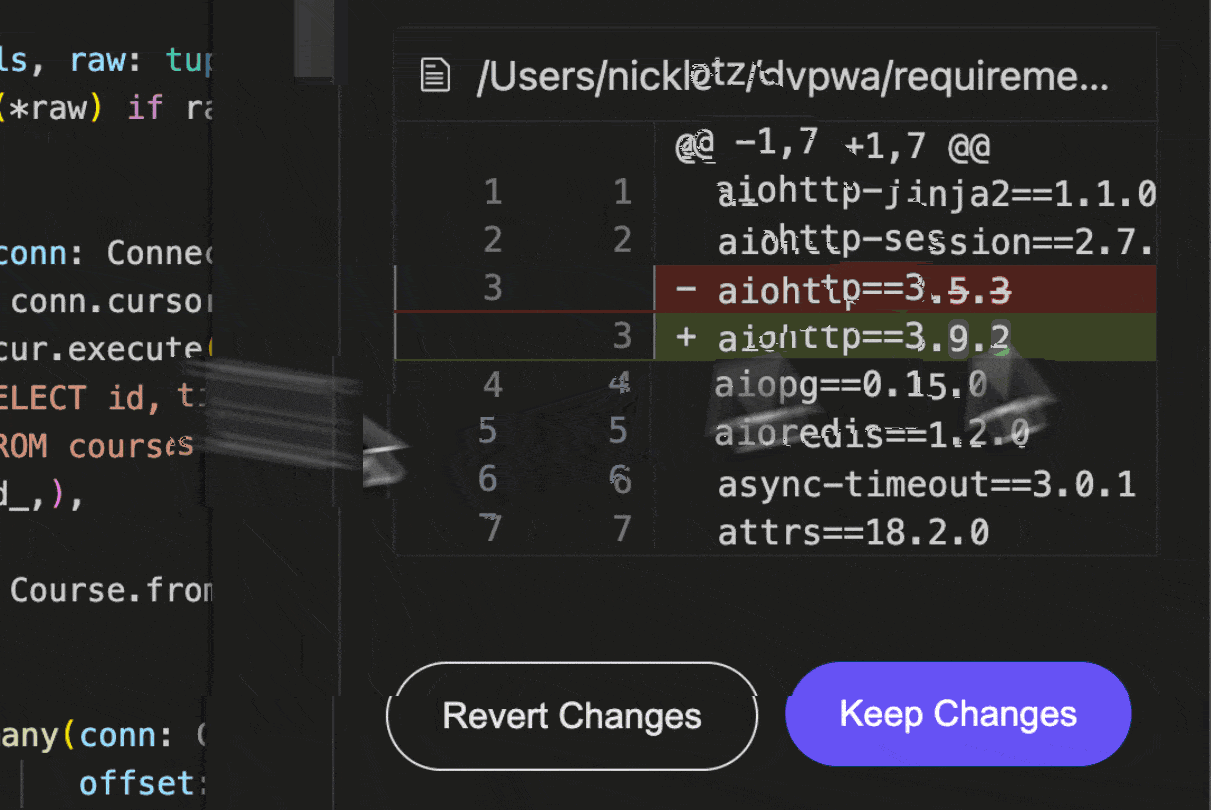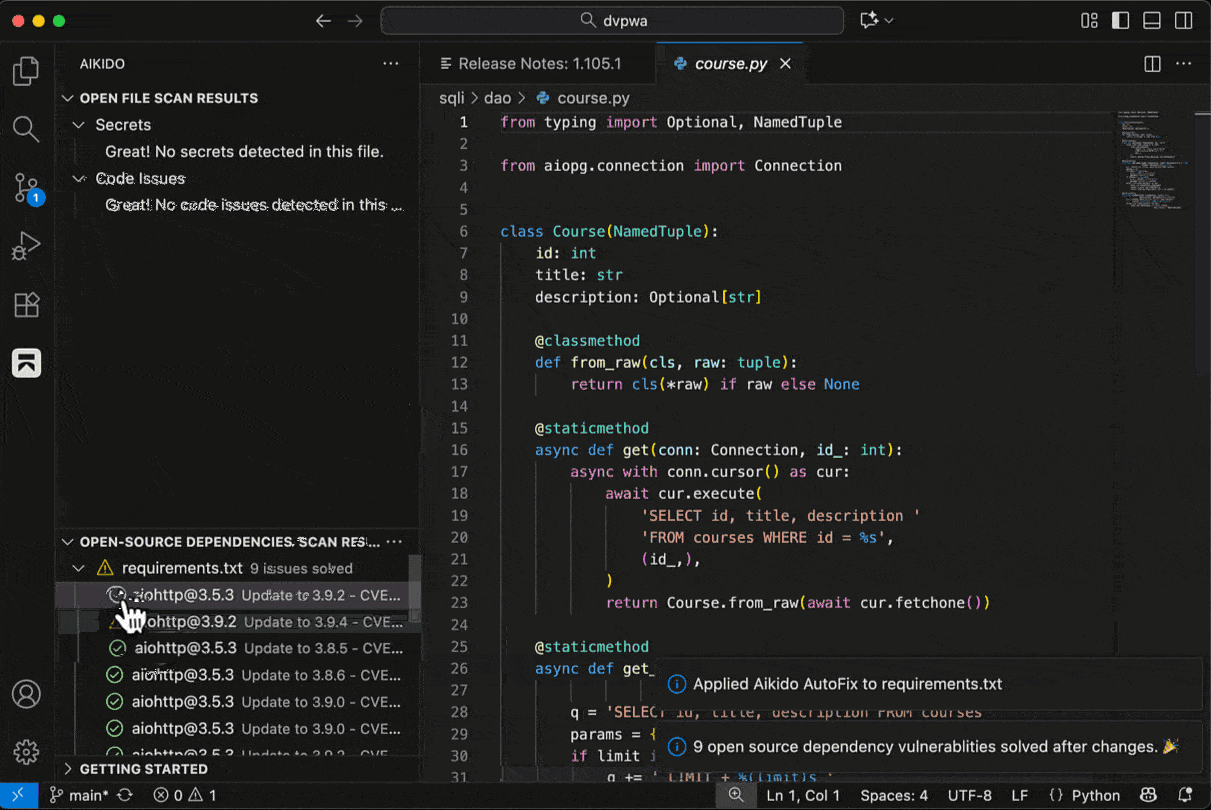
Dependency issues are easiest to address when they show up directly in the development workflow. With this release, we’re bringing the full SCA workflow into the Aikido IDE extension, combining in-editor scanning with the ability to apply safe upgrades through AutoFix. Developers can detect vulnerable packages and resolve them without switching tools or breaking focus.
Our goal across product, engineering, and security remains the same: shorten the distance between identifying an issue and acting on it.
From product and engineering discussions, the reasoning has been clear. Developers need to surface dependency issues earlier, resolve them without switching tools, reduce the noise that comes from late findings in CI, and keep the workflow as close to the code as possible. SCA has traditionally lived outside the development loop, often discovered after the work has moved on. Bringing it into the IDE puts these issues in the right place and time and reduces the gap between identifying an outdated or vulnerable package and taking action, especially now that fixes can be applied in the same workflow through AutoFix.
To run a scan:
This keeps detection and remediation in one place. Scan and fix now happen inside the editor instead of across multiple tools.
With SCA available in the IDE, dependency checks become:
For engineering teams, this reduces dependency drift and the backlog of late fixes. For security teams, issues are discovered and resolved with less noise and fewer handoffs.
We perform SCA scans of dependencies for known CVEs and risky open-source licenses. Scanning is based on dependency manifests and lockfiles, which help make builds reproducible and improve detection of vulnerable packages. Lockfiles are scanned both in the root of a project and in all subfolders.
The IDE uses the same dependency scanning support as Aikido’s repository and CI scans. This includes JavaScript and TypeScript, PHP, Java, Swift, Go, Python, .NET, Ruby, Rust, Kotlin, Dart, Elixir, C and C++, Scala, Clojure, and Unity UPM.
For the full list of supported languages and lockfiles scanned, see the documentation:
https://help.aikido.dev/code-scanning/scanning-practices/support-for-dependency-scanning-by-language
Bringing the full SCA workflow into the IDE is part of a broader effort to surface essential checks where developers already write and ship code. The goal is to keep security signals fast, accurate, and close to the work. This now includes scanning dependencies and applying safe upgrades with AutoFix in the same place. We will continue expanding ecosystem coverage and improving the in-editor experience. The direction is simple: keep security close to the work and make it easier for teams to act on what they see.
Try SCA free in your IDE → https://help.aikido.dev/ide-plugins/features/open-source-dependency-scanning-sca-in-ide
Last updated on:
Jan 9, 2026
Secure your software now
Start today, for free.
Start for Free
No CC required
4.7/5
Tired of false positives?
Try Aikido like 100k others.
Start Now
Get a personalized walkthrough
Trusted by 100k+ teams
Book Now
Scan your app for IDORs and real attack paths
Trusted by 100k+ teams
Start Scanning
See how AI pentests your app
Trusted by 100k+ teams
Start Testing
March 24, 2026
•
Product & Company Updates
Lovable and Aikido bring pentesting into the platform, allowing builders to simulate real-world attacks and fix issues before shipping.

#
Announcements
#
AI Penetration Testing
March 12, 2026
•
Product & Company Updates
Betterleaks is a new open source secrets scanner from the creator of Gitleaks. A drop-in replacement with faster scans, token efficiency detection, configurable validation, and more.
February 26, 2026
•
Product & Company Updates
Aikido Infinite runs AI penetration testing on every code change, validates exploitability, generates patches, and retests fixes before code hits production, making self-securing software a reality.
#
AI Penetration Testing
#
Announcements
#
Self-securing Software
Secure your code, cloud, and runtime in one central system.
Find and fix vulnerabilities fast automatically.
No credit card required | Scan results in 32secs.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。