


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

让小产品的独立变现更简单 - ezindie.com
罗磊的独立博客
博客园 - 【当耐特】
M
MIT News - Artificial intelligence
月光博客
月光博客
博客园_首页
博客园 - 叶小钗
T
Tailwind CSS Blog
H
Hackread – Cybersecurity News, Data Breaches, AI and More
I
InfoQ
量子位
小众软件
小众软件
爱范儿
爱范儿
The GitHub Blog
The GitHub Blog
IT之家
IT之家
Jina AI
Jina AI
阮一峰的网络日志
阮一峰的网络日志
G
Google Developers Blog
WordPress大学
WordPress大学
人人都是产品经理
人人都是产品经理
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
J
Java Code Geeks
云风的 BLOG
云风的 BLOG
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报

Aikido Security's Blog

GlassWorm goes native: New Zig dropper infects every IDE on your machine Aikido Attack finds multiple 0-days in Hoppscotch The cybersecurity doomerism around Mythos doesn't match what we see on the ground axios compromised on npm: maintainer account hijacked, RAT deployed Popular telnyx package compromised on PyPI by TeamPCP Aikido × Lovable: Vibe, Fix, Ship CanisterWorm Gets Teeth: TeamPCP's Kubernetes Wiper Targets Iran TeamPCP deploys CanisterWorm on NPM following Trivy compromise Security testing is validating software that no longer exists Aikido Recognized by Frost & Sullivan with the 2026 Customer Value Leadership Award in ASPM GlassWorm Hides a RAT Inside a Malicious Chrome Extension fast-draft Open VSX Extension Compromised by BlokTrooper Glassworm Strikes Popular React Native Phone Number Packages Glassworm Is Back: A New Wave of Invisible Unicode Attacks Hits Hundreds of Repositories How Security Teams Fight Back Against AI-Powered Hackers Introducing Betterleaks, an open source secrets scanner by the author of Gitleaks Trump’s 2026 cybersecurity strategy: From compliance to consequence How does AI pentesting work with compliance? What continuous pentesting actually requires Rare Not Random: Using Token Efficiency for Secrets Scanning Persistent XSS/RCE using WebSockets in Storybook’s dev server Why Determinism Is Still a Necessity in Security WAF vs. RASP vs. ADR Introducing Aikido Infinite: A new model of self-securing software How Aikido secures AI pentesting agents by design Astro Full-Read SSRF via Host Header Injection How to Get Your Board to Care About Security (Before a Breach Forces the Issue) What is Slopsquatting? The AI Package Hallucination Attack Already Happening SvelteSpill: A Cache Deception Bug in SvelteKit + Vercel Top 6 Wiz Code Alternatives
Aikido x OWASP: 200 free credits for individual members
Mario Popescu · 2026-06-18 · via Aikido Security's Blog

Published on:

Jun 18, 2026

We partnered with OWASP to give every OWASP individual member 200 free Aikido credits to run Code Audit. In this blog article we explain who qualifies, how to claim the credits, and how to use them for a Code Audit

What the benefit gives you

Every OWASP individual member gets 200 Aikido credits to run Code Audit on their own codebase. The benefit went live on 18 June 2026 and runs for six months.

Who can claim

The benefit is open to OWASP individual members. You can only claim it with your @owasp.org email address, so make sure to have that ready before you start.

How to claim your credits

You claim the credits in two steps:

  1. Sign up to Aikido on https://app.aikido.dev/login using your @owasp.org email address.
  2. Once you are in, send the message AIKIDO💜OWASP26 in the in-app chat. Our team will manually add the 200 credits to your account.

If you already signed up with a different email, sign up again with your @owasp.org address so we can match you to the benefit.

What Code Audit does

Code Audit reads your source code and reasons through it the way an attacker would, following references across files and modules to find the multi-step, logic-layer issues where no single line is the vulnerability. It catches things like IDOR, broken access control, and business logic flaws.

What you can run with the credits

Because Code Audit works on your codebase, you do not need a live application or auth credentials to start. Connect a repository and start an audit. The set-up takes a few minutes, and code audits run in a couple of minuutes, depending on the codebase size and its complexity.
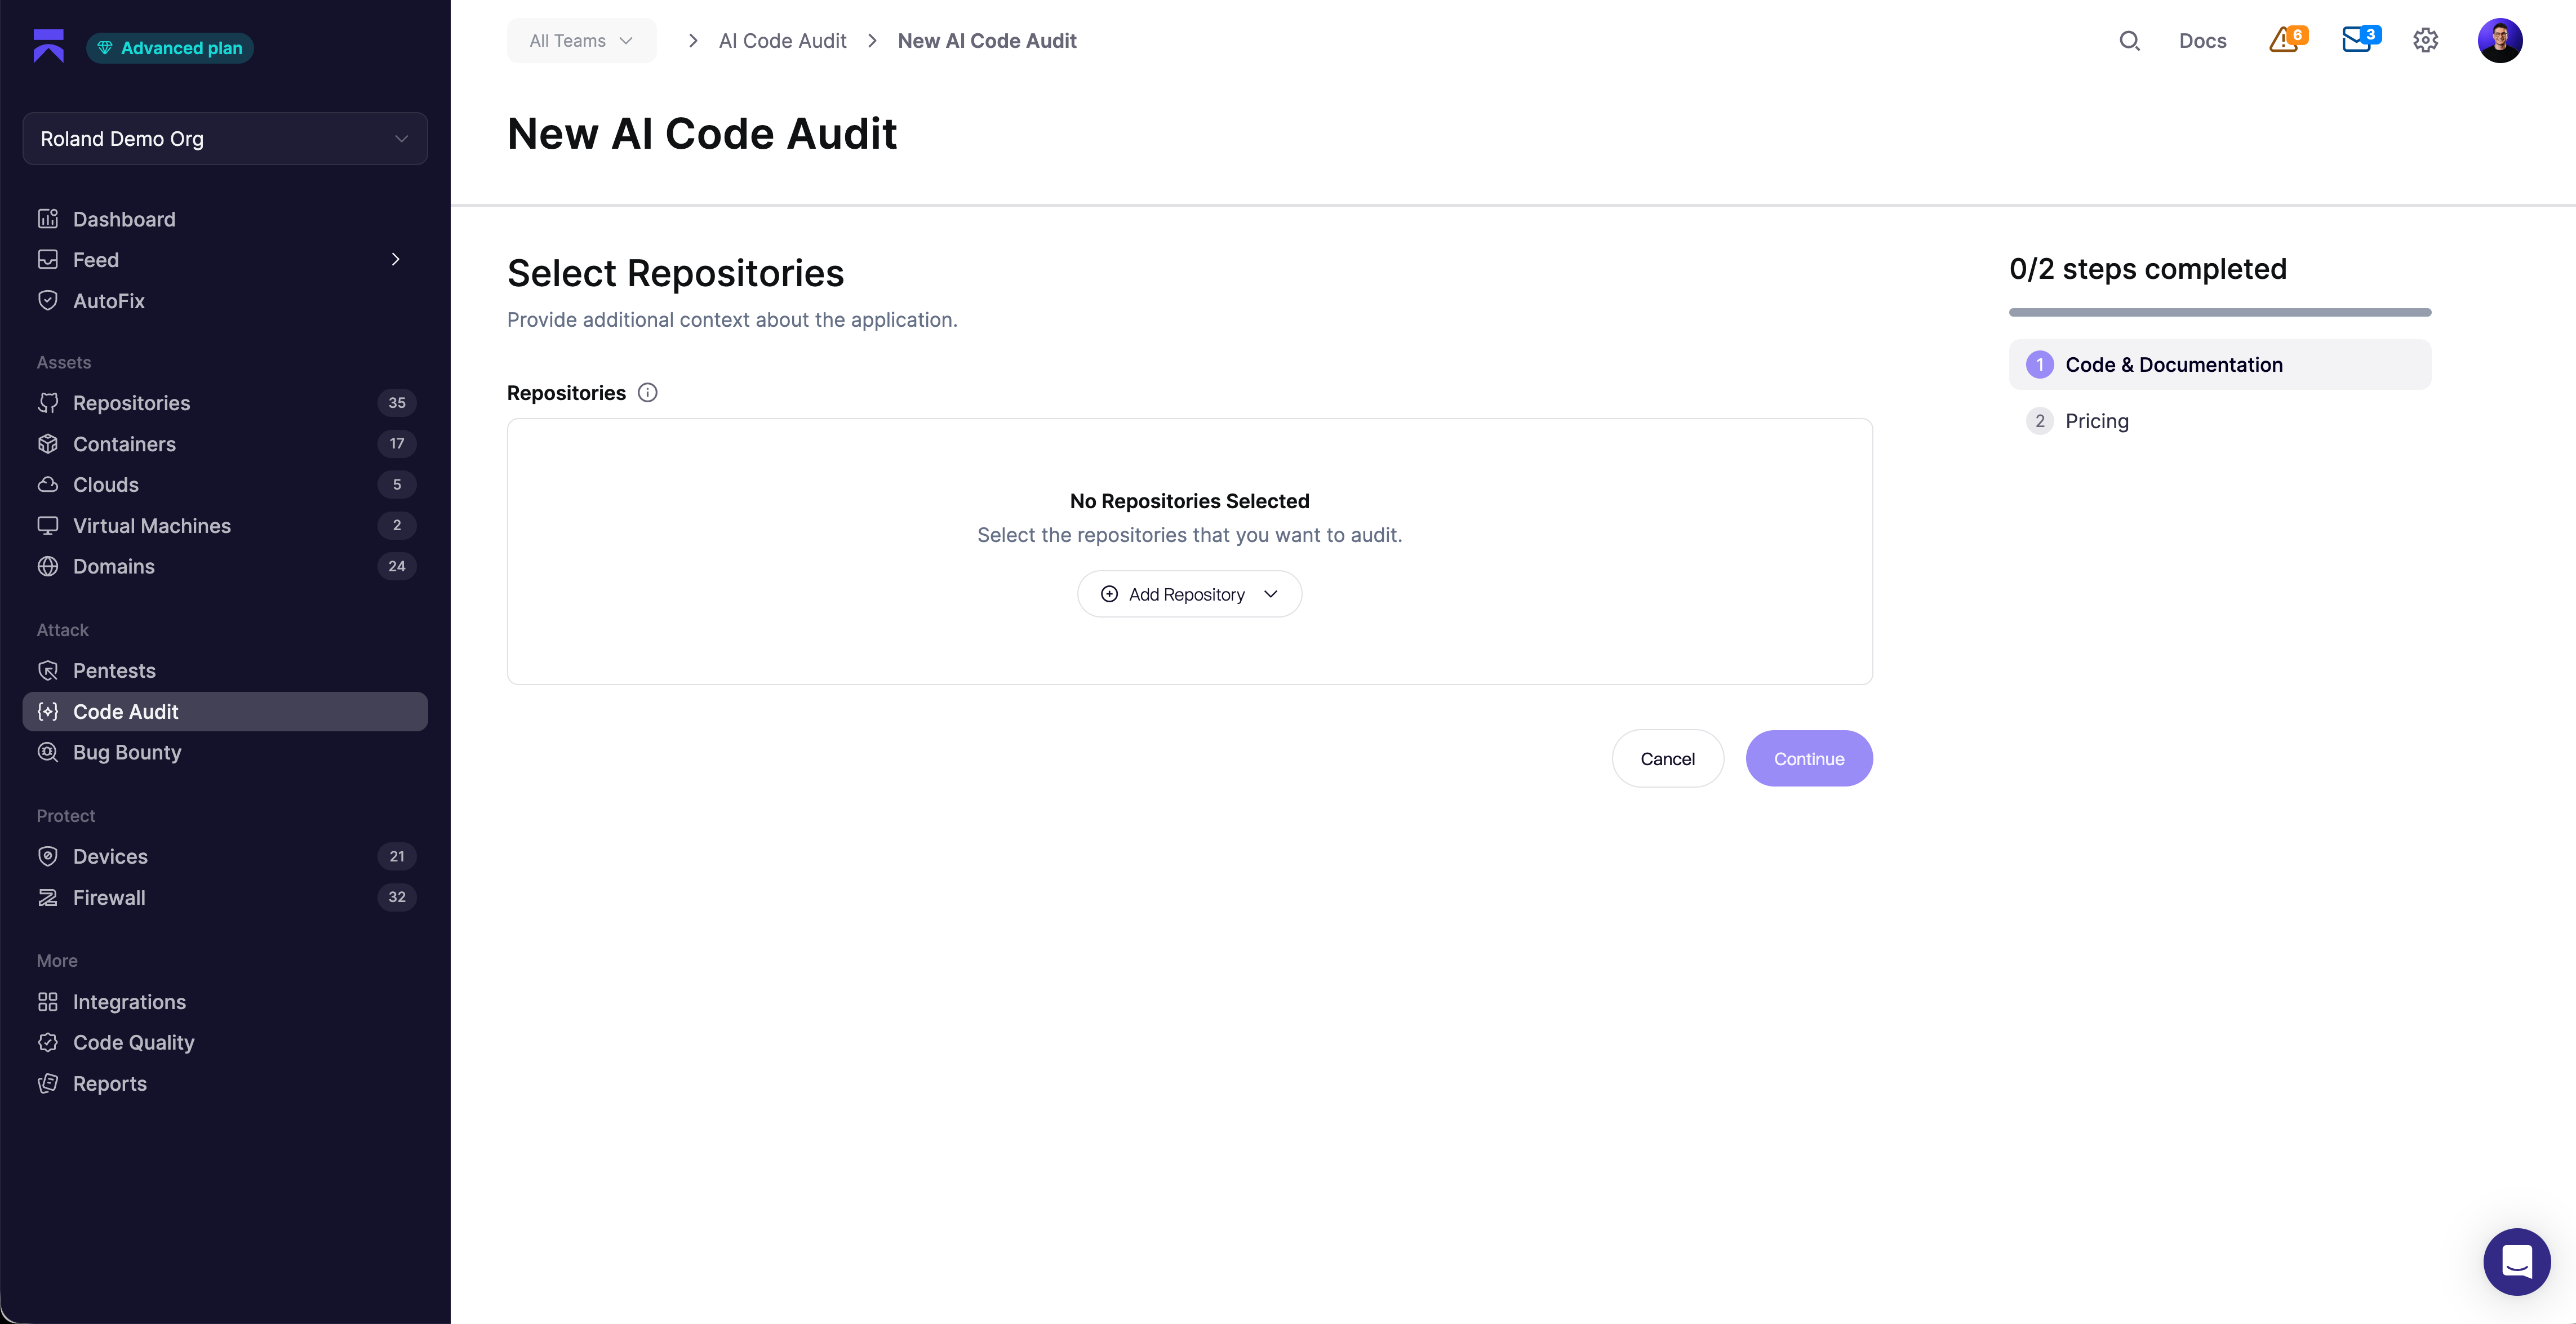
Cost per audit depends on the size and complexity of the repositories you select, and Aikido estimates the credit total before each audit begins.

Last updated on:

Jun 20, 2026

Tired of false positives?

Try Aikido like 100k others.

Start Now

Get a personalized walkthrough

Trusted by 100k+ teams

Book Now

Scan your app for IDORs and real attack paths

Trusted by 100k+ teams

Start Scanning

See how AI pentests your app

Trusted by 100k+ teams

Start Testing

Product & Company Updates

Introducing Code Audit: Find complex vulnerabilities hidden in your source code

SAST catches patterns. Code Audit reasons through your code like an attacker would, finding the logic flaws that only show up after you ship.

Product & Company Updates

Aikido x Docker: less noise, more signal in your containers

Aikido now supports Docker Hardened Images with built-in VEX integration, helping teams reduce CVE noise and focus on container vulnerabilities that actually need attention.

Product & Company Updates

One year of Opengrep: What we built and what’s next

A year after forking Semgrep, Opengrep is faster, supports deeper taint analysis, and produces consistent, reproducible results.

Get secure now

Secure your code, cloud, and runtime in one central system.
Find and fix vulnerabilities fast automatically.

No credit card required | Scan results in 32secs.
