






Published on:
Jun 16, 2026
TL;DR: Aikido Code Audit fills the gap between SAST and pentesting by reasoning through your static codebases to surface multi-step, intent-dependent vulnerabilities before they ship.
Last week Anthropic released Claude Fable 5, a public version of their Mythos-class model, which was able to discover and chain zero-day exploits. Fable 5 ships with guardrails that block cybersecurity queries and fall back to a more limited model, so the public version doesn't run those attacks for you.
At least that was the idea.
But it appears 1 or more organizations have successfully jail-broken Fable 5, causing Anthropic to withdraw the model under pressure from the US government. The thing is, you can't put the genie back in the bottle. Whether through jail breaks or open source, attacker will gain access to increasingly capable models.
The direction is set. The skill and time it took to find and chain flaws across a application is collapsing into something an agent does without hours or days of human effort. This is particularly true for logic-based flaws not covered by existing static code analysis engines. These classes of flaws don't follow predictable patterns, so static analysis has nothing to match against.
But defenders can stay ahead using the same agentic models by analyzing and catching security flaws in their codebases before they make it to production. And that's why we built Aikido Code Audit.
Code Audit is not a replacement for your SAST engine, which is great at finding rules-based security vulnerabilities as you develop. It's also not a replacement for pentests. It sits between the two, working on your static code, with pentest-grade reasoning.
Reach for Code Audit before a significant release or after a major feature lands. It follows references across files and modules. It surfaces multi-step issues where no single line is the vulnerability. Each finding comes back with root cause, code-based evidence, and an AutoFix that lets you instantly generate a PR to resolve the issue.
In practice, this looks like:
A multi-step IDOR chain across three files that a pattern-based scanner would never connect, because no individual line triggers a rule. Code Audit traces the reference, follows the missing authorization check in context, and surfaces the full exploit path.
The same concept applies to other logic based vulnerabilities like a ReDoS pattern identified from source without live exploitation, or an admin-only route that's never been exercised by a live pentest because no one had valid credentials. I'm sure you can think of other examples.

Because Code Audit works on your source code, you don't need an active staging environment or to create auth credentials. Just connect your codebase and start an audit. If the code exists in source, it's in scope: multiple repos, feature-flagged paths, undeployed changes, and admin routes that live tests can't safely touch.
Code Audit reasons through static source rather than probing a live environment, it isn't constrained by SAST rule coverage or by which platform your code runs on.
That means you can test:
Based on our internal testing and early users, Code Audit covers roughly 70-80% of what a full pentest engagement surfaces, at around 10x lower cost. Early users have found ~25 security issues per codebase (median), with 0 audits coming back clean.
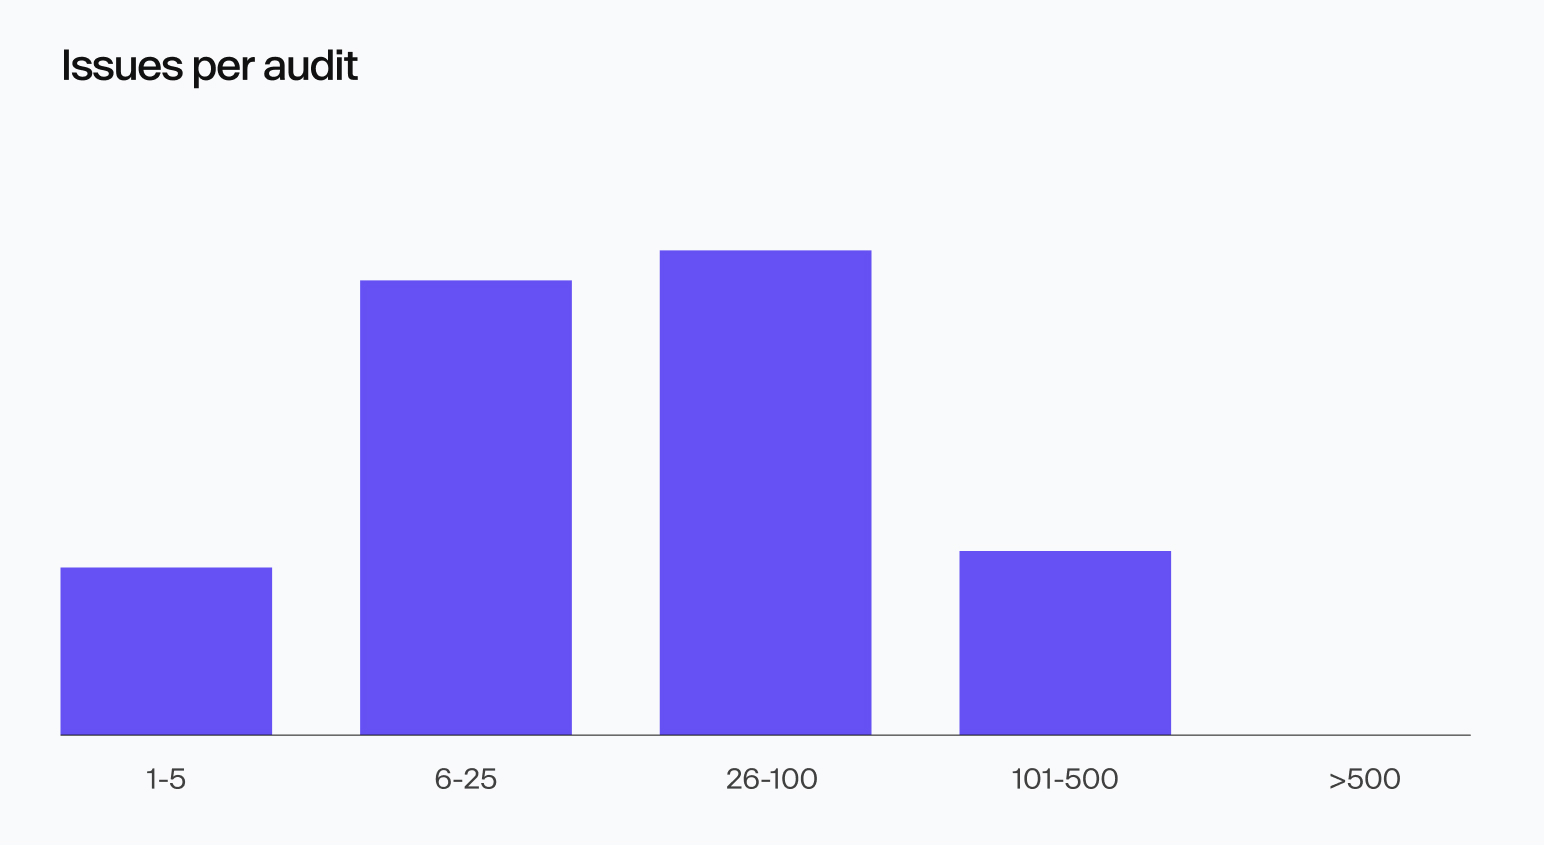
But the number of issues found is secondary to the timing. Finding a vulnerability before release only costs a code change while the developer is still context-aware. Finding it after it reaches production, likely costs a remediation cycle and pulling a developer from another project to fix it. Code Audit moves discovery to the moment before the code ships, when the developer who worked on it still has full context and the fix is straightforward.
From your Aikido account, select Code Audit from the menu and click Create Audit. From there you select 1 or more repositories and Aikido estimates the cost in credits. Add credits to your account and start the audit. It only takes a few minutes to set up and audits take as little as 5 minutes, based on your codebase size and complexity.
Run your first Code Audit.
Last updated on:
Jun 19, 2026
Tired of false positives?
Try Aikido like 100k others.
Start Now
Get a personalized walkthrough
Trusted by 100k+ teams
Book Now
Scan your app for IDORs and real attack paths
Trusted by 100k+ teams
Start Scanning
See how AI pentests your app
Trusted by 100k+ teams
Start Testing
•
Product & Company Updates
Aikido now supports Docker Hardened Images with built-in VEX integration, helping teams reduce CVE noise and focus on container vulnerabilities that actually need attention.

•
Product & Company Updates
A year after forking Semgrep, Opengrep is faster, supports deeper taint analysis, and produces consistent, reproducible results.
•
Product & Company Updates
AI agents writing your code. Aikido integrates directly into AWS Kiro's agentic workflow to keep security in the loop, automatically, from the first line. Aikido is AWS's first global security partner for Kiro.
Secure your code, cloud, and runtime in one central system.
Find and fix vulnerabilities fast automatically.
No credit card required | Scan results in 32secs.


此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。