


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

B
Blog RSS Feed
量子位
Recent Announcements
T
The Blog of Author Tim Ferriss
美团技术团队
Cyber Security Advisories - MS-ISAC
Blog — PlanetScale
Blog — PlanetScale
H
Help Net Security
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
博客园 - Franky
让小产品的独立变现更简单 - ezindie.com
宝玉的分享
宝玉的分享
大猫的无限游戏
大猫的无限游戏
V
Visual Studio Blog
博客园 - 聂微东
aimingoo的专栏
aimingoo的专栏
Microsoft Security Blog
U
Unit 42
J
Java Code Geeks
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
IT之家
IT之家
Hugging Face - Blog
Hugging Face - Blog
腾讯CDC
L
LangChain Blog

Aikido Security's Blog

Axios CVE-2026-40175: a critical bug that’s… not exploitable GlassWorm goes native: New Zig dropper infects every IDE on your machine Aikido Attack finds multiple 0-days in Hoppscotch The cybersecurity doomerism around Mythos doesn't match what we see on the ground axios compromised on npm: maintainer account hijacked, RAT deployed Popular telnyx package compromised on PyPI by TeamPCP Aikido × Lovable: Vibe, Fix, Ship CanisterWorm Gets Teeth: TeamPCP's Kubernetes Wiper Targets Iran TeamPCP deploys CanisterWorm on NPM following Trivy compromise Security testing is validating software that no longer exists Aikido Recognized by Frost & Sullivan with the 2026 Customer Value Leadership Award in ASPM GlassWorm Hides a RAT Inside a Malicious Chrome Extension fast-draft Open VSX Extension Compromised by BlokTrooper Glassworm Strikes Popular React Native Phone Number Packages Glassworm Is Back: A New Wave of Invisible Unicode Attacks Hits Hundreds of Repositories How Security Teams Fight Back Against AI-Powered Hackers Introducing Betterleaks, an open source secrets scanner by the author of Gitleaks Trump’s 2026 cybersecurity strategy: From compliance to consequence How does AI pentesting work with compliance? What continuous pentesting actually requires Rare Not Random: Using Token Efficiency for Secrets Scanning Persistent XSS/RCE using WebSockets in Storybook’s dev server Why Determinism Is Still a Necessity in Security WAF vs. RASP vs. ADR Introducing Aikido Infinite: A new model of self-securing software How Aikido secures AI pentesting agents by design Astro Full-Read SSRF via Host Header Injection How to Get Your Board to Care About Security (Before a Breach Forces the Issue) What is Slopsquatting? The AI Package Hallucination Attack Already Happening SvelteSpill: A Cache Deception Bug in SvelteKit + Vercel
Safe Chain now enforces a minimum package age before install
2025-11-28 · via Aikido Security's Blog

The last few months have made something clear. Attackers are not guessing anymore. They are watching how developers install dependencies and they are using timing itself as an attack vector. Fresh versions are where attackers strike first and they strike fast.

So we upgraded Safe Chain to close that window.

Safe Chain now enforces a minimum package age, holding any version published in the last 24 hours so it can be analysed properly before install. Fresh releases are the easiest place for attackers to hide, so this window gives security tools enough time to analyse them. If a version is too new and not yet verified, Safe Chain automatically falls back to an older clean version. It does not break builds. Safe Chain is free, open source and runs locally.

This change makes Safe Chain the safe default for developers.

Why attackers focus on fresh versions

Across incidents in 2025, attackers consistently used newly published versions as their first point of infection. This pattern shows up across malware campaigns, and fresh releases work for attackers because:

  • new versions blend into normal maintenance and developers trust them
  • CI systems pull the latest version immediately
  • registries, sandboxes and security teams need time to analyse new code
  • transitive dependency chains spread the malicious version quickly

These behaviours were visible in real incidents this year including the Shai Hulud waves in September and November, the React Native Aria compromise, the XRP backdoor event, the rand-user-agent RAT and multiple maintainer-token hijacks that all started with a new release.

In every major incident we flagged this year, the malicious versions appeared as newly published releases before anyone had time to review or flag them.

Why we introduced a minimum package age

Fresh versions became the biggest blind spot in the npm ecosystem. Attackers repeatedly exploited that timing gap because it works. Our threat pipeline sees the same pattern every week: a new malicious version is published, CI pipelines or developer machines pull it instantly, and exfiltration begins long before the wider community notices anything suspicious.

Introducing a minimum 24-hour age gives defenders the time needed to classify and verify releases. During that period Safe Chain checks whether:
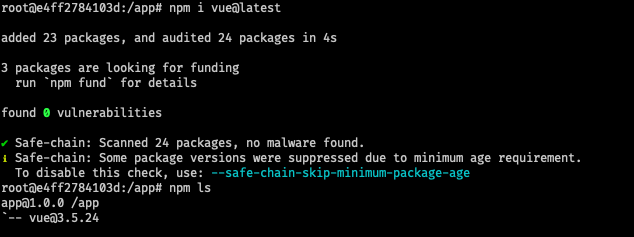
  • the version is known to Aikido Intel
  • it has passed malware scanning
  • it is linked to an active threat pattern or incident

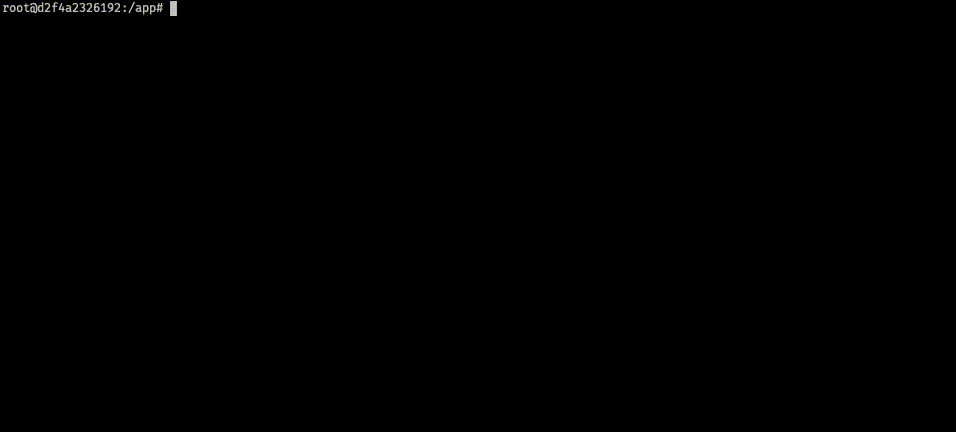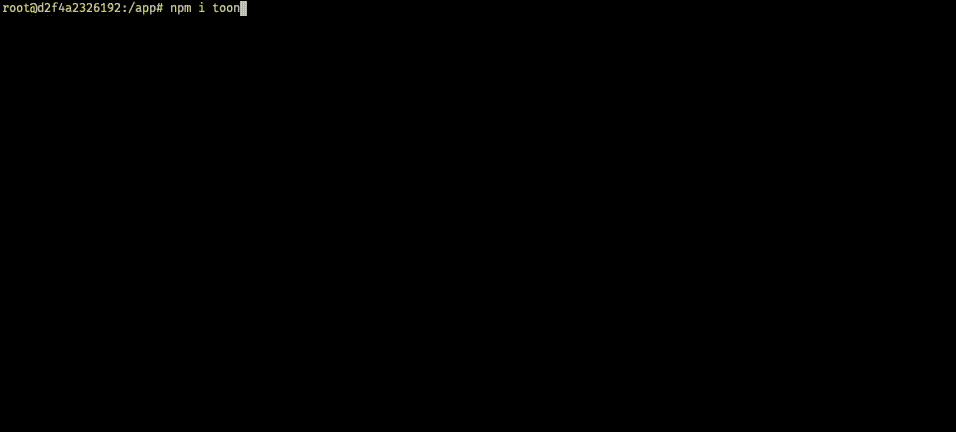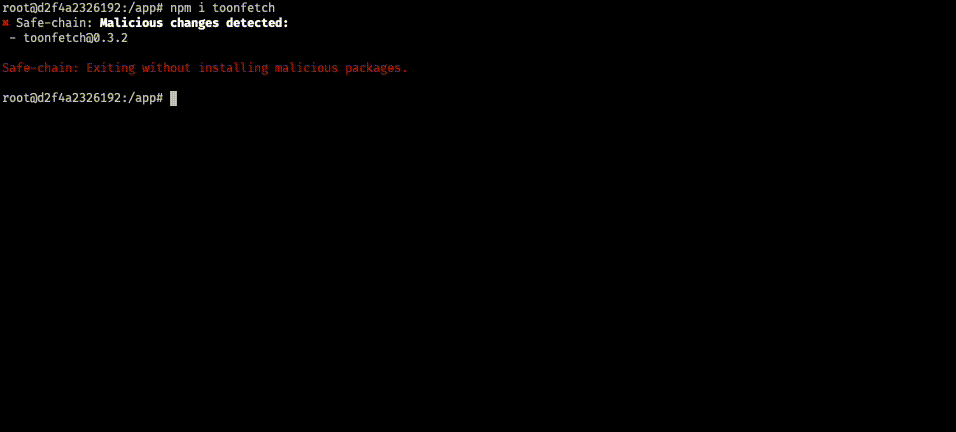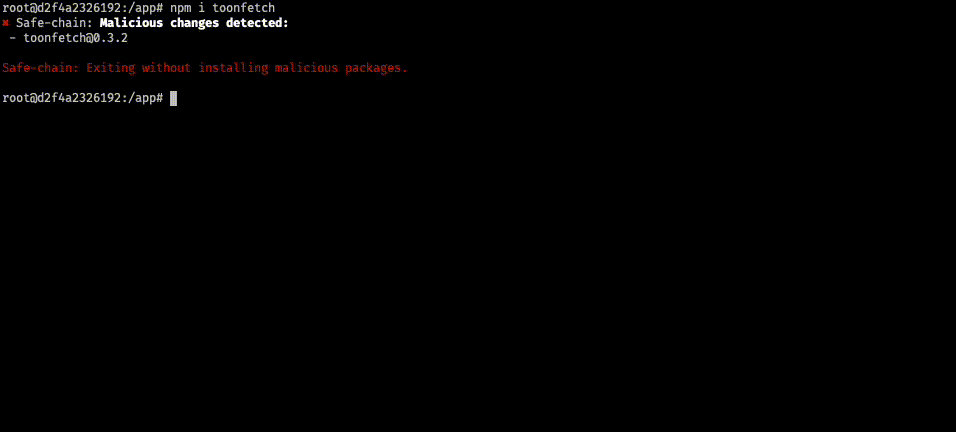
If verification is incomplete, Safe Chain suppresses the version temporarily and falls back to the last safe one. This already prevented installs of active Shai Hulud malware including compromised packages such as toonfetch, which remained live on npm at the time of testing.
Safe Chain is the safe default for devs

Developers should not have to track malware campaigns or manually review every dependency update. Tooling should handle that automatically.

Safe Chain now gives you a stronger baseline while staying out of your way:

  • blocks malicious packages before install
  • suppresses versions less than 24 hours old until verified
  • falls back to the last clean version automatically
  • works with npm cli, npx, yarn, pnpm, pnpx, Bun, bunx and pip
  • free, open source, no tokens or configuration

Safe Chain is powered by Aikido Intel, our threat pipeline that identifies around 200 malicious packages per day before they appear in public vulnerability databases. Other tools detect malware after install. Safe Chain stops it before it reaches your machine.

This is how package ecosystems should work by default. Safe Chain brings that model directly into the developer workflow.

Installing the Aikido Safe Chain is easy. You just need 3 simple steps:

Install the Aikido Safe Chain package globally using npm:

npm install -g @aikidosec/safe-chain

Setup the shell integration by running:

safe-chain setup

❗Restart your terminal to start using the Aikido Safe Chain.

  • This step is crucial as it ensures that the shell aliases for npm, npx, and yarn are loaded correctly. If you do not restart your terminal, the aliases will not be available.

Verify the installation by running:

npm install safe-chain-test

  • The output should show that Aikido Safe Chain is blocking the installation of this package as it is flagged as malware. (Installing this package does not have any risks)