


The calculus of cybersecurity has changed. AI is reshaping how organizations build, deploy, operate, and defend digital systems. AI-powered development tools, agents, and autonomous workflows are accelerating innovation but they are also introducing new attack surfaces, new trust boundaries, and new security challenges.
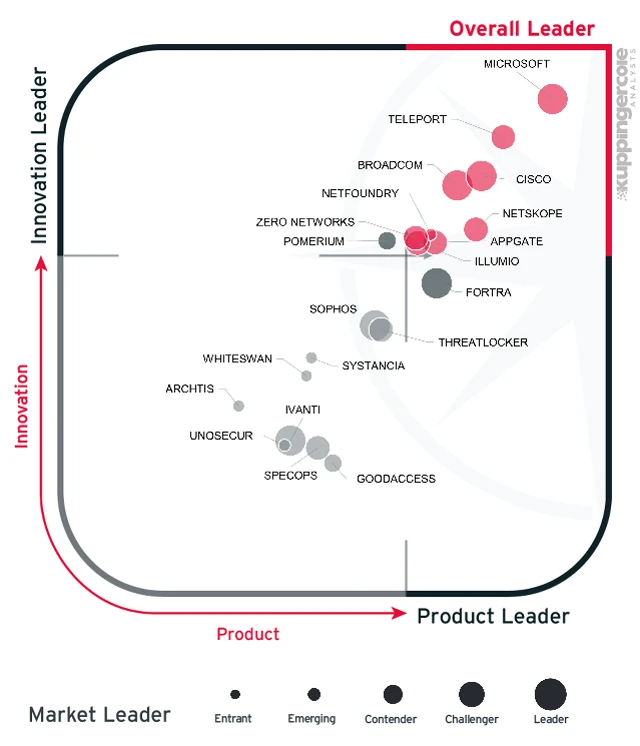
Microsoft has long helped organizations secure their digital estates using Zero Trust principles. That leadership was recently recognized by KuppingerCole analysts, which named Microsoft as the Overall Leader in its Zero Trust Platform Leadership Compass, ranking Microsoft highest for both product and innovation leadership.
As organizations accelerate AI adoption, secure software development becomes more important than ever. That’s why we are expanding the Zero Trust for AI strategy with two major additions: a new AI-focused Zero Trust Assessment experience and a new DevSecOps pillar in the Zero Trust Workshop. Together, they help organizations get ready for AI by assessing exposure, risks, prioritizing remediation, and securing AI-enabled development from source code to deployment.
This builds directly on the Zero Trust for AI strategy announced at RSA Conference 2026 and moves the conversation from architecture to implementation. If that announcement was about establishing Zero Trust for AI, this one is about operationalizing it: giving security, engineering, and platform teams the specific controls they need to act.
To learn more about our work in applying Zero Trust for AI and agents watch this Microsoft Mechanics video:
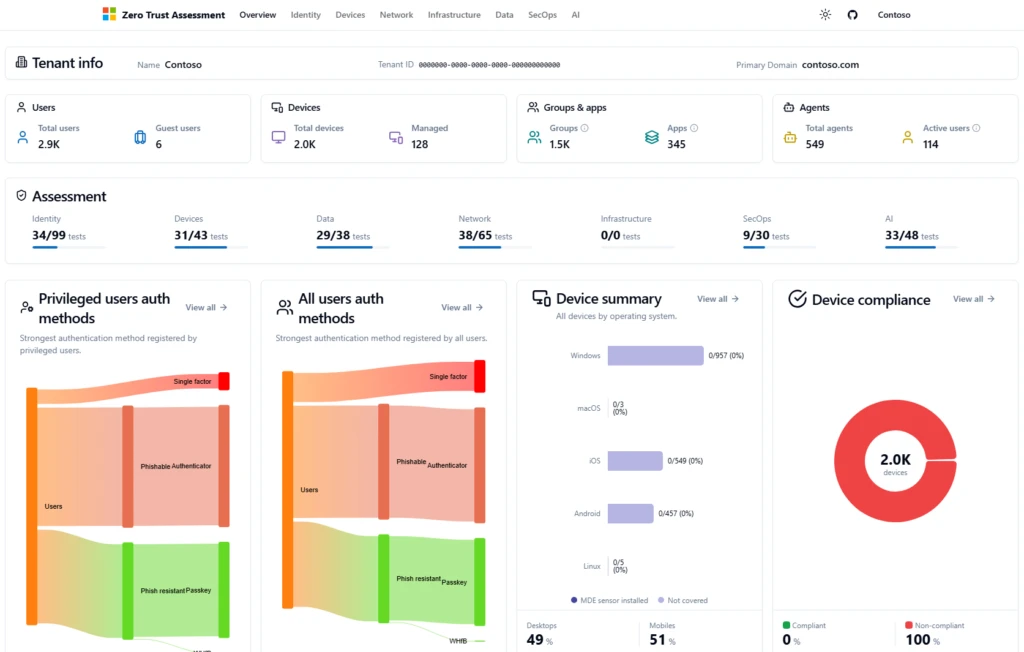
The Zero Trust Assessment provides an automated view of security posture by evaluating tenant configuration and activity signals across the environment and translating those findings into prioritized recommendations. As organizations adopt AI agents, Copilots, developer tools, and autonomous workflows, the Assessment helps security and platform teams establish a baseline, measure progress, and identify gaps across both traditional and AI-powered environments. It now includes expanded coverage with new pillars for AI, Security Operations, and Infrastructure (in addition to existing Identity, Devices, Network, and Data pillars), with Zero Trust for AI-focused checks that help organizations evaluate the controls required for secure AI adoption.
Additionally, enhanced reporting delivers both practitioner-level guidance and executive-ready summaries that communicate risk, progress, and next steps. Results map directly into the Zero Trust Workshop’s First, Then, Next framework, transforming assessment findings into a prioritized roadmap for remediation and implementation. Together, the Assessment and Workshop help organizations move from understanding risk to executing a structured plan for continuous improvement across their Zero Trust and AI security journey.
AI is fundamentally changing software development. Developers increasingly rely on AI assistants to generate code, recommend packages, create infrastructure configurations, and automate testing. While these capabilities accelerate delivery, they also amplify the consequences of governance gaps, excessive permissions, insecure dependencies, and compromised supply chains.
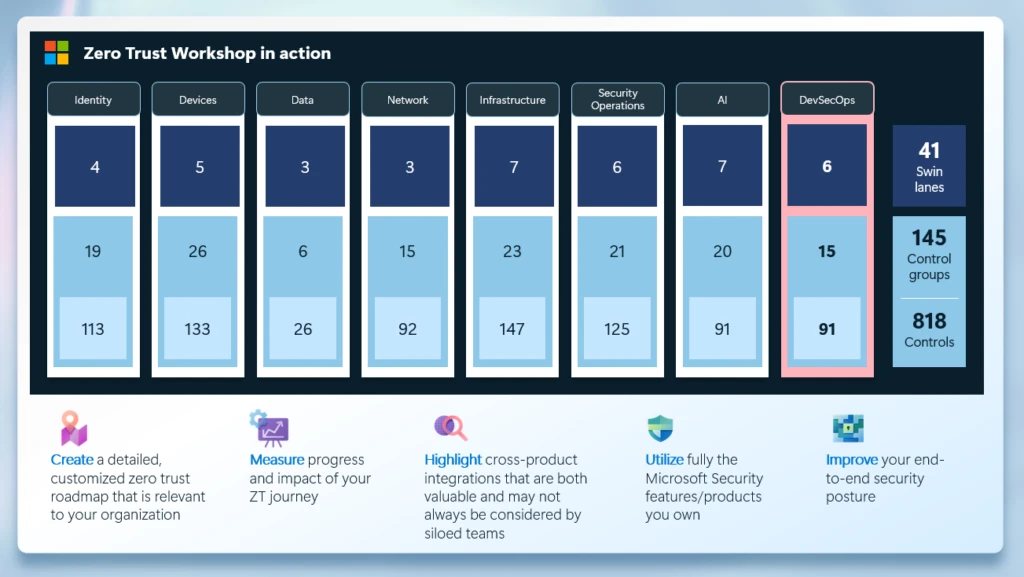
That is why Microsoft is introducing a new DevSecOps pillar (with 15 control groups and 91 tasks that help teams apply Zero Trust from source code to cloud deployment) in the Zero Trust Workshop. The pillar translates the three Zero Trust principles—verify explicitly, use least privilege, and assume breach—into practical guidance and controls for developer platforms, continuous integration and continuous delivery (CI/CD) pipelines, source repositories, dependencies, artifacts, and infrastructure-as-code.
The Zero Trust Workshop also improves the AI pillar to include guidance based on the Microsoft AI Memory framework, helping teams treat memory as a governed security boundary with clear intent, provenance, lifecycle visibility, and user control.
The Zero Trust Workshop follows a simple three-step motion: plan the right pillars and stakeholders, run the Zero Trust Assessment to establish a baseline, and use the facilitated workshop to turn findings into a 12- to 24-month roadmap.
Tasks are organized into First, Then, Next phases so teams can start with foundational controls and build momentum. The new DevSecOps pillar also highlights cross-pillar work that strengthens Identity, Infrastructure, and Security Operations, plus four tasks focused directly on AI-assisted development: code governance, tool allowlisting, data protection, and AI and machine learning pipeline supply-chain security.
To help organizations navigate this shift, Microsoft recently published Zero Trust for AI: Rebuilding security controls for autonomous and agentic systems, a practical guide that applies Zero Trust principles to AI agents, tools, memory, data, and runtime operations. The e-book provides security leaders, architects, and practitioners with a framework for evaluating AI risks and implementing controls that scale with AI adoption.
Knowing what to do is one thing. Knowing how to operationalize it at scale is another. Our patterns and practices provide repeatable, proven approaches to the most complex AI security challenges, much like software design patterns offer reusable solutions to common engineering problems.
The table below highlights our practical recommendations aligned with Zero Trust principles to help practitioners translate strategy into concrete implementation.
| Pattern and Practice Guidance | What it covers |
|---|---|
| Least privilege for AI agents | Guidance on applying Zero Trust to AI agents. |
| Zero Trust for source code access | Guidance on building Zero Trust protections for source code security. |
| Manage memory safety in agentic systems | Guidance for treating AI memory as a governed security boundary. |
| Protect the software supply chain | Guidance for applying Zero Trust across the software development lifecycle. |
| Security adoption guidance for development | Guidance on building secure development programs and governance. |
Partners can use the Zero Trust Assessment tool and Workshop to turn broad security interest into a focused, outcome-driven customer engagement. The Assessment tool helps establish a baseline across one or more Zero Trust pillars, including AI and DevSecOps scenarios, so customers can see where they are today and where to prioritize first. The Workshop then translates those findings into an executive summary, prioritized recommendations, and a phased roadmap. For customers, this creates a clear path from risk visibility to practical action plans that partners—as trusted advisors—can help prioritize and execute.
Learn how Microsoft partners deliver the Zero Trust Workshop through Frontier Accelerate for Security: Envisioning and POC.
Ford Motor Company: Microsoft Security solutions offered Ford a unified, AI-powered platform to detect, address, and prevent cyberthreats across its hybrid environment. Grounded in a Zero Trust architecture, every access request—whether from users, devices, or applications—is continuously verified. This principle guided Ford’s approach to securing its hybrid environment, reinforcing protection before expanding visibility. Read more about how Ford builds trust across global operations.
The Microsoft security stack is more than technology. It contributes to Ford’s business in moving faster against cyberthreats and building a more secure future.”
—Weston Maggetti, Platform Manager, Ford Motor Company

SEB Group: SEB based its Zero Trust journey on identity, deploying Microsoft Entra ID and Microsoft Defender for Identity. It removed online identity exposure with Windows Hello for passwordless access, and extended protection with Microsoft Defender for Endpoint. Read more about how SEB implements Zero Trust.
Our Microsoft Security solutions are vital to our Zero Trust journey. That enhanced visibility helps to keep our SaaS (software as a service) landscape as simple as possible so that it’s easier to defend.”
—Ulf Larsson, Security Chief Technology Officer (CTO), SEB Group
To get started, use the Assessment and Workshop together to turn Zero Trust for AI into a practical implementation plan:
Learn more about Microsoft Security solutions on our website and bookmark the Microsoft Security blog for expert insights on security matters. Follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest cybersecurity news and updates.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。