


Update: this post generated some interesting discussion on Hacker News.
Friendly fraud is the laundered name for something that the payment system is not really able to prevent. Even though I’m pretty sure they can do way better. Particularly big and sophisticated payment providers like Stripe, with a mountain of signals.
I had a customer buy my product twice. It’s called Ciglue. It’s cigar glue. Not Rolex or iPhone. The first order was shipped with DHL and delivered, with proof of delivery. The customer didn’t contact to request a refund or a re-delivery, but I saw a dispute filed, so I reached out to them.
They said it was the bank’s mistake because the bank bundled this payment with some real fraudulent transactions from the Philippines. They promised to contact their bank and even offered to pay me back via Paypal. I was happy that it’s just a misunderstanding. I submitted the evidence of the delivery, customer communication, website policies, everything by the book.
It turned out the customer was doing it on purpose, and lying to me. They not only didn’t contact the bank to correct the situation, they actually pretended not to have received the product. And the bank, naturally, sided with them. I had no recourse. Dispute granted. Money, product, shipping and dispute fees, all gone. This is annoying, but not exactly unheard of. If you sell online, you probably know the feeling: you send the product, collect the evidence, submit everything properly, and then somehow still lose.
Before the dispute came in, the same customer placed another order, this time with untracked shipping, and a few days after the first dispute, another dispute followed. Once the first dispute was granted, things became clear. The customer emailed me to gloat about their clever scheme. Literally giving me the finger.
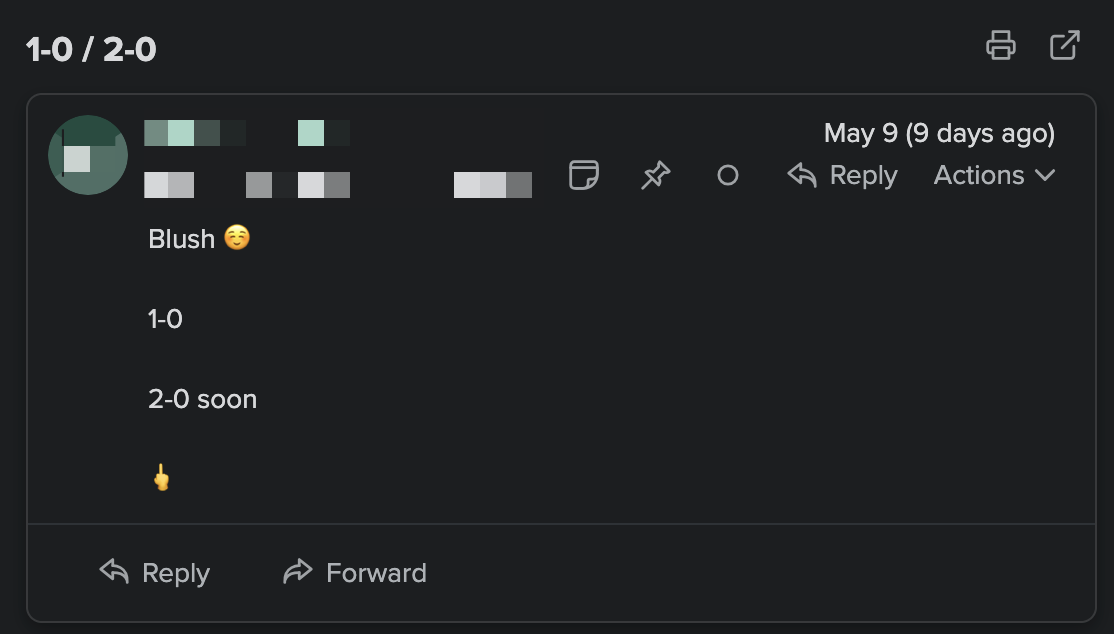
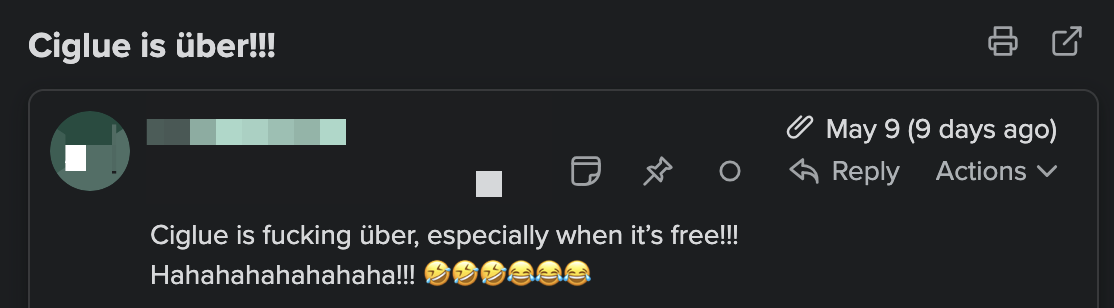
I sent the screenshots to Stripe and asked if this could be reported properly. To the bank, to some fraud reporting network, or even just internally inside Stripe.
I wasn’t expecting Stripe to recover the money or reverse a closed dispute. I understand that the customer’s bank makes the final decision, and that card network rules are what they are. But I did expect the report itself to matter. This is a very clear case of “friendly fraud”. The card belonged to the customer, the address was valid etc. The customer appeared to enjoy screwing me over. Pretty sad considering this is a pretty cheap product in a niche hobby. But still.
I would have expected Stripe to use this evidence in some way to feed into the sophisticated machine-learning anti-fraud system. But No.
After quite a bit of back and forth, Stripe’s answer seems to be that it doesn’t really matter beyond my own account.
They told me they don’t use evidence of chargeback abuse from one merchant to create cross-merchant fraud signals, or to take action against the customer’s card, email, or other details for other merchants.
You probably don’t want a system where one annoyed merchant can get someone blocked across the whole Stripe payment system. But there’s a pretty big gap between “automatically block this person everywhere” and “thanks for the screenshots, please consider Radar”, and this is where it gets frustrating.
Stripe sells Radar on the strength of its network: lots of payments, lots of signals, better fraud detection, machine learning, etc. Stripe sees a lot of transactions, so in theory it can spot things that an individual merchant can’t. But when a merchant sends actual evidence that a customer is abusing chargebacks, suddenly it means nothing. The recommended solution is to use Radar rules to block the customer from buying from me again. And I probably have to upgrade and pay Stripe to use this rule anyway. Gee thanks!
The next merchant still starts from zero. This is also not the kind of fraud Radar can easily solve before the payment. The transaction looked fine, checks passed, physical address matched. The abuse happened later, through the dispute process. There is no clever checkout rule for “customer receives the product and later lies to their bank”.
Small merchants already have very little leverage in disputes: the bank decides, Stripe points at the bank, and I lose the money, the product, the dispute fee, and the time spent dealing with it all. If new evidence appears later, it may be too late to submit. If the customer does the same thing elsewhere, and something tells me this isn’t this person’s first rodeo, then the next merchant gets to get suckered.
Nothing friendly about this. Besides perhaps Stripe effectively being friendly with the fraudsters here by not doing anything about it.