


As organizations adopt AI-assisted development and increase their release velocity, they are not only generating more code but also finding more vulnerabilities from static analysis. The traditional remediation workflow of manually triaging issues, creating tickets, and opening individual pull requests (PRs) cannot keep pace. Fixing tens of thousands of vulnerabilities one by one is not a viable remediation strategy.
To help remediate vulnerabilities at scale, Datadog is introducing Bits AI Dev Agent for Code Security. Built into Datadog Code Security, the Dev Agent can automatically generate fixes for vulnerabilities in your codebase and open PRs on your behalf for review.
This post explains how Bits AI Dev Agent for Code Security helps you:
Reduce vulnerability backlogs more efficiently
Maintain control and visibility over automated remediation
Scale your vulnerability management practices with AI
Datadog Static Code Analysis (SAST) continuously scans your source code repositories to identify vulnerabilities, using a combination of rule-based and AI-native scans. It filters out false positives and highlights high-confidence issues mapped to Common Weakness Enumeration (CWE) entries in the OWASP Top 10.
As development accelerates with AI-generated code, the volume of findings tends to increase just as quickly. Bits AI Dev Agent helps teams keep pace by generating fixes, both for individual findings and for batches of vulnerabilities.
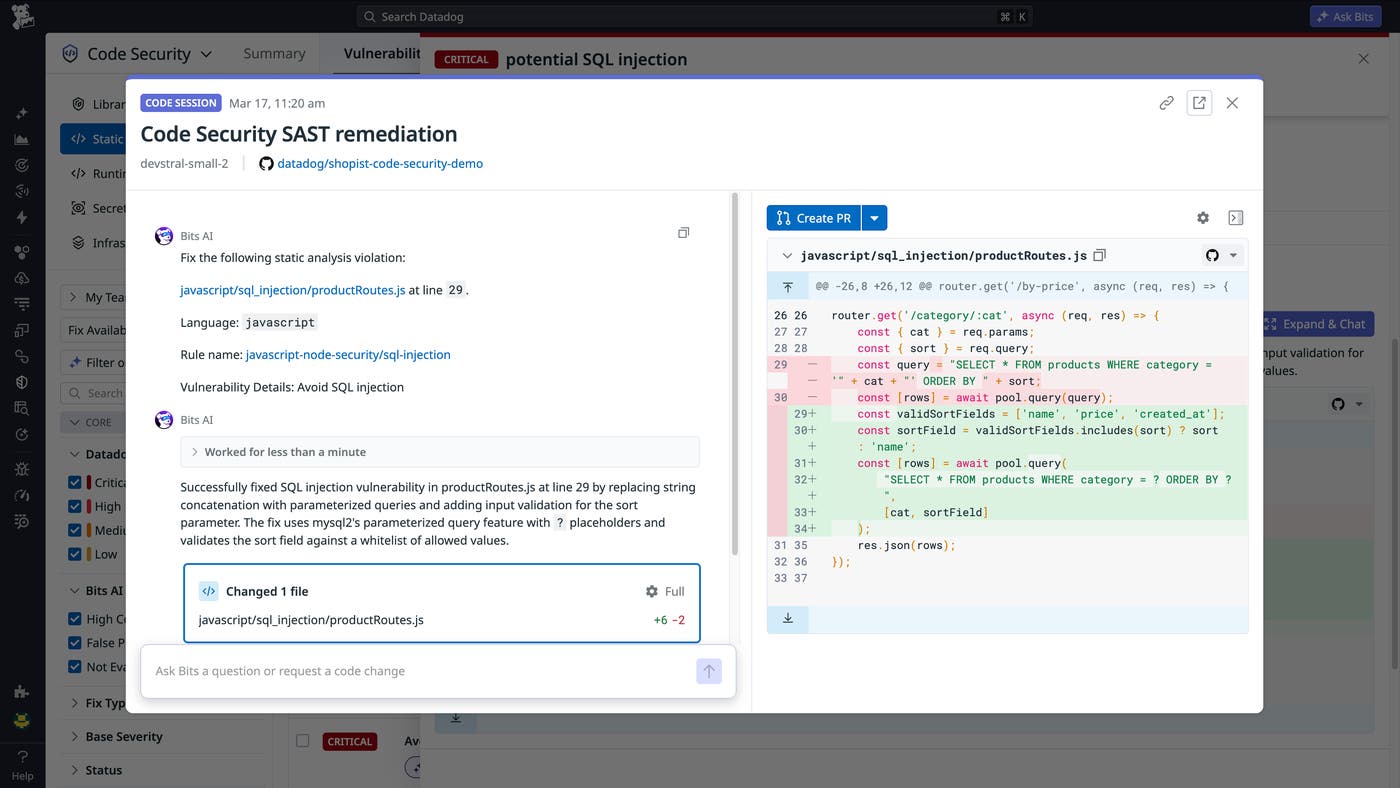
When reviewing a SAST finding, you can generate a fix directly from Bits AI Dev Agent. For supported high-confidence vulnerabilities, fixes can be pre-generated and made ready for review. This gives security engineers a fast way to assess a proposed remediation before involving a developer.
If you want to refine the proposed change, you can expand the session and interact with the Dev Agent to adjust the fix. Once you’re satisfied, you can create a GitHub PR directly from the interface. Instead of filing a ticket and waiting for someone to pick it up, you can provide developers with concrete, code-level changes that they can review and merge.
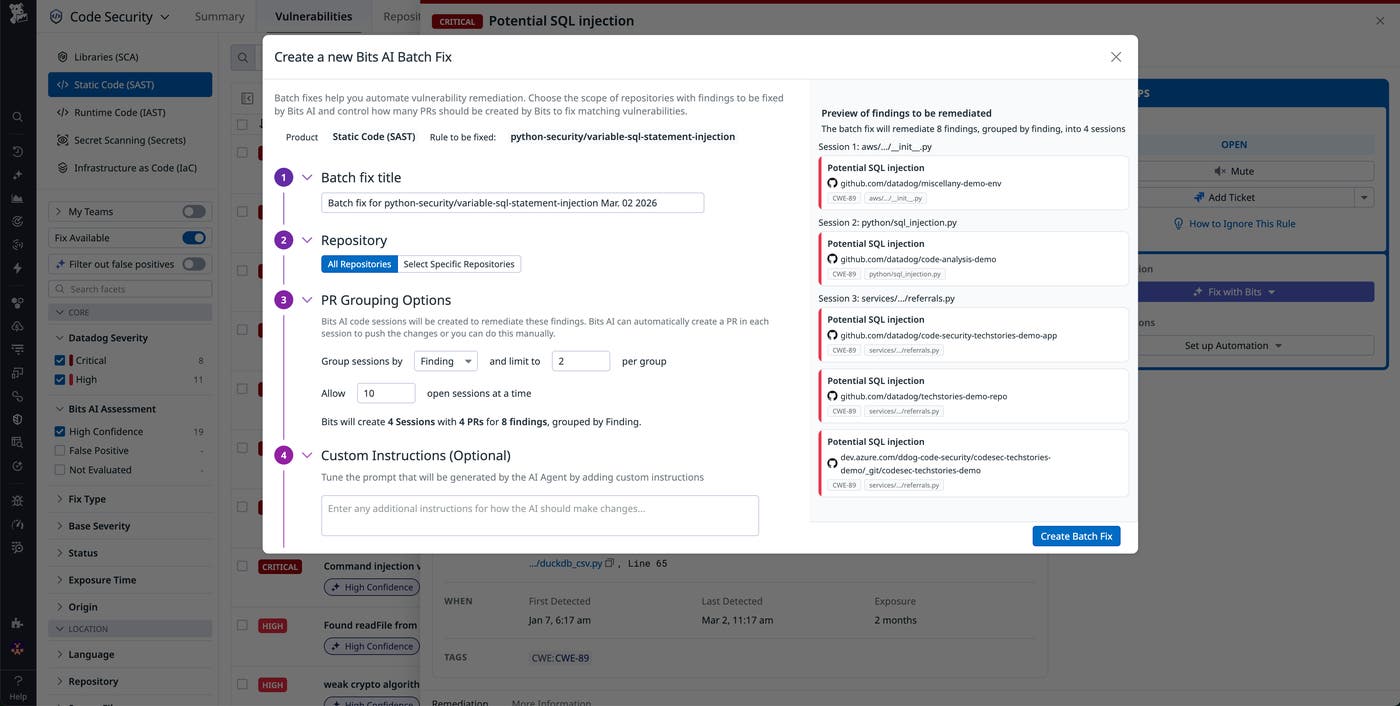
For large backlogs, single fixes simply aren’t efficient enough to scale with the pace of backlog growth. This is where batch fixes come in. With batch fixes, you can define a set of many vulnerabilities that the Dev Agent should remediate at once. For example, you can choose to fix all SQL injections in selected repositories, addressing one type of vulnerability at once across many instances of it in your codebase.
You can also define how fixes should be grouped into PRs that the Dev Agent will create. You can group PRs by repository (e.g., “fix all matching findings in this repository in one PR”), by file, or by individual finding (e.g., “create one fix PR per finding”). These options are provided to help you match Dev Agent PR cadence to your development teams’ code review processes and bandwidth for reviewing security patches.
Once a batch fix is created, the Dev Agent generates individual fixes and can open PRs according to the preferences you defined. You no longer have to open thousands of PRs manually. Now, you can define the strategy once and let the agent handle the repetitive work.
Bits AI Dev Agent is designed to operate transparently, providing security and engineering teams with clear visibility into every action it takes.
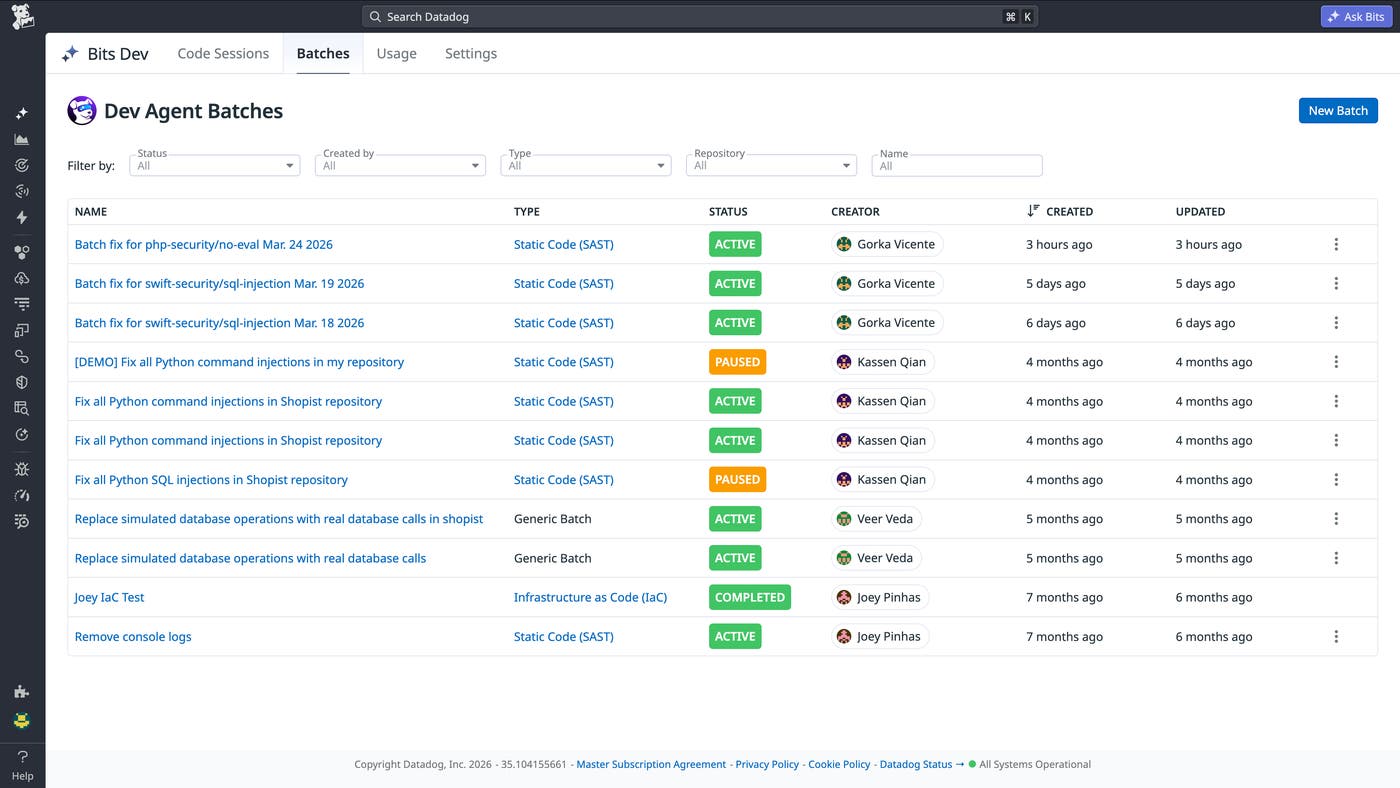
Every unit of work performed by the Dev Agent is captured as a session, which maps 1:1 to a PR created by Bits. Each session is saved in the Sessions view, which provides a centralized record of activity, including the associated findings, generated fixes, and PR status. From any session, you can review progress, inspect generated diffs, and stop or restart remediation progress as needed.
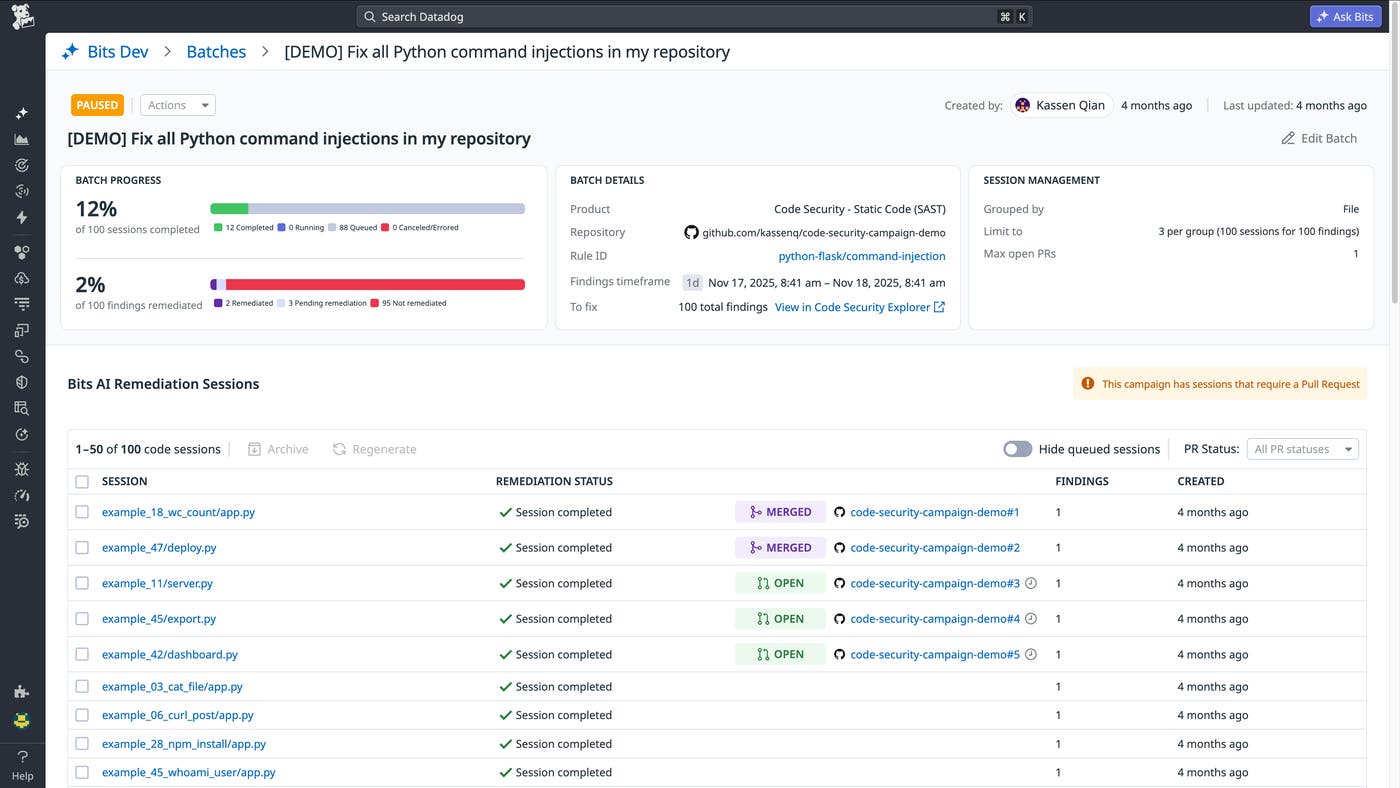
The Batches view gives you a high-level picture of remediation progress across different sessions. In this view, you can track how many findings have been remediated in the source code, how many PRs are open, and which PRs have been approved or merged.
If priorities shift, you can pause or stop a batch fix at any time. Because remediation is tied to tracked findings, you keep a clear link between vulnerabilities and the code changes meant to address them. That context helps security and development teams collaborate more efficiently.
Remediations by Bits AI Dev Agent reflect a shift in how security and development teams are approaching vulnerability management. As the pace of software development accelerates, security teams must scale existing processes to keep up. AI can be used not only to fix vulnerabilities in bulk but also to increase efficiency across other parts of the vulnerability management life cycle.
For example, at Datadog, we have seen that combining a traditional static analysis approach with AI-native scanning leads to higher detection accuracy of code vulnerabilities. From that set of vulnerabilities, Code Security also filters out false positives with LLM-based filtering. Once findings have been narrowed down, you can now use the Bits AI Dev Agent to automatically generate fixes, open PRs, and track remediation progress—all while maintaining control over scope and review.
As codebases grow and release cycles accelerate, security teams need tools that go beyond detection and help drive remediation at scale. Bits AI Dev Agent for Code Security helps these teams reduce their vulnerability backlogs while maintaining visibility and control over every remediation.
To get started, visit the documentation for Bits AI Dev Agent and the Datadog Code Security. And if you’re new to Datadog, sign up for our 14-day free trial.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。