





According to the GDPR, to transfer personal data outside the European Union, you need to make sure there are specific data protection standards in place. If there aren’t, then transfers are not allowed.
However, to make transfers possible, there are several legal bases on which you could rely. One of these are Standard Contractual Clauses (SCCs).
In this short guide, we’ll explain everything you need to know about Standard Contractual Clauses, when you may need to rely on SCCs and what you should do to transfer data outside the EU.
In short
- What are standard contractual clauses?
- When are standard contractual clauses required?
- What is the UK equivalent of Standard Contractual Clauses?
- How can I create SCC?
- Are there any alternatives to SCCs?
What are standard contractual clauses?
Standard Contractual Clauses (SCCs) are standardized clauses, approved by the European Commission, that allow the transfers of data outside the European Economic Area (EEA).
Both parties involved in the transfer need to sign an agreement containing the Standard Contractual Clauses, without altering their text. As stated by the European Commission, SCCs can be added in any “contractual arrangement” between the parties.
A bit of legal background
👉 Standard Contractual Clauses were first mentioned in the Data Protection Directive of 1995. According to this Directive, data transfers outside the EU were allowed only when certain data protection standards were met, or when there were Standard Contractual Clauses in place. In 2018, the GDPR replaced the Data Protection Directive, keeping the same mention to SCCs.
👉 Fast forward to July 2020, the Schrems II ruling invalidated the transfer agreement between EU and USA, the Privacy Shield. SCCs became essential for any kind of data transfer between these countries. However, they were not binding for the US government, but only for the company signing the agreement.
👉 In order to facilitate the transfer of data between the EU and the US, the European Commission revised the clauses. On June 4th, 2021, the Commission adopted two sets of Standard Contractual Clauses:
- SCCs regulating the relationship between controllers and processors;
- SCCs as a tool for data transfers outside of the EEA.
👉 On July 10, 2023, the European Commission adopted an adequacy decision with the US, the EU-US Data Privacy Framework (DPF). With the adequacy decision in place, the flow of personal data from the EU to US companies has resumed without additional safeguards. However, US companies need to self-certify for compliance with the Data Privacy Framework.
👉 GDPR Standard Contractual Clauses are still valid for those countries that don’t have an adequacy decision.
When are standard contractual clauses required?
SCCs aren’t always required.
In fact, you first need to check if there’s an adequacy decision in place. Usually, when the level of data protection is the same as the GDPR, the European Commission issues an adequacy decision. In that case, there’s no need for Standard Contractual Clauses.
💡 So far, the only countries for which the European Commission has issued an adequacy decision are: Andorra, Argentina, Canada (commercial organizations), Faroe Islands, Guernsey, Israel, Isle of Man, Japan, Jersey, New Zealand, Republic of Korea, Switzerland, the United Kingdom, the United States (commercial organizations participating in the EU-US Data Privacy Framework), and Uruguay.
Once you’re sure of this aspect, you also need to ensure that GDPR SCCs are the mechanism that applies to your activity. If so, then you need to sign an agreement containing Standard Contractual Clauses.
How to disclose data transfers in your privacy policy
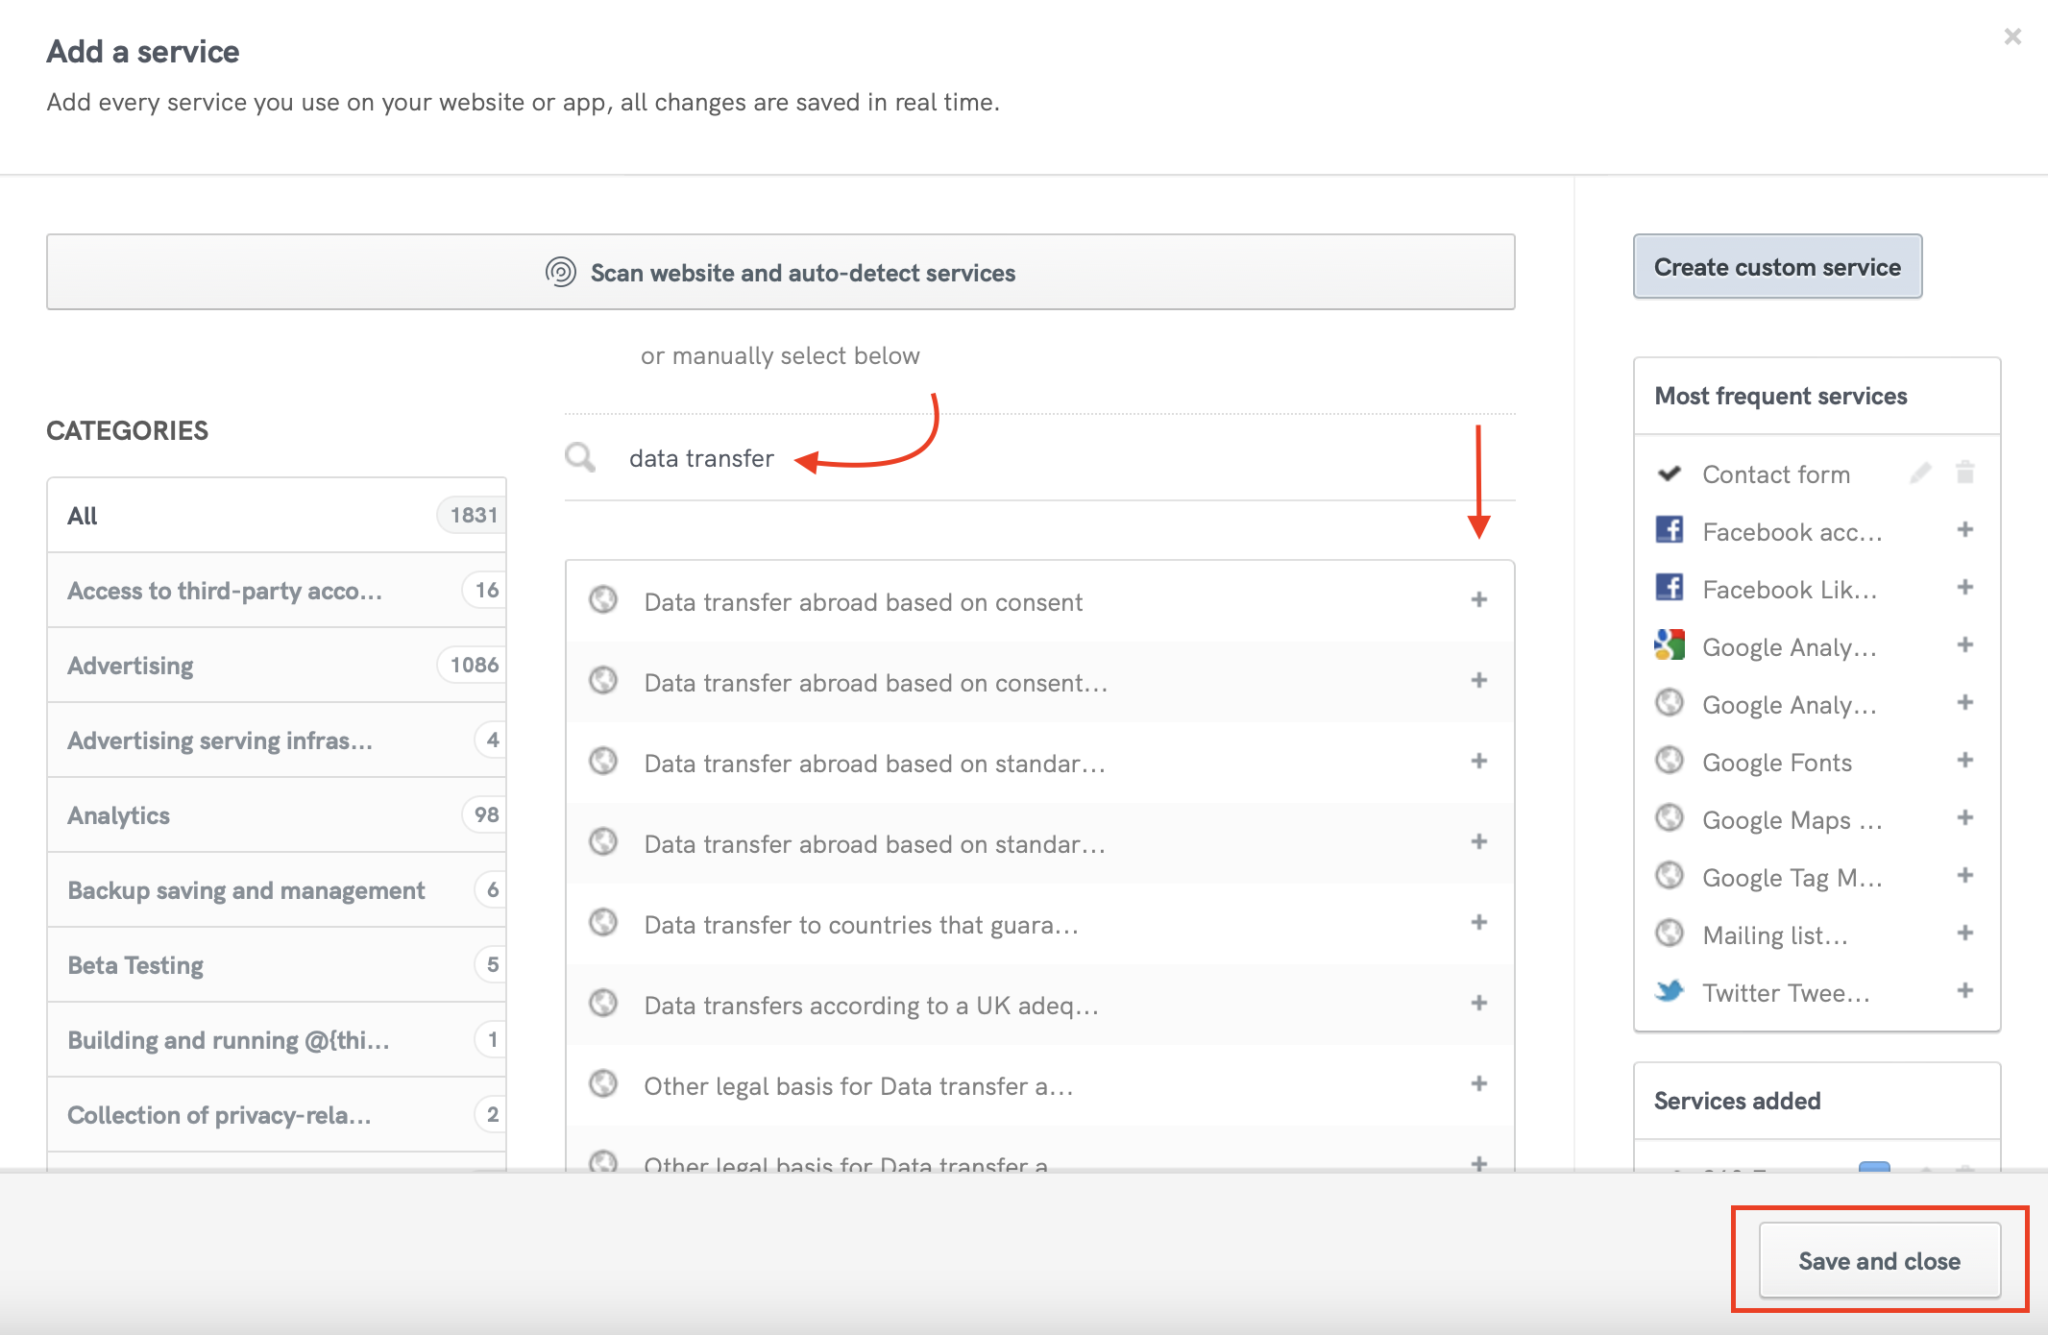
If you’re transferring data outside the EEA, you also need to disclose it in your privacy policy. With iubenda, this is really easy:
- Look for the clauses within the Generator
- Click on “+” and add them to your document
- Save!
What is the UK equivalent of Standard Contractual Clauses?
After Brexit, the UK adopted its version of the GDPR, the UK GDPR.
Under the UK GDPR, Standard Contractual Clauses were replaced by the International Data Transfer Agreement (IDTA) or the UK Addendum to the EU SCCs.
This means that organizations transferring data to a third-country that doesn’t have an adequacy decision can either:
- Use the International Data Transfer Agreement (IDTA), or
- Use the EU Standard Contractual Clauses, but add the UK Addendum.
You can find more information here.
How can I create SCC?
As we already mentioned, your Standard Contractual Clauses can either be added to any agreement you have with the party you’re transferring data to, or they can be a document on their own.
Creating your SCCs is easier than you think, but you must strictly follow the text suggested by the European Commission.
Are there any alternatives to SCCs?
Yes, Standard Contractual Clauses aren’t the only way you can transfer data outside the EEA, you have other alternatives:
- Binding Corporate Rules (BCRs): data protection policies adopted by multinational companies. BCRs allow companies to transfer data internationally within the same corporate group. Binding Corporate Rules are for internal use only, but Article 47 of the GDPR mentions them as an adequate method to ensure compliance.
- Derogations: according to Article 49 of the GDPR, there are also specific cases when you can transfer personal data without any safeguards. Anyway, these derogations apply just to a specific data transfer or set of transfers, and there are requirements you should meet, for example:
- you have your user’s explicit consent and you’ve informed them of all the possible risks of the transfer;
- the transfer is necessary for the fulfillment of a contract;
- the transfer is necessary for important reasons of public interest.
Compliance tip
If you’re transferring data, you need to disclose it in your privacy policy! Failure to do it, could invalidate your activity.
Read also
- What is the GDPR? The Ultimate Guide to GDPR Compliance
- GDPR & Brexit – What it means for businesses and the impact on data protection
- How to Edit a Privacy Policy
About us
Attorney-level solutions to make your websites and apps compliant with the law across multiple countries and legislations.