


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

WordPress大学
WordPress大学
酷 壳 – CoolShell
酷 壳 – CoolShell
小众软件
小众软件
Vercel News
Vercel News
Last Week in AI
Last Week in AI
H
Help Net Security
The Cloudflare Blog
L
LangChain Blog
Microsoft Security Blog
B
Blog RSS Feed
云风的 BLOG
云风的 BLOG
I
InfoQ
U
Unit 42
美团技术团队
人人都是产品经理
人人都是产品经理
雷峰网
雷峰网
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
博客园 - 叶小钗
Y
Y Combinator Blog
Hugging Face - Blog
Hugging Face - Blog
A
About on SuperTechFans
宝玉的分享
宝玉的分享
量子位
博客园_首页

NodeJS Security & NodeJS Secure Coding's Blog

Hardening Your npm and pnpm Configs in the Age of Shai-Hulud Argument Injection vulnerability in git-blame@1.4.0 Argument Injection vulnerability in `gits@0.1.8` Command Injection vulnerability in `@fab1o/git@1.4.0` Command Injection vulnerability in `git-contributors` via unsanitized CLI arguments Command Injection vulnerability in `git-q@0.0.3` Command injection vulnerability via unsanitized CLI arguments in touxing/fast-git-clone Command Injection vulnerability in `willitmerge@0.2.1` A Directory Traversal Vulnerability I found in Mastra AI Frameworks MCP Server Mastering NPX: A Cheatsheet for npm and Node.js Power Users Mitigate Supply Chain Security with DevContainers and 1Password for Node.js Local Development The Tale of the Vulnerable MCP Database Server Bad Security Defaults in Mastra AI Frameworks Templates SQL Injection and Bypassing "Read-Only" Mode in Xata's MCP Server Security Advisory for qix npm supply-chain compromise affecting debug and billions of weekly download users How to Mitigate SQL Bypass in MCP Servers Enhancing MCP Server Security: A Guide to Using execFile Argument Injection Vulnerability in ggit How to Bypass Access Control in PostgreSQL in Simple PSQL MCP Server for SQL Injection Command Injection Flaws in ggit: Unveiling a Vulnerability Command Injection Vulnerability in Create MCP Server STDIO Tool Exposes System Monitoring Functions GitHub Kanban MCP Server Command Injection Vulnerability Threatens Developer Workflows Critical Command Injection Flaw in iOS Simulator MCP Server Exposes Development Environments Command Injection Vulnerability Discovered in Codehooks MCP Server: A Critical Security Analysis SSRF Shenanigans in safe-axios: Redirects Open the Backdoor SSRF Vulnerability in safe-axios: Unintended Public Address Classification Bypassing SSRF Safeguards in ssrfcheck: A Case of Incomplete Denylists Don't Be Fooled by Multicast, SSRF Bypass in private-ip Node.js Authentication from Lucia to Better Auth Bypassing SSRF Protection in nossrf: When Your Safeguards Become Loopholes
Where to find npm vulnerabilities?
2025-01-13 · via NodeJS Security & NodeJS Secure Coding's Blog

If you’re looking to educate yourself on the latest npm vulnerabilities, you’ve come to the right place.

In this article, I’ll call out some open sources to find security vulnerabilities in the npm ecosystem and how to stay up-to-date with the latest security threats.

Snyk Vulnerability Database

To kick us off, the Snyk Vulnerability Database is a great place to start. It’s a comprehensive database of vulnerabilities in open-source projects, including npm packages. You can search for vulnerabilities by package name or a CVE.

Disclaimer: I work at Snyk as a developer advocate
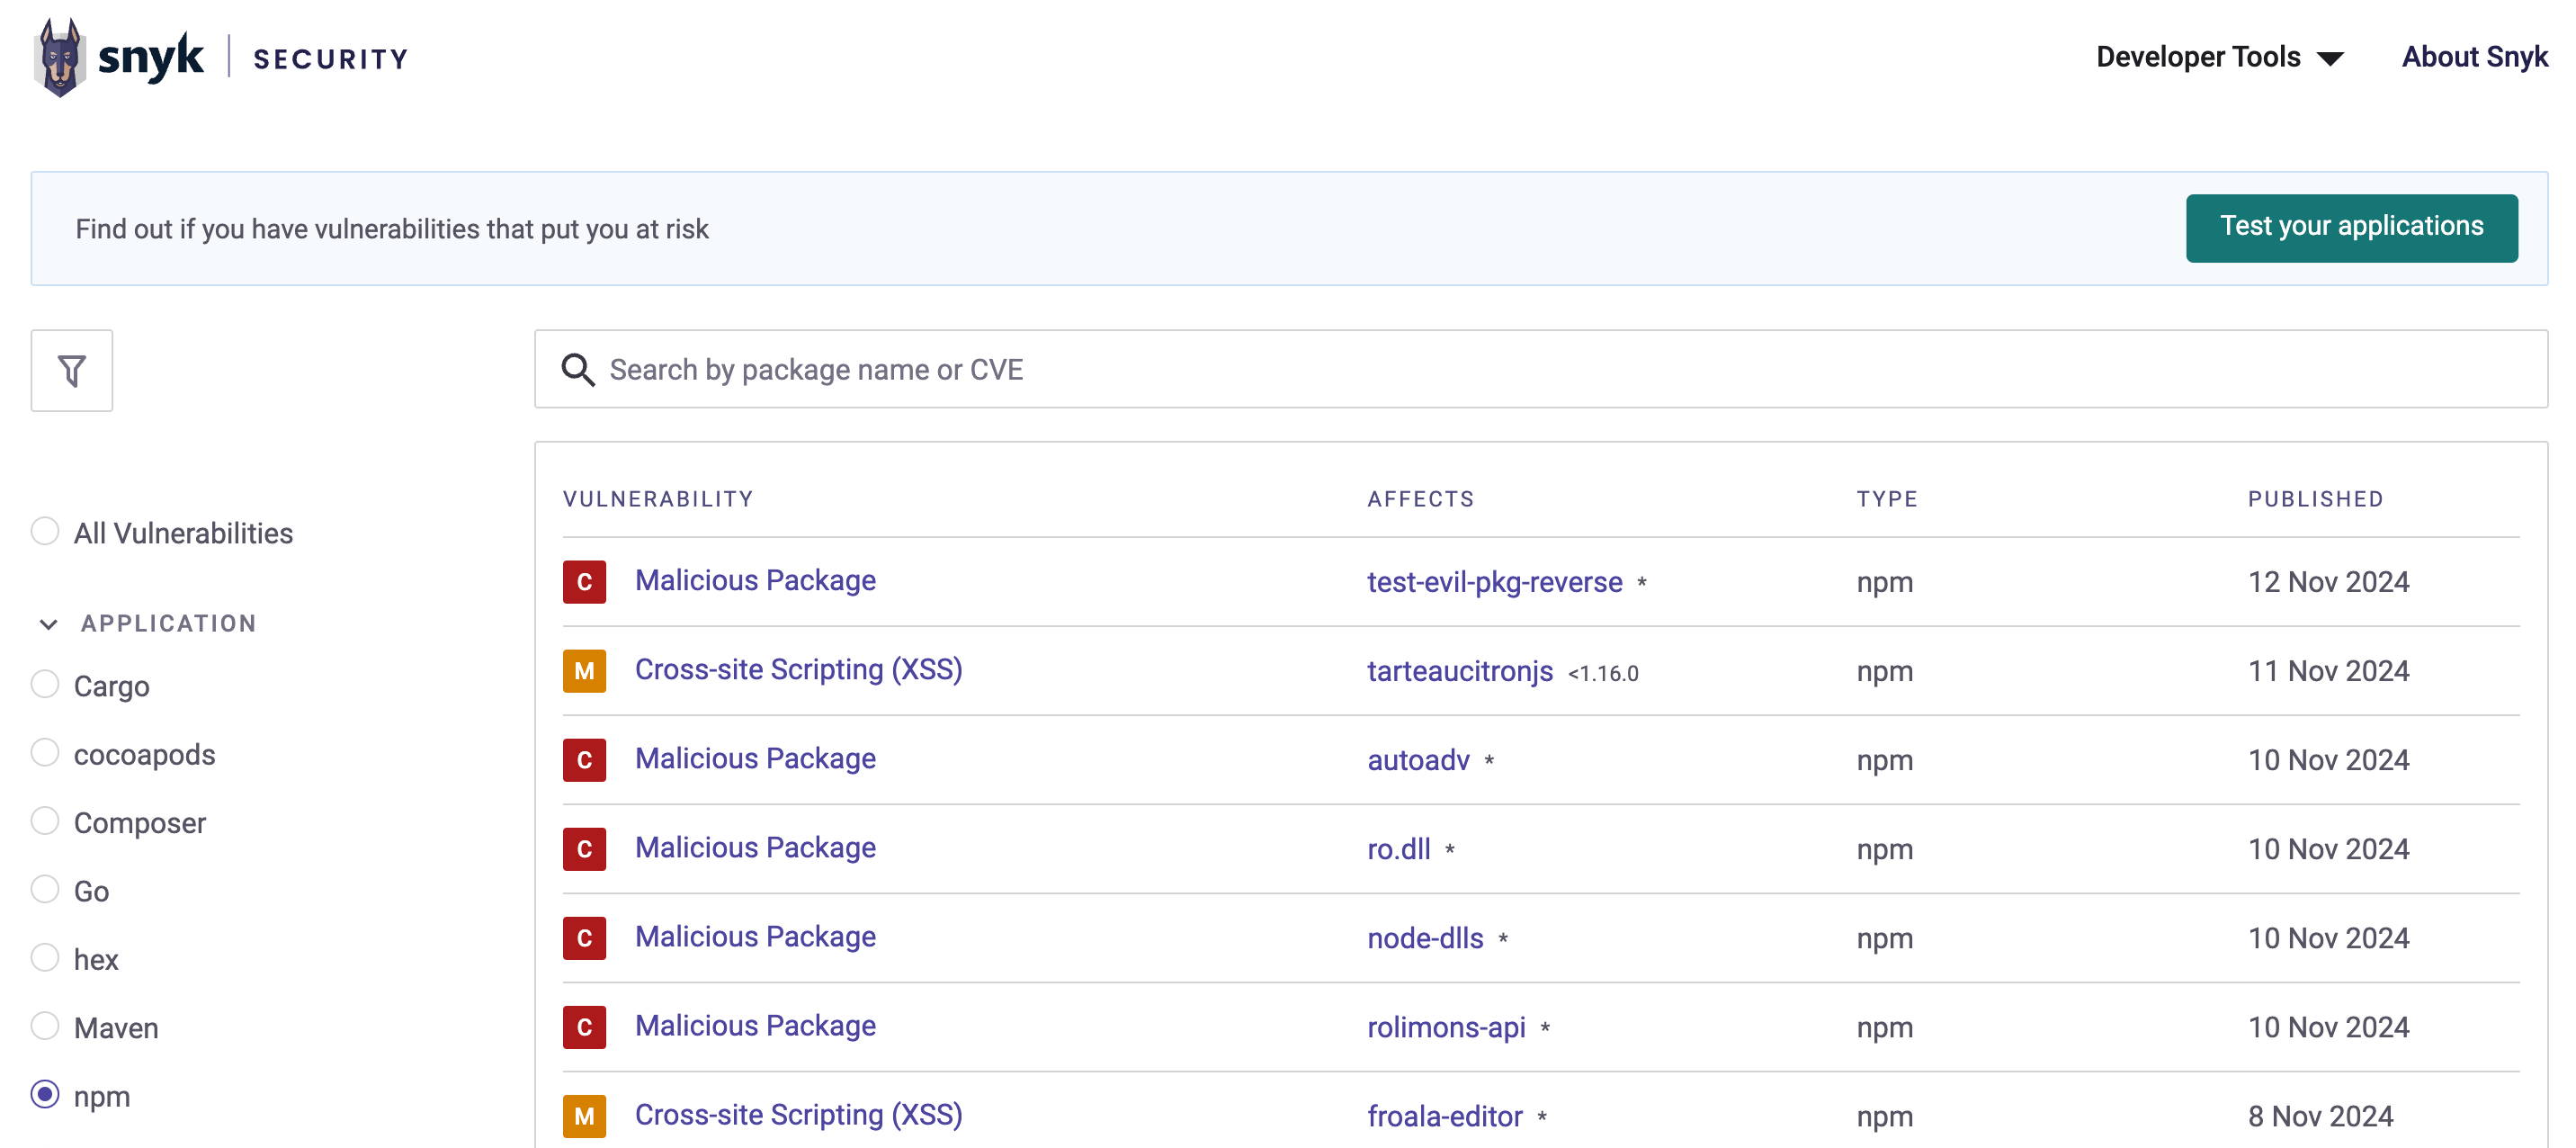
Snyk vulnerability database CVEs for npm vulnerabilities

Specifically what makes the Snyk vulnerability database stand out is the following highly enriched metadata:

  • The database is extremely timely, accurate and up-to-date
  • The vulnerability report includes dates of the security disclosure and also the publishing time
  • The vulnerability report includes a description the vulnerability itself with instructions on how to remediate it
  • Enriched metadata with links to the GitHub commit, GitHub pull request, a link to the npm package, or the researcher’s gist
  • It uses CVSS 4 scoring

GitHub Security Advisories

The GitHub Security Advisories is another good place to find vulnerabilities in npm packages. Specifically it is helpful due to the free-text search.
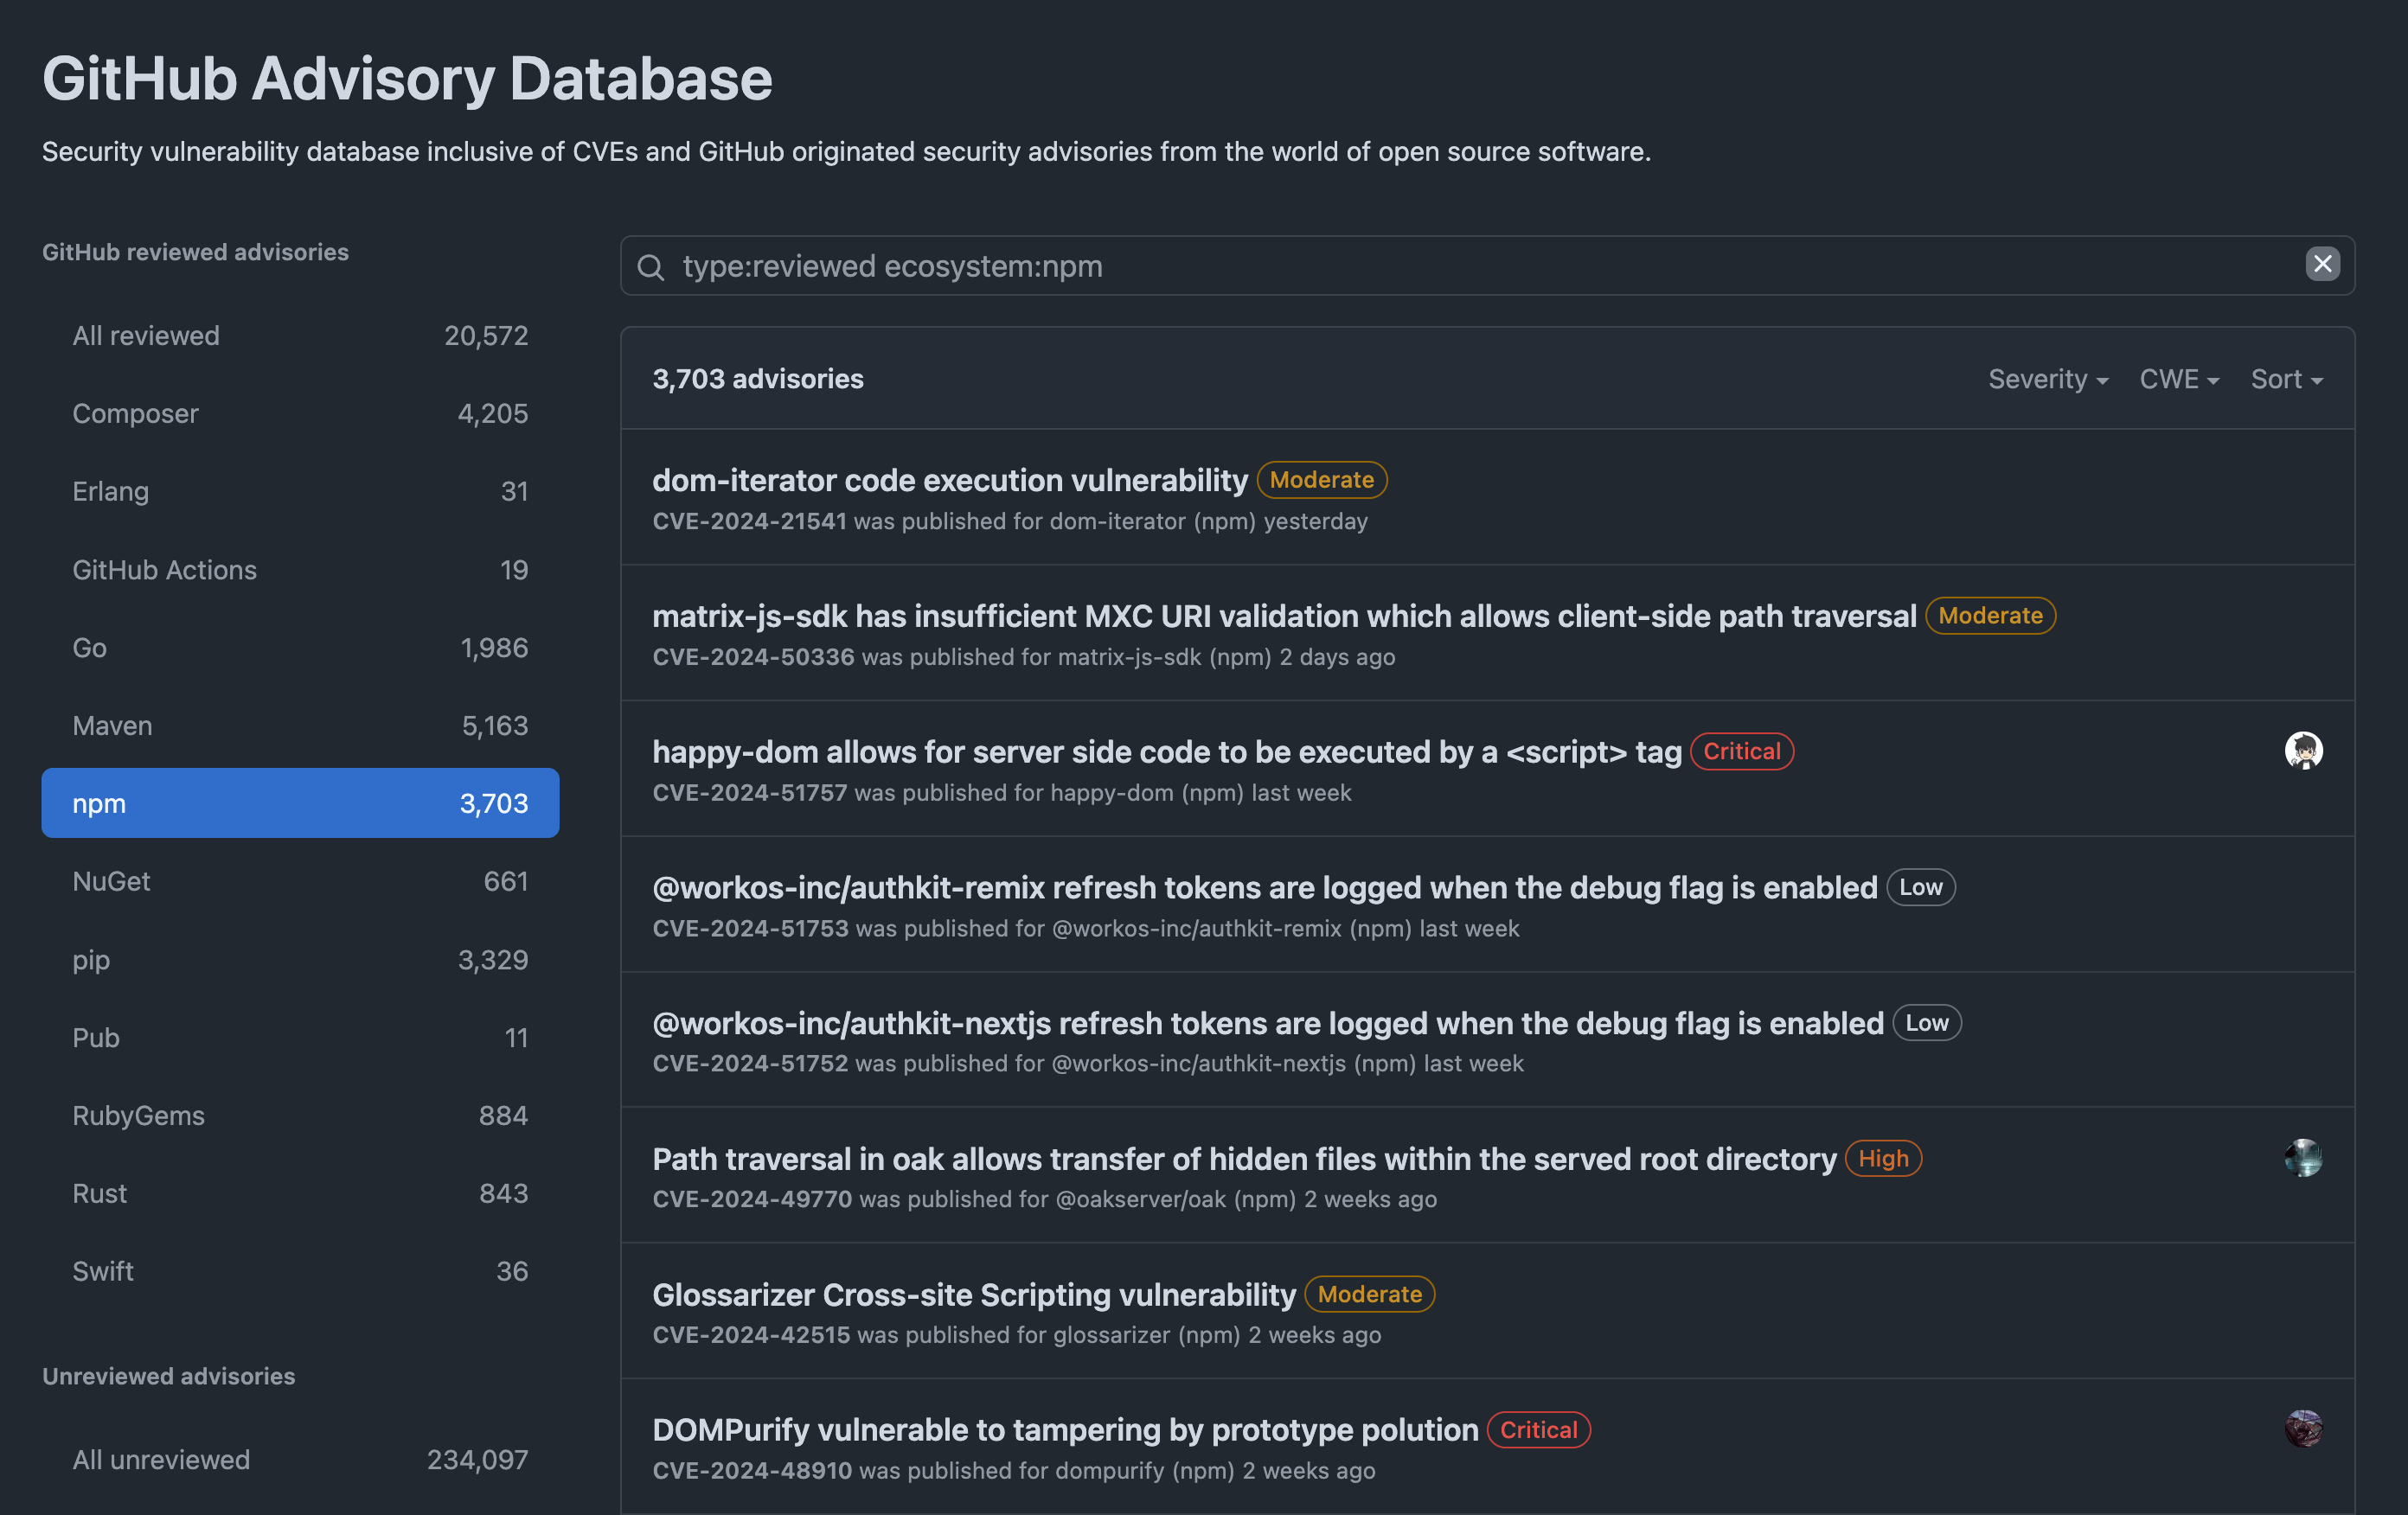
GitHub Security Advisories for npm vulnerabilities

Google’s OSV

Another security vulnerability resource is the Open Source Vulnerabilities (OSV). It’s a new project by Google that aims to provide a comprehensive vulnerability database for open-source projects.

Specifically, OSV also provides an API layer to query the vulnerabilities programmatically which could prove handy, depending on your use-case.
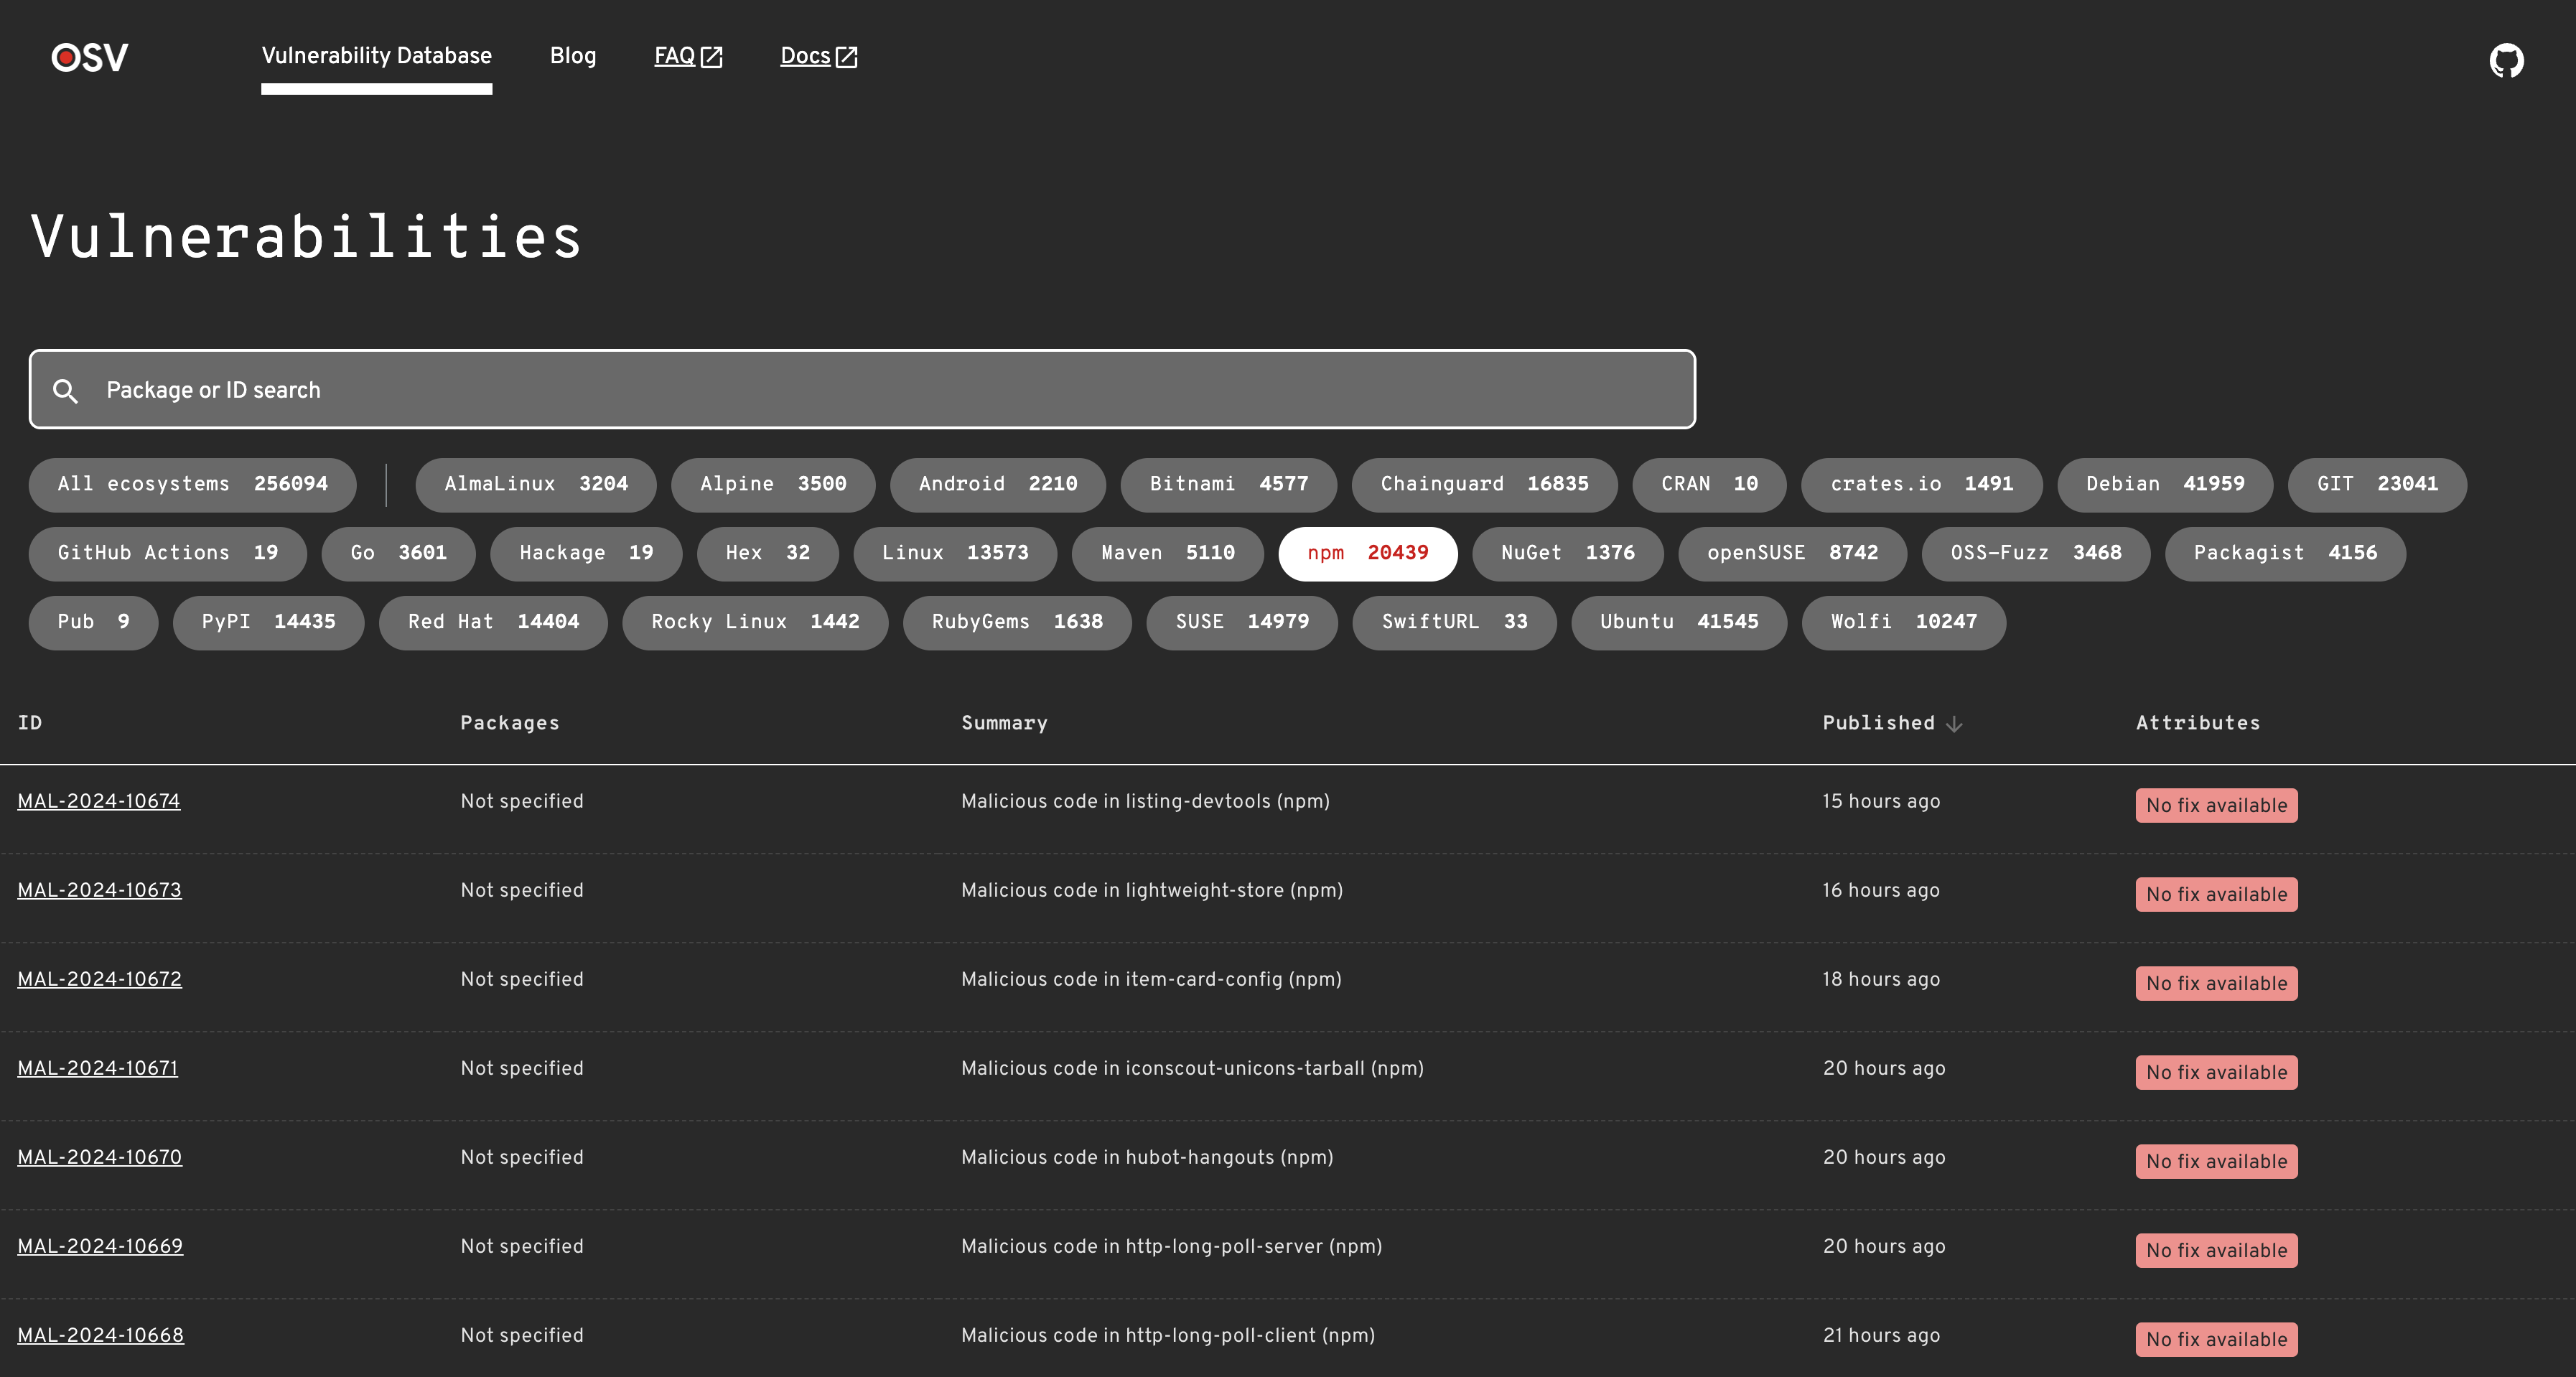
OSV for npm vulnerabilities