



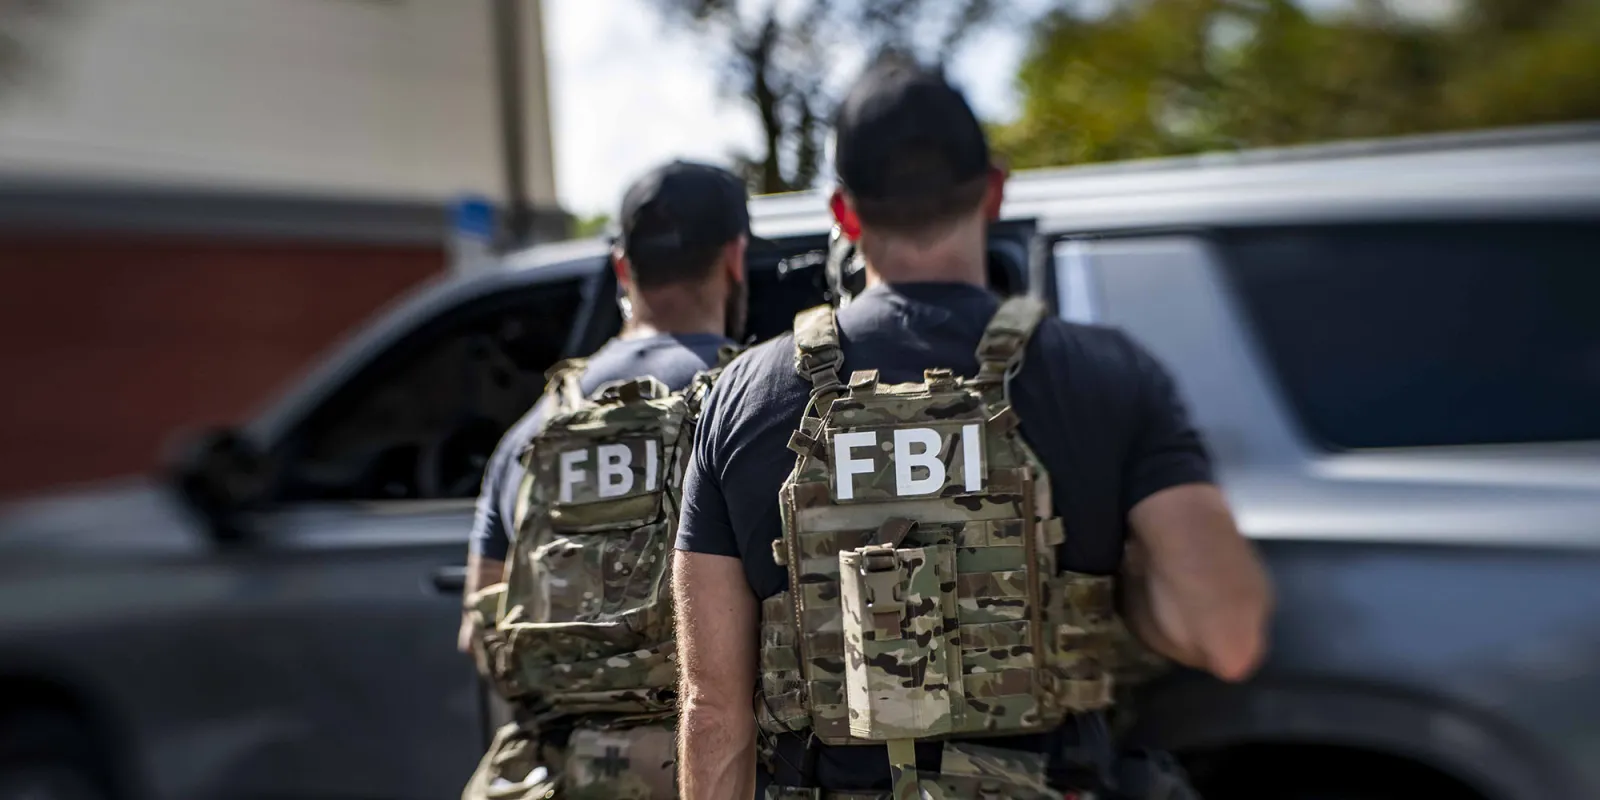
A new report from 404 Media reveals that the FBI was able to recover deleted Signal messages from an iPhone by extracting data stored in the device’s notification database. Here are the details.
According to 404 Media, testimony in a recent trial involving “a group of people setting off fireworks and vandalizing property at the ICE Prairieland Detention Facility in Alvarado, Texas,” showed that the FBI was able to recover content of incoming Signal messages from a defendant’s iPhone, even though Signal had been removed from the device:
One of the defendants was Lynette Sharp, who previously pleaded guilty to providing material support to terrorists. During one day of the related trial, FBI Special Agent Clark Wiethorn testified about some of the collected evidence. A summary of Exhibit 158 published on a group of supporters’ website says, “Messages were recovered from Sharp’s phone through Apple’s internal notification storage—Signal had been removed, but incoming notifications were preserved in internal memory. Only incoming messages were captured (no outgoing).”
As 404 Media notes, Signal’s settings include an option that prevents the actual message content from being previewed in notifications. However, it appears the defendant did not have that setting enabled, which, in turn, seemingly allowed the system to store the content in the database.
404 Media reached out to Signal and Apple, but neither company provided any statements on how notifications are handled or stored.
With little to no technical details about the exact condition of the defendant’s iPhone, it is obviously impossible to pinpoint the precise method the FBI used to recover the information.
For instance, there are multiple system states an iPhone can be in, each with its own security and data access constraints, such as BFU (Before First Unlock), AFU (After First Unlock) mode, and so on.
Security and data access also change even more dramatically when the device is unlocked, since the system assumes the user is present and permits access to a wider range of protected data.
That said, iOS does store and cache a lot of data locally, trusting that it can rely on these different states to keep that information safe but readily available in case the device’s rightful owner needs it.
Another important factor to keep in mind: the token used to send push notifications isn’t immediately invalidated when an app is deleted. And since the server has no way of knowing whether the app is still installed after the last notification it sent, it may continue pushing notifications, leaving it up to the iPhone to decide whether to display them.
Interestingly, Apple just changed how iOS validates push notification tokens on iOS 26.4. While it is impossible to tell whether this is a result of this case, the timing is still notable.
Post by @_inside@mastodon.social
View on Mastodon
Back to the case, given Exhibit 158’s description that the messages “were recovered from Sharp’s phone through Apple’s internal notification storage,” it is possible the FBI extracted the information from a device backup.
In that case, there are many commercially available tools for law enforcement that exploit iOS vulnerabilities to extract data that could have helped the FBI access this information.
To read 404 Media’s original report of this case, follow this link.
FTC: We use income earning auto affiliate links. More.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。