



Robocalls are really annoying. Everyone knows the misery of scam calls, spoofed numbers, fake warranty pitches, fraudulent bank alerts, and automated political spam. The FCC is correct to claim that illegal calls erode trust in the phone system and cost Americans time, money, and security. But this problem does not justify a dragnet solution. Under the guise of fighting robocallers, the FCC is now considering “Know Your Customer” rules that could force phone providers to collect identity information from ordinary people before they can acquire or renew service with a phone carrier.
The proposal is being sold as consumer protection, but the surveillance regime it would create is something else entirely.
On April 30, 2026, the FCC adopted a Further Notice of Proposed Rulemaking seeking stronger KYC rules for voice service providers. The agency says possible measures include requiring providers to verify customer identities before enabling service, including name, address, government ID, and alternate phone numbers. The item was approved by Chairman Brendan Carr and Commissioners Gomez and Trusty.
That should alarm anyone who believes phone access is basic infrastructure, not a privilege conditioned on identity verification. The danger is not that the FCC wants to punish robocall scammers. The danger is that the FCC is contemplating rules that would put millions of innocent people into telecom identity databases in the hope that criminals will be inconvenienced. We've seen this playbook before. Such measures take more privacy from lawful users while determined criminals will adapt and find ways around the "gate."
KYC does not reliably stop determined criminals. We know this to be true simply from looking at KYC requirements in the financial system. There's no shortage of money laundering that occurs through regulated venues, in part because criminals don't have much trouble providing the required documentation to pass KYC checks. Why is this easy to route around? Mainly because so much personally identifiable information gets leaked on an ongoing basis that entire markets exist to trade this information. Buying a new identity and the associated documents to go along with it is cheap.
The proposal also reaches directly into prepaid service. The FCC is asking whether KYC requirements should vary between prepaid and postpaid plans, what information wireless providers currently obtain from prepaid SIM customers, and whether KYC measures should be imposed for prepaid service purchased through third-party vendors. That is the heart of the burner-phone issue. A prepaid phone is not just a movie prop for criminals. It can be a lifeline for a domestic violence survivor, a worker reporting misconduct, a journalist protecting a source, a protester avoiding retaliation, or someone who simply does not want every communication account tied to a government ID.
ACLU senior policy analyst Jay Stanley warned that the rulemaking contemplates taking away people’s ability to get a burner phone and could harm low-income people, domestic violence victims, and anyone who values privacy. That is the point the public needs to understand: anonymous or pseudonymous communication is not suspicious by default.
I've used KYC-free phone services for many years both as a security and privacy protection tactic. I, like anyone who might be suspected of having access to significant amounts of bitcoin, need strong privacy in order to protect myself from wrench attacks. This is not a theoretical threat; hundreds of Bitcoiners have been physically attacked and I myself have been swatted and extorted.
The most chilling parts of the FCC’s proposal go beyond ordinary ID collection. In its section on risk-based KYC differences, the FCC even asks whether providers should consult lists of terrorists, terrorist organizations, and “criminal persons” maintained by law enforcement entities. We've also seen this before and such lists would surely lead to false positives, abuse of innocent people being opaquely added to said lists, and the possibility that people could be denied basic communication infrastructure without a conviction or meaningful due process. Even though the FCC frames this as a question rather than a final decision, it is a dangerous question for a communications regulator to normalize.
The proposal also contemplates long retention periods. The FCC asks about requiring providers to retain KYC information and supporting records for four years after the customer relationship ends. That means the risk does not end when someone cancels service. A person’s identifying information could remain in carrier databases for years, exposed to breach, misuse, subpoena, sale, or mission creep.
Mission creep is already visible in the FCC’s own words. The agency asks whether enhanced KYC rules could help law enforcement investigate crimes beyond illegal calls, including organized crime, trafficking, espionage, influence operations, and other national-security concerns. That is a very different pitch from “we are stopping robocalls.” Once telecom providers are required to verify, retain, re-verify, and possibly screen customers, the phone system starts looking less like an open communications network and more like a chokepoint.
The FCC also proposes a per-call enforcement structure. It asks about assessing KYC violations on a per-call basis and specifically proposes a $2,500 per-call base forfeiture. That creates an obvious incentive: providers will protect themselves by over-verifying, over-retaining, and over-denying. When the penalty for under-screening can multiply by call volume, the safest corporate choice is not the one that protects consumer privacy, but rather the one that intrudes upon it greatly.
A free society does not require citizens to continually fight to retain their privacy. The burden should be on the government to justify eroding the rights of citizens via surveillance, data retention, and denial of access to essential communications tools.
We have seen this playbook before, oh so many times, to the point that it has become a meme. Those who seek to control the channels of communication must first be able to identify anyone who is using a network so that they can then send their thugs to silence the undesirable speaker.
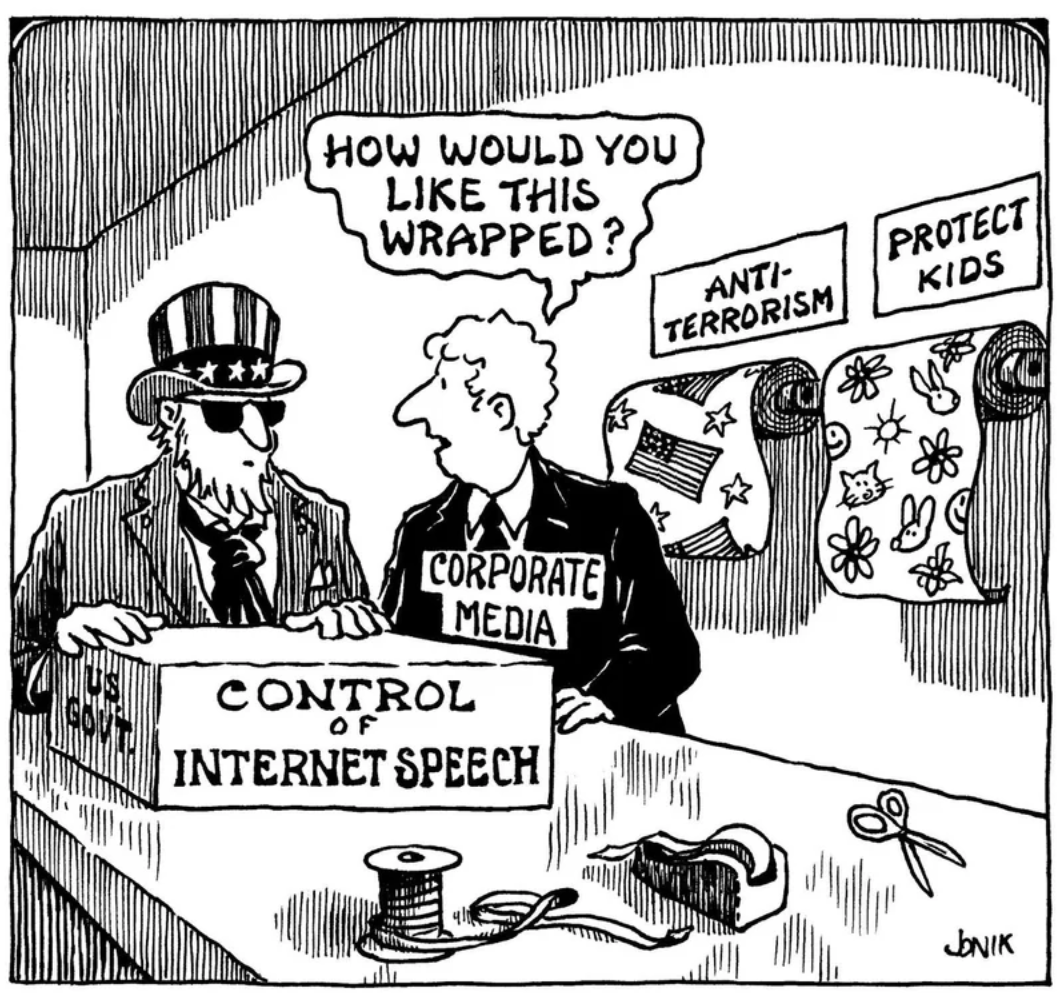
There is a better path. The FCC can target high-volume commercial origination, negligent providers, spoofing infrastructure, SIM-box abuse, and repeat bad actors without forcing every ordinary person to surrender identity documents to get a phone number. It can strengthen enforcement against carriers that knowingly enable illegal call traffic. It can require narrow, risk-based due diligence for bulk callers. What it should not do is make every phone user prove who they are before they can communicate.
This is not a partisan issue. The average citizen does not want the government compiling lists of people who are conducting completely normal activities. They do not want “consumer protection” turned into surveillance. They do not want privacy treated as a loophole. And they do not want to find out later that a rule meant to stop robocalls quietly ended the last practical way to access the telephone system without government permission.
I often refer to KYC as Kill Your Customer, because the very act of collecting sensitive personally identifiable information about a customer puts them at risk. The KYC regime has made itself into a joke by resulting in massive data leaks over the years, which now undermine the reliability of KYC since criminals can easily obtain fresh documents to bypass KYC checks with stolen identities.
Specific to phone service, KYC will actively degrade the security of your phone account because tying your account to an identity means that a criminal who obtains enough of your PII becomes better positioned to impersonate you to your phone provider and attempt to transfer your number to a SIM under the criminal's control. This "SIM swapping" / "SIM jacking" issue has been a problem for over a decade now and is only getting worse as more and more of our lives are going digital and most of our important online accounts are tied to phone numbers and email addresses. The common attack vector for SIM jacking is:
KYC is a laughable regime put in place under the claim of "stopping criminals" but the reality is that it is security theater that actually weakens the privacy and security of consumers rather than protecting them from bad actors. We should not double down on this broken system by implementing it in even more aspects of our lives.
This is not yet a final rule. It is a proposed rule, which means the public still has a chance to push back. In the Federal Register, the FCC says it is seeking comment on this proposed change. That means we can give them a piece of our minds.
The comment deadline is June 25, 2026, with reply comments due July 27, 2026.
I urge you to submit a public comment to the FCC before June 25, 2026 opposing mandatory KYC identity checks for ordinary phone users. You can use the form at this link to submit a comment on this matter. Just click the link right now and submit a comment before you close this post! Yes, you, dear reader!
Remember that FCC comments are public. Assume that anything you submit, including personal information in the comment text or attachments, may become publicly viewable online. Don't include personal details you can't safely reveal to the world.
Feel free to use the following template to save yourself some time. Add / remove / edit whatever you wish to personalize it to your view.
I oppose any FCC rule that would require ordinary phone users, including prepaid users, to provide government-issued identification numbers, identity documents, physical addresses, alternate phone numbers, or similar personal information as a condition of obtaining or renewing phone service.Robocalls and scam calls are serious problems, but mandatory identity collection for all users is overly broad, privacy-invasive, and likely to harm lawful users who need privacy, including domestic violence survivors, journalists, whistleblowers, low-income citizens, political organizers, and people facing retaliation or stalking.
The FCC should reject any requirement that voice providers consult law-enforcement watchlists or lists of “criminal persons” before granting service. Access to basic communications infrastructure should not depend on opaque lists, screening systems prone to abuse and false positives, or processes lacking transparency.
The FCC should also reject multi-year retention of KYC records for ordinary customers. Retaining identity information and supporting records after a customer leaves service creates unnecessary breach, misuse, and surveillance risks.
The Commission should instead focus on narrow, evidence-based enforcement against high-volume illegal callers, spoofing abuse, SIM-box operations, and providers that knowingly or recklessly enable illegal traffic. Any new rules should be targeted, privacy-protective, data-minimizing, and should preserve access to prepaid and privacy-protective phone service for lawful users.
Please do not turn phone service into an identity checkpoint. Reject mandatory KYC requirements for ordinary telephone users.
Now is the time for all Americans who are concerned about the constant erosion of their privacy to speak out.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。