









Overwhelmed by an escalating volume of security flaws, the National Institute of Standards and Technology (NIST) has announced significant changes to how it handles cybersecurity vulnerabilities and exposures (CVEs).
Rather than commit to providing enrichment for all entries in its National Vulnerability Database (NVD), the agency will focus on just the most critical CVEs, which will “allow us to stabilize the program while we develop the automated systems and workflow enhancements required for long-term sustainability.”
Starting immediately, NIST will focus on CVEs appearing in CISA’s Known Exploited Vulnerabilities (KEV) catalog. “Our goal is to enrich these within one business day of receipt,” the agency said.
Other high-priority CVEs will also include those for software used in the federal government and for other critical software.
All the other CVEs will still be added to the NVD, but will be categorized as “not scheduled,” meaning that NIST will no longer prioritize their enrichment.
Broken by backlog
According to NIST, a backlog of CVEs started to accumulate in early 2024, and the agency has been unable to clear it due to increasing submissions.
Submissions grew by 263% between 2020 and 2025, according to the agency, with nearly one-third more vulnerabilities reported in Q1 2026 than the same time last year.
The agency, which enriched nearly 42,000 CVEs in 2025, 45% more than any previous year, now faces a total backlog of more than 30,000 CVEs, said Harold Booth, a technical and program lead at NIST, at this week’s VulnCon cybersecurity conference.
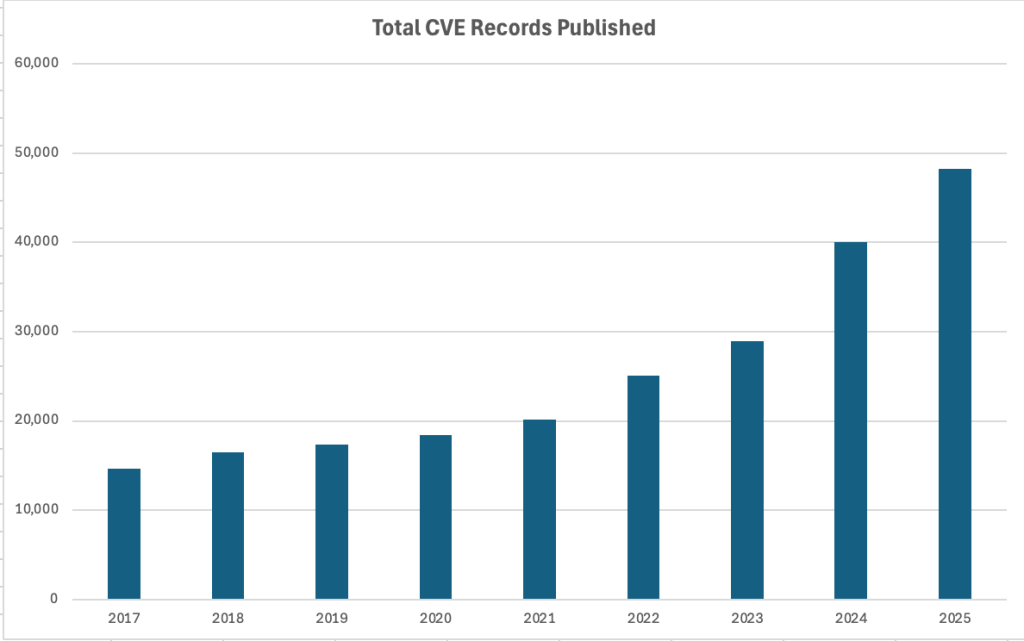
SOURCE: https://www.cve.org/about/Metrics
CSO
As a result, NIST will now forego enrichment for all but the most critical of vulnerabilities.
Backlogged CVEs received prior to March 1 will also be labeled “not scheduled.” None of those are critical vulnerabilities, NIST said, because those have always been handled first.
“They’ve just come out and publicly stated, ‘We are never going to get through this backlog,’“ Dustin Childs, head of threat awareness at Trend Micro’s Zero Day Initiative, told CSO.
In addition, NIST will no longer calculate severity scores for CVEs submitted with scores provided by the reporting organization.
Security leaders reliant on NIST enrichment will need to take stock of their technology inventories to see whether they fall under NIST’s priority list, Childs said. That’s not easy.
“Discovery is one of the most difficult problems we’re dealing with,” he noted, adding that it’s also not clear what software actually falls into the priority category. “Software used by the federal government is a very vague statement.”
Mounting CVE counts — with AI flaw discovery on the rise
Childs is not surprised that CVEs numbers have been going up, citing AI as part of the reason why.
“We’re already seeing more garbage CVEs — and more real CVEs — related to AIs,” he says.
Dealing with these CVEs is going to be a massive problem for companies. “People still don’t patch,” he says. “And we’re going to quadruple the number of patches they’re going to have to deploy. How do we build our defenses across the entire enterprise? I don’t know if we’ll get there before the bad guys do.”
According to the Forum of Incident Response and Security Teams (FIRST), 59,427 CVEs are expected to be submitted this year, up from a little over 48,000 in 2025. That makes 2026 the first year that CVEs will pass the 50,000 milestone.
“The sheer velocity of vulnerability discovery and exploitation is unlike anything we’ve seen before,” FIRST CEO Chris Gibson told CSO.
FIRST has also modeled “realistic scenarios” in which the total number of CVEs cracks 100,000 for 2026 — but that was in February, before Anthropic announced Mythos, its vulnerability-finding AI model many foresee as a structural shift for the cybersecurity industry.
“And if it’s not Mythos, or whatever else is coming out now, something is going to come out next week,” said Empirical Security founder Jay Jacobs, who also leads the Exploit Prediction Scoring System special interest group at FIRST.
Still, Jacobs is optimistic that turning to technology will help NIST deal with rising CVE volumes.
“Harold Booth has a lot of experience and skill working with AI over the last few years,” Jacobs told CSO. “So I’m expecting him to bring some expertise and I hope we do see some AI news there.”
Both large language models and AI agents are on the agency’s to-do list, as is old-fashioned robotic process automation (RPA), Booth said in his presentation at VulnCon, which Jacobs chairs. NIST also plans to delegate some of the work to CVE Numbering Authorities (CNAs), which includes security vendors and researchers.
“Among other things, we are pursuing efforts to determine how large language models and other machine learning tools can be leveraged to speed up analysis and enrichment tasks that are currently manual and labor-intensive,” Booth added in follow-up with CSO.
This story has been updated to include added comment from Harold Booth on NIST’s AI plans.
SUBSCRIBE TO OUR NEWSLETTER
From our editors straight to your inbox
Get started by entering your email address below.