



Qodo has announced three new platform capabilities: Cross-Repo Code Review, Custom Rules Miner, and Skill Review Standards. These new capabilities address a set of governance gaps that have emerged as AI-generated code reaches enterprise scale.
AI agents have fundamentally changed how software is built. Code that once required developers to write, test, and review is now generated and pushed by agents operating with increasing autonomy across the development lifecycle.
The governance systems that enterprises created for human-paced development were not designed for the agentic SDLC. Pull requests from teams with high AI adoption are already 154% larger, taking 91% longer to review, and shipping 9% more bugs (Google DORA 2025).
Organizations with historically strong governance frameworks are running into the same three problems:
“The volume of AI-generated code has outpaced every quality process enterprises had in place. Engineering organizations now need three things they have never had to govern at this scale: standards that exist somewhere a system can read and enforce, agents that apply those standards consistently, and visibility into the health of a codebase that no single engineer can hold in their head anymore. That is not a tooling problem. That is infrastructure,” said Itamar Friedman, CEO of Qodo.
With its new capabilities, Qodo is giving enterprises the ability to solve these problems and govern AI-generated code across repository boundaries; enforce standards that were previously unenforceable; and ensure that the standards teams have already defined are connected to every review.
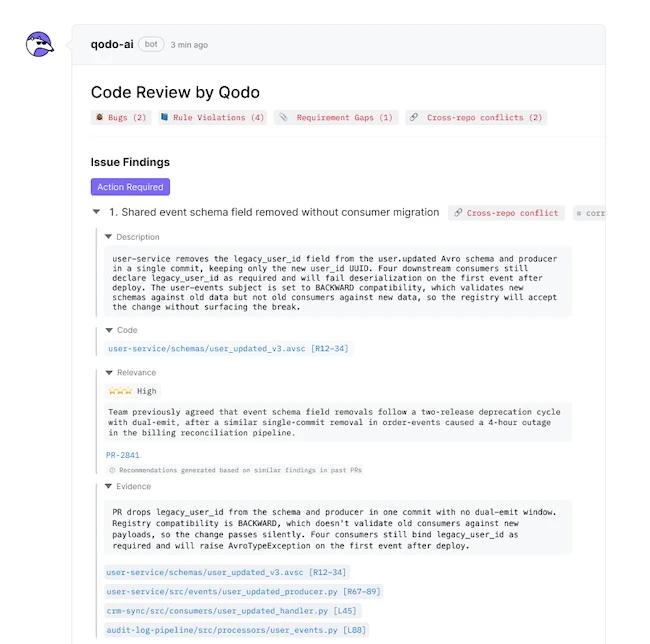
As engineering organizations scale, the most consequential bugs are rarely contained within a single repository. A change to a shared library, an exported API, a data schema, or an infrastructure file can introduce breaking changes across dozens of downstream services, with no warning surfaced at the point of merge.
Cross-Repo Code Review (Beta) extends Qodo’s Git plugin to close this gap. When a PR modifies a shared dependency, the agent reads the registered consumer repositories and surfaces impact findings directly on the PR before merge: function signature violations, API contract breaks, schema evolution, and infrastructure drift that only become visible at the intersection of repositories. Engineering teams receive a complete cross-system impact assessment as part of their standard review workflow, without changing how they work.
Enforcing coding standards at scale requires a prerequisite most approaches ignore: the standards have to exist somewhere a system can read them. For most engineering organizations, they don’t. They live in wikis, PR comments, and the institutional memory of senior engineers.
Qodo Rules Miner changes the starting point. Rather than requiring teams to define standards before enforcement can begin, it automatically discovers coding patterns from existing codebase behavior and PR history, then surfaces them as structured, enforceable rules within the Qodo platform. Standards that experienced engineers have consistently applied or consistently flagged become rules the entire organization can enforce, measure, and evolve, without manual authorship.
As organizations increasingly use agent skills to encode development workflows and best practices, managing those skills has become a governance challenge of its own. Qodo now provides centralized management for skills that contain code review instructions, coding standards, and engineering best practices. The platform discovers skills across repositories, surfaces them in a dedicated portal experience, and gives teams the ability to control and measure their impact.
With skill-level controls, analytics, and attribution, engineering organizations can manage review standards as a governed program rather than a collection of files distributed across repositories.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。