


The Android 17 rollout has started for supported Pixel devices, delivering new security and privacy capabilities before expanding to other devices later this year.
Google has improved location privacy features so users can choose to share their approximate location with websites and grant apps temporary access to their precise location when services require exact coordinates.
In previous Android versions, users had no OS-level way to grant an app access to only one or a few contacts. Contact Picker allows them to share selected contacts with an app instead of granting access to their entire address book, while READ_CONTACTS is reserved for apps that require ongoing access.
Find Hub’s Mark as lost feature allows users to lock a missing phone with biometrics, preventing anyone who knows the passcode from accessing data on the device or turning off location tracking. Marking a device as lost hides Quick Settings and prevents new Wi-Fi and Bluetooth pairings.
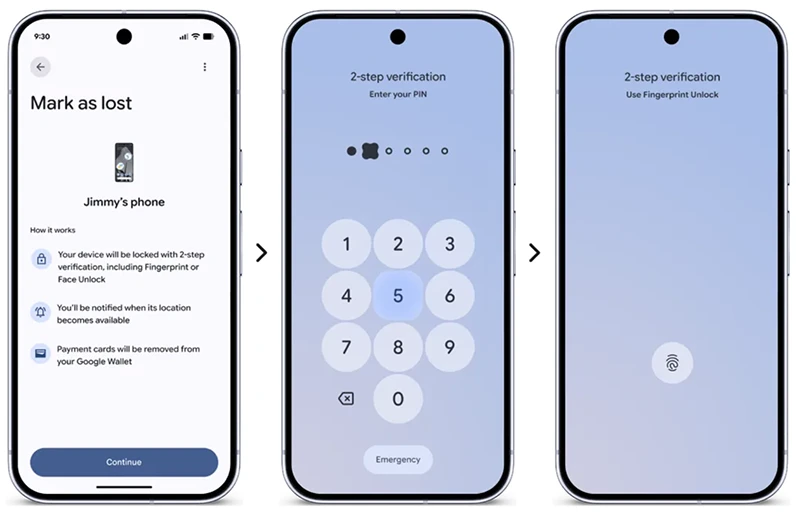
“Mark as lost” feature ‘Source: Google)
The company is expanding Live Threat Detection, an on-device AI feature that monitors app behavior and warns users about suspicious activity. New protections can detect actions such as SMS forwarding and misuse of accessibility overlays, which can be used to trick users.
Android 17 introduces dynamic signal monitoring, which detects known malicious behavior patterns in real time, such as apps hiding their icons, launching in the background, or abusing accessibility permissions. These protections will begin rolling out in the second half of the year.
To help protect users from sophisticated threats, Advanced Protection, Google’s one-tap security hardening mode, integrates scam detection for chat notifications, disables device-to-device unlocking and Chrome WebGPU support, and removes accessibility service access from apps that are not labeled as accessibility tools.
“To stop a thief who’s trying to guess their way into your phone, we also reduced the number of times someone can guess your PIN and added longer wait times between failed attempts,” Seang Chau, VP and GM of Android Platform, wrote in a blog.
Parental Controls are available on all devices that update to Android 17. This on-device feature is protected by a PIN and provides a direct link to Google Family Link, which offers additional capabilities such as School Time, app purchase approvals, and location alerts.
Parents can set daily screen time limits, schedule downtime that automatically locks a device at night, and restrict or block access to specific apps. They can also grant extra screen time when needed or extend a scheduled break. Web content filters can block explicit websites and search results.
“Historically, apps required broad, permanent permissions to access information like contacts, precise location and media files. Android 17 continues the shift toward privacy-preserving choices that grant temporary, session-based access only to the data the user explicitly selects,” Matthew McCullough, VP of Product Management, Android Developer, explained.
Android 17 introduces the ACCESS_LOCAL_NETWORK permission, which apps must request before discovering or connecting to devices on a local network, such as smart home devices or casting receivers. The change limits access to local network data and helps prevent unauthorized tracking or data collection. Apps can also use Android’s built-in device pickers to connect to devices without requesting the permission directly.
SMS OTP protection delays access to SMS messages for three hours. It applies to WebOTP and messages that follow the standard SMS OTP format. Default SMS apps, digital assistants, and companion device apps are exempt. Google recommends that other apps use the SMS Retriever API or SMS User Consent API instead of requesting direct access to SMS messages.
Android 17 adds support for post-quantum cryptography. Compatible devices can generate ML-DSA digital signature keys in secure hardware through the Android Keystore, helping protect against future quantum computing threats. The new APK Signature Scheme v3.2 combines traditional and ML-DSA signatures to strengthen app authentication and software distribution.
Apps targeting SDK 37 or later must mark native libraries loaded with System.load() as read-only. Otherwise, the system will block them from loading and throw an UnsatisfiedLinkError. This extends the Safer Dynamic Code Loading protection introduced in Android 14 for DEX and JAR files to native libraries.
When users enter passwords, PINs, and other sensitive data with a physical keyboard, the last typed character will no longer be displayed. Users can customize these settings, subject to support from device manufacturers. The feature is supported by Android’s built-in SDK components and will be supported in Compose 1.12 for SecureTextFields.

Read more:
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。