
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

D
Docker
V
V2EX
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
云风的 BLOG
云风的 BLOG
Blog — PlanetScale
Blog — PlanetScale
Recent Announcements
Last Week in AI
Last Week in AI
博客园 - Franky
Microsoft Security Blog
Hugging Face - Blog
Hugging Face - Blog
H
Hackread – Cybersecurity News, Data Breaches, AI and More
Vercel News
Vercel News
MyScale Blog
MyScale Blog
大猫的无限游戏
大猫的无限游戏
罗磊的独立博客
H
Help Net Security
月光博客
月光博客
Martin Fowler
Martin Fowler
博客园 - 【当耐特】
宝玉的分享
宝玉的分享
P
Proofpoint News Feed
GbyAI
GbyAI
腾讯CDC
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More

Help Net Security

Police arrest 10 suspected members of Black Axe cybercrime gang ShinyHunters claims it stole 1.4 million records from Udemy Sevii unveils Cyber Swarm Defense Mode to stop AI-driven attacks at scale Alleged Chinese hacker extradited to US over cyberattacks targeting COVID-19 research Cequence Agent Personas bring granular control and governance to enterprise AI agents NowSecure MARI gives enterprises evidence-based visibility into third-party mobile app risk The metrics killing your SOC, and what to use instead US state privacy fines reached $3.425 billion in 2025 Canada’s first SMS blaster case leads to three arrests Linux storage management tool Stratis 3.9.0 adds online encryption and cache-less pool startup TLS Connect gives SMBs a right-sized automated tool to manage TLS certificates Aptori expands its platform with autonomous offensive testing to reduce security bottlenecks Your IAM was built for humans, AI agents don’t care The AI criminal mastermind is already hiring on gig platforms 25 open-source cybersecurity tools that don’t care about your budget Product showcase: LuLu reveals unauthorized outbound connections from Mac apps Week in review: Claude Mythos finds 271 Firefox flaws, Vercel breach Users advised to drop passwords and make room for passkeys - Help Net Security Indirect prompt injection is taking hold in the wild - Help Net Security Compromised everyday devices power Chinese cyber espionage operations - Help Net Security New Cisco firewall malware can only be killed by pulling the plug - Help Net Security Meta is overhauling how you sign in, manage settings, and protect your accounts - Help Net Security Ubuntu 26.04 LTS delivers memory-safe system tools and live patching for Arm servers - Help Net Security OpenAI’s GPT-5.5 is out with expanded cybersecurity safeguards - Help Net Security AI is speeding up nation-state cyber programs - Help Net Security A study of 1,000 Android apps finds a privacy policy logging gap - Help Net Security IT spending to hit $6.31 trillion record, thanks to AI - Help Net Security Where AI in CI/CD is working for engineering teams - Help Net Security With AI's help, North Korean hackers stumbled into a near-undetectable attack - Help Net Security Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security
The hidden risk of non-human identities in AI adoption
Help Net Sec · 2026-05-13 · via Help Net Security

An employee with persistent, unsupervised admin access across critical systems, with no audit trail, no clear owner, and no regular access reviews, would raise immediate concern in most organizations.

Yet non-human identities and AI agents are often granted that same kind of persistent, broadly privileged access. As AI adoption grows, that gap is becoming harder to ignore.

NHIs today encompass far more than traditional service accounts and API keys. They also often include AI agents that make autonomous decisions, automated workflows with cross-system access, and shadow AI tools deployed by business users.
non-human identities AI adoption

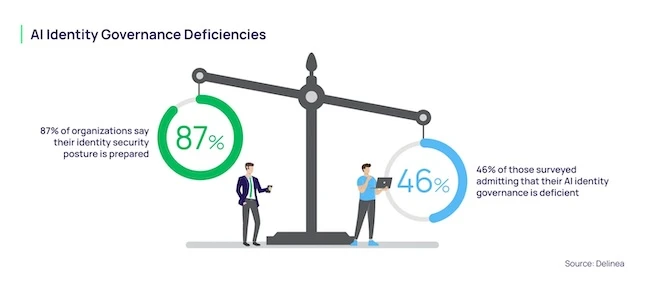
Security teams think they’re ready for AI adoption at scale. A recent Delinea survey shows 87% of organizations say their identity security posture is prepared. However, NHIs operate with speed and behavior patterns that legacy controls weren’t designed to handle, and IT teams are aware, with 46% of those surveyed admitting that their AI identity governance is deficient.

This dissonance represents a risky double standard in enterprise security.

Why the NHI double standard exists

Three fundamental factors drive this double standard, each reinforcing the others to create a cycle of compromised identity governance.

  • Priority of speed over governance: Business pressure to deploy AI initiatives fast means identity controls get relaxed or skipped entirely. The survey found that 90% of organizations place pressure on security teams to loosen access controls to support AI-driven automation.

    When tension arises between security requirements and business speed, fewer than 1 in 3 organizations enforce security requirements consistently.

  • Poor monitoring of shadow AI: Unsanctioned agents operate outside any governance framework entirely. A significant 53% of surveyed organizations regularly encounter unauthorized AI tools and agents accessing company systems.

    These deployments bypass traditional provisioning processes, creating unmonitored access points that security teams struggle to detect.

  • Unchecked NHI activity: Traditional identity management systems rely on predictable, human-centric workflows. Legacy IAM tools lack the velocity and dynamic capabilities needed to govern autonomous agents that make independent decisions and request elevated privileges without warning.

The operational reality makes this challenge even more complex. According to the survey data, 74% of organizations say standing access for NHIs and AI agents is necessary to meet uptime expectations. Meanwhile, 59% report they lack viable alternatives to persistent access for these accounts. This creates a situation where security teams knowingly accept risk under operational pressure.

What does closing the AI identity risk gap require?

Organizations must confront the AI security confidence paradox. Expressing high confidence in AI readiness despite knowing there are fundamental AI-related identity governance gaps happens because information is incomplete. Security teams can’t protect against what they can’t see.

Consider this: 82% of organizations report confidence in their ability to discover NHIs with access to production systems, but fewer than 1 in 3 actually validate NHI and AI agent activity in real-time. The vast majority of IT decision-makers surveyed admit to at least some sort of identity visibility gap, with NHIs representing the largest blind spot.

Step 1: Visibility

Before implementing new access controls or policies, organizations must establish a clear inventory of which NHIs exist—including shadow AI use, what they have access to, and whether any of that access is standing or persistent. Without foundational visibility, any governance efforts become guesswork rather than risk-based decision-making.

Step 2: Zero standing privilege

Just-in-time and ephemeral access represent the goal, even if they’re not immediately achievable for most organizations. The survey shows organizations are more than twice as likely to use long-lived credentials (34%) compared to modern just-in-time authorization (16%). As Gerry Auger, head of SimplyCyber, notes: “I’ll count it as a win if we just have an inventory of all the identities that have standing access.”

More practical governance tips
  • Watch for NHIs requesting elevated privileges unexpectedly because it often signals either compromised accounts or poorly configured automation.
  • Flag accounts with no clear owner or business justification for immediate review.
  • Treat NHI access reviews with the same rigor you apply to human access reviews, including regular certification and deprovisioning of unused accounts.

Build secure AI without slowing innovation

You can’t halt AI adoption. The reality-based goal is closing the visibility gap that allows risky access patterns to persist undetected. Organizations need automated discovery tools that can map machine identities across cloud and hybrid environments in real time. Governance frameworks must operate at speed without the friction that drives teams to bypass strict oversight.

This requires upgrading identity infrastructure to handle the velocity and unpredictability of agentic AI. Security teams can satisfy business demands for speed without abandoning identity governance entirely.

Download: 2026 Identity Security Report