






Phishing activity declined by roughly 20% in both 2024 and 2025, according to research from Zscaler’s ThreatLabz team. The drop followed years of growth that pushed phishing activity above 2 billion hits in 2023.
“Phishing volume measured by blocked emails is no longer a reliable proxy for phishing risk.”
Researchers found greater use of targeted phishing campaigns designed to resemble routine business communications. The services sector recorded a 65.5% year-over-year increase in phishing activity, making it the most targeted industry in the dataset.
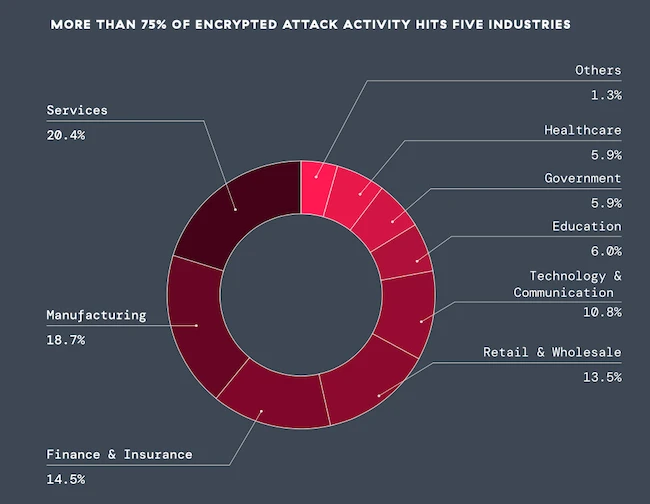
Encrypted attack hits by industry (Source: Zscaler)
Billing notices, onboarding documents, renewals, support requests, and document-sharing workflows appeared frequently in campaigns targeting the sector. One campaign cited by Zscaler used tax-themed lures and legitimate services such as OneDrive to target more than 29,000 users across 10,000 services organizations.
Microsoft and Google topped the list of brands most frequently impersonated in phishing campaigns. Credentials tied to those platforms often provide access to multiple business services through a single account.
A Microsoft 365 login can unlock email, files, Teams, SharePoint, OneDrive, and connected SaaS applications. Access to one account can expose a much larger portion of an organization’s environment.
ThreatLabz identified 413,524 AI-generated website instances and classified 37,447 of them as malicious.
The activity was associated with platforms including Manus AI, Blackbox AI, Anything AI, Bolt AI, Vercel v0, and Framer AI. Unattributed AI tooling accounted for the largest share of observed activity, followed by Manus AI and Blackbox AI.
Researchers documented phishing pages, fake applications, and brand impersonation sites created through these services.
One case involved a counterfeit Coinbase Wallet website generated with an AI application builder. The site promoted a fake browser extension and was hosted on a legitimate platform. Researchers noted that branding from the AI platform remained embedded in parts of the page metadata.
“What used to require a developer, a template kit, and time now often takes little more than a prompt and a few iterations.”
More than 95% of phishing activity observed by Zscaler was delivered over encrypted channels.
Researchers also found that 87% of all malicious activity blocked during 2025 was delivered over HTTPS. Credential theft, session abuse, and redirects increasingly occur through the same encrypted connections employees use to access cloud applications and business services.
“What makes this shift more dangerous is where compromise actually happens: in the browser, over HTTPS.”
ThreatLabz identified phishing kits that combine adversary-in-the-middle (AiTM) and browser-in-the-middle (BiTM) techniques to intercept login sessions and capture credentials, MFA codes, and session tokens in real time.
BlackForce, a phishing-as-a-service platform cited by ThreatLabz, was among the examples. The kit captures credentials, MFA codes, and session information during the login process, turning a single click into a session-level compromise.
Between October 2025 and March 2026, external decoys deployed in customer environments recorded 89.9 million hostile interactions from 1.37 million unique attacker IP addresses.
Attackers were probing exposed services and looking for assets that could provide a path into an organization. Researchers described reconnaissance efforts focused on exposed assets, leaked credentials, misconfigured applications, and forgotten subdomains.
ThreatLabz observed more than 121,000 AWS-hosted IP addresses probing customer environments.
Public cloud platforms accounted for a significant share of the attacker infrastructure observed in the dataset. Researchers said cloud-hosted infrastructure can be provisioned quickly, used for reconnaissance, and replaced when it is blocked or detected.
Zscaler expects phishing campaigns to become more automated in 2026, with AI agents targeting other AI agents, attacks moving between email, messaging apps, SMS, and voice channels, and attackers focusing on active sessions and identities instead of credentials alone.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。