







Cybersecurity has become a key priority for small and medium-sized businesses due to growing threats and wider AI adoption. An IDC survey of 2,200 SMBs in eight markets examined how organizations manage cyber risks, prepare for AI-related threats, and handle third-party vendor security.
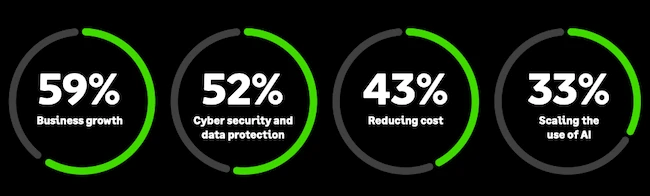
Top business priorities for the year (Source: IDC)
60% of SMBs expect to increase cybersecurity spending over the next 12 months. The findings show that businesses continue to rely on reactive approaches and remain underprepared for emerging risks.
Data protection and cybersecurity rank high on SMB priorities over the next 12 months, behind business growth and ahead of cost reduction. SMBs plan to increase cybersecurity spending over the next year, showing greater awareness of security risks. Cost pressures and accelerating AI adoption can slow progress and create a gap between intention and action, leaving businesses struggling to translate investment into stronger security practices.
Security responsibilities remain part of broader IT functions, with less defined ownership and fewer documented processes. Cybersecurity activity often becomes reactive, with action following incidents instead of routine oversight. Stronger accountability and consistent practices are necessary because increased spending alone may not improve security readiness.
Tool management, staff training, and incident response planning remain difficult. Security maturity depends on operational discipline that helps maintain existing safeguards during business growth.
SMBs can strengthen cybersecurity posture through stronger data governance, security controls, and transparency supported by formal review cycles, defined accountability, and documented processes.
Small and medium-sized businesses encounter a broad and less predictable mix of threats, including phishing, social engineering, insider risk, third-party exposure, and supply chain vulnerabilities. Resilience depends on how quickly organizations detect, contain, and resolve problems while maintaining trust, cash flow, and business operations.
Nearly half of SMBs say keeping up with new cyber threats is their biggest security concern. AI-powered attacks, sophisticated phishing attempts, and expanded use of cloud and SaaS tools make risks harder to track and manage. Limited specialist skills, competing operational priorities, and budget constraints can make continuous monitoring and structured risk assessment difficult, which can delay the identification of problems and response efforts.
AI is increasing pressure on SMBs, particularly smaller businesses with limited resources and weaker security oversight. SMBs remain in the early stages of preparing for AI-related threats, particularly smaller organizations. Eighty-four percent of micro businesses and 65% of small businesses say they are unprepared or taking early steps. AI-powered phishing, deepfakes, and automated exploitation continue to become more convincing and harder to detect.
“The research suggests many SMBs still believe they are not a prime target for cyberattacks, despite threats becoming more sophisticated and widespread. IDC recommends SMBs embed cybersecurity into AI initiatives from the outset and take an organization-wide approach to cyber resilience. Businesses that close the gap between growth ambitions and security readiness will be best placed to build long-term digital trust with customers, partners and investors,” said Joel Stradling, Senior Research Director, European Security at IDC.
Organizations are adopting AI faster than they can understand risks, assess exposure, or evaluate third-party provider security. Visibility, governance, and internal security expertise continue to present challenges. Strong oversight and practical safeguards are necessary to reduce exposure and support business outcomes.
Vendor risk reviews often take place at the start of a relationship or during contract renewal periods instead of continuous monitoring. Issues can remain undetected until disruption occurs. Micro and small businesses remain more exposed because a significant share report limited or no ongoing monitoring of third-party services.
Vendor trust depends on practical information about security practices and data handling. Businesses value transparency around how customer data is protected, where it is stored, and what happens if an incident occurs.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。