





AI deployments are moving into environments with tighter controls around data, infrastructure, and system operations. Organizations are building AI systems across multiple providers, platforms, and computing environments while managing governance, security, and compliance obligations within defined boundaries. NTT DATA’s 2026 Global AI Report A Playbook for Private and Sovereign AI examined these conditions in more than 2,500 organizations.
About 35% of CAIOs identify enabling private and sovereign AI as their biggest barrier to adoption, often requiring significant changes to infrastructure.
Private AI focuses on controlling access to sensitive data and keeping that data inside organizational boundaries. Sovereign AI adds demands around where data resides, how it moves between regions, and where AI systems can process it.
“As AI evolves, private and sovereign approaches are testing enterprise readiness,” said Abhijit Dubey, CEO and Chief AI Officer, NTT DATA. “The organizations that are succeeding are going beyond regulatory compliance and risk mitigation. They are building the operating foundation for AI that can perform across markets, jurisdictions and business environments. Our research shows AI leaders are pulling ahead by treating architecture, infrastructure and governance as strategic requirements.”
Cross-border data restrictions have become a major challenge because data can move legally at a slower rate than AI architectures assume. This creates competing priorities around performance, compliance, efficiency, and control.
Organizations continue to translate private and sovereign AI demands into operating models and architecture. AI leaders build those conditions into infrastructure and governance decisions early in deployment planning. Their operating environments support movement from pilot projects to larger deployments in regulated settings.
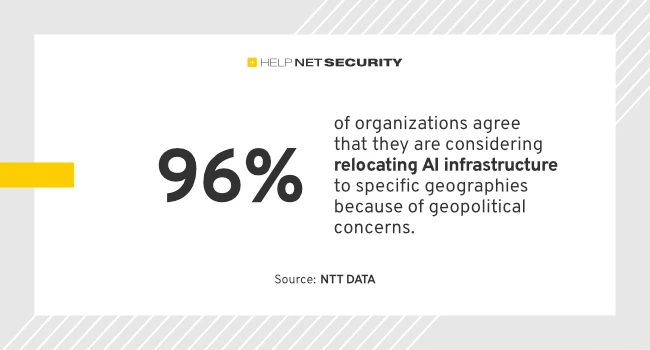
About 95% of organizations consider private or sovereign AI important to their AI strategy, and 96% are considering relocating AI infrastructure to specific regions because of geopolitical pressures and supply chain concerns.
These considerations fall into three categories. Mandated AI sovereignty refers to legal or geopolitical requirements for domestic control. Regulated privacy requires organizations to demonstrate auditable control over data, models, and operations. Strategic AI autonomy reflects efforts to gain greater control over intellectual property, costs, and vendor dependence.
About 98% of C-suite executives say it is imperative to establish a private domain that protects proprietary intellectual property and sensitive data through a GenAI model that cannot be trained publicly.
Nearly every company is reviewing how to integrate AI into legacy environments, and 96% say their infrastructure is slowing AI adoption.
Organizations are designing AI architectures to support multiple jurisdictions, each with distinct data, regulatory, and infrastructure constraints tied to private and sovereign AI.
Companies globally cite privacy violations and misuse of customer data related to AI and GenAI as key concerns because keeping data local requires storage capacity, processing power, and resilient networks within defined boundaries.
Data privacy and sovereignty across regions and environments are considered the top security or compliance governance concern, and 57% of CEOs rank them as a risk for their organizations.
Infrastructure, data, and model design sit at the center of sovereignty strategies, and organizations are beginning to separate data from intelligence.
Different AI workloads create different demands for computing density, network design, resilience, and data gravity. Regulatory and compliance obligations can make workload placement as important as performance considerations. Organizations are adopting hybrid architectures that reserve controlled environments for sensitive data, predictable performance, and regulatory oversight. Lower-risk workloads run in other environments.
Most organizations recognize that AI must operate in controlled and compliant environments, and many continue to determine how to build scalable architectures and operating models around those demands. Private and sovereign AI conditions add complexity and create execution and confidence gaps.
Sovereign AI investments in the European Union are largely driven by regulation. In parts of the Middle East, political priorities and national strategy often influence investment decisions. Industries with significant consequences associated with failure, including public sector organizations, healthcare, natural resources, and manufacturing, are more likely to adopt sovereign approaches to designing and deploying AI solutions over the next two years.
AI leaders are taking a more structured approach to governance by embedding it from the beginning of AI initiatives. They are more likely to adopt centralized governance structures and support federated operating models. They also tend to formalize accountability through executive-backed steering committees that bring together business, legal, and security stakeholders.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。