






Anthropic and its Project Glasswing partners have identified more than 10,000 high- or critical-severity vulnerabilities in critical software systems, the company announced in an update on the project’s progress.
In April 2026, Anthropic introduced Claude Mythos Preview, a new large language model that can autonomously find zero-day vulnerabilities and create exploits for them.
The company also launched Project Glasswing and gave Amazon Web Services, Apple, Broadcom, Cisco, CrowdStrike, Google, JPMorganChase, the Linux Foundation, Microsoft, NVIDIA, Palo Alto Networks, and other partners in the open source community access to the LLM, to help them secure critical software before AI systems can be used to target it.
Since then, with Mythos’ help, several companies, including Cloudflare and Mozilla, have discovered hundreds of vulnerabilities in their codebases.
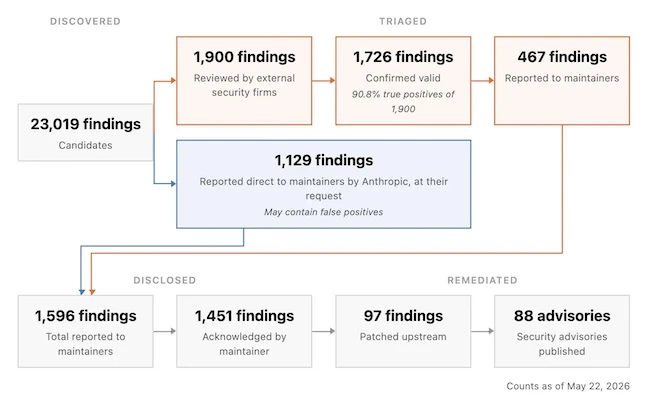
Anthropic has also scanned more than 1,000 open-source projects with Mythos, and has identified 23,019 issues, of which 6,202 were high- or critical-severity vulnerabilities.
The company and six independent security research firms have assessed 1,752 of those high- or critical-severity findings, and more than 90% were validated as true positives, the company added.
Anthropic’s dashboard of open-source vulnerabilities, showing vulnerabilities of all severities
More disclosures of vulnerabilities unearthed with Mythos’ help are yet to come, as the project was started just a couple of months ago and the coordinated vulnerability disclosure process typically takes time. (Newly discovered flaws are kept private, usually for 90 days or until patches are available, before being made public.)
For example, Mythos identified a vulnerability in wolfSSL, an open-source cryptography library used by billions of devices, and constructed an exploit that would let an attacker forge certificates that would allow them to host a fake website for a bank or email provider. The vulnerability has been patched, but technical details are still under wraps.
Anthropic says that even though they made sure to deliver detailed vulnerability reports to open source maintainers, the latter have become a major bottleneck in the AI-driven vulnerability discovery process.
“The relative ease of finding vulnerabilities compared with the difficulty of fixing them amounts to a major challenge for cybersecurity,” the company said.
To help open source maintainers process and triage bug reports, Anthropic partnered with the Open Source Security Foundation’s Alpha-Omega project.
To make vulnerability discovery and patching easier, Anthropic released Claude Security in public beta for Claude Enterprise customers.
Its Cyber Verification Program allows approved security professionals to use its models for legitimate cybersecurity work with fewer restrictions, Anthropic noted, and said it is also making tools used with Mythos Preview available to qualifying security teams. These include custom skills, an automated scanning and reporting framework, and a threat-modeling tool for identifying and prioritizing attack targets.
Anthropic plans to work with partners, including the US government and allied governments, to expand Project Glasswing, and intends to make Mythos-class models generally available, but only after developing stronger safeguards.
“At present, no company — including Anthropic — has developed safeguards strong enough to prevent such models from being misused and potentially causing severe harm,” the company concluded.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。