


Attackers are hosting counterfeit installers and plugins on GitHub and SourceForge that pose as widely used software, including ChatGPT, Claude, AutoTune, Kontakt, Ableton Live, and ZENOLOGY. The downloads deliver a backdoor called DinDoor, which then loads a remote access Trojan built on the Deno JavaScript runtime, according to Malwarebytes.
Compromised YouTube channels push victims toward the malicious repositories. The videos promoting the fake tools have accumulated more than 50,000 views. The attackers rotate through GitHub accounts and create multiple repositories per account, refreshing the lures as old ones are taken down. Malwarebytes reported the activity to GitHub, which removed the flagged repositories, though new ones are expected to appear.
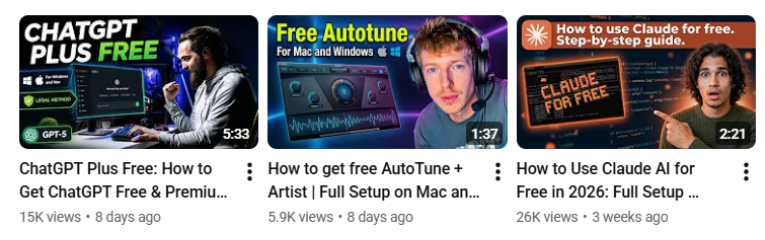
Compromised YouTube channels with AI-generated videos (Source: Malwarebytes)
The malicious repositories ask visitors to open a terminal and paste a command that downloads an MSI installer or a PowerShell script from GitHub. Both Windows and macOS commands are offered. Once executed, the script installs the Scoop package manager and WinGet, then uses them to install the legitimate Deno runtime. Deno is then used to fetch and run the DinDoor backdoor directly from a remote server, with the next stage executed in memory through standard input so it never touches disk.
DinDoor sets up persistence through a registry Run key, reports system details to a command-and-control server, and pulls down further payloads. In the cases analyzed, one of those payloads is a Deno-based RAT that has previously been tracked under the name Smokest. Code similarities suggest the same author or team built both tools.
The RAT gives operators wide control of an infected machine. It can execute arbitrary commands and PowerShell scripts, capture screenshots, manage files, launch or kill processes, and open SOCKS5 proxy tunnels. Its built-in stealer module targets more than 50 cryptocurrency wallet extensions and 10 wallet applications, including Atomic Wallet, Exodus, Electrum, and ByteCoin. It also pulls data from Chrome, Brave, Edge, Opera, Vivaldi, and other Chromium-based browsers, along with Telegram, Discord, and Lightcord.
One feature stands out. To stream live video of a victim’s screen, the RAT silently launches Microsoft Edge, connects to it through the Chrome DevTools Protocol, and injects a WebRTC page. Edge then relays encrypted video frames directly to the attacker over a peer-to-peer connection, with traffic flowing through a legitimate browser process. This design helps the operator evade network detection.
The campaign blends trusted hosting, legitimate development tooling, and social engineering. GitHub and SourceForge carry credibility with developers and power users. Scoop, WinGet, and Deno are mainstream tools. Stitching them together lets the attackers stay under the radar of security products that look for unsigned binaries or unusual download sources.
“The fake software appears designed to target creators, AI enthusiasts, gamers, and technically inclined users who are more likely to download unofficial tools, cracked software, or community-distributed installers from sites like GitHub and SourceForge,” Gabriele Orini, Malware Research Engineer at Malwarebytes, explained.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。