


Smart TVs in living rooms run small apps that show fish tanks, clocks, solitaire games, and slideshows of puppies. A share of those apps can also send other people’s internet traffic out through the home connection.
Spur Intelligence scanned 6,038 apps across LG webOS and Samsung Tizen and found 2,058 that contain residential proxy software. On LG webOS, 42.5 percent of apps carried such code. On Samsung Tizen, the rate was 26.9 percent. Across both platforms it reached 34.1 percent.
A residential proxy lets a third party send web requests that appear to originate from a home internet connection. Embedded in a TV app, the SDK uses the device’s network link to carry that traffic. The visible app stays calm and ad-light. The connection earns money in the background.
“Smart TVs are almost ideal proxy hosts. They sit on the same home network as everything else, but they do not feel like computers, so people rarely audit them like computers. There is no battery drain to notice, no cellular bill to spike, no app switcher full of suspicious background activity. A TV can stay plugged in, signed in, and online for years while the user thinks of it as furniture,” Trevor Sutter from Spur Intelligence explained.
The proxy software asks permission a single time. All three prompts in the dataset state that the proxy keeps running after the app closes. A Bright Data prompt in a game called Galactic Harmony offers ad-free play in exchange for letting the company use the device’s IP address for web indexing. A Pac-Man title on Tizen presents the same exchange.
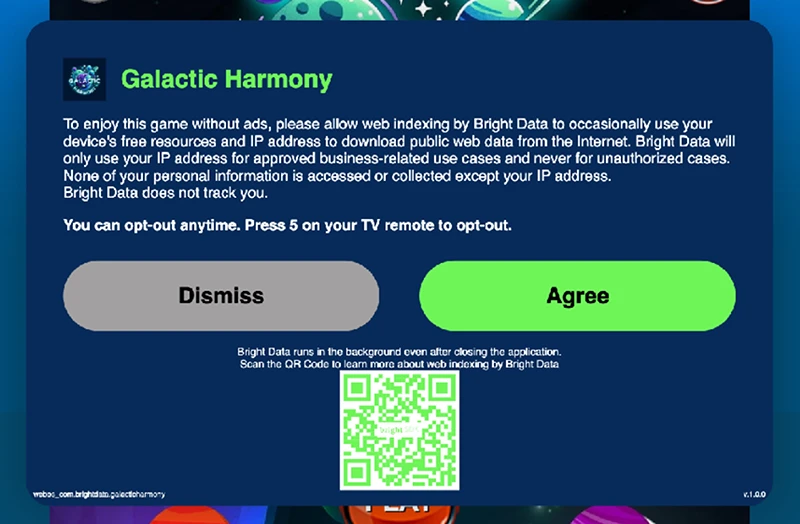
Galactic Harmony notice (Source: Spur Intelligence)
“Bright Data, Bright Data Ltd, and Bright SDK account for 367 proxy-flagged apps in the dataset. Honeygain UAB (subsidiary of Oxylabs) shows up as the publisher on another 16,” Sutter said.
Some of the inventory consists of thin shovelware games, screensavers, and utility shells shipped at scale so the software has somewhere to run. The app serves as the wrapper. The residential IP address is the product.
Amazon prohibits this category through its Device and System Abuse Policy, which bars apps that facilitate proxy services for third parties. Roku reportedly bars developers from using Bright SDK and similar services, and affected apps disappeared after the company was contacted. LG and Samsung have yet to publish an equivalent policy, and the same business model continues to appear at scale on webOS and Tizen.
A TV app acting as a proxy runs inside the home network. If a provider permits requests to private or local addresses, or if filtering fails, the device can reach router admin panels, NAS devices, printers, cameras, and developer machines.
The Bright Data sample ships with a blocklist covering private ranges including 10.0.0.0/8, 172.16.0.0/12, and 192.168.0.0/16. The local Massive and Honeygain/Oxylabs samples lacked a comparable private-range blocklist. The provider’s filtering and customer vetting form the boundary, and the device owner lacks any means to verify it from the TV.
“We did not rely on store descriptions or permission prompts. We downloaded the actual LG webOS and Samsung Tizen app packages, unpacked them, and scanned the files inside. The fingerprints looked for confirmed SDK artifacts: Bright Data brd_api.js and brd_sdk services, Massive clients and .massivesdk services, Honeygain/Oxylabs SDK files and service names, and related tokens or package names. Every app counted there had a confirmed proxy SDK fingerprint,” Sutter said.
Bright Data, Massive, and Oxylabs responded before publication. Bright Data said consent and independent audits separate a legitimate network from a harmful one, and that it approves use only for verified business, research, and journalistic purposes. Massive said its network users pass a Know Your Customer process and that its technical controls operate server-side. Oxylabs said it restricts access to private and local ranges through filtering, traffic inspection, and blocklists, and that only applications approved through its Honeygain SDK Partnership Program enter its proxy network.
“The proxy providers contacted for this research emphasized customer vetting, traffic restrictions, and abuse-prevention controls. Those controls may reduce risk, but they do not change the underlying reality that residential proxy infrastructure is being embedded at scale in devices that most consumers do not recognize as participating in such networks,” Sutter concluded.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。