
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

博客园 - Franky
J
Java Code Geeks
腾讯CDC
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
Jina AI
Jina AI
博客园 - 司徒正美
Stack Overflow Blog
Stack Overflow Blog
美团技术团队
L
LangChain Blog
WordPress大学
WordPress大学
A
About on SuperTechFans
Martin Fowler
Martin Fowler
月光博客
月光博客
Y
Y Combinator Blog
U
Unit 42
D
Docker
Recent Announcements
Hugging Face - Blog
Hugging Face - Blog
B
Blog
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
G
Google Developers Blog
Last Week in AI
Last Week in AI
T
The Blog of Author Tim Ferriss
让小产品的独立变现更简单 - ezindie.com

Help Net Security

Police arrest 10 suspected members of Black Axe cybercrime gang ShinyHunters claims it stole 1.4 million records from Udemy Sevii unveils Cyber Swarm Defense Mode to stop AI-driven attacks at scale Alleged Chinese hacker extradited to US over cyberattacks targeting COVID-19 research Cequence Agent Personas bring granular control and governance to enterprise AI agents NowSecure MARI gives enterprises evidence-based visibility into third-party mobile app risk The metrics killing your SOC, and what to use instead US state privacy fines reached $3.425 billion in 2025 Canada’s first SMS blaster case leads to three arrests Linux storage management tool Stratis 3.9.0 adds online encryption and cache-less pool startup TLS Connect gives SMBs a right-sized automated tool to manage TLS certificates Aptori expands its platform with autonomous offensive testing to reduce security bottlenecks Your IAM was built for humans, AI agents don’t care The AI criminal mastermind is already hiring on gig platforms 25 open-source cybersecurity tools that don’t care about your budget Product showcase: LuLu reveals unauthorized outbound connections from Mac apps Week in review: Claude Mythos finds 271 Firefox flaws, Vercel breach Users advised to drop passwords and make room for passkeys - Help Net Security Indirect prompt injection is taking hold in the wild - Help Net Security Compromised everyday devices power Chinese cyber espionage operations - Help Net Security New Cisco firewall malware can only be killed by pulling the plug - Help Net Security Meta is overhauling how you sign in, manage settings, and protect your accounts - Help Net Security Ubuntu 26.04 LTS delivers memory-safe system tools and live patching for Arm servers - Help Net Security OpenAI’s GPT-5.5 is out with expanded cybersecurity safeguards - Help Net Security AI is speeding up nation-state cyber programs - Help Net Security A study of 1,000 Android apps finds a privacy policy logging gap - Help Net Security IT spending to hit $6.31 trillion record, thanks to AI - Help Net Security Where AI in CI/CD is working for engineering teams - Help Net Security With AI's help, North Korean hackers stumbled into a near-undetectable attack - Help Net Security Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security
Webworm APT targets European government organizations wit...
Anamarija Po · 2026-05-20 · via Help Net Security

ESET has released an analysis of the 2025 activity of Webworm, a China-aligned APT group tracked as Space Pirates and UAT-8302. Active since at least 2022, the group initially focused on targets in Asia, but has recently expanded its operations into Europe.

ESET observed Webworm targeting government organizations in Belgium, Italy, Poland, Serbia, and Spain during 2025. The group also expanded its activity into South Africa, where researchers identified activity involving a local university.

Discord messages expose infrastructure and targets

By decrypting more than 400 Discord messages used for command-and-control (C&C) communication, ESET gained visibility into the group’s infrastructure and operations. The analysis revealed reconnaissance activity involving more than 50 unique targets.

“Through our analysis, we were fortunate enough to recover commands executed from a server that gave a view into the group’s potential initial access techniques, using an open-source vulnerability scanner as well as identifying some of its focused targets,” said Eric Howard, ESET researcher who investigated the campaign.

The recovered information led ESET to an attacker-operated GitHub repository used to host staged malware and supporting tools that could be downloaded onto victim systems.

The repository contained artifacts including the SoftEther VPN application. Researchers identified an IP address in a SoftEther configuration file that matched infrastructure previously linked to Webworm.
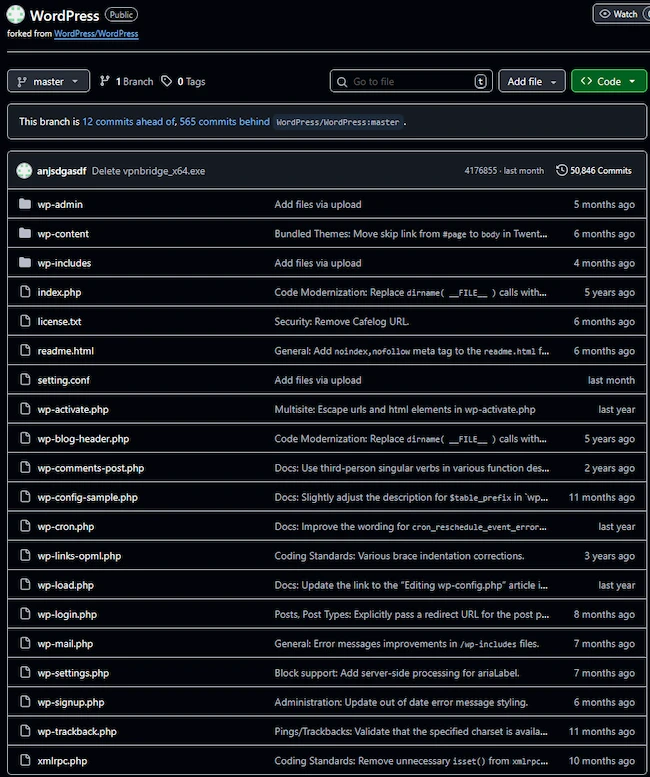
Webworm APT campaign Europe

Forked WordPress repository (Source: ESET)

New backdoors

According to ESET, the group’s latest campaigns introduced two new backdoors: EchoCreep and GraphWorm.

EchoCreep uses Discord for C&C communication, allowing attackers to upload files, send runtime reports, and receive commands.

GraphWorm relies on Microsoft Graph API and OneDrive endpoints to retrieve tasks and upload victim information.

The group expanded its use of proxy tools. Existing proxy capabilities were supplemented with custom tools including WormFrp, ChainWorm, SmuxProxy, and WormSocket. Based on the number and complexity of these tools, ESET believes Webworm may be building a larger hidden network by using compromised systems as proxy infrastructure.

During the investigation, ESET discovered that Webworm had started using WormFrp to retrieve configurations from a compromised AWS S3 bucket.

“It is apparent that through this S3 bucket, Webworm can leverage data exfiltration while an unsuspecting victim foots the bill for the service,” Howard said.

Between December 2025 and January 2026, Webworm operators uploaded 20 new files to the service, two of which had been exfiltrated from a government organization in Spain.

ESET noted that Webworm continues to stage files on GitHub and expects the group to maintain that approach in future campaigns.