
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

MongoDB | Blog
MongoDB | Blog
B
Blog RSS Feed
MyScale Blog
MyScale Blog
M
MIT News - Artificial intelligence
H
Hackread – Cybersecurity News, Data Breaches, AI and More
J
Java Code Geeks
U
Unit 42
Blog — PlanetScale
Blog — PlanetScale
L
LangChain Blog
C
Check Point Blog
WordPress大学
WordPress大学
Last Week in AI
Last Week in AI
人人都是产品经理
人人都是产品经理
T
Tailwind CSS Blog
Vercel News
Vercel News
腾讯CDC
GbyAI
GbyAI
有赞技术团队
有赞技术团队
S
SegmentFault 最新的问题
H
Help Net Security
博客园 - 三生石上(FineUI控件)
D
DataBreaches.Net
Microsoft Security Blog
小众软件
小众软件

Help Net Security

Police arrest 10 suspected members of Black Axe cybercrime gang ShinyHunters claims it stole 1.4 million records from Udemy Sevii unveils Cyber Swarm Defense Mode to stop AI-driven attacks at scale Alleged Chinese hacker extradited to US over cyberattacks targeting COVID-19 research Cequence Agent Personas bring granular control and governance to enterprise AI agents NowSecure MARI gives enterprises evidence-based visibility into third-party mobile app risk The metrics killing your SOC, and what to use instead US state privacy fines reached $3.425 billion in 2025 Canada’s first SMS blaster case leads to three arrests Linux storage management tool Stratis 3.9.0 adds online encryption and cache-less pool startup TLS Connect gives SMBs a right-sized automated tool to manage TLS certificates Aptori expands its platform with autonomous offensive testing to reduce security bottlenecks Your IAM was built for humans, AI agents don’t care The AI criminal mastermind is already hiring on gig platforms 25 open-source cybersecurity tools that don’t care about your budget Product showcase: LuLu reveals unauthorized outbound connections from Mac apps Week in review: Claude Mythos finds 271 Firefox flaws, Vercel breach Users advised to drop passwords and make room for passkeys - Help Net Security Indirect prompt injection is taking hold in the wild - Help Net Security Compromised everyday devices power Chinese cyber espionage operations - Help Net Security New Cisco firewall malware can only be killed by pulling the plug - Help Net Security Meta is overhauling how you sign in, manage settings, and protect your accounts - Help Net Security Ubuntu 26.04 LTS delivers memory-safe system tools and live patching for Arm servers - Help Net Security OpenAI’s GPT-5.5 is out with expanded cybersecurity safeguards - Help Net Security AI is speeding up nation-state cyber programs - Help Net Security A study of 1,000 Android apps finds a privacy policy logging gap - Help Net Security IT spending to hit $6.31 trillion record, thanks to AI - Help Net Security Where AI in CI/CD is working for engineering teams - Help Net Security With AI's help, North Korean hackers stumbled into a near-undetectable attack - Help Net Security Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security
Hundreds of AI-powered iOS apps found exposing credential...
Sinisa Markovic · 2026-06-22 · via Help Net Security

Mobile app developers are packing AI features into everything from writing assistants to productivity tools and lifestyle apps. New research shows that securing access to those services remains a challenge.
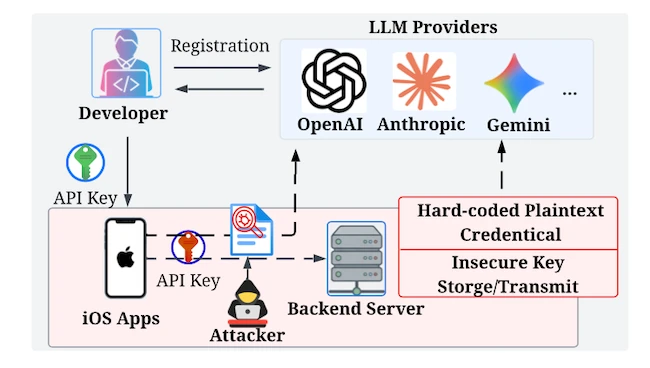
iOS apps credential leakage

LLM API credential leakage via network traffic interception (Source: Research paper)

Researchers from Wake Forest University analyzed 444 iOS applications with LLM features and found 282 that exposed exploitable credentials or backend access mechanisms. The affected apps covered 13 categories, including productivity, entertainment, lifestyle, education, utilities, and health and fitness.

LLM-powered applications reached 17 billion downloads in 2025 and accounted for 13% of all mobile app downloads.

“LLM API key leakage is a widespread and systemic issue in the iOS ecosystem, affecting 26% of analyzed Apps across diverse categories and developer types. The vulnerability’s impact extends from niche Apps to popular apps with hundreds of thousands of users,” the researchers noted.

The team began with more than 38,000 App Store listings before narrowing the dataset to 444 applications with confirmed LLM functionality. Among those apps, 64% exposed credentials or access mechanisms that remained exploitable during testing.

The issue was not confined to little-known applications. Fifteen percent of vulnerable apps had more than 1,000 user ratings, and the most popular affected app had accumulated more than 2.3 million ratings.

Among the vulnerable apps, 136 exposed authentication tokens, 92 allowed unauthenticated backend access, and 54 exposed plaintext API keys. In 28 of the plaintext key cases, the applications also exposed system prompts used by the underlying AI service.

Productivity apps accounted for the largest number of vulnerable applications, followed by entertainment and lifestyle apps. Health & Fitness recorded the highest leakage rate among the categories examined.

The largest group of vulnerable applications relied on custom developer-operated backends. Researchers identified 155 apps in that category. Another 67 used cloud platforms such as Firebase, Google Cloud Run, and AWS, while 60 communicated directly with AI providers.

“Over half of leaked Apps (55%) route LLM traffic through custom developer backends, making provider-side mitigations alone insufficient. Cloud platforms and direct API services account for comparable shares of leakage (23% and 21%, respectively), confirming that adopting a proxy architecture does not prevent credential exposure,” they added.

The issues were disclosed to the developers of all 282 vulnerable applications, and the apps were retested 90 days later.

“After responsible disclosure, 28% of vulnerable applications successfully remediated through credential revocation or access control enforcement. However, 23% remain exploitable due to either absence of remediation action (36 apps) or fundamentally flawed authentication implementations (30 apps),” they concluded.