


A China-linked cyber espionage operation targeted North American medical research institutions through compromised REDCap servers, using custom malware to gain persistent access and collect sensitive information, Google’s Threat Intelligence Group (GTIG) researchers found.
GTIG attributed the campaign to UNC6508, a threat actor linked to the People’s Republic of China that remained undetected in victim environments for more than a year. According to the researchers, the activity began in September 2023 and continued through at least November 2025.
REDCap is a web-based platform for building and managing online databases and surveys in compliance with regulations for medical and scientific research. The platform is widely used in the North American medical research community.
Google said it was unable to determine how UNC6508 initially gained access to the REDCap servers, though the group was observed probing vulnerable legacy versions of the platform on several target systems.
“Upon establishing a foothold on the REDCap server, UNC6508 performed internal reconnaissance and credential discovery to obtain database and service account credentials. The threat actor also deployed a web shell named ‘help.php’, which maintained persistence and functioned as an uploader in the REDCap application,” GTIG wrote.
Three months after the initial compromise, UNC6508 deployed a custom malware payload tracked as INFINITERED. The malware implemented its functionality through three distinct modular components by trojanizing legitimate REDCap system files.
The components consist of a dropper that intercepts REDCap software upgrades, a credential harvester that captures usernames and passwords entered into the application, and a backdoor that provides command-and-control functionality.
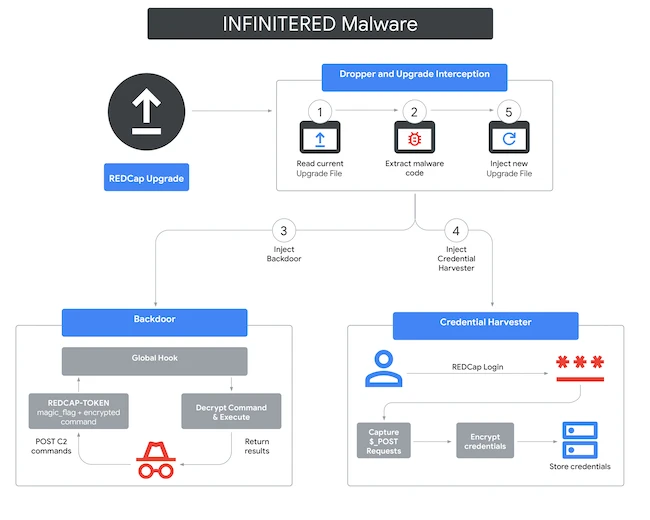
INFINITERED diagram (Source: Google)
The upgrade interception component monitors for REDCap upgrades and injects malicious code into future versions of REDCap.
The credential harvester captures usernames and passwords submitted through REDCap login pages and stores them in the REDCap sessions table for later retrieval.
The backdoor receives commands through HTTP cookies and allows UNC6508 to execute shell commands, upload and download files, run arbitrary SQL queries, retrieve stolen credentials, delete harvested credential records, and collect system and database information.
More than a year after the initial compromise, UNC6508 used harvested credentials to access an administrator account. The threat actor subsequently created a content compliance rule named “Patroit” that monitored emails for selected keywords and forwarded matching messages to an attacker-controlled Gmail account.
“The patterns used in the ‘Patroit’ compliance rule suggest strategic intelligence collection targeting geo-strategic policy, military strategy, advanced technology, and medical research,” the analysts noted.
“The patterns also include professional email addresses and phone numbers for members of organizations in these spaces. Several of the terms applied have spelling errors, suggesting the list was manually maintained.”
The findings suggest UNC6508 may have been pursuing a broader set of targets than the medical research organizations identified during the investigation. GTIG said the group’s intelligence collection priorities align with the strategic interests of the People’s Republic of China.
Google identified multiple organizations in the United States and Canada compromised with INFINITERED, notified affected organizations of the intrusions, and offered assistance with remediation. The researchers stated that malicious infrastructure associated with UNC6508 was disrupted.
REDCap administrators are advised to upgrade to the latest available version of the platform and remove legacy versions to reduce exposure to known vulnerabilities.
Google also recommends that users and customers follow security best practices for third-party identity providers (IdPs) and ensure 2-step verification (2SV) is enabled on all accounts.
YARA rules and indicators of compromise (IoCs) published with the report can help organizations scan their environments for signs of INFINITERED malware.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。