








Cybercrime is taking a larger share of criminal activity in Asia and the Pacific. More than half of surveyed jurisdictions reported that cybercrime accounts for over 30% of all crimes recorded nationally, according to INTERPOL’s 2025/2026 Asia and South Pacific Cyberthreat Assessment Report.
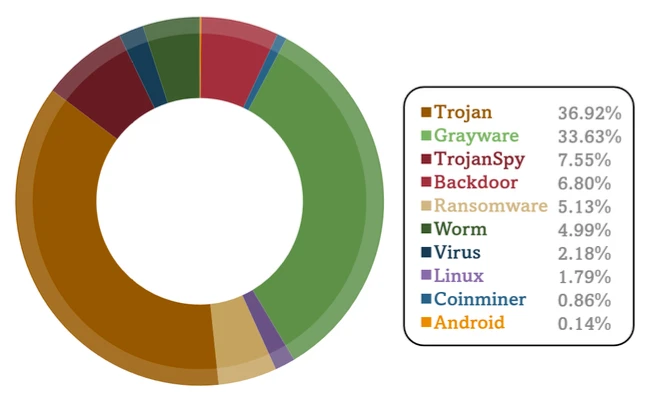
Distribution of malware types detected within the Asia and South Pacific region in 2024 (Source: INTERPOL)
Rapid digital adoption has expanded the region’s digital footprint and increased exposure to cyber threats. Criminal groups target businesses, governments, and individuals through online fraud, ransomware, phishing campaigns, and credential theft.
“The Asia and South Pacific region is home to some of the world’s fastest-growing digital economies – and, increasingly, some of its most determined cybercriminals. Rapid connectivity has unlocked immense opportunity, but uneven cybersecurity maturity across the region continues to create openings that transnational actors are quick to exploit,” said Neal Jetton, Director, Cybercrime Executive Directorate Investigation Support at INTERPOL.
One of the most significant developments is the industrialization of online scam operations. Transnational organized crime groups have established scam compounds in several countries, including Cambodia, Lao PDR, Myanmar, and the Philippines. These operations generate close to $40 billion annually through investment fraud, romance scams, and other forms of online deception. In some cases, authorities have linked them to human trafficking and forced labor.
Cybercrime has evolved into a large-scale cross-border enterprise. Criminal networks rely on dedicated infrastructure, online platforms, and international operations to support their activities. With victims spread across multiple countries, investigations have become more complex and depend on international law enforcement cooperation.
More than 135,000 ransomware-related attacks were recorded in the region during 2024. These attacks increasingly target critical infrastructure, healthcare organizations, large enterprises, and sectors including real estate, manufacturing, and financial services. One incident involving Indonesia’s National Data Centre disrupted more than 280 public services, including immigration and airport operations, illustrating the operational impact ransomware can have on government infrastructure.
Phishing remains one of the most common methods used to gain access to systems and steal credentials. Attackers use social engineering techniques to exploit trust and persuade victims to disclose sensitive information. These campaigns often serve as the entry point for financial fraud, account compromise, and malware deployment.
Credential theft remains a major component of the regional threat landscape. Information-stealing malware is used to collect usernames, passwords, financial information, and other sensitive data. Stolen credentials frequently facilitate fraud, account compromise, and ransomware attacks. Survey respondents ranked banking trojans and information-stealing malware among the most prevalent cybercrime categories affecting the region.
Threat actors use AI tools to enhance phishing campaigns, create convincing fake content, and automate parts of their operations. Deepfake technology has attracted particular attention. Discussions related to deepfakes on cybercriminal forums and messaging channels used by Southeast Asian threat actors increased by 600% during the first half of 2024. The technology has been used in fraud schemes involving the impersonation of executives and other trusted individuals.
Survey respondents ranked misinformation, manipulation, and deepfake-related crimes as the fourth most pressing cybercrime concern in the region. The ability to create realistic synthetic media makes it more difficult for organizations and law enforcement agencies to verify identities and distinguish legitimate communications from fraudulent ones.
One widely reported case involved an employee at a multinational firm in Hong Kong who transferred $25 million after participating in a video call featuring deepfake impersonations of company executives.
DDoS attacks and data breaches remain persistent threats. Government institutions, financial organizations, and businesses continue to experience attacks designed to disrupt services or gain unauthorized access to sensitive information. System intrusions accounted for approximately 80% of data breaches reported in the region during 2024, showing the prevalence of unauthorized access in cyber incidents.
The impact of these threats varies by country. More digitally advanced economies generally have stronger cybersecurity capabilities and greater access to security resources. Smaller island states and developing economies often have limited cybersecurity resources, expertise, and technical capacity. This can make them attractive targets for cybercriminals and create conditions that reduce the likelihood of detection or prosecution.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。