










Wireless security training programs lean heavily on generic network labs, with Wi-Fi appearing as a checkbox alongside Bluetooth, Zigbee, and cellular. Hands-on environments dedicated to IEEE 802.11 are uncommon, even as Wi-Fi remains the default on-ramp to corporate networks and a recurring entry point for attackers. A new paper from researchers at the Norwegian University of Science and Technology and the University of the Aegean takes aim at that gap with a cyber range built specifically for Wi-Fi.
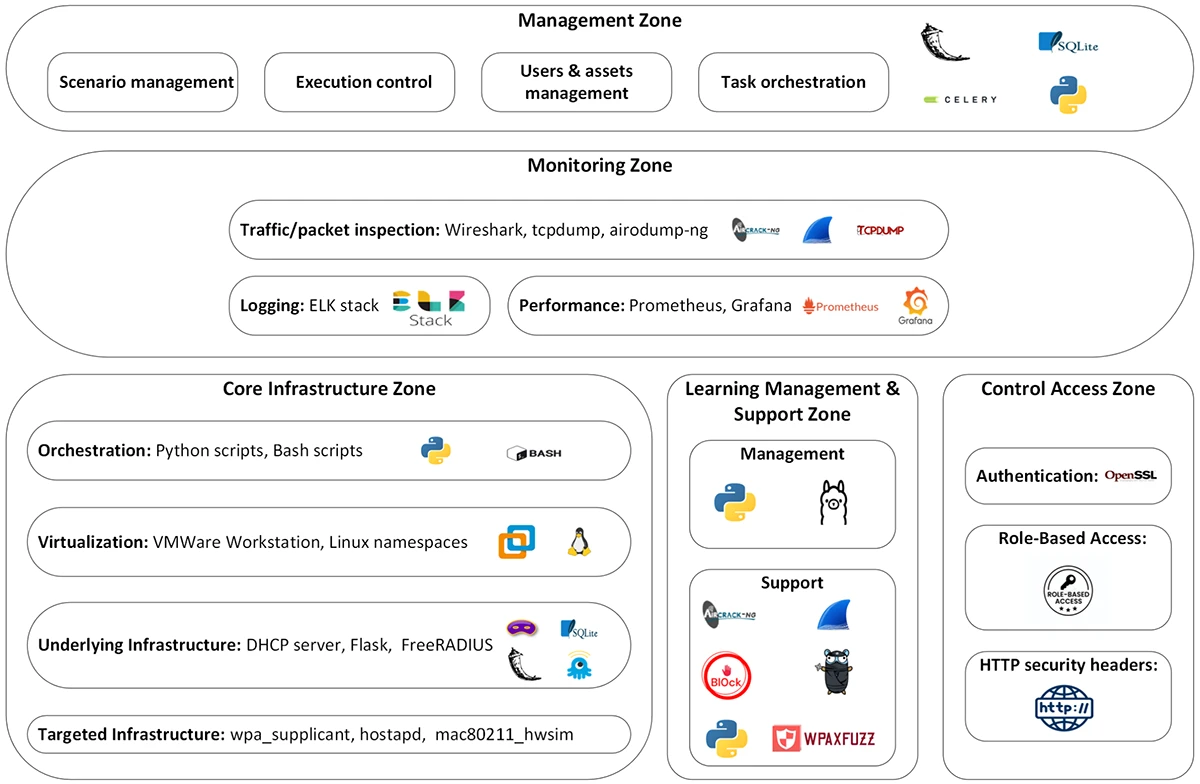
Structural view of the proposed Wi-Fi CR (Source: Research paper)
Rogue access points, deauthentication attacks, handshake weaknesses in WPA2 and WPA3, and protocol-level flaws in 802.11 frame handling each require setups that generic wireless labs rarely reproduce. The researchers point out that most existing cyber ranges and testbeds combine many wireless technologies under one roof, leaving 802.11-specific scenarios underserved. Their review of the field finds no platform purpose-built around Wi-Fi security.
The educational side has a similar problem. Wireless security teaching still leans on lectures and seminars, with limited access to scenario-driven environments where learners can practice against realistic 802.11 conditions.
The proposed cyber range emulates Wi-Fi networks in software using mac80211_hwsim, a Linux kernel module for simulated 802.11 radios. Linux namespaces isolate each emulated access point and client, so a single virtual host can run multiple wireless nodes that behave as separate devices. Standard user-space services do the rest: hostapd runs the access points, wpa_supplicant runs the clients, dnsmasq handles DHCP, and FreeRADIUS provides 802.1X/EAP authentication when a scenario calls for enterprise-grade setups.
On top of that emulated network, the platform bundles offensive and analysis tools learners would reach for in real engagements. Aircrack-ng covers wireless discovery and deauthentication testing. Wireshark, tcpdump, and tshark handle packet inspection. Two specialized tools developed by the same research group, WPAxFuzz and Bl0ck, extend the kit into WPA implementation fuzzing and block-acknowledgment-frame attacks against 802.11 connections.
The architecture itself is organized into five zones covering infrastructure, learning management, monitoring, administration, and access control. The zoning is conventional cyber range design, applied here to a Wi-Fi-specific workload.
One of the more interesting design choices sits in the scenario authoring workflow. Instructors can define exercises through a web interface in two ways. They can pick from prebuilt topology templates, or they can describe what they want in plain language and hand it to a locally hosted Llama model, which converts the description into a structured scenario definition that the platform can deploy. Scenarios are stored as a bundle of configuration files, shell scripts, and a topology manifest, then instantiated on demand.
The semi-automated path matters for a teaching tool. Writing a multi-AP, 802.1X-enabled scenario by hand is tedious, and that tedium is often what keeps instructors from running varied exercises week to week.
The full architecture is conceptual. A working prototype covering scenario creation, storage, retrieval, and deployment is available on GitHub. The remaining zones, including monitoring dashboards, role-based access enforcement, and asynchronous task orchestration, are specified in the design and earmarked for later implementation.
The researchers are upfront about the limits. Software emulation does not reproduce radio interference, propagation effects, or hardware quirks that show up in real deployments. The platform has not been tested at scale with many concurrent learners. Learning outcomes have not been measured. Cellular, Bluetooth, and other wireless technologies sit outside its scope by design.
“We anticipate that, when we have a full-fledged prototype developed, the platform can be utilized for further educational purposes (e.g., university lab exercises, education platforms like Udemy, and so on). At the same time, its modular design will also allow corporate training teams to utilize it on personnel with minimal adjustment and fine-tuning,” Vyron Kampourakis, co-author of the research, told Help Net Security.
Wi-Fi sits at the edge of nearly every corporate network, and the attack surface keeps growing as Wi-Fi 6 and Wi-Fi 7 roll out. A reproducible, software-only environment for practicing 802.11 attacks and defenses lowers the cost of building wireless security skills. The open-source release gives instructors and self-taught practitioners somewhere to start, with room for the platform to grow into the full design the paper lays out.

Download: Automating Pentest Delivery Guide
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。