






A cryptocurrency-stealing malware campaign used inflated GitHub activity, software reviews, YouTube tutorials and favorable VirusTotal comments to make malicious trading and gambling tools appear trustworthy, Check Point researchers found.
According to the researchers, the attackers packaged the malware as tools designed to help users make money. The offerings included cryptocurrency sniper bots and gambling “predictors” that claimed to identify winning opportunities before other traders or forecast the outcome of online betting games.
Instead of quick profits, the tools delivered Rust-based clipboard hijackers, or clippers, built for Windows and macOS that monitor the clipboard for cryptocurrency wallet addresses and replace them with attacker-controlled addresses from a large internal list.
The internal list contained more than 15,500 cryptocurrency wallet addresses spanning Bitcoin, Ethereum, Monero, Dogecoin, Cardano, Litecoin and other digital currencies.
“The attacker’s wallets appear to be replaced quite frequently. In many cases, it seems that once a malicious transaction is completed, the attacker swaps the used wallet for a new, ‘clean’ one,” the researchers wrote.
What distinguishes the operation is the effort invested in making it appear legitimate. A WordPress phishing site served as the campaign’s front door, while GitHub and SourceForge repositories hosted the downloads and displayed signs of popularity, including stars, forks, ratings and download counts.
The same tools were promoted through a YouTube channel featuring AI-generated narration, and some malware samples received favorable votes and comments describing them as safe on VirusTotal.
“From a user’s perspective, the ability to manipulate sentiment and reputation on platforms like VirusTotal marks an important evolution in how threat actors shape trust,” they added.
A key part of the operation involved “Ghost Networks”, coordinated accounts used to boost stars, reviews, downloads and other signs of popularity around the malicious tools.
“The actor appears to operate at least six GitHub accounts to promote and distribute his malicious software. These accounts also seem to collaborate with each other, as they are sometimes listed as contributors to one another’s repositories,” the researchers found.
GitHub repositories linked to the campaign recorded more than 5,000 downloads, including over 1,250 downloads of the macOS version of Aviator Predictor, software that claims to predict the outcome of the popular Aviator multiplier game, suggesting the campaign affected Mac users as well.
The tools were also distributed through the phishing site and SourceForge. On SourceForge, the report describes coordinated positive reviews and download figures that appeared heavily inflated, with more than 44,000 downloads recorded, most of them originating from Pakistan and India.
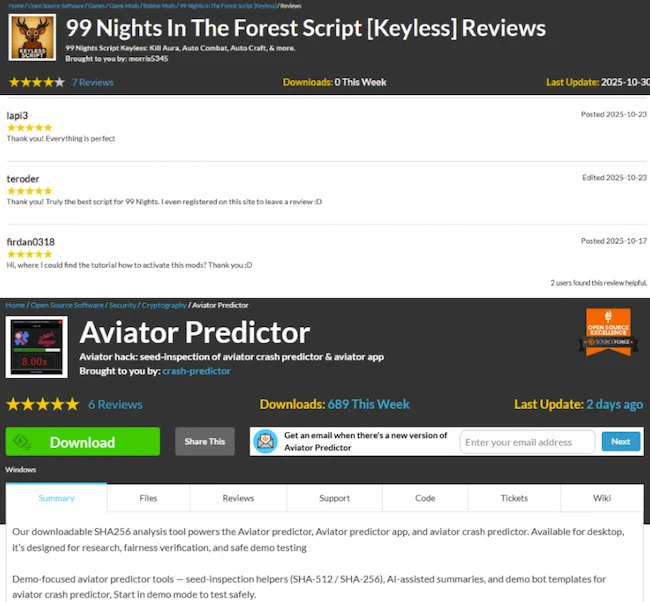
Positive engagement on SourceForge (Source: Check Point)
Of the more than 44,000 recorded downloads, about 37,460 appeared to originate from Android devices, even though the promoted software was available only for Windows and macOS.
The researchers said a possible explanation is the use of an Android device farm to inflate the download figures.
The attackers also promoted the tools through a YouTube channel with more than 91,000 subscribers. The videos were presented as personal tutorials, showing a desktop screen with visible mouse movements as the software was demonstrated. An AI-generated narrator appeared in the corner of the screen, guiding viewers through the process step by step.
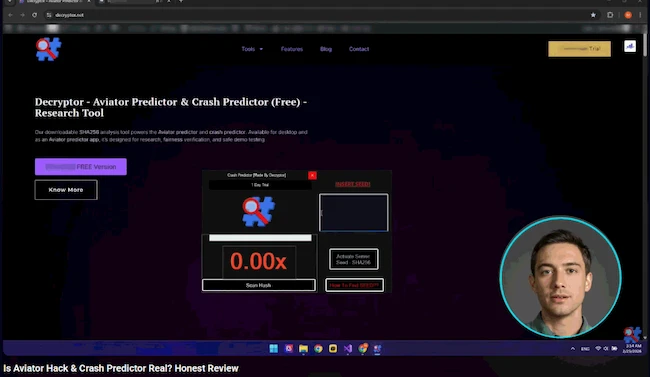
AI-generated narrator (Source: Check Point)
“This combination of on-screen activity and synthetic presenter is likely used to build trust and make the demonstration appear more authentic and convincing to potential victims.”
Posts promoting the tool appeared on several news websites on April 27, 2026, suggesting a coordinated effort to push the malicious software within a short period of time. Most of the articles have since been removed, leaving only traces in search results.
“Even if this campaign is not primarily aimed at large enterprises, it shows that attackers no longer rely only on classic malware distribution techniques to reach victims. Instead, they can manipulate reputation systems, crowd‑sourced feedback, and cross‑platform promotion to lower suspicion and attract more users,” they concluded.
Check Point has published indicators of compromise (IOCs) associated with the campaign to help defenders identify related activity.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。