

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

WordPress大学
WordPress大学
Jina AI
Jina AI
小众软件
小众软件
GbyAI
GbyAI
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
博客园 - 【当耐特】
D
DataBreaches.Net
腾讯CDC
V
Visual Studio Blog
博客园 - 叶小钗
B
Blog
Apple Machine Learning Research
T
The Blog of Author Tim Ferriss
S
SegmentFault 最新的问题
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
V
V2EX
博客园 - 三生石上(FineUI控件)
云风的 BLOG
云风的 BLOG
The Cloudflare Blog
MongoDB | Blog
MongoDB | Blog
有赞技术团队
有赞技术团队
U
Unit 42
博客园 - 司徒正美
博客园 - 聂微东

Help Net Security

Police arrest 10 suspected members of Black Axe cybercrime gang ShinyHunters claims it stole 1.4 million records from Udemy Sevii unveils Cyber Swarm Defense Mode to stop AI-driven attacks at scale Alleged Chinese hacker extradited to US over cyberattacks targeting COVID-19 research Cequence Agent Personas bring granular control and governance to enterprise AI agents NowSecure MARI gives enterprises evidence-based visibility into third-party mobile app risk The metrics killing your SOC, and what to use instead US state privacy fines reached $3.425 billion in 2025 Canada’s first SMS blaster case leads to three arrests Linux storage management tool Stratis 3.9.0 adds online encryption and cache-less pool startup TLS Connect gives SMBs a right-sized automated tool to manage TLS certificates Aptori expands its platform with autonomous offensive testing to reduce security bottlenecks Your IAM was built for humans, AI agents don’t care The AI criminal mastermind is already hiring on gig platforms 25 open-source cybersecurity tools that don’t care about your budget Product showcase: LuLu reveals unauthorized outbound connections from Mac apps Week in review: Claude Mythos finds 271 Firefox flaws, Vercel breach Users advised to drop passwords and make room for passkeys - Help Net Security Indirect prompt injection is taking hold in the wild - Help Net Security Compromised everyday devices power Chinese cyber espionage operations - Help Net Security New Cisco firewall malware can only be killed by pulling the plug - Help Net Security Meta is overhauling how you sign in, manage settings, and protect your accounts - Help Net Security Ubuntu 26.04 LTS delivers memory-safe system tools and live patching for Arm servers - Help Net Security OpenAI’s GPT-5.5 is out with expanded cybersecurity safeguards - Help Net Security AI is speeding up nation-state cyber programs - Help Net Security A study of 1,000 Android apps finds a privacy policy logging gap - Help Net Security IT spending to hit $6.31 trillion record, thanks to AI - Help Net Security Where AI in CI/CD is working for engineering teams - Help Net Security With AI's help, North Korean hackers stumbled into a near-undetectable attack - Help Net Security Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security
Tigera introduces unified control plane for Kubernetes-ba...
Industry News · 2026-06-17 · via Help Net Security

Tigera has announced the general availability of Tigera Lynx, a unified control plane for Kubernetes-native AI agents. Lynx gives enterprises a single place to find every agent in their Kubernetes estate, tighten security posture, assign sandboxes, provide each agent with a cryptographic identity, enforce policy on every action it takes, audit agent activity, and detect anomalous behavior, all without changing a line of agent code.
Tigera Lynx

AI agents do not behave like the workloads enterprise security stacks were built to manage. They are autonomous and non-deterministic: acting on behalf of users, accessing tools, LLMs, and other agents, operating through delegation chains, and consuming untrusted input. As a result, three teams often view the same challenge from different perspectives. AI teams want to experiment with new technologies and move quickly.

Platform engineering teams are measured on deployment velocity but cannot easily prove the platform is under control. Security teams are asked to approve agents without being able to confidently assess their security posture. A valid credential does not guarantee safe behavior, and the blast radius can change every time a new agent, tool, or platform update is introduced.

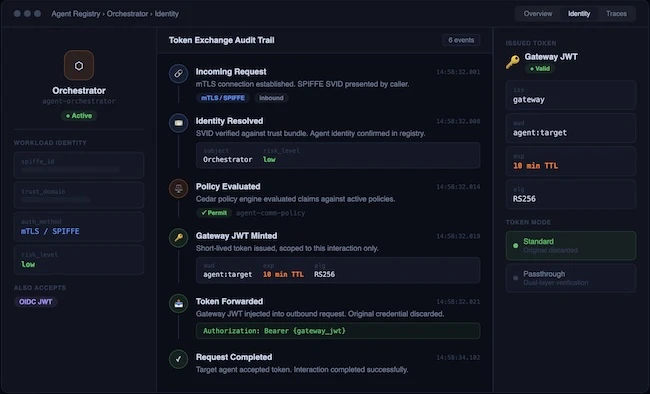
Lynx sits in the path of every agent call, agent-to-agent, agent-to-tool, and agent-to-LLM, to authenticate, authorize, mediate, and audit each one. It plugs into the tools enterprises already run, including their identity provider (EntraID, Okta) or via SPIFFE/SPIRE, and existing observability systems, and is built on open standards rather than proprietary lock-in.

One control plane, five capabilities

  • Discovery, registration, and observability. A central registry catalogs every agent with its owner, purpose, and version, while eBPF-powered auto-discovery finds agents nobody registered. Shadow agents are flagged and quarantined, and any agent’s actions can be reconstructed end-to-end through OpenTelemetry traces.
  • Configuration and posture management. AI-CSPM continuously evaluates every agent against a baseline, surfacing drift and over-permissions the moment they happen, with per-agent sandboxing and pre-built compliance packs mapping to GDPR, HIPAA, SOC 2, and financial services requirements. A Red Team Agent continuously probes for weaknesses in posture and misconfigurations.
  • Identity and authentication. Every agent gets a verifiable cryptographic identity through integration into an enterprise’s identity provider (EntraID, Okta) or through SPIFFE/SPIRE, with no shared secrets. Long-lived API keys are replaced by short-lived and tightly scoped, auto-rotated tokens. A JWT token is minted for every hop in a multi-agent workflow.
  • Policy definition and enforcement. A single default-deny policy governs LLM, MCP, and agent access using the Cedar policy language, enforced at the gateway before any call executes — with no agent code changes. Misbehaving agents can be quarantined instantly and high-stakes calls routed to a human.
  • Anomalous behavior detection. eBPF and LSM watch every syscall, network call, and file access at a layer agents can’t tamper with, catching credential theft and lateral movement even when an action passes policy. This provides a forensic audit trail. Guardian Agent detects anomalous behavior and quarantines suspicious agents.

“For over a decade, Tigera’s Calico platform has served Global 2000 companies running the largest Kubernetes platforms in the world, securing tens of millions of mission-critical transactions every day. AI agents are the next class of workloads: autonomous, distributed, and increasingly embedded in critical business processes. Lynx brings that same unified control and security rigor to AI agents. We’re building on our core competency — securing mission-critical workloads at scale on Kubernetes, in a highly performant way,” said Ratan Tipirneni, CEO of Tigera.

“Control only matters if it’s enforced uniformly. Lynx gives every agent a cryptographic identity, scopes credentials to a single hop, and evaluates every LLM, MCP, and tool call against a default-deny policy at the gateway — with no agent code changes. Because we watch behavior with eBPF and LSM at the kernel, we can detect an agent going wrong even when it carries a valid credential, and produce a reproducible audit trail to prove it,” said Peter Kelly, Chief Technology Officer of Tigera.