


Ransomware, supply chain vulnerabilities, insider threats, compliance failures, and software disruptions remain major concerns for security leaders, according to The Ransomware Reality: Zero Days to Recover report by Absolute Security.
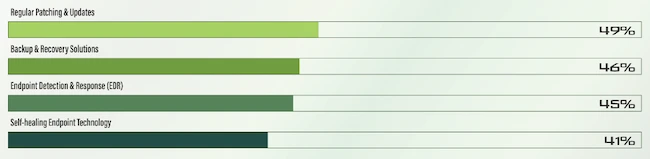
How CISOs currently ensure endpoint resilience against ransomware (overall, %) (Source: Absolute Security)
A survey of 750 CISOs from enterprise organizations with more than 5,000 employees in the United States and the United Kingdom revealed gaps between ransomware frequency, confidence in recovery capabilities, and remediation timelines.
Ransomware-as-a-service (RaaS) has evolved from a niche criminal capability into a model accessible to actors with limited technical expertise. Ransomware syndicates now provide malware, infrastructure, and negotiation services through operations structured like legitimate businesses.
“The window between initial compromise and full infection can now be as fast as only a few minutes, bringing consequences that include operational downtime, financial loss, reputational damage, regulatory exposure, and even personal liability for security leaders,” said Harold Rivas, CISO at Absolute Security.
Double and triple extortion have become standard practices, increasing pressure on firms to strengthen response capabilities. Restoring from backups alone cannot address ransomware attacks.
The weaponization of AI by threat actors has become a major development in the ransomware landscape. Attackers use AI to craft phishing campaigns, automate vulnerability discovery, accelerate lateral movement, and generate malware variants designed to bypass detection.
US security leaders reported higher levels of concern across all threat categories, especially ransomware. UK respondents showed higher rates of neutral responses.
The distributed endpoint estate has become the primary attack surface as enterprises continue to operate remote and hybrid work environments.
57% of leaders experienced an attack that originated from a mobile, remote, or hybrid endpoint device. Once ransomware enters through an endpoint, widespread disruption becomes difficult to contain without device-level resilience.
Across industries, they ranked operational downtime as their leading concern. Data breaches, reputational damage, financial loss, and regulatory penalties followed closely behind, showing the cumulative impact of ransomware incidents.
The impact of ransomware varies by sector. Regulatory penalties ranked highest in financial services, reputational damage in healthcare, and data breach concerns in professional services. No sector remained unaffected across all categories.
The survey revealed a gap between confidence and recovery outcomes. 83% of CISOs said they were confident their organization could recover from a ransomware attack. For US respondents, that figure reached 91%, compared with 69% in the UK.
Despite that confidence, 55% of CISOs experienced a ransomware attack or disruptive cyber incident that rendered endpoint devices inoperable. None recovered in less than a day, 57% required up to six days, and nearly 20% needed two weeks to recover.
When CISOs are expected to prevent every breach, organizations often prioritize prevention over recovery infrastructure. Board-level communication about ransomware is frequently distorted because security executives fear legal, professional, and personal consequences after an incident. This pressure can lead to underreporting, poor documentation of known gaps, and overstated readiness.
SEC disclosure rules in the US and GDPR reporting requirements in the UK are increasing pressure on security professionals. These regulations influence decisions about whether to pay attackers during a ransomware incident.
The 58% willingness for enterprise security leaders to consider ransom payments exceeds the broader market average. The figure reached 63% for US CISOs and 47% for UK respondents. For large organizations, extended downtime can cost millions, making payment appear to be the fastest option during a crisis.
“It’s not surprising to learn that despite regulatory pressure, security and risk leaders remain open to paying a ransom to recover their systems and protect data, especially when considering that prolonged downtime can lead to unsustainable losses,” said Christy Wyatt, President and CEO, Absolute Security.
Companies should focus on recovery infrastructure that reduces the need to pay ransoms. Companies with automated endpoint recovery can restore systems faster than those relying on manual reimaging or device replacement.
When ransomware renders endpoint devices inoperable, recovery speed depends on the organization’s ability to restore them. Physical device collection and repair remains the most common recovery method at 59% and one of the slowest. Remote repair capability followed at 53%, while 49% of organizations relied on replacement devices for end users.
In distributed work environments, recovering, reimaging, and returning thousands of devices creates significant logistical challenges. This helps explain the average recovery time of 4.96 days.
Endpoint recovery suffers from unclear ownership. Thirty-seven percent of companies said endpoint restoration falls to IT teams, 35% assigned responsibility to security teams, and 28% reported shared responsibility.
Training gaps remain a major challenge for security professionals. Phishing continues to be a common ransomware entry point, showing that employees remain a frequent target for attackers seeking initial access.
Many firms recognize the importance of patching, but older infrastructure makes updates difficult to deploy consistently, leaving exploitable gaps.
Ransomware attacks increasingly begin with exploited vulnerabilities, and attackers continue to reduce the time between vulnerability disclosure and exploitation.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。