








Noma has announced the launch of Noma Agent Access Control, which helps security teams discover, govern, and enforce access policies for AI agents and Model Context Protocol (MCP) servers throughout the enterprise.
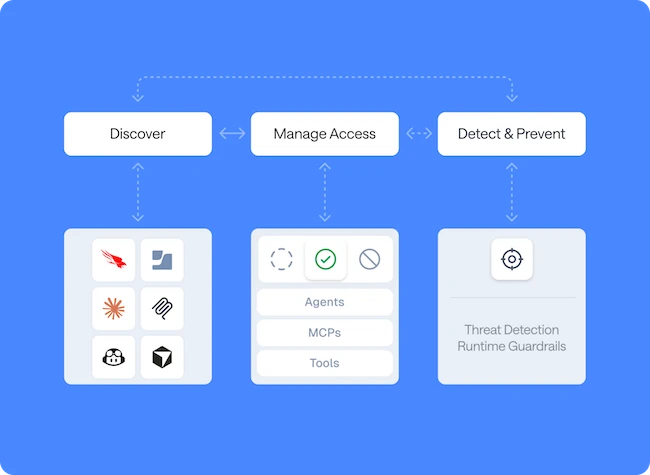
AI agents and MCP servers have proliferated across developer environments faster than existing governance frameworks were designed to handle. In less than 12 months, organizations have gone from experimenting with a handful of agents to running dozens, or even hundreds of them, each connecting to sensitive data and executing actions on behalf of users. Reining in this chaos requires tooling that can discover what’s running, establish identity, and enforce policy automatically.
“Knowing what each agent is authorized to do is the foundation,” said Niv Braun, CEO of Noma. “But agents are also influenced by everything they encounter at runtime: the prompts they receive, the tools they call, the data they retrieve. A single malicious input can redirect an agent’s behavior in ways no access policy anticipates, coercing it into misusing authorization it was legitimately granted. Complete governance means defining the rules and continuously verifying they hold. Noma Agent Access Control gives organizations the first layer. AI Detection and Response gives them the second.”
Security teams can’t govern what they can’t see. Noma Agent Access Control automatically builds a complete inventory of every agent and MCP server in an organization, controls what each one can access, and keeps that picture current from day one. This means there’s no need for weeks of manual work and there are no gaps.
Governing agents requires two layers: access control defines the boundaries, runtime enforcement verifies they hold.
Key capabilities include:
Enterprise Agentic Registry. Every agent, connected MCP server, and tool surfaces in a dynamic registry with context already attached: what each server exposes, which agents connect to it, and where it stands against current security policies. The registry updates continuously in real time.
Agent Identity. Noma Agent Access Control gives each autonomous agent a distinct, attributable identity when it connects to MCP servers and tools. Rather than operating under shared credentials or permissive service accounts, every agent’s actions trace back to a specific identity.
Flexible Governance Model. Security teams configure each agent and MCP connection in one of three states: Approved, Requires Review, or Blocked. Approved resources connect with zero friction. Items flagged for review surface in a queue with full risk context. Blocked resources are prevented from connecting automatically, without requiring manual intervention at each occurrence.
Tool-Level Control. Not every tool within the same MCP server carries equal risk. A single server might expose a safe read-only file tool alongside one that can delete records or send emails. Noma Agent Access Control lets security teams approve or block individual tools rather than entire systems, and apply those policies at the granularity of tool, agent type, user, team, or environment.
Defining what an agent is permitted to do creates the policy baseline. Enforcing it in practice requires more. Agents ingest input from external sources at runtime: user prompts, tool responses, data retrieved from connected systems. Any of those inputs can be manipulated. Prompt injection attacks, compromised tool responses, and combinations of risk factors can redirect an agent’s behavior mid-session, coercing it into actions its policy nominally allows but its actual task does not require.
The threat rarely appears in a single action. An agent that retrieves customer records in one step and sends a summary to an external address three steps later may have been technically authorized to do both. It is the full sequence of actions, seen together, that reveals the risk.
With Noma’s AI Detection and Response (AI-DR), organizations can monitor the complete behavioral chain of every agent session: prompts, tool calls, data access, and actions taken. It detects prompt injection, data exfiltration, and scope violations in real time. Because AI-DR shares context directly with Agent Access Control, the platform knows both what each agent is permitted to do and what it is actually doing. When those two layers operate together, detections sharpen and false positives drop.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。