


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Martin Fowler
Martin Fowler
大猫的无限游戏
大猫的无限游戏
J
Java Code Geeks
罗磊的独立博客
雷峰网
雷峰网
G
Google Developers Blog
Cyber Security Advisories - MS-ISAC
爱范儿
爱范儿
B
Blog RSS Feed
腾讯CDC
Apple Machine Learning Research
D
Docker
Recent Announcements
T
Tailwind CSS Blog
博客园 - 聂微东
让小产品的独立变现更简单 - ezindie.com
Vercel News
Vercel News
小众软件
小众软件
人人都是产品经理
人人都是产品经理
云风的 BLOG
云风的 BLOG
IT之家
IT之家
Blog — PlanetScale
Blog — PlanetScale
I
InfoQ
S
SegmentFault 最新的问题

Help Net Security

Police arrest 10 suspected members of Black Axe cybercrime gang ShinyHunters claims it stole 1.4 million records from Udemy Sevii unveils Cyber Swarm Defense Mode to stop AI-driven attacks at scale Alleged Chinese hacker extradited to US over cyberattacks targeting COVID-19 research Cequence Agent Personas bring granular control and governance to enterprise AI agents NowSecure MARI gives enterprises evidence-based visibility into third-party mobile app risk The metrics killing your SOC, and what to use instead US state privacy fines reached $3.425 billion in 2025 Canada’s first SMS blaster case leads to three arrests Linux storage management tool Stratis 3.9.0 adds online encryption and cache-less pool startup TLS Connect gives SMBs a right-sized automated tool to manage TLS certificates Aptori expands its platform with autonomous offensive testing to reduce security bottlenecks Your IAM was built for humans, AI agents don’t care The AI criminal mastermind is already hiring on gig platforms 25 open-source cybersecurity tools that don’t care about your budget Product showcase: LuLu reveals unauthorized outbound connections from Mac apps Week in review: Claude Mythos finds 271 Firefox flaws, Vercel breach Users advised to drop passwords and make room for passkeys - Help Net Security Indirect prompt injection is taking hold in the wild - Help Net Security Compromised everyday devices power Chinese cyber espionage operations - Help Net Security New Cisco firewall malware can only be killed by pulling the plug - Help Net Security Meta is overhauling how you sign in, manage settings, and protect your accounts - Help Net Security Ubuntu 26.04 LTS delivers memory-safe system tools and live patching for Arm servers - Help Net Security OpenAI’s GPT-5.5 is out with expanded cybersecurity safeguards - Help Net Security AI is speeding up nation-state cyber programs - Help Net Security A study of 1,000 Android apps finds a privacy policy logging gap - Help Net Security IT spending to hit $6.31 trillion record, thanks to AI - Help Net Security Where AI in CI/CD is working for engineering teams - Help Net Security With AI's help, North Korean hackers stumbled into a near-undetectable attack - Help Net Security Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security
depthfirst adds pre-install protection against malicious ...
Industry News · 2026-06-01 · via Help Net Security

depthfirst has introduced Dependency Firewall, a product that reviews every open-source package being downloaded anywhere in a company and blocks the malicious ones before they reach the person or system that requested them. Developers, AI agents, and any employee using Claude, Codex, or other AI tools keep installing exactly as they do today, and nothing dangerous makes it through. Security teams can ensure that AI is rolled out safely across the company.
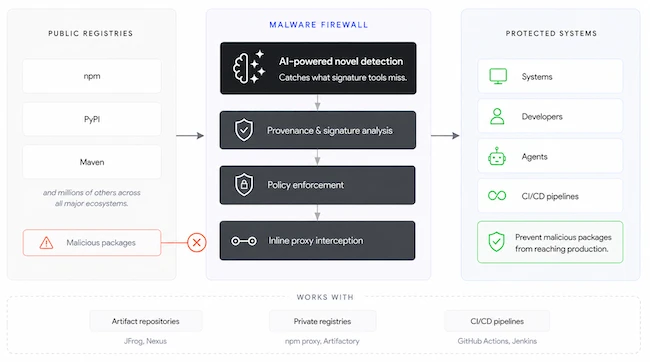
depthfirst Dependency Firewall

Modern software runs on open source, and attackers exploit that trust by publishing packages that mimic popular libraries and hide malicious code inside install scripts. The breach can happen on a first install, even before production: malicious scripts can execute the moment a package is pulled down, so a single developer machine or coding agent installing a malicious dependency can leak credentials, plant a backdoor, or exfiltrate source code before anything has been reviewed, built, or deployed.

Verizon reported that 48% of data breaches analyzed in its 2026 DBIR involved ransomware. And malware attacks have surged in recent months. They cost almost nothing to launch, and the people pulling in dependencies now include business users running AI assistants and autonomous coding agents, not only security-conscious engineers.

Dependency Firewall inspects every package being downloaded in a company, regardless of who is installing it, and returns a verdict before it is installed. Approved packages pass through with negligible latency, packages that warrant review are quarantined, and anything malicious is blocked with the supporting evidence attached. Engineers use the same install commands, CI pipelines run unchanged, and AI agents keep operating normally.

Because Dependency Firewall analyzes packages the moment they are published rather than at install time, every package has already been assessed by the time anyone requests it. The analysis runs on depthfirst’s agentic defense platform, the same system that discovered NGINX Rift, a critical 18-year-old vulnerability affecting a significant portion of global web traffic. For every new package version, it:

  • Runs proprietary analysis on code and install scripts
  • Performs runtime analysis to detect malicious package behavior
  • Reasons about package intent and investigates unknown behavior
  • Flags publisher and maintainer anomalies
  • Maps dependency and transitive risk
  • Checks against public and private threat and data feeds

Every verdict ships with the evidence behind it, so any decision can be audited back to the underlying signals. Beyond blocking what is clearly malicious, Dependency Firewall gives teams a programmable enforcement layer: requiring a minimum package age, restricting acceptable dependency trees, enforcing license policies across direct and transitive dependencies, and quarantining packages pending manual review. Verdicts route into the tools teams already use, and when the firewall calls something wrong, a team can override the decision in seconds, with every override logged automatically.

“We recently had an incident where an internal vibecoded app inadvertently pulled in a malicious package that put our company at risk. depthfirst’s Dependency Firewall is a game changer as it enables us to safely leverage AI across the company,” said a CISO at a Fortune 100 company.