


The normalization of AI and automation within internet infrastructure is changing how organizations interpret traffic. Activity that once appeared anomalous is now treated as expected behavior. AI agents have emerged as a third category of automated traffic alongside good and bad bots, according to the Thales 2026 Bad Bot Report: Bad Bots in the Agentic Age.
The distinction between legitimate and malicious automation is difficult to define because both operate through similar channels, workflows, and infrastructure.
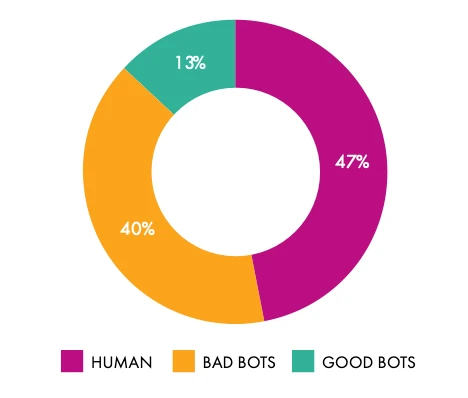
Bad bot vs good bot vs human traffic in 2025 (Source: Thales)
Human traffic continues to decline as a share of overall activity. Automated traffic accounted for 53% of all observed internet traffic in 2025, with bad bots making up 40% and benign automation accounting for 13%.
General automation remains the most common attack type, accounting for 29% of activity. This includes brute-force attacks, vulnerability scanning, credential testing, and large-scale data scraping.
Business logic abuse and API violations also represent a significant share of attacks. These methods rely on manipulating legitimate application workflows or exploiting weaknesses in API design and authorization.
AI is increasing the effectiveness of these attacks. Bots now mutate fingerprints, adjust interaction timing, and adapt to mitigation controls. This enables persistent probing of applications until a viable path is identified. High-volume, low-complexity attacks create continuous background pressure, while more advanced bots target specific workflows.
“AI is transforming automation from something organizations try to block into something they must also manage,” said Tim Chang, Global VP and GM, Application Security at Thales. “The challenge is no longer identifying bots. It’s understanding what the bot, agent, or automation is doing, whether it aligns with business intent, and how it interacts with critical systems.”
The United States remains the most targeted country, accounting for 59% of bot attacks, followed by Australia, United Kingdom, and France.
AI-driven bot activity increased more than tenfold (12.5×) in 2025, with daily blocked requests rising from 2 million to 25 million.
AI agents retrieve data and perform tasks on behalf of users, operating through browsers, search platforms, and enterprise tools. Their behavior aligns with normal application usage, which makes them difficult to distinguish from legitimate traffic.
Current visibility is limited to detectable or declared AI clients, leaving a large portion of AI-driven automation unverified. This creates a gap between observed activity and the full scale of AI-enabled risk.
Attackers are also deploying self-hosted or modified LLMs that do not identify themselves as AI agents. These systems can be fine-tuned for malicious use, further reducing visibility.
A portion of AI-driven traffic already overlaps with malicious patterns. More than 10% of AI fetcher sessions and nearly 9% of AI crawler sessions trigger bad bot detection rules. Many of these sessions are blocked through customer-defined policies, reflecting decisions about which AI tools are allowed to access applications.
Access controls depend on application sensitivity. Public content may remain accessible, while authentication, transactional, and data-intensive endpoints are more tightly restricted.
The rise of AI agents is driving new operational models, including verification and monetization of AI-generated traffic.
Verified AI bots use cryptographically signed headers, allowing organizations to authenticate and measure AI-driven access. This enables differentiation between approved AI agents and unverified automation and supports control over how these agents interact with applications and APIs.
Growing adoption is expected to drive the implementation of enforceable access models. AI traffic may be governed through policy, rate limiting, or commercial agreements, turning it into a managed and potentially billable channel.
APIs continue to be a primary target, with 27% of bot attacks directed at API endpoints. As organizations rely more on APIs to power digital services, they have become a critical point of exposure.
The most common API threats include data leakage, business logic abuse, and remote code execution or file inclusion attacks. These attacks often rely on valid, well-formed requests executed at scale.
AI-driven tools are accelerating API interactions, increasing request volume and complexity. This trend is raising concerns among developers and security teams.
To evade detection, bots frequently disguise themselves as legitimate browsers. Google Chrome remains the most commonly impersonated browser, followed by Android Browser. This shows how mobile traffic is used to mask automated activity.
Financial services was the most targeted industry in 2025, accounting for 24% of all bot attacks. Bots increasingly interact directly with APIs, identity systems, and workflows that support customer transactions and digital banking operations.
While financial services leads in overall attack volume, telecoms, society (non-profit organizations), computing and IT, travel, and business sectors show the highest proportion of bad bot traffic. This reflects the extent to which automated threats are embedded across digital environments.

Webinar: The True State of Security 2026
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。