A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.
Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press.
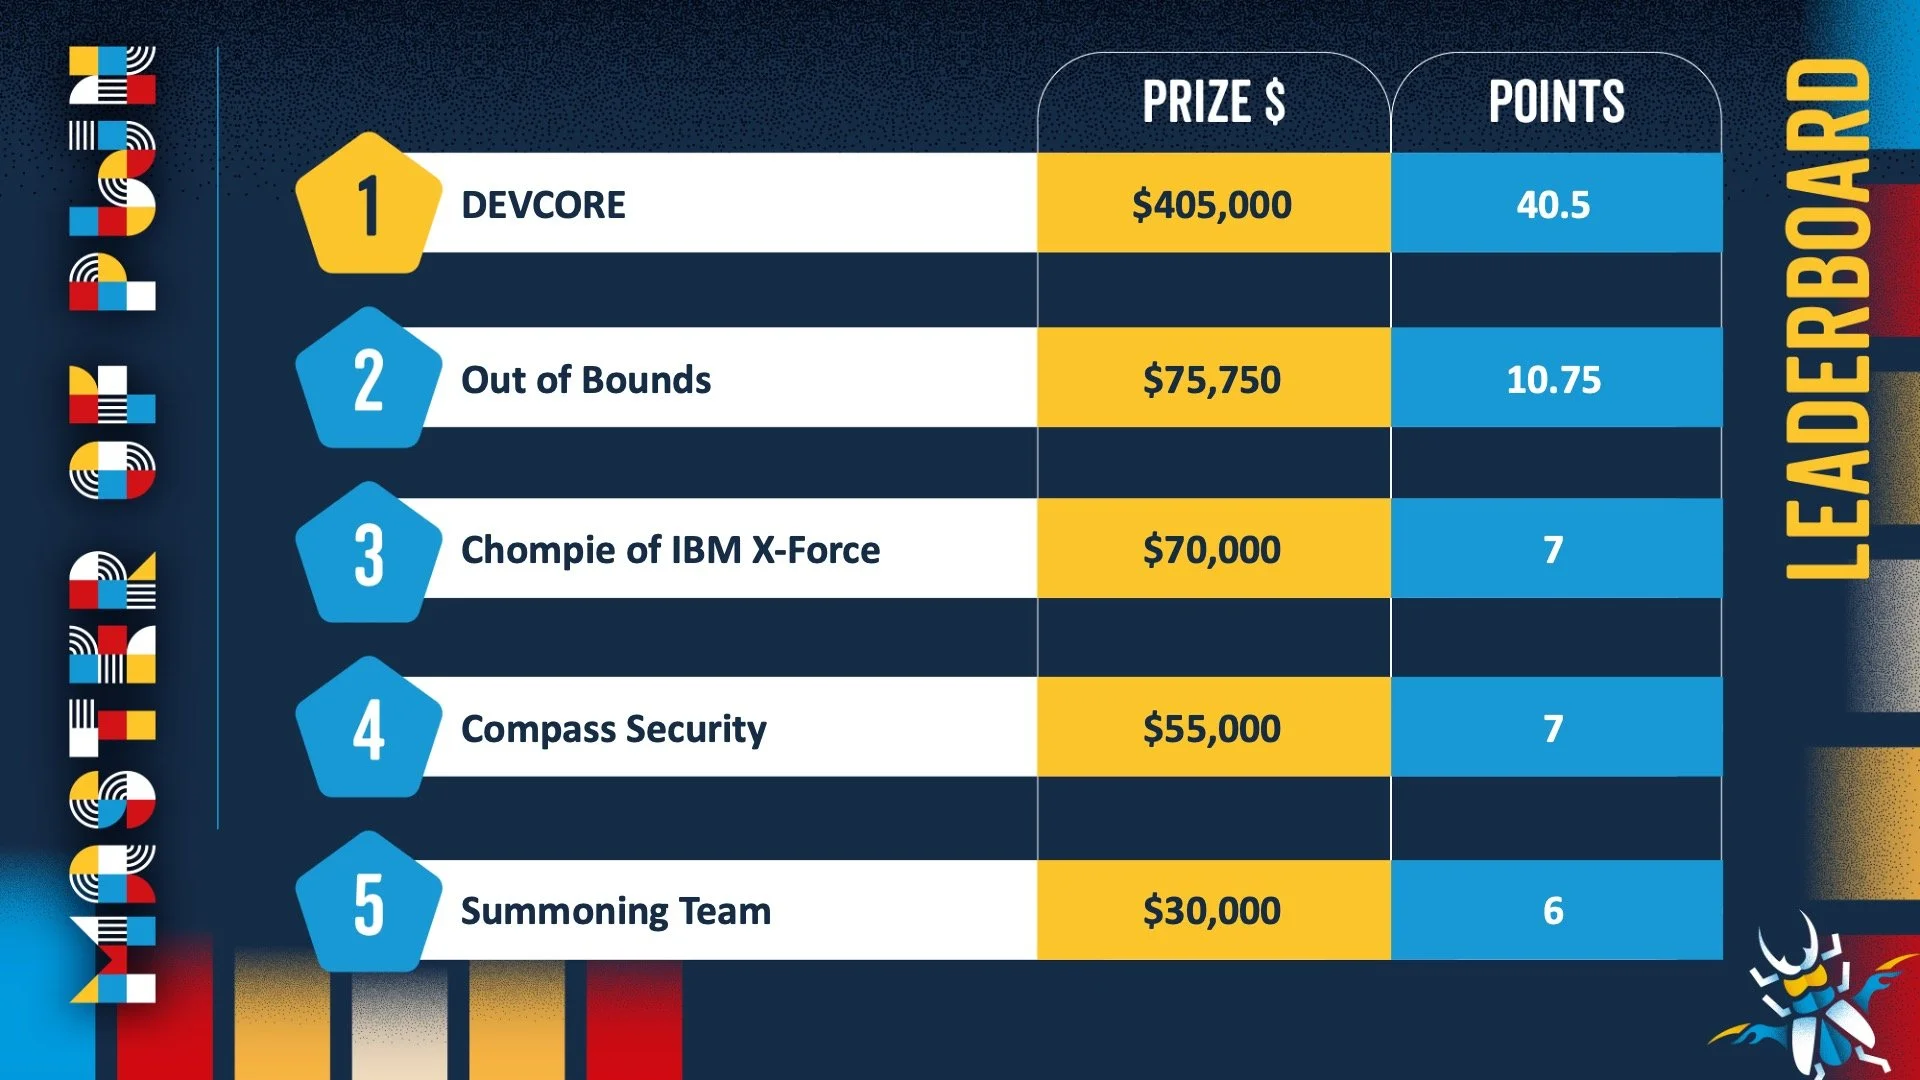
Attackers exploit Funnel Builder bug to inject e-skimmers into e-stores Pwn2Own Berlin 2026, Day Three: DEVCORE Crowned Master of Pwn, $1.298 Million Total U.S. CISA adds a flaw in Microsoft Exchange Server to its Known Exploited Vulnerabilities catalog Russian APT Turla builds long-term access tool with Kazuar Botnet evolution OpenAI hit by supply chain attack linked to malicious TanStack packages Pwn2Own Berlin 2026, Day Two: $385,750 more, Microsoft Exchange falls, and the running total crosses $900K CVE-2026-42897: Microsoft confirms active exploitation of Exchange Server zero-day Ghostwriter group resumes attacks on Ukrainian Government targets Researchers uncover YellowKey and GreenPlasma Windows Zero-Days Pwn2Own Berlin 2026, Day One: $523,000 paid out, AI products fall U.S. CISA adds a flaw in Cisco Catalyst SD-WAN to its Known Exploited Vulnerabilities catalog Linux Kernel bug Fragnesia allows local root access attacks Broadcom releases VMware Fusion security update for root access bug NGINX Rift: an 18-year-old flaw in the world’s most deployed web server just came to light FamousSparrow targets Azerbaijani energy sector in multi-wave espionage campaign Nitrogen Ransomware claims massive data theft from Foxconn Microsoft Patch Tuesday for May 2026 fix 138 bugs, some of them are alarming OpenLoop Health confirms January 2026 Data breach affecting 716,000 Quest KACE SMA flaw CVE-2025-32975: when one unpatched tool opens the door to 60 organizations Instructure settles with hackers following massive student data theft Critical Fortinet vulnerabilities fixed in FortiSandbox and FortiAuthenticator Hackers accessed BWH Hotels reservation system for months The world’s most “Dangerous” AI, Anthropic’s Mythos, found only one flaw in curl Attackers exploit cPanel CVE-2026-41940 to deploy Filemanager Backdoor WannaCry, the ransomware attack that changed the history of cybersecurity Android banking Trojan TrickMo evolves using TON network for C2 Identity security firm SailPoint discloses GitHub repository breach Google warns artificial intelligence is accelerating cyberattacks and zero-day exploits Crimenetwork returns after takedown, dismantled again by German authorities U.S. CISA adds a flaw in BerriAI LiteLLM to its Known Exploited Vulnerabilities catalog Instagram removed end-to-end encryption for DMs. What should users do? New cPanel vulnerabilities could allow file access and remote code execution Official JDownloader site served malware to Windows and Linux users between May 6 and May 7
International Press – Newsletter
Cybercrime
Healthcare Data Breach: Cybercriminals Attacked Health Insurance Agency in Ecuador
German operator of “Crimenetwork” arrested in Spain New version of the criminal trading platform “Crimenetwork” shut down – law enforcement authorities secure
Foxconn confirms cyberattack impacting North American factories
Cops arrest man suspected of being Dream Market kingpin
TeamPCP’s Mini Shai-Hulud Is Back: A Self-Spreading Supply Chain Attack Compromises TanStack npm Packages
Our response to the TanStack npm supply chain attack
Malware
JDownloader site hacked to replace installers with Python RAT malware
New TrickMo Variant: Device Take Over malware targeting Banking, Fintech, Wallet & Auth apps
Threat Actor Mr_Rot13 Actively Exploits CVE-2026-41940 for Backdoor Deployment
This is what some the world’s largest banks of malware look like stacked as hard drives
Popular node-ipc npm Package Infected with Credential Stealer
Hacking
AI Vulnerability Research and the Fuzzer Era Déjà Vu: Why the Numbers Are Only Half the Story
Behind the Scenes Hardening Firefox with Claude Mythos Preview
Mythos finds a curl vulnerability
NGINX Rift: Achieving NGINX Remote Code Execution via an 18-Year-Old Vulnerability
Microsoft Vibing — capturing screenshots and voice samples without governance
TrustFall: coding agent security flaw enables one-click RCE in Claude, Cursor, Gemini CLI and GitHub Copilot
Pwn2Own 2026 Capacity Overflow, Hackers Drop 0-Days Solo
Mythos finds a curl vulnerability
CVE-2025-32975: The Open Directory Behind the KACE SMA Breach and 60+ Downstream Victims
GhostLock — Lockout Without Encryption
Fragnesia: Linux Kernel Local Privilege Escalation via ESP-in-TCP
CVE-2026-20182: Critical authentication bypass in Cisco Catalyst SD-WAN Controller (FIXED)
BitUnlocker Downgrade Attack
Two more public disclosures, it will never stop
Microsoft Warns of Exchange Server Zero-Day Exploited in the Wild
Pwn2Own Berlin 2026: Day Three Results and Master of Pwn
Intelligence and Information Warfare
‘Disposable spies’: Poland records unprecedented number of Russian espionage cases
Revealed: Israeli Tech Exposes Users of Musk’s Starlink Satellite-based Internet
FamousSparrow APT Targets Azerbaijani Oil and Gas Industry
FrostyNeighbor: Fresh mischief and digital shenanigans
Gamaredon’s infection chain: Spoofed emails, GammaDrop and GammaLoad
What BO Team is hiding: the ZeronetKit backdoor from the inside and connections to Head Mare
Kazuar: Anatomy of a nation-state botnet
Cybersecurity
Meta can read your Instagram DMs starting Friday. One step could protect you
GTIG AI Threat Tracker: Adversaries Leverage AI for Vulnerability Exploitation, Augmented Operations, and Initial Access
NHS to grant Palantir contractors ‘unlimited access’ to patient data
The May 2026 Security Update Review
US govt seeks Instructure testimony on massive Canvas cyberattack
Welcome to the vulnpocalypse, as vendors use AI to find bugs and patches multiply like rabbits
Is the SOC Obsolete, and We Just Haven’t Admitted It Yet?
MPs want social media treated more like unsafe toys than harmless apps
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
Pierluigi Paganini
( SecurityAffairs – hacking, newsletter)