


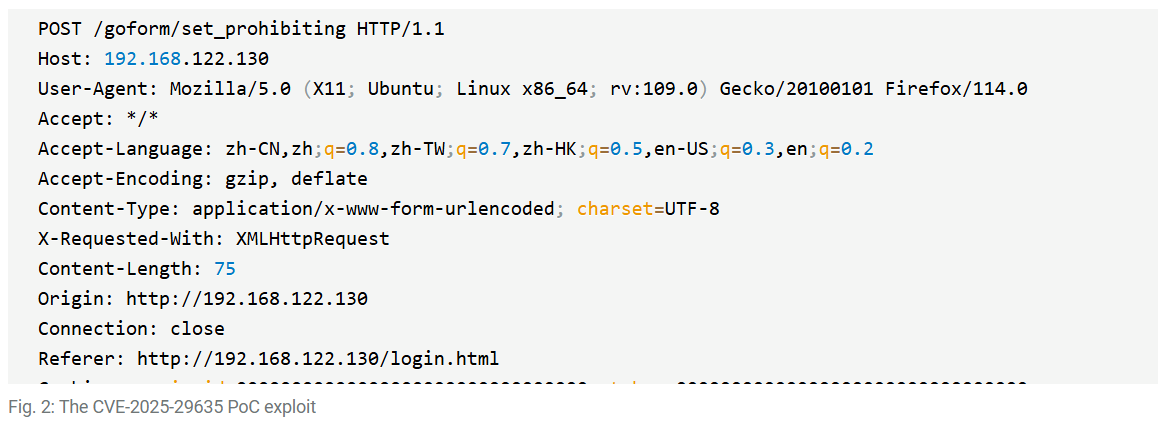
A Mirai botnet is actively exploiting a command injection vulnerability, tracked as CVE-2025-29635, in discontinued D-Link routers, Akamai reports. The flaw allows attackers to inject commands because an attacker-controlled value is copied without proper validation. The vulnerability impacts firmware versions 240126 and 24082 of D-Link DIR-823X series routers.
The experts observed that exploitation began about a year after public disclosure and PoC release, using crafted POST requests to compromise devices.

“The Akamai Security Intelligence and Response Team (SIRT) has identified active exploitation of command injection vulnerability CVE-2025-29635 against D-Link DIR-823X series routers. Although the devices were discontinued in 2025, threat actors are using this flaw to deploy Mirai botnet variants.” reads the report published by Akamai.
“The SIRT first identified this activity in our global network of honeypots in March 2026. This is the first reported active exploitation of these vulnerabilities since their initial disclosures in March 2025. “
Security researchers Wang Jinshuai and Zhao Jiangting reverse engineered the firmware’s sub_42232C function and found that attacker-controlled macaddr input is copied into a command buffer with snprintf and then passed to system(), enabling remote command execution via a crafted POST request to /goform/set_prohibiting.
They also published a PoC on GitHub, later removed, while the issue was still absent from CISA’s Known Exploited Vulnerabilities catalog at the time of the report. In early March 2026, Akamai SIRT observed active exploitation attempts using similar request patterns, including shell commands that fetch and execute malware from external infrastructure.
A simple shell script drops a Mirai variant (“tuxnokill”) from 88.214.20[.]14, supporting multiple architectures. The payload uses XOR encoding (key 0x30), includes standard Mirai strings, and contacts C2 at 64.89.161[.]130:44300. Hard-coded elements suggest manual development. The actor also exploits CVE-2025-29635, CVE-2023-1389 (TP-Link AX21), and a ZTE ZXV10 H108L RCE.
Mirai campaigns persist as attackers reuse its leaked code, lowering the barrier to entry and attracting both skilled and inexperienced actors seeking profit. While some threat actors reject AI, others increasingly adopt it to develop malware or discover vulnerabilities. AI thus represents both a growing risk in cybercrime and a valuable tool for defenders.
“many threat actors in the botnet space frequently target older vulnerabilities. Especially when public PoC exploits exist for these vulnerabilities, attackers can easily incorporate them into their exploitation vectors.” concludes the report that includes Indicators of Compromise (IoCs) along with Yara rules for malware samples. “Unfortunately, many organizations globally will improperly configure devices, fail to patch in a timely manner, or continue to use vulnerable devices that have been retired, as in the case with D-Link 823X series routers. We highly recommend that organizations regularly monitor vulnerability disclosures that are relevant to their infrastructure, and apply the proper patches, upgrades, and safeguards to ensure their own operational security.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Mirai)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。