





Malware targeting industrial control systems (ICS) poses a serious risk to critical infrastructure, with threats like Stuxnet, Industroyer, Triton, Havex, and BlackEnergy already demonstrating the ability to disrupt operations, cause outages, and even inflict physical damage. Recent research shows that ICS vulnerability disclosures nearly doubled between 2024 and 2025, driven in part by increased interest from threat actors targeting sectors such as energy, manufacturing, and utilities.
A key concern is the exposure of ICS devices to the internet, especially those using legacy protocols like Modbus. Widely used in industrial environments to enable communication between sensors and controllers, Modbus lacks basic security features such as encryption and authentication. This makes internet-exposed devices particularly vulnerable, as attackers can both read and modify data without needing credentials.
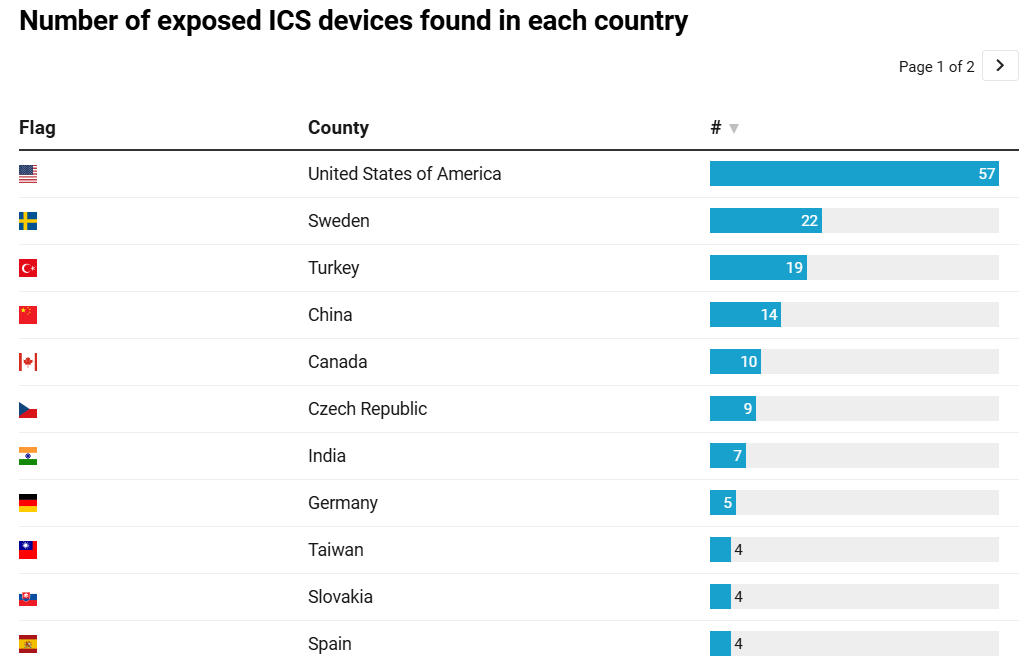
To better understand the scale of the issue, researchers conducted a global scan for devices responding on port 502, the default port for Modbus. Out of 311 initial responses, 179 were identified as likely real ICS devices after filtering out honeypots and unreliable data. These devices were found across multiple countries, with the United States hosting the largest number (57), followed by Sweden (22) and Turkey (19).

Some of the exposed systems were linked to highly sensitive environments. For example, one device appeared to be part of a national railway network, where ICS systems are used for train routing and signalling—functions critical to both safety and operations. Other devices were tied to national power grids in Europe and Asia, where ICS technology plays a central role in monitoring energy consumption and controlling distribution.
In terms of vendors, many devices did not reveal detailed manufacturer information, which is common for custom or embedded systems. However, among those that did, Schneider Electric devices were the most common, followed by Data Electronics and ABB Stotz-Kontakt.
“The majority of devices (128) only exposed their firmware versions and/or internal IDs without including a vendor string. This is to be expected from custom controllers or embedded modules.” reads the report published by Comparitech. “A total of 54 devices did advertise their manufacturer (though not always their model information). Schneider devices were most prevalent (22 instances), followed by Data Electronics (14 instances) and ABB Stotz-Kontakt (6 instances).”
Examples of exposed equipment included logic controllers, processor modules, energy meters, and power quality loggers—components essential for managing industrial processes and electrical systems.
Exposing device details such as make and model increases the risk further. Attackers can use this information to locate documentation like register maps, which define how data is stored and interpreted within the device. These registers may contain critical operational data such as temperature, voltage, pressure, or system status. In one case, researchers were able to monitor real-time energy consumption of a live system using publicly available documentation.
Even when device details are not explicitly disclosed, attackers may infer their function by analyzing how data values change over time. Since Modbus allows write access without authentication, attackers could alter register values, potentially disrupting operations. Even small changes could have cascading effects on industrial processes that rely on accurate sensor data.
The broader context makes the issue even more urgent. The global ICS market is growing rapidly, expected to more than double in value by 2033. As more devices are connected to networks, the attack surface expands, increasing the likelihood of exploitation if proper security measures are not implemented.
From a defensive standpoint, basic protections such as firewalls, VPNs, network segmentation, and strong authentication are essential to prevent unauthorized access. However, many ICS environments still rely on outdated architectures that were originally designed for isolated networks, not today’s interconnected landscape.
The research highlights how even attackers with limited technical skills could exploit exposed ICS devices, particularly those using insecure protocols like Modbus, DNP3, or BACnet.
“From an attacker’s perspective, devices running protocols like Modbus (as well as DNP3, or BACnet) are particularly vulnerable because they were designed for closed networks and often lack built-in authentication or encryption.” continues the report. “These devices could be exploited by attackers with limited technical expertise if exposed directly to the internet. This is particularly concerning given some ICS devices’ critical role in economic activity and essential infrastructure.”
Given the critical role these systems play in infrastructure and economic activity, their compromise could have wide-ranging consequences, from service disruptions to safety hazards.
In summary, the growing exposure of ICS devices, combined with insecure legacy protocols and increasing attacker interest, creates a high-risk environment. Without significant improvements in how these systems are secured and managed, industrial infrastructure will remain a prime target for cyber threats.
More info is included in the report by Justin Schamotta and Mantas Sasnauskas.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ICS)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。