
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

人人都是产品经理
人人都是产品经理
Google DeepMind News
博客园 - 【当耐特】
量子位
博客园 - 司徒正美
爱范儿
爱范儿
Hugging Face - Blog
Hugging Face - Blog
博客园 - 聂微东
Jina AI
Jina AI
J
Java Code Geeks
腾讯CDC
大猫的无限游戏
大猫的无限游戏
V
Visual Studio Blog
I
InfoQ
D
Docker
Recent Announcements
MongoDB | Blog
MongoDB | Blog
博客园 - Franky
宝玉的分享
宝玉的分享
G
Google Developers Blog
GbyAI
GbyAI
Y
Y Combinator Blog
有赞技术团队
有赞技术团队
H
Help Net Security

www.infosecurity-magazine.com

Just Three Ransomware Gangs Accounted for 40% of Attacks Last Month Google Chrome Rolls Out Protection Against Infostealers Targeting Session Cookies STX RAT Targets Finance Sector With Advanced Stealth Tactics Bitcoin Depot Reports $3.6m Crypto Theft After System Breach Atomic Stealer MacOS ClickFix Attack Bypasses Apple Security Warnings Middle East Hack-for-Hire Operation Traced to South Asian Cyber Espionage Group Governance Gaps Emerge as AI Agents Drive 76% Increase in NHIs Google Warns of New Threat Group Targeting BPOs and Helpdesks Google API Keys Quietly Gain Access to Gemini on Android Devices Critical Vulnerability in Ninja Forms Exposes WordPress Sites Anthropic Launches Project Glasswing to Use AI to Find and Fix Critical Software Vulnerabilities US Thwarts DNS Hijacking Network Controlled by Russian APT28 Hackers Claude Discovers Apache ActiveMQ Bug Hidden for 13 Years Iran‑Backed Threat Actors Hit US CNI Providers via Internet‑Facing OT Assets Russian APT28 Hackers Hijack Routers to Steal Credentials, UK Security Agency Warns GPU Rowhammer Attack Enables Privilege Escalation and Full System Compromise GrafanaGhost Exploit Bypasses AI Guardrails for Silent Data Exfiltration Over $17bn Lost to Cyber Fraud in the Last Year, Warns FBI Storm-1175 Exploits Flaws in High-Velocity Medusa Attacks Fortinet Releases Emergency Patch After FortiClient EMS Bug Is Exploited New Phishing Platform Used in Credential Theft Campaigns Against C-Suite Execs New 'Storm' Infostealer Remotely Decrypts Stolen Credentials NCSC Issues Security Alert Over Hackers Targeting WhatsApp and Signal Accounts Apple Expands iOS 18 Security Updates Amid DarkSword Threat Researchers Observe Sub-One-Hour Ransomware Attacks GitHub Used as Covert Channel in Multi-Stage Malware Campaign Most CNI Firms Face Up to £5m in Downtime from OT Attacks Google Introduces Android Dev Verification Amid Openness Debate New Venom Stealer MaaS Platform Automates Continuous Data Theft Chinese Hackers Target European Governments in Espionage Campaigns
Law Enforcement Dismantles SocksEscort Proxy Network in O...
Beth Maundrill · 2026-03-13 · via www.infosecurity-magazine.com

Written by

International law enforcement partners have executed Operation Lightning and dismantled malicious proxy service ‘SocksEscort.’

The proxy service is alleged to have compromised over 360,000 routers and internet of things (IoT) devices in163 countries since 2020 and offered ‘SocksEscort’ customers over 35,000 proxies in recent years.

As of February 2026, the SocksEscort application listed approximately 8000 infected routers to which its customers could buy access, of those, 2500 were in the US, a US Department of Justice (DoJ) statement said.

The malware allowed SocksEscort to direct internet traffic through the infected routers, which belonged to both businesses and individuals globally.

The malware-infected routers enabled cybercriminals to conceal their true originating IP addresses and locations, which furthered frauds like takeovers of US banks and cryptocurrency accounts and fraudulent unemployment insurance claims.

SocksEscort also enabled other criminal activities, including ransomware, distributed denial-of-service (DDoS) attacks and the distribution of child sexual abuse material (CSAM).

To get access to the proxy service, customers had to use a payment platform that made it possible to anonymously purchase the service using cryptocurrency. It is estimated that this payment platform received almost $6m from proxy service customers.

To protect against such exploits, router users, and vendors are advised to update the firmware of their devices regularly.
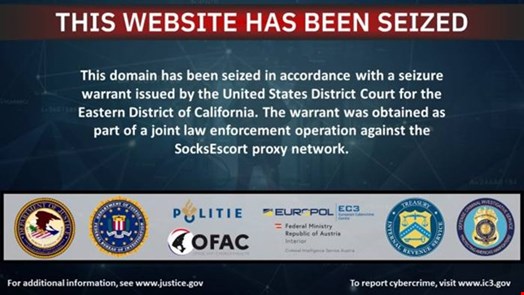
During the action day on March 11, law enforcement agencies successfully took down and seized 34 domains as well as 23 servers located in seven countries.

The US also froze $3.5m in cryptocurrency.

Law enforcement agencies involved in Operation Lightning included those from the US, Austria, France and the Netherlands. The European Union Agency for Criminal Justice, Eurojust, was also involved.

On the action day, Europol hosted a Virtual Command Post in its premises in The Hague, the Netherlands, to facilitate coordination between all partners.

Lumen Technologie’s Black Lotus Labs and the Shadowserver Foundation both provided assistance during the investigation and operation.